> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/ja/active-directory/acl-security-descriptors-and-permissions/vulnerable-acl-identification.md).
# 脆弱なACLを特定する
脆弱なACLを特定するためのActive Directoryセキュリティノート。列挙、Kerberos、資格情報、ACL悪用、ラテラルムーブメント、攻撃のワークフロー、検証手順を扱う。
分析を始めるには、機密性の高いグループの ACL を絞り込むことができます。たとえば、ドメイン管理者グループです。
脆弱な ACE の一覧
**ForceChangePassword**: 対象ユーザーの現在のパスワードを知らなくても、そのパスワードを変更できるようにします。次のものを使って悪用できます `Set-DomainUserPassword`.
**AddMembers**: 対象グループに任意のユーザー、グループ、またはコンピューターを追加できるようにします。次のものを使って悪用できます `Add-DomainGroupMember`.
**GenericAll**: オブジェクトに対する完全な制御権を与えます。これには、たとえば、他のユーザーをグループに追加する、ユーザーの現在のパスワードを知らなくてもそのパスワードを変更する、またはユーザーオブジェクトに SPN を設定するといった機能が含まれます。次のものを使って悪用できます `Set-DomainUserPassword` または `Add-DomainGroupMember`.
**GenericWrite**: 対象オブジェクトの保護されていない任意の属性を変更できるようにします。たとえば、次の `scriptPath` 属性を対象ユーザーに対して変更し、そのユーザーが次回ログインしたときに指定されたコマンドや実行ファイルを実行するようにできます。次のものを使って悪用できます `Set-DomainObject`.
**WriteOwner**: 対象オブジェクトの所有者を変更できるようにします。オブジェクトの所有者が攻撃者の制御下にあるユーザーに変更されると、攻撃者はその後自分に付与した権限に従ってオブジェクトを操作できます。次のものを使って悪用できます `Set-DomainObjectOwner`.
**WriteDACL**: 対象オブジェクトの DACL に新しい ACE を書き込めるようにします。たとえば、攻撃者は対象オブジェクトの DACL に新しい ACE を追加して、このオブジェクトに対する完全な制御権を自分に付与できます。次のものを使って悪用できます `Add-NewADObjectAccessControlEntry`.
**AllExtendedRights**: 対象オブジェクトに対して、Active Directory の拡張権限に関連付けられたすべての操作を実行できるようにします。たとえば、ユーザーをグループに追加したり、対象ユーザーのパスワード変更を強制したりできます。次のものを使って悪用できます `Set-DomainUserPassword` または `Add-DomainGroupMember`.
{% code overflow="wrap" %}
```powershell
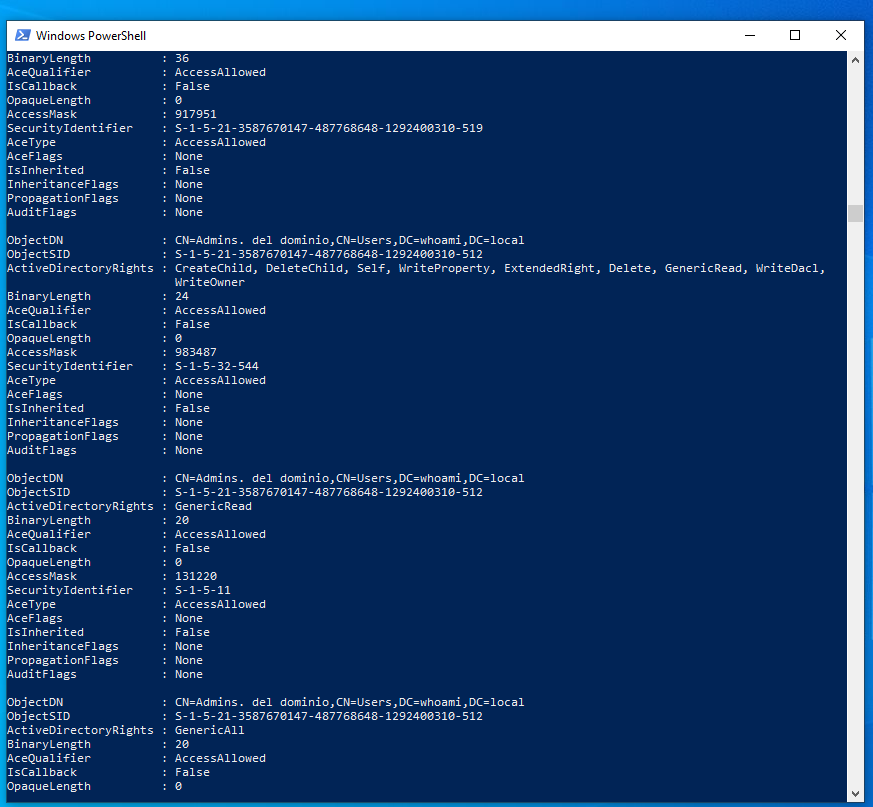
Get-DomainObjectAcl -Identity "Domain Admins"
```
{% endcode %}
システムの言語によっては、このグループは次の名前でも表示される場合があります:
```bash
Domain Admins
```
または:
```bash
Domain Admins
```
このコマンドはオブジェクトに適用された権限を返しますが、識別子はしばしば次のように表示されます **SID**.
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/ja/active-directory/acl-security-descriptors-and-permissions/vulnerable-acl-identification.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.