> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/ja/hacking-tools/web/wmap-scan-web-vulnerabilities.md).
# WMAP Web 脆弱性スキャン
Metasploit 経由で Web 脆弱性スキャンを実行し、見つかったアプリケーション問題を確認するための WMAP メモ。
{% hint style="info" %}
WMAPは、Webアプリケーションに対するペネトレーションテストを実施するために設計されたMetasploitプラグインで、特にサイト固有の脆弱性を見つけることを目的としています。Web対象に対して自動化されたセキュリティスキャンを実行できます。
{% endhint %}
**Metasploitへの接続:** 他のツールとは異なり、WMAPはMetasploitへの特定の接続を必要とせず、Metasploitフレームワークに直接統合されて動作します。
#### WMAPスキャンを実行する
1. **WMAPモジュールを読み込む:** まず、次のコマンドでMetasploitにWMAPモジュールを読み込む必要があります:
```
load wmap
```
2. **対象サイトを作成する:** 次のコマンドを使用して、テスト対象サイトのIPアドレスまたはドメインを指定する必要があります:
```
wmap_sites -a 10.10.10.10
```
3. **対象を指定する:** 対象サイトのURLを設定するには、スキャン用のURLを構成する次のコマンドを使用します:
```bash
wmap_target -t http://10.10.10.10/
```
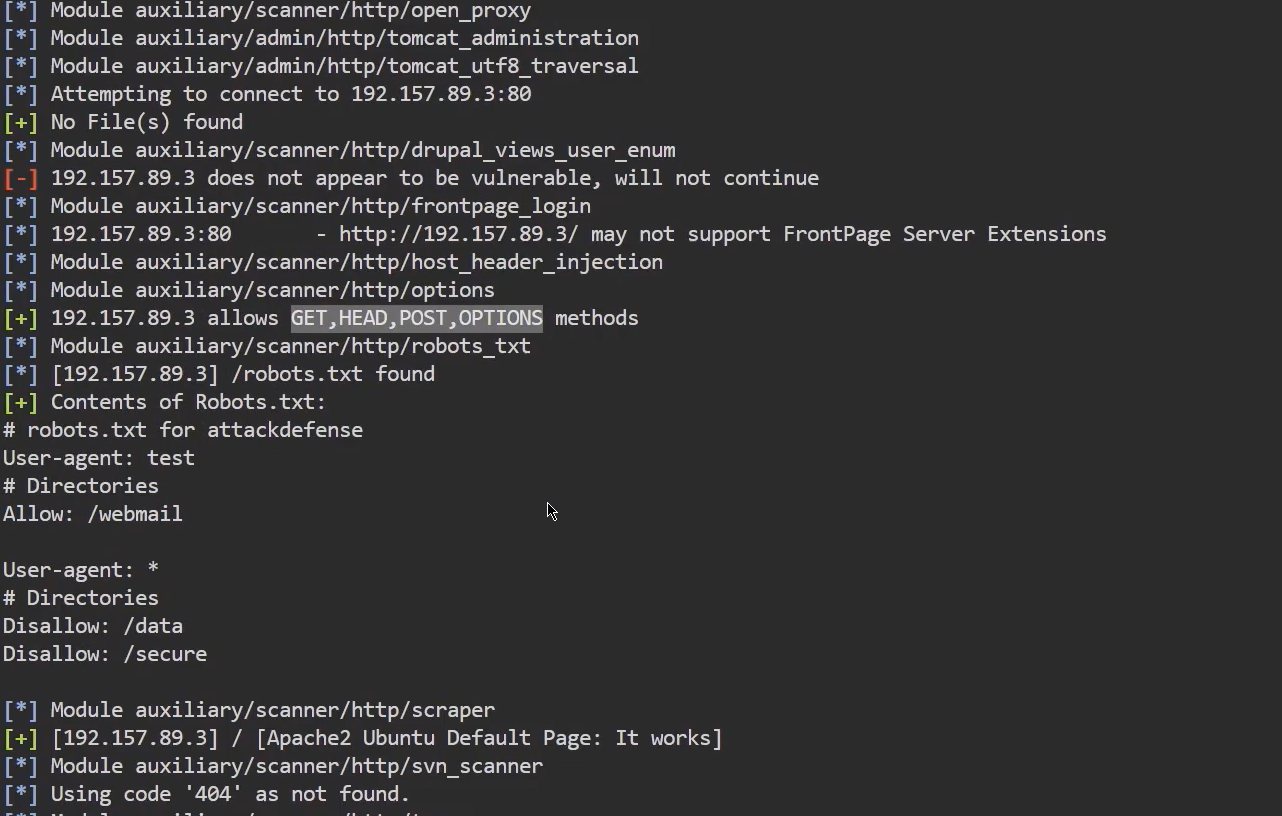
4. **すべてのモジュールでスキャンを開始する:** すべてのWMAPモジュールを有効にしてフルスキャンを実行するには、次のコマンドを使用します:
```bash
wmap_run -t
```
* このコマンドは、利用可能なすべてのモジュールを使用してスキャンを開始し、対象のWebアプリケーションの脆弱性を調査します。
```bash
wmap_run -e
```
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/ja/hacking-tools/web/wmap-scan-web-vulnerabilities.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.