> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/ja/hacking-tools/windows/windows-enumeration.md).
# Windows 列挙
ユーザー、権限、グループ、サービス、プロセス、ネットワーク状態、システムコンテキストのための Windows ローカル列挙コマンド。
### MetasploitによるWindows列挙
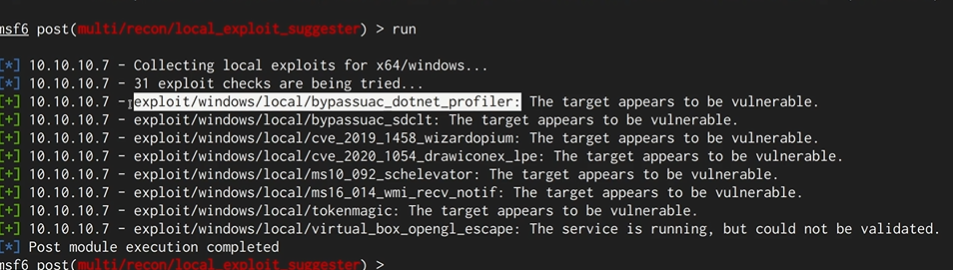
カーネルの脆弱性に基づく権限昇格エクスプロイトを見つけるには、次を使用できます **multi/recon/local/\_exploit/\_suggester** これはMetasploitのモジュールで、カーネルのバージョンを分析して潜在的なエクスプロイトを特定します。
```bash
multi/recon/local_exploit_suggester を使用します
```
### 手動でのWindows列挙
{% embed url="" %}
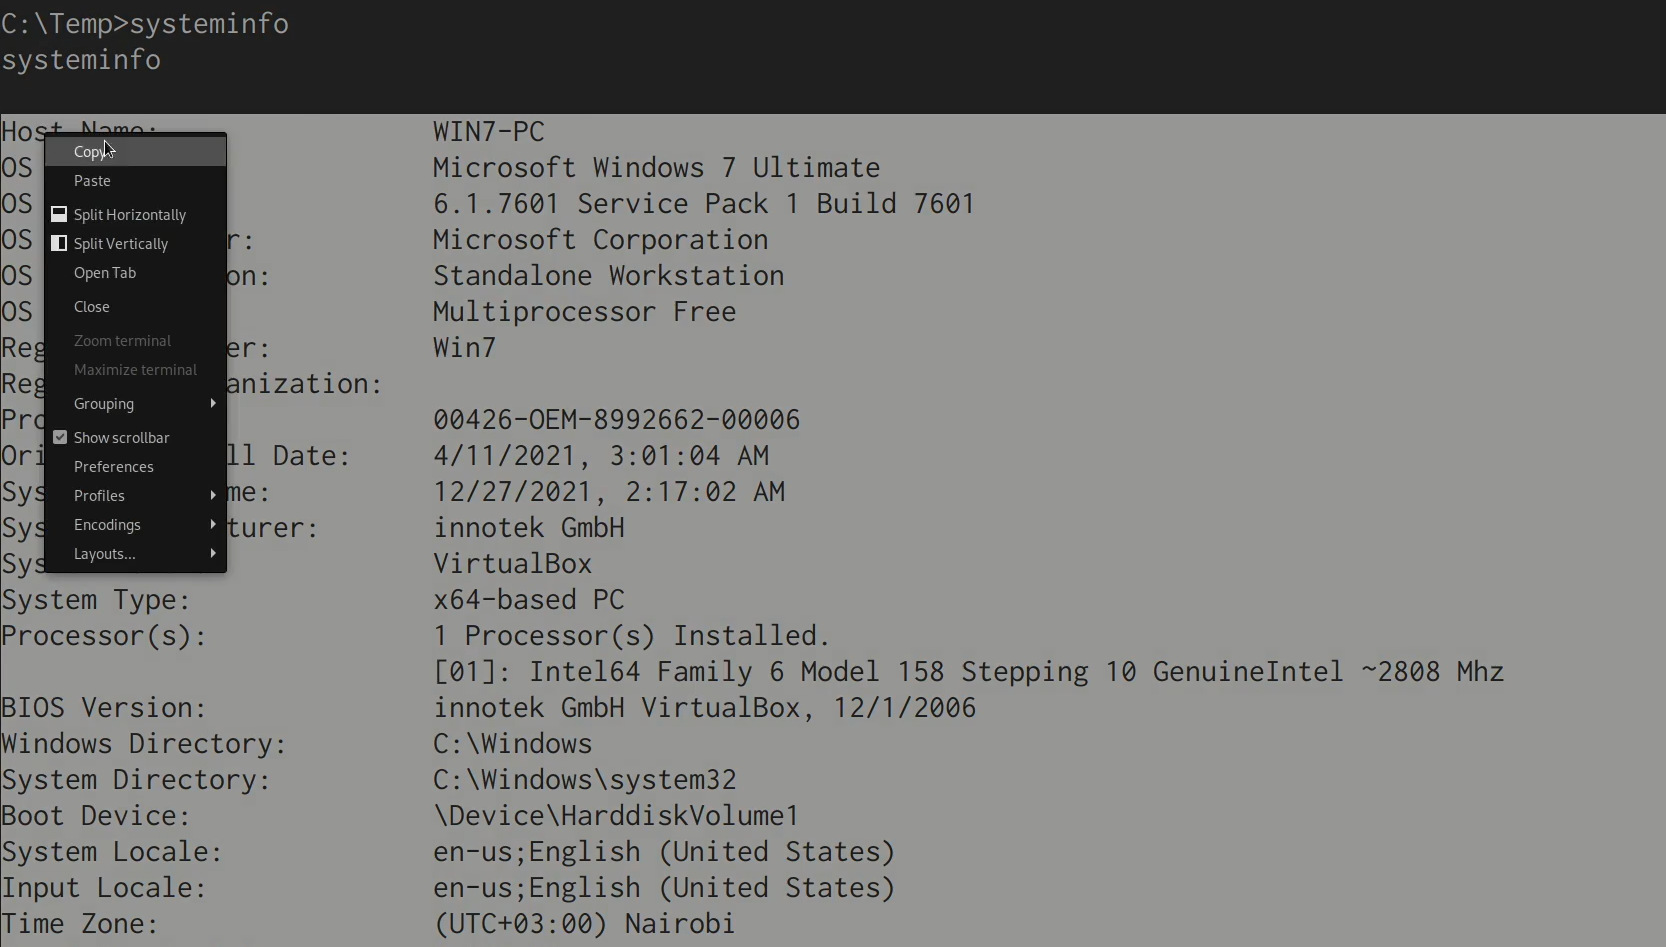
まず、次を使ってシステム情報を一覧表示します `systeminfo` コマンド:
```bash
systeminfo
```
* すべての結果を、という名前のファイルにコピーします **win.txt**.
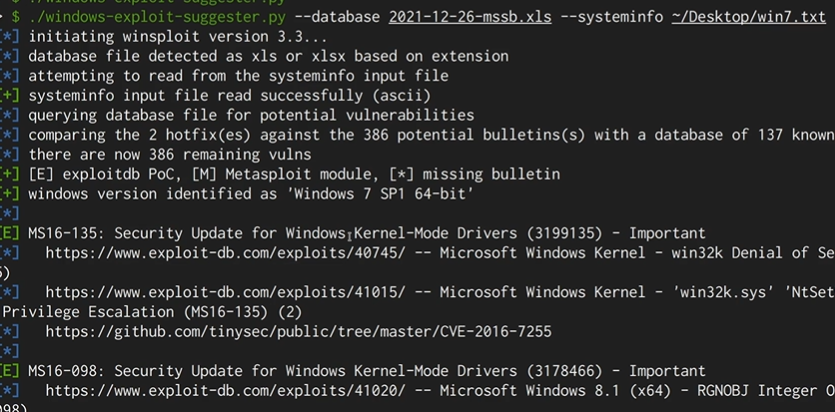
次を使用します **windows-exploit-suggester** システムのバージョンに一致するエクスプロイトを見つけるスクリプト:
```bash
./windows-exploit-suggester.py --update
```
```bash
./windows-exploit-suggester.py --database 2025-03-29-mssb.xls --systeminfo win.txt
```
* これにより、対象マシンに対する潜在的なエクスプロイトの一覧が生成されます。
### PowerShellスクリプトによる列挙
> JAWSは、ペネトレーションテスター(およびCTF参加者)がWindowsシステム上の潜在的な権限昇格経路を素早く特定できるように設計されたPowerShellスクリプトです。PowerShell 2.0で記述されているため、Windows 7以降のすべてのWindowsバージョンで動作するはずです。
{% embed url="" %}
手順:
{% code overflow="wrap" %}
```
CMD C:/temp> powershell.exe -ExecutionPolicy Bypass -File ./jaws-enum.ps1 -OutputFilename JAWS-Enum.txt
```
{% endcode %}
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/ja/hacking-tools/windows/windows-enumeration.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.