> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/ja/reconnaissance/web-fuzzing.md).
# Webファジング
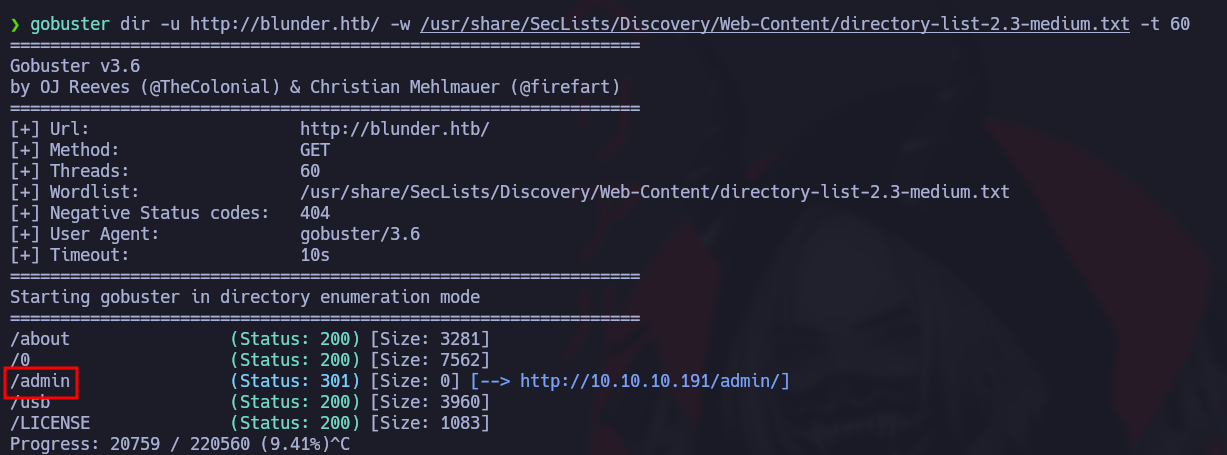
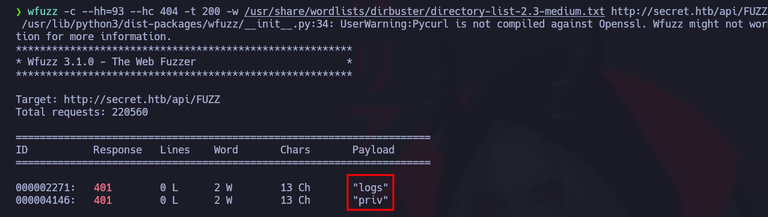
Gobuster や Wfuzz などのツールを使って、隠されたディレクトリ、ファイル、拡張子、パラメータ、公開リソースを見つけるための Web ファジング手法。
Webファジングは、Webアプリケーションの調査中に、隠れたディレクトリ、ファイル、拡張子、パラメータ、仮想ホスト、および露出したリソースを見つけるのに役立ちます。
{% hint style="info" %}
ウェブサイト上のディレクトリやファイルを見つけるためのツールや方法は多くあり、コマンドラインからでもオンラインリソース経由でも行えます。主なアプローチと最も有用なツールは次のとおりです:
{% endhint %}
## Gobuster:
> Gobusterは、Webサイトのディレクトリやファイルに対してブルートフォース攻撃を行うための高速で効果的なツールです。
### **ディレクトリのみ:**
```bash
gobuster dir -u http://website.com/ -w /usr/share/SecLists/Discovery/Web-Content/directory-list-2.3-medium.txt -t 100
```
* **-u**: 対象サイトのURL。
* **-w**: キーワード一覧(ワードリスト)を含むファイルのパス。
* **-t**: 検索に使用するスレッド数。
### **特定の拡張子を持つファイル:**
```bash
gobuster dir -u http://website.com/ -w /usr/share/SecLists/Discovery/Web-Content/quickhits.txt -t 100 -x html,php,txt
```
* **-x**: 検索対象の拡張子を指定します。
### **レスポンスに特定のフィルターを追加する:**
* **-hh**: 本文サイズをバイト単位でフィルタリングします。
* **-hc**: 特定のステータスコード(たとえば 404)を含むレスポンスを除外します。
## Wfuzz:
> Wfuzzは、ディレクトリやURL内のパラメータのいずれに対しても、ブルートフォース攻撃による高度で設定可能な検索を可能にします。
### **ディレクトリのみ:**
```bash
wfuzz -c -t 100 -w /usr/share/SecLists/Discovery/Web-Content/directory-list-2.3-medium.txt http://website.com/FUZZ
```
* **-c**: 色付きで出力を表示します。
* **FUZZ**: キーワードを挿入する位置を示します。
### **特定の拡張子を持つファイル:**
```bash
wfuzz -c -t 100 -w /usr/share/SecLists/Discovery/Web-Content/quickhits.tx -z list,html-txt-php http://website.com/
```
* **-z**: 検索に使用する追加の拡張子を定義します(list を使うと複数の拡張子を指定できます)。
### **動的なパラメータ値(`?product_id=`) :**
```bash
wfuzz -c -t 100 -z range,1-200000 'http://website.com/shop/buy/detail?product_id=FUZZ'
```
* **-z range,1-200000**: 1から200,000までの範囲でブルートフォース攻撃を実行します。
## **追加の方法:**
### 公開ソースの発見:
視覚的な公開ソースの方法を好む場合は、以下の管理されたカタログを使用してください [OSINTおよび調査ツール](/ja/hacking-tools/osint.md).
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/ja/reconnaissance/web-fuzzing.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.