> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/ja/web/business-logic/high-level-logic-vulnerability.md).
# 高レベルの論理脆弱性
高レベルの論理脆弱性の PortSwigger Web Security Academy ラボ向けノート。攻撃フロー、ペイロードテスト、Burp Suite による検証、および是正策の文脈を含みます。
### 高レベルのロジック脆弱性
**ラボの説明**
このラボでは、ユーザーが提供したデータを適切に検証していません。購入プロセスの論理的な欠陥を悪用して、商品の最終価格を変更することができます。/ 目的は \*\* を購入することです
提供された識別子:
* **ユーザー**: wiener
* **パスワード**: peter
**バスケットの動作の分析**
商品をバスケットに追加すると、送信されるリクエストは次のようになります:
```bash
productId=1&redir=PRODUCT&quantity=1
```
その `数量` パラメータはクライアントによって直接制御され、サーバー側で適切に検証されていません。
**論理的欠陥の悪用**
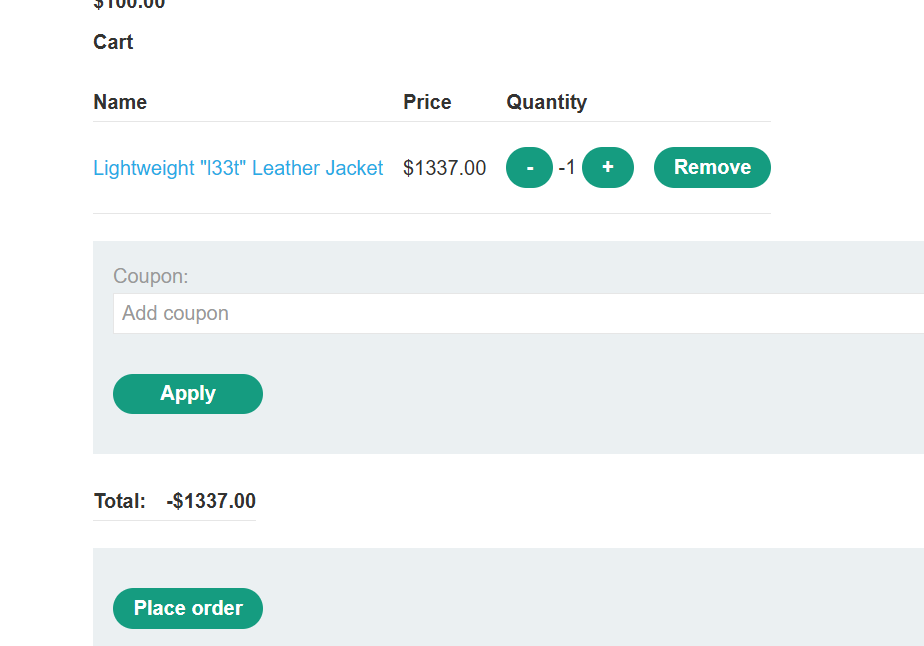
たとえば、数量を負の値に変更すると、次のようになります:
```bash
productId=1&redir=PRODUCT&quantity=-1
```
バスケットの合計金額が減少し、負の価格になります(例: \*\* $1337)。
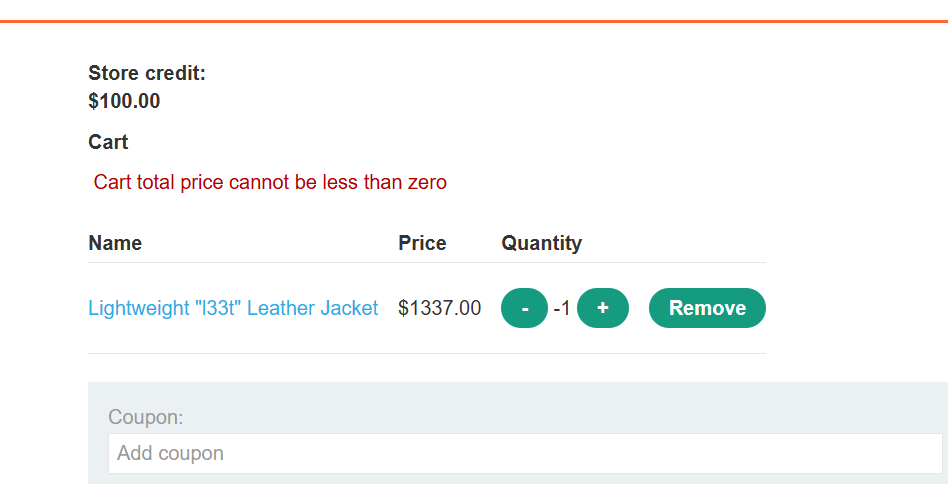
ただし、バスケットを検証する際に、アプリケーションはこのケースを次のメッセージでブロックします:
> *カートの合計価格はゼロ未満にできません*
**制限の回避**
脆弱性を悪用するには:
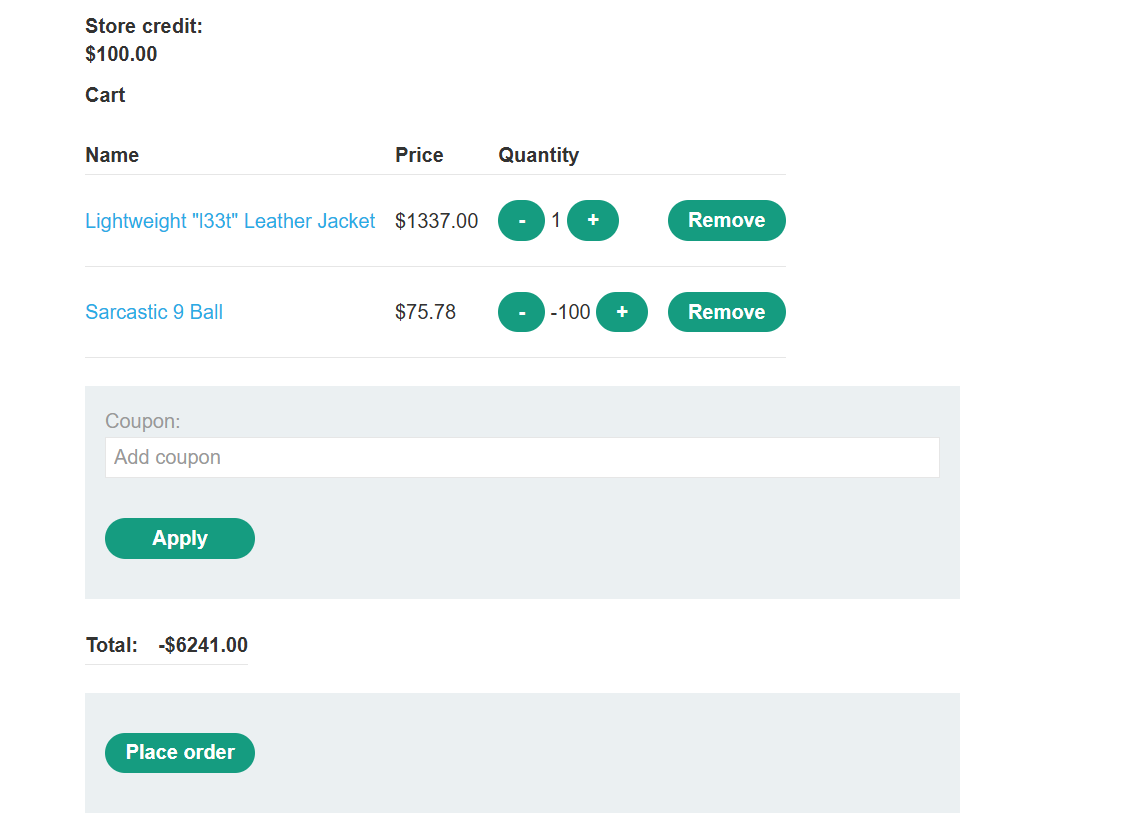
次を追加 **対象のジャケット** 有効な数量で:
```bash
productId=1&redir=PRODUCT&quantity=1
```
その後、合計を減らすために、別の商品を負の数量で追加します:
```bash
productId=2&redir=PRODUCT&quantity=-100
```
その結果、合計は大きく負の値になります(例: **-$6241.00**).
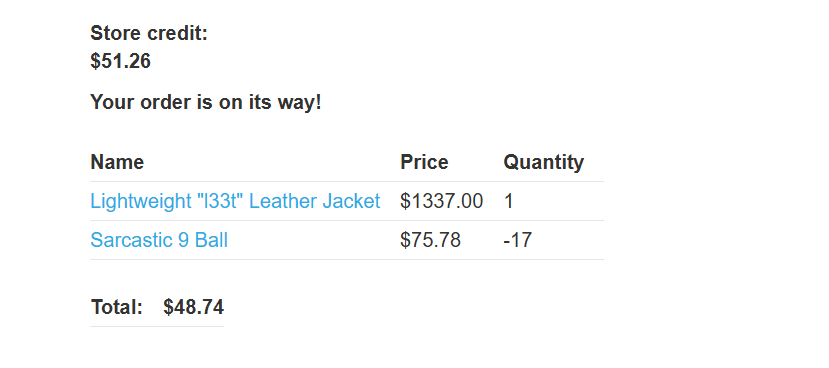
負の数量を調整し(例: `-17`) して、最終合計が **正の**ただし非常に低い値(100ドル未満)にします。
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/ja/web/business-logic/high-level-logic-vulnerability.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.