> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/ja/web/csrf/csrf-vulnerability-with-no-defenses.md).
# 保護なしのCSRF脆弱性
PortSwigger Web Security Academy のラボ向けメモ。保護なしのCSRF脆弱性に関するもので、攻撃手順、ペイロードのテスト、Burp Suite による検証、および対策の文脈を含む。
### 防御のないCSRF脆弱性
#### 説明
このラボのメール変更機能はCSRF攻撃に対して脆弱です。目的は、被害者ユーザーのメールアドレスを同意なしに変更するクライアント側リクエストを偽造することです。
#### 目的
訪問者のメールアドレスを変更するCSRF攻撃を実行するHTMLコンテンツを作成し、そのコンテンツをエクスプロイトサーバーにアップロードしてください。
#### 識別子
次のアカウントでログインできます:/ **wiener: peter**
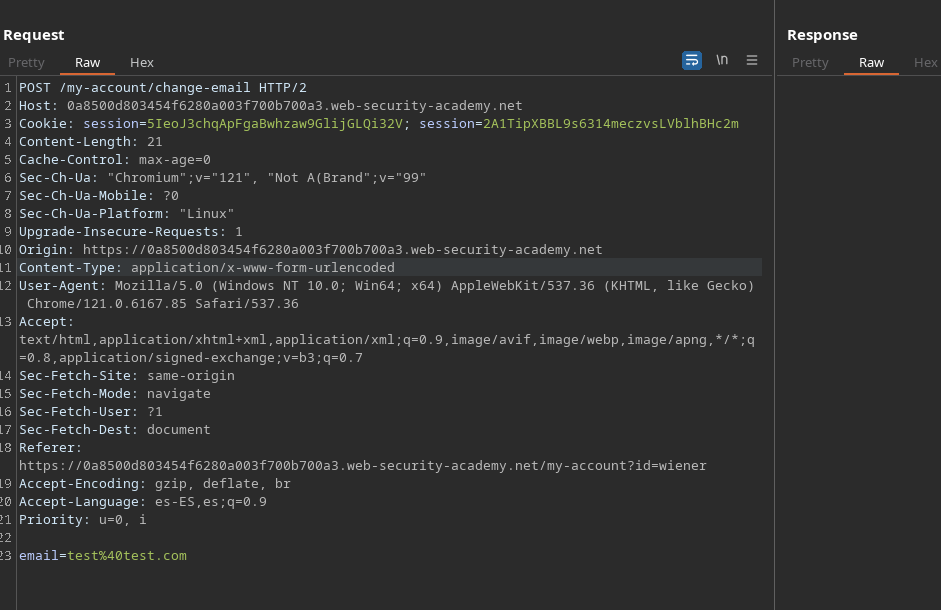
傍受すると、メール変更のリクエストは単純なPOSTリクエストであり、次を受け入れていることがわかります `email` パラメータ。CSRF対策(トークン、オリジンなど)はありません。そのため、エクスプロイトサーバーでホストされたページからフォーム送信を自動化できます。
#### エクスプロイトサーバーに配置するペイロードHTML
以下のHTMLは、メール変更URLをターゲットにしたフォームを作成し、ページ読み込み時に自動送信します:
```html
```
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/ja/web/csrf/csrf-vulnerability-with-no-defenses.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.