> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/ports-and-services/smb-445/crackmapexec-smb-tool.md).
# CrackMapExec (SMB Tool)
SMB enumeration with CrackMapExec for hosts, users, credentials, shares, elevated access, and RID brute force.
> CrackMapExec (CME) is a post-exploitation security auditing tool for Active Directory environments. It validates credentials, enumerates SMB exposure, detects common weaknesses, and can execute remote commands when sufficient privileges are available.
### **System enumeration**
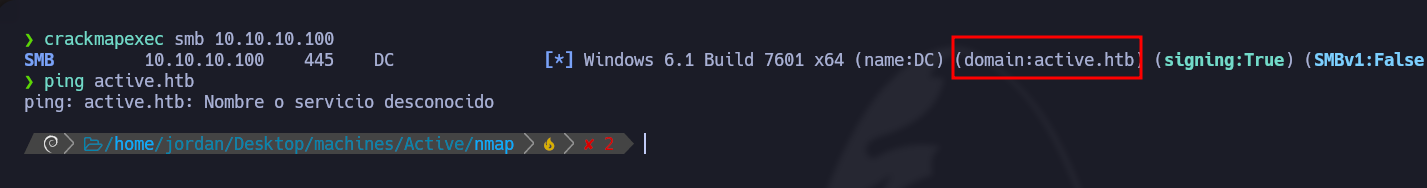
To identify systems on the network and discover the domain name:
```bash
crackmapexec smb 10.10.10.10
```
This provides information about the target SMB server, including the domain and available services.
#### User enumeration
```bash
crackmapexec smb 10.10.10.10 -u '' -p '' --users
```
### **Credential validation**
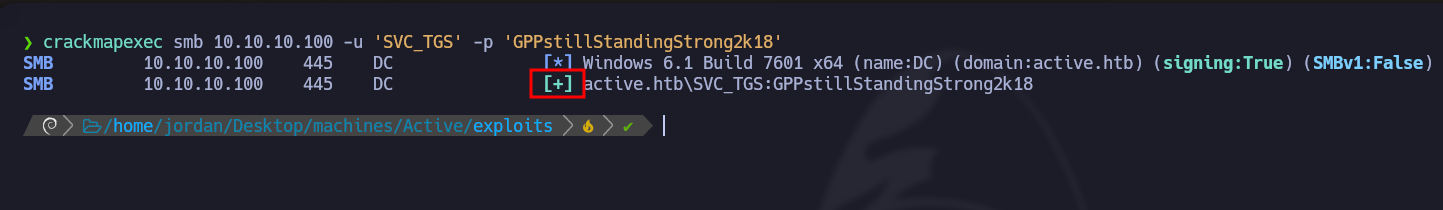
To check if a user/password pair is valid:
```bash
crackmapexec smb 10.10.10.10 -u '' -p ''
```
If the credentials are correct, CME will confirm access to the target system.
### **Credential validation with elevated access (PWNED)**
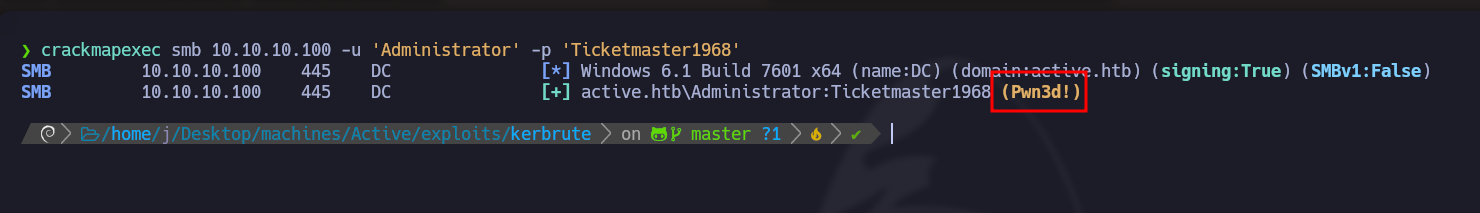
If the user belongs to the **Remote Management Users** group, the account can connect directly to the target system. To validate these credentials:
```bash
crackmapexec smb 10.10.10.10 -u '' -p ''
```
A response indicating PWNED access means that the user has elevated permissions, potentially allowing remote execution.
### **Share and permission enumeration**
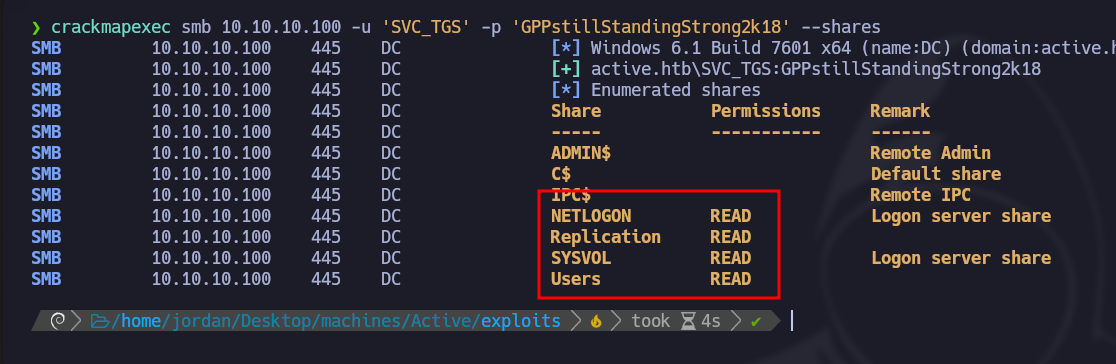
To explore the permissions and network shares accessible with the credentials provided:
```bash
crackmapexec smb 10.10.10.10 -u '' -p '' --shares
```
This displays the available shares and permissions associated with the user.
### RID brute force
#### To identify domain users, launch a RID brute force attack:
```bash
crackmapexec smb 10.10.11.35 -u 'Guest' -p "" --rid-brute
```
> The `--rid-brute` parameter performs a **brute force attack** against **RIDs (Relative Identifiers)** in a Windows domain. A RID is part of a Windows security identifier and is commonly used to identify user and group accounts.
Here is the list of users found:
```
Administrator
Guest
krbtgt
CICADA-DC$
john.smoulder
sarah.dantelia
michael.wrightson
david.orelious
emily.oscars
```
#### User validation
Test the discovered password against all enumerated users:
```bash
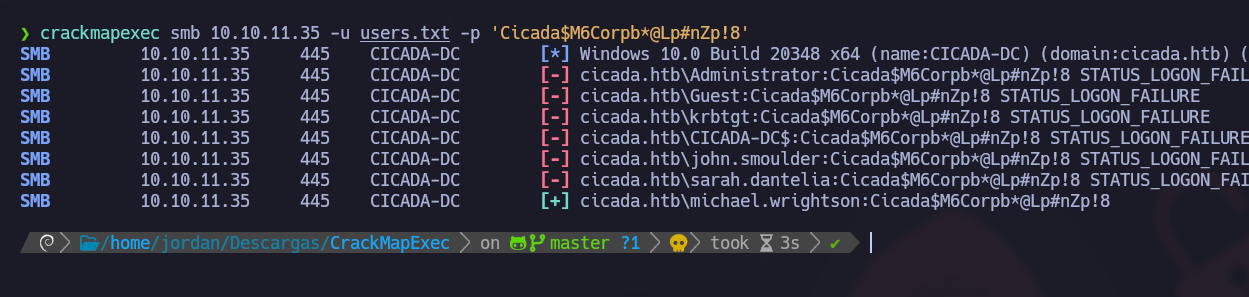
crackmapexec smb 10.10.11.35 -u users.txt -p 'Cicada$M6Corpb*@Lp#nZp!8'
```
The user **michael.wrightson** uses this password.
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/ports-and-services/smb-445/crackmapexec-smb-tool.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.